Chapterبەش 4 · Lectureوانە 4.4
Reverse Engineering: Taking Software Apart to Understand Itئەندازیاریی پێچەوانە: لێککردنەوەی نەرمەواڵە بۆ تێگەیشتن لێی
What reverse engineering is and why it matters for defenders: forward vs. reverse engineering, where it is used (interoperability, finding weaknesses, malware analysis, recovering lost source), how compiled code looks with two safe demos (Python's dis and Java's javap -c), static vs. dynamic analysis, the tool categories (disassemblers, decompilers, debuggers, sandboxes, network monitors, with free examples such as Ghidra and Wireshark), the defender's malware-analysis workflow and indicators of compromise, obfuscation and packing, the law and ethics (EU Directive 2009/24/EC, US DMCA §1201, licences, check the law where you live, responsible disclosure), and why security by obscurity fails.
چییە و بۆچی بۆ بەرگریکەران گرنگە: بەرامبەر پێچەوانە، لە کوێ بەکار دێت (، دۆزینەوەی لاوازی، ، گەڕاندنەوەی سەرچاوەی ونبوو)، بەرنامەیەکی کۆمپایلکراو چۆن دیارە بە دوو نموونەی سەلامەت (disـی Python و javap -cـی Java)، بەرامبەر ، پۆلەکانی ئامراز (، ، ، ، چاودێری ، بە نموونەی بێبەرانبەر وەک Ghidra و Wireshark)، ڕێڕەوی بەرگریکەر و ، و پێچانەوە، یاسا و ئەخلاق (ئاراستەی ئەوروپی 2009/24/EC، DMCA §1201ـی ئەمریکا، مۆڵەتەکان، پشکنینی یاسای شوێنی خۆت، ) و بۆچی شکست دەهێنێت.
What you will learnچی فێر دەبیت
- Explain what reverse engineering is and how it differs from forward engineering.
- List where reverse engineering is used, in hardware and software.
- Read a tiny program's bytecode with Python's dis and Java's javap -c.
- Tell static analysis from dynamic analysis and name the main tool categories.
- Describe the defender's malware-analysis workflow and indicators of compromise.
- State the limits set by law and ethics, and why security by obscurity fails.
- ڕوون بکەیتەوە چییە و چۆن لە جیاوازە.
- ڕیز بکەیت لە کوێ بەکار دێت، لە و .
- بەرنامەیەکی بچووک بە disـی Python و javap -cـی Java بخوێنیتەوە.
- لە جیا بکەیتەوە و پۆلە سەرەکییەکانی ئامراز ناو ببەیت.
- ڕێڕەوی بەرگریکەر و وەسف بکەیت.
- ئەو چوارچێوانە بڵێیت کە یاسا و ئەخلاق دایدەنێن و بۆچی شکست دەهێنێت.
What is reverse engineering?ئەندازیاریی پێچەوانە چییە؟
Taking a finished product, such as a program, a device or a file format, and studying it to work out how it was made and how it works, without its design documents or .
وەرگرتنی بەرهەمێکی تەواوکراو (وەک بەرنامەیەک، ئامێرێک یان شێوەی فایلێک) و لێکۆڵینەوە لێی بۆ ئەوەی بزانیت چۆن دروست کراوە و چۆن کار دەکات، بەبێ بەڵگەنامەکانی دیزاین یان .
You already know forward engineering: a maker starts with an idea, draws a design, writes the , and ends with a finished product. Reverse engineering goes the other way. You start with the finished product — a program, a chip, a file — and study it to work out how it was made and how it works, without the design papers or the source code.
تۆ پێشتر دەناسیت: دروستکەرێک بە بیرۆکەیەک دەست پێ دەکات، دیزاینێک دەکێشێت، دەنووسێت و بە بەرهەمێکی تەواوکراو کۆتایی دێت. بە پێچەوانەوە دەڕوات. بە بەرهەمە تەواوکراوەکەوە دەست پێ دەکەیت — بەرنامەیەک، چیپێک، فایلێک — و لێی دەکۆڵیتەوە بۆ ئەوەی بزانیت چۆن دروست کراوە و چۆن کار دەکات، بەبێ کاغەزەکانی دیزاین یان .
A mechanic who has never seen the plans of a car engine can still open it, look at every part, and learn how it turns fuel into movement. A cook can taste a dish and work out the recipe. Reverse engineering is the same idea for software and hardware: learn the design from the finished thing.
مەکانیکییەک کە هەرگیز نەخشەی بزوێنەری ئۆتۆمبێلێکی نەدیوە، هێشتا دەتوانێت بیکاتەوە، سەیری هەموو پارچەیەک بکات و فێر ببێت چۆن سووتەمەنی دەکات بە جووڵە. چێشتلێنەرێک دەتوانێت تامی خواردنێک بکات و ڕێسەتەکەی بدۆزێتەوە. هەمان بیرۆکەیە بۆ و : فێربوونی دیزاین لە شتە تەواوکراوەکەوە.
Where the analogy stops workingسنووری ئەم نموونەیە
An engine is made of metal parts you can see and touch. Software is hidden inside a file, so you need tools like a to look inside.
بزوێنەر لە پارچەی ئاسنە کە دەیبینیت و دەستی لێ دەدەیت. لە ناو فایلێکدا شاردراوەتەوە، بۆیە پێویستت بە ئامرازی وەک هەیە بۆ سەیرکردنی ناوەوەی.
Reverse engineering is a skill, not a crime. Engineers, researchers and security teams use it every day. Whether a particular use is allowed depends on why you do it and on the law where you live — we come to that at the end of the lesson.
کارامەییەکە، نەک تاوان. ئەندازیار، توێژەر و تیمەکانی هەموو ڕۆژێک بەکاری دەهێنن. ئایا بەکارهێنانێکی دیاریکراو ڕێپێدراوە، ئەوە بەس بەوە دەزانرێت کە بۆچی دەیکەیت و بە یاسای شوێنی خۆت — لە کۆتایی وانەکەدا دێینە سەری.
What is reverse engineering?ئەندازیاریی پێچەوانە چییە؟
Forward vs. reverse, side by sideبەرەوپێش بەرامبەر پێچەوانە، تەنیشت یەک
In forward engineering each step adds detail: idea → design → source code → product. In reverse engineering you walk the road backwards: product → study it → how it works. You can rarely get back the maker's exact source code or comments, but you can understand what the thing does.
لە ئەندازیاریی بەرەوپێشدا هەر هەنگاوێک وردەکاری زیاد دەکات: بیرۆکە ← دیزاین ← ← بەرهەم. لە پێچەوانەدا ڕێگاکە بەرەو دواوە دەبڕیت: بەرهەم ← لێی بکۆڵەرەوە ← چۆن کار دەکات. بە دەگمەن دەتوانیت ڕێک یان دروستکەرەکە بگەڕێنیتەوە، بەڵام دەتوانیت تێبگەیت کە شتەکە چی دەکات.
Where it is usedلە کوێ بەکار دێت
Reverse engineering is used on both hardware and software, almost always for good reasons:
لەسەر هەردوو و بەکار دێت، تەواو زۆرجار بۆ هۆکاری باش:
- Interoperability — making your program work with another maker's program or file format.
- Finding weaknesses — a security team studies a product to find before attackers do.
- Malware analysis — defenders take a bad program apart to see what it does and how to stop it.
- Recovering lost source code — an old program still runs, but its is gone, so it is rebuilt from the compiled file.
- Checking an app — seeing what data an app really sends, and to whom.
- — وا کردنی بەرنامەکەت بۆ ئەوەی لەگەڵ بەرنامە یان فۆرماتی فایلی دروستکەرێکی تردا کار بکات.
- دۆزینەوەی لاوازی — تیمێکی لە بەرهەمێک دەکۆڵێتەوە بۆ دۆزینەوەی پێش .
- — بەرگریکەران بەرنامەیەکی خراپ لێک دەدەنەوە بۆ بینینی ئەوەی چی دەکات و چۆن ڕایدەگرن.
- گەڕاندنەوەی ونبوو — بەرنامەیەکی کۆن هێشتا کار دەکات، بەڵام نەماوە، بۆیە لە فایلە کۆمپایلکراوەکەوە دروست دەکرێتەوە.
- پشکنینی — بینینی ئەوەی بە ڕاستی چ دەنێرێت و بۆ کێ.
Where it is usedلە کوێ بەکار دێت
A real story: Samba and interoperabilityچیرۆکێکی ڕاستەقینە: Samba و توانای پێکەوەکارکردن
In 1992 a student named Andrew Tridgell wanted his Unix computer to share files with Windows computers. Microsoft's file-sharing rules were not published. So he watched the on the to learn the rules, and wrote Samba, which still lets Linux and Windows share files today. That is reverse engineering for — making different systems work together — and it is a classic, lawful use.
لە ساڵی 1992دا خوێندکارێک بە ناوی ئەندرو تریجڵ دەیویست Unixـەکەی فایل لەگەڵ Windows هاوبەش بکات. ڕێساکانی هاوبەشکردنی فایلی Microsoft بڵاو نەکرابوونەوە. بۆیە سەیری سەر کرد بۆ فێربوونی ڕێساکان و Sambaـی نووسی، کە تا ئەمڕۆش ڕێگە دەدات Linux و Windows فایل هاوبەش بکەن. ئەوە بۆ — وا کردنی سیستەمە جیاوازەکان بۆ ئەوەی پێکەوە کار بکەن — و بەکارهێنانێکی کلاسیکی و یاساییە.
The same idea protects you as a user. By watching what an app sends, a researcher can find an app that quietly ships your to a far-away you never agreed to.
هەمان بیرۆکە وەک بەکارهێنەرێک تۆ دەپارێزێت. بە سەیرکردنی ئەوەی دەینێرێت، توێژەرێک دەتوانێت بدۆزێتەوە کە بە بێدەنگی بۆ دوور دەنێرێت کە تۆ هەرگیز ڕازی نەبوویت.
What a compiled program looks likeبەرنامەیەکی کۆمپایلکراو چۆن دیارە
A program is written as that people can read. Before it runs, a turns it into (0s and 1s for the ) or into for a . You do not need to re-learn this step here — it is taught in How code becomes a running program. The point for us is what is kept and what is lost.
بەرنامە وەک دەنووسرێت کە خەڵک دەتوانن بیخوێننەوە. پێش ئەوەی جێبەجێ بێت، دەیکات بە (0 و 1 بۆ ) یان بە بۆ . پێویست ناکات ئەم هەنگاوە لێرە دووپاتە فێر ببیت — لە چۆن کۆد دەبێت بە بەرنامەیەک کە کار دەکاتدا دەوترێت. خاڵە گرنگەکە بۆ ئێمە ئەوەیە کە چی دەمێنێتەوە و چی لەدەست دەچێت.
When a program is compiled, the exact logic stays — every if, every number, every call to a library. The text and names a user sees also stay. What is thrown away is only for humans: your , your names, blank lines and layout. That is why reverse engineering is possible: the logic is all still there, just harder to read.
کاتێک بەرنامەیەک کۆمپایل دەکرێت، هەمان لۆجیک دەمێنێتەوە — هەر if، هەر ژمارەیەک، هەر بانگێکی کتێبخانە. ئەو دەق و ناوانەی بەکارهێنەر دەیانبینێت ئەوانیش دەمێننەوە. ئەوەی فڕێ دەدرێت تەنیا بۆ مرۆڤ بوو: ، ناوی ، دێڕی بەتاڵ و ڕازان. لەبەر ئەوەیە شدەنییە: لۆجیکەکە هەمووی هێشتا لەوێیە، تەنیا خوێندنەوەی قورستر.
See it yourself: Python's disخۆت بیبینە: disـی Python
You do not need any special tool to meet . Python has a built-in module called dis (short for disassemble) that shows the bytecode of your own function. Here is a tiny, harmless program and its real output.
بۆ ناسینی پێویستت بە هیچ ئامرازێکی تایبەت نییە. Python مۆدیوڵێکی ناوەکیی هەیە بە ناوی dis (کورتکراوەی disassemble) کە خۆت پیشان دەدات. ئەمە بەرنامەیەکی بچووکی بێزیانە و دەرئەنجامە ڕاستەقینەکەی.
import dis

def shipping_cost(weight_kg):
    # Heavy parcels cost more.
    if weight_kg > 5:
        return 8000
    return 3000

print(shipping_cost(7))
dis.dis(shipping_cost)8000
3 RESUME 0
5 LOAD_FAST 0 (weight_kg)
LOAD_CONST 1 (5)
COMPARE_OP 148 (bool(>))
POP_JUMP_IF_FALSE 1 (to L1)
6 RETURN_CONST 2 (8000)
7 L1: RETURN_CONST 3 (3000)Explain the codeڕوونکردنەوەی کۆدەکە
- Lineدێڕی 9
First the program runs normally and prints 8000.
سەرەتا بەرنامەکە بە ئاسایی کار دەکات و 8000 چاپ دەکات.
- Lineدێڕی 10
dis.disprints the bytecode steps of the function.dis.disهەنگاوەکانی چاپ دەکات.
Read it like a recipe: LOAD_FAST weight_kg and LOAD_CONST 5 put your value and the number 5 ready; COMPARE_OP > compares them; POP_JUMP_IF_FALSE jumps to the second return when the test is false. Your comment and the line spacing are gone, but the if weight_kg > 5 logic is right there — anyone can read it back.
وەک ڕێسەتێک بیخوێنەوە: LOAD_FAST weight_kg و LOAD_CONST 5 بەهاکەت و ژمارە 5 ئامادە دەکەن؛ COMPARE_OP > بەراوردیان دەکات؛ POP_JUMP_IF_FALSE دەبازێتە سەر دووەم return کاتێک تاقیکردنەوەکە درۆیە. و بۆشاییی دێڕەکان نەماون، بەڵام لۆجیکی if weight_kg > 5 هەر لەوێیە — هەر کەسێک دەتوانێت بیخوێنێتەوە.
See it yourself: Java's javapخۆت بیبینە: javapـی Java
Java works the same way. You compile a .java file into a .class file of with javac, and the JDK comes with a tool, javap -c, that shows that bytecode. The lesson Inside a class file uses it on the Java track; here it shows how little a compiled file hides.
Java بە هەمان شێوە کار دەکات. .java بە javac کۆمپایل دەکەیت بۆ .classـی . JDK ئامرازێکی لەگەڵە، javap -c، کە ئەو پیشان دەدات. وانەی ناو فایلێکی class لە بەشی Javaدا بەکاری دەهێنێت؛ لێرە پیشان دەدات کە کۆمپایلکراو چەند کەم دەشارێتەوە.
public class Shipping {
    // Heavy parcels cost more.
    static int cost(int weightKg) {
        if (weightKg > 5) {
            return 8000;
        }
        return 3000;
    }

    public static void main(String[] args) {
        System.out.println(cost(7));
    }
}javac Shipping.java
javap -c ShippingCompiled from "Shipping.java"
public class Shipping {
static int cost(int);
Code:
0: iload_0
1: iconst_5
2: if_icmple 9
5: sipush 8000
8: ireturn
9: sipush 3000
12: ireturn
...
}if_icmple 9 means if the first value is less than or equal to 5, jump to line 9 (return 3000); otherwise sipush 8000 pushes 8000 and returns it. It is the same if (weightKg > 5) you wrote — only the word weightKg and your comment are gone. The compiled file is not a locked box.
if_icmple 9 واتە ئەگەر یەکەم بەها بچووکتر یان یەکسانی 5 بوو، بازبدە بۆ دێڕی 9 (return 3000)؛ ئەگەرنا sipush 8000 ژمارە 8000 دەخاتە سەرێ و دەیگەڕێنێتەوە. هەمان if (weightKg > 5)ـە کە نووسیت — تەنیا وشەی weightKg و نەماون. کۆمپایلکراو سندوقێکی قفڵکراو نییە.
Two ways to study: static and dynamicدوو ڕێگای لێکۆڵینەوە: ستاتیکی و داینامیکی
There are two big approaches, and analysts use them together.
دوو ڕێبازی گەورە هەن و شیکەرەوان پێکەوە بەکاریان دەهێنن.
- Static analysis — study the program without running it: read its bytes, its text and its (for example with
disorjavap). It is safe, because nothing runs. - Dynamic analysis — run the program in a safe, closed space and watch what it does: which it opens, what it sends on the , how changes.
- — لێکۆڵینەوە لە بەرنامەکە بەبێ جێبەجێکردنی: خوێندنەوەی بایتەکانی، دەقەکەی و (بۆ نموونە بە
disیانjavap). سەلامەتە، چونکە هیچ جێبەجێ نابێت. - — بەرنامەکە لە شوێنێکی سەلامەتی داخراودا جێبەجێ بکە و تەماشا بکە چی دەکات: کام دەکاتەوە، چی لەسەر دەنێرێت، چۆن دەگۆڕێت.
The tool categoriesپۆلەکانی ئامراز
Reverse engineers group their tools into a few kinds. You do not need to know any one product — just what each kind is for. The examples below are well-known free tools, checked on their official pages in 2026.
کەسانی ئامرازەکانیان دەکەنە چەند جۆرێک. پێویست ناکات هیچ بەرهەمێکی تاکە بناسیت — تەنیا ئەوەی هەر جۆرێک بۆ چییە. ئەم نموونانەی خوارەوە ئامرازی بێبەرانبەری ناسراون، کە لە 2026دا لەسەر لاپەڕە فەرمییەکانیان پشکنراون.
| Categoryپۆل | What it doesچی دەکات | Free exampleنموونەی بێبەرانبەر |
|---|---|---|
| Turns or into readable . یان دەکات بە خوێندراو. | radare2 | |
| Rebuilds higher-level, C-like code from the compiled form.کۆدی ئاستبەرزتری هاوشێوەی C لە فۆرمە کۆمپایلکراوەکەوە دروست دەکاتەوە. | Ghidra | |
| Pauses a running program at a and steps through it.بەرنامەیەکی کارکەر لە ڕادەگرێت و هەنگاو بە هەنگاو دەیبات. | x64dbg | |
| Runs a program safely in a closed space to watch its behaviour.بەرنامەیەک بە سەلامەتی لە شوێنێکی داخراودا جێبەجێ دەکات بۆ بینینی ڕەفتاری. | an isolated VM جیاکراوە | |
| Network monitorچاودێری | Shows the a program sends and receives.ئەو بەرنامەیەک دەینێرێت و وەریدەگرێت پیشان دەدات. | Wireshark |
Malware analysis: reverse engineering for defendersشیکاریی نەرمەواڵەی زیانبەخش: ئەندازیاریی پێچەوانە بۆ بەرگریکەران
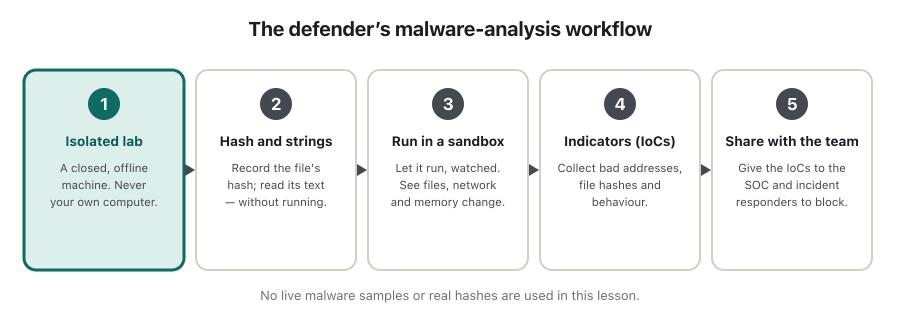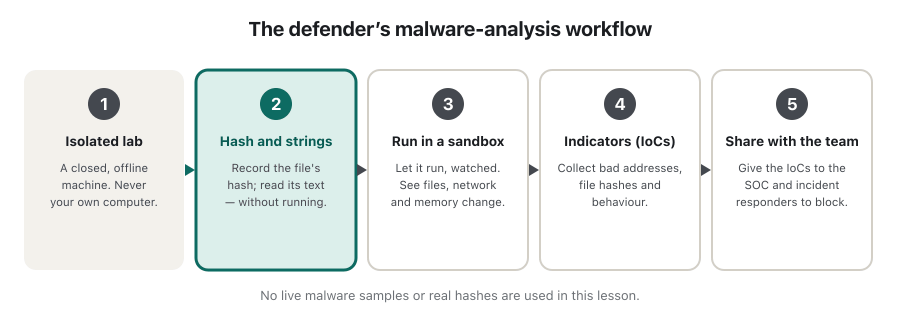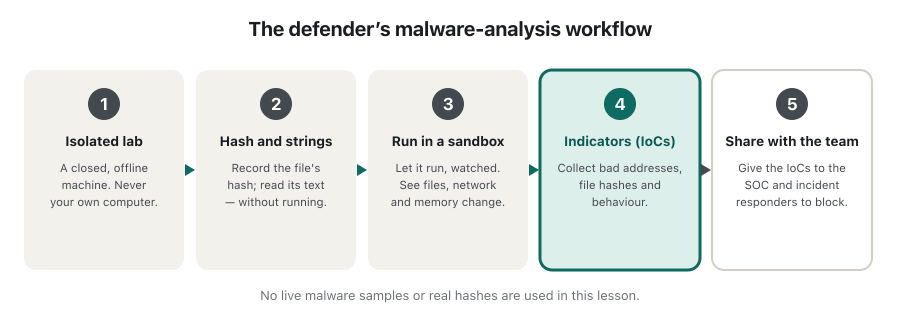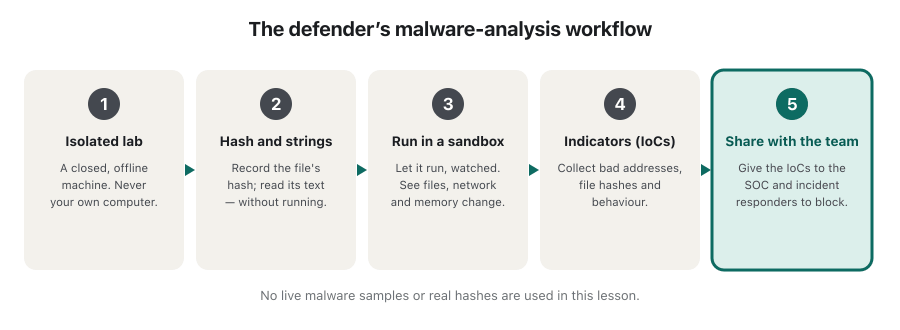
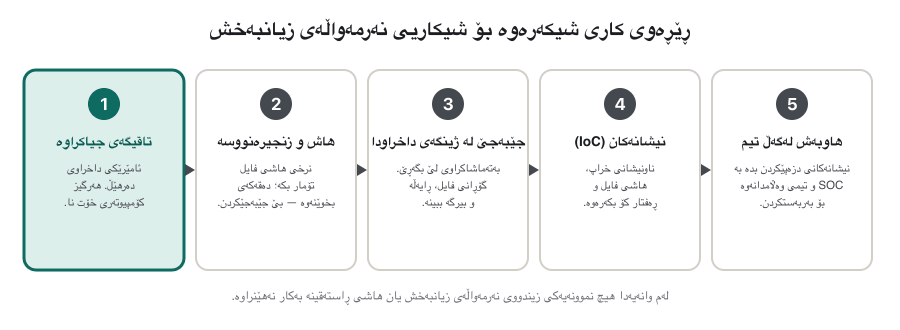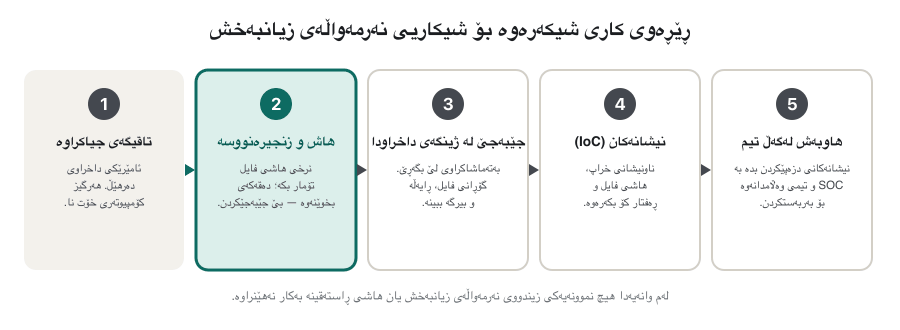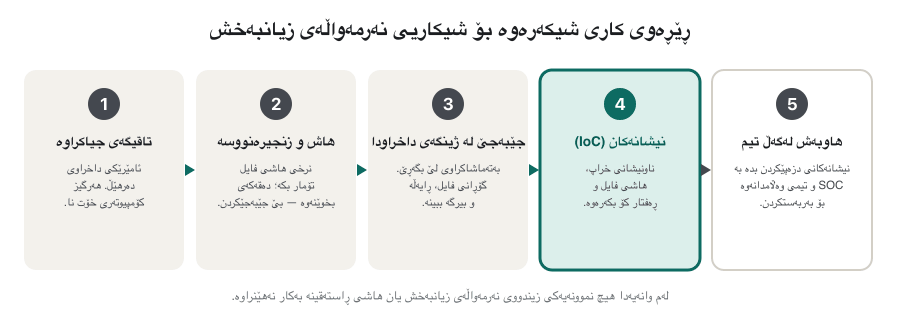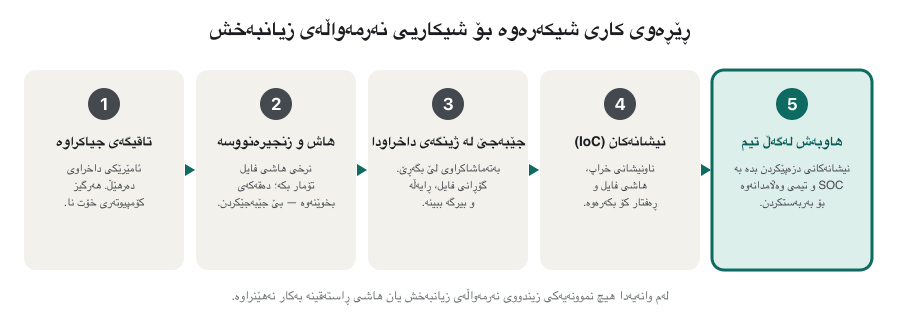
The most common defensive use is malware analysis. When new appears, defenders take it apart to learn what it does, so they can detect and remove it. They never run it on their own computer — only in an isolated lab. This lesson uses no real samples and no real hashes.
باوترین بەکارهێنانی بەرگریکارانە . کاتێک نوێ دەردەکەوێت، بەرگریکەران لێکی دەدەنەوە بۆ زانینی ئەوەی چی دەکات، تاکو بتوانن بیدۆزنەوە و لایببەن. هەرگیز لەسەر خۆیان جێبەجێی ناکەن — تەنیا لە تاقیگەیەکی جیاکراوەدا. ئەم وانەیە هیچ نموونەیەکی ڕاستەقینەی و هیچ هاشی ڕاستەقینە بەکار ناهێنێت.
Every file has a fingerprint: its . The same file always gives the same hash, so analysts record a file's hash to recognise it later. Here is the harmless Shipping.class from before:
هەر فایلێک پەنجەمۆرێکی هەیە: . هەمان فایل هەمیشە هەمان هاش دەداتەوە، بۆیە شیکەرەوان هاشی فایلێک تۆمار دەکەن بۆ ناسینەوەی دواتر. ئەمە Shipping.classـی بێزیانی پێشووە:
shasum -a 256 Shipping.class24d39378199cf46b947941a3a83be04e1366ef5edfe706def14d4f4b5b41ce4c Shipping.class
Analysts share such fingerprints, bad and other clues as (IoCs), so other teams can block the same attack. The IoCs go to the people who act on them — see Triage and indicators of compromise and the Security operations centre.
شیکەرەوان ئەم پەنجەمۆرانە، خراپ و بەڵگەی تر وەک (IoC) هاوبەش دەکەن، بۆ ئەوەی تیمەکانی تر هەمان هێرش بەربەست بکەن. ئەم دەگەنە دەست ئەو کەسانەی کاریان لەسەر دەکەن — بڕوانە هەڵسەنگاندنی سەرەتایی و نیشانەکانی دزەپێکردن و ناوەندی کارەکانی ئاسایش.
Obfuscation and packingناڕوونکردنی کۆد و پێچانەوە
Because compiled code can be read, people try to make it harder. changes a program on purpose so it still works the same but is hard to read — for example by renaming everything to short, meaningless names. Packing compresses or encrypts the program and wraps it in a tiny starter that unpacks the real program in when it runs.
لەبەر ئەوەی کۆدی کۆمپایلکراو دەخوێندرێتەوە، خەڵک هەوڵ دەدەن قورستری بکەن. بەرنامەیەک بە ئەنقەست دەگۆڕێت بۆ ئەوەی هەر وەک خۆی کار بکات بەڵام خوێندنەوەی قورس بێت — بۆ نموونە بە گۆڕینی هەموو ناوێک بۆ ناوی کورت و بێمانا. پێچانەوە بەرنامەکە دەپەستێنێت یان شفرە دەکات و لە دەستپێکەرێکی بچووکدا دەیپێچێتەوە کە لە کاتی کارکردندا بەرنامە ڕاستەقینەکە لە دەکاتەوە.
Both sides use these. App makers obfuscate to make apps smaller and to make their work harder to copy — Android's R8 shortens names like com.example.MyActivity to a.b.a. Attackers pack so a will not match. But neither one makes a secret safe: they only slow an analyst down, and a still sees what a packed program does when it runs.
هەردوو لا بەکاریان دەهێنن. دروستکەران دەکەن بۆ بچووککردنەوەی و قورسکردنی لەبەرگرتنەوەی کارەکەیان — R8ـی Android ناوی وەک com.example.MyActivity کورت دەکاتەوە بۆ a.b.a. دەپێچنەوە بۆ ئەوەی نەیگرێتەوە. بەڵام هیچیان نهێنی سەلامەت ناکەن: تەنیا شیکەرەوە خاو دەکەنەوە و هێشتا دەبینێت بەرنامەیەکی پێچراو لە کاتی کارکردندا چی دەکات.
The law and ethicsیاسا و ئەخلاق
Reverse engineering a program is legal in many cases, but within limits, and the limits differ by country. Two well-known laws show the pattern (checked in 2026).
بەرنامەیەک لە زۆر حاڵەتدا یاساییە، بەڵام لە چوارچێوەدا. چوارچێوەکان لە وڵاتێکەوە بۆ وڵاتێکی تر دەگۆڕێن. دوو یاسای ناسراو شێوازەکە پیشان دەدەن (لە 2026دا پشکنراون).
- European Union — Directive 2009/24/EC. You may study how a program works while you use it (Article 5(3)), and you may decompile it as far as needed to achieve with another program (Article 6). A contract cannot take these rights away (Article 8).
- United States — DMCA, 17 U.S.C. §1201. It allows reverse engineering for (§1201(f)) and good-faith security testing (§1201(j)). A 2024 rule also gives an exemption for good-faith security research.
- یەکێتیی ئەوروپا — ئاراستەی 2009/24/EC. دەتوانیت لە کاتی بەکارهێنانی بەرنامەیەکدا لێی بکۆڵیتەوە چۆن کار دەکات (ماددەی 5(3)). هەروەها دەتوانیت بەو ئەندازەی بۆ گەیشتن بە لەگەڵ بەرنامەیەکی تر پێویستە دیکۆمپایلی بکەیت (ماددەی 6). گرێبەست ناتوانێت ئەم مافانە بسڕێتەوە (ماددەی 8).
- ئەمریکا — DMCA، 17 U.S.C. §1201. ڕێگە دەدات بە بۆ (§1201(f)) و تاقیکردنەوەی بە نیەتپاک (§1201(j)). ڕێسایەکی 2024ـیش بەدەرکراوێک بۆ توێژینەوەی بە نیەتپاک دەدات.
Three rules keep you safe. First, read the program's licence (the EULA) — it may forbid reverse engineering, and a licence often adds rules the law does not. Second, check the law where you live: Iraq and the Kurdistan Region have their own rules (see Computer-crime laws), and nobody should guess them. Third, never cross into cracking software, bypassing a licence or digital rights protection (DRM), or attacking a system you do not own.
سێ ڕێسا سەلامەتت دەکەن. یەکەم، (EULA) بەرنامەکە بخوێنەوە — لەوانەیە قەدەغەی بکات و مۆڵەت زۆرجار ڕێسایەک زیاد دەکات کە یاسا نایکات. دووەم، یاسای شوێنی خۆت بپشکنە: عێراق و هەرێمی کوردستان یاسای خۆیانیان هەیە (بڕوانە یاساکانی تاوانی سایبەری) و کەس نابێت مەزەندەیان بکات. سێیەم، هەرگیز مەچۆرە ناو شکاندنی ، تێپەڕاندنی مۆڵەت یان پاراستنی مافی دیجیتاڵی (DRM)، یان هێرشکردنە سەر سیستەمێک کە هی تۆ نییە.
Why hiding the design does not protect itبۆچی شاردنەوەی دیزاین ناپارێزێتی
Reverse engineering explains an important security rule. Anything you send to the user's device — an , a game, a file — can be copied and taken apart. So a secret hidden inside the thing the user holds is not safe: a skilled person can read it back. Trusting such a hidden secret is called , and on its own it fails.
ڕێسایەکی گرنگی ڕوون دەکاتەوە. هەر شتێک کە بۆ ئامێری بەکارهێنەر دەنێریت — ، یارییەک، فایلێک — دەکرێت کۆپی بکرێت و لێک بدرێتەوە. بۆیە نهێنییەک کە لە ناو ئەو شتەدا شاردراوەتەوە کە بەکارهێنەر هەڵیدەگرێت سەلامەت نییە: کەسێکی شارەزا دەتوانێت بیخوێنێتەوە. متمانەکردن بەم نهێنییە شاراوەیە پێی دەوترێت و بە تەنیا شکست دەهێنێت.
The fix is not to hide harder, but to put secrets and important decisions on a you control, and to use open, tested where only the key is secret. Security Principles teaches this rule in full; reverse engineering is the reason it is true.
چارەسەرەکە ئەوە نییە کە زیاتر بیشاریتەوە، بەڵکو نهێنی و بڕیارە گرنگەکان بخەیتە سەر کە کۆنترۆڵی دەکەیت و کراوە و تاقیکراوە بەکار بهێنیت کە تەنیا کلیلەکەی نهێنییە. بنەماکانی ئاسایش ئەم ڕێسایە بە تەواوی دەڵێتەوە؛ ئەو هۆیەیە کە وای دەکات ڕاست بێت.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| "Reverse engineering is always illegal."« هەمیشە نایاساییە.» | It is a normal engineering skill; many uses are lawful, within limits.کارامەییەکی ئاسایی ئەندازیارییە؛ زۆر بەکارهێنان یاسایین، لە چوارچێوەدا. | Learn the limits: read the licence and check the law where you live.چوارچێوەکان فێر ببە: مۆڵەتەکە بخوێنەوە و یاسای شوێنی خۆت بپشکنە. |
| "Compiling my app keeps the code secret."«کۆمپایلکردنی کۆدەکە نهێنی دەهێڵێتەوە.» | The logic, text and library calls all survive compiling; only comments and names are lost.لۆجیک، دەق و بانگی کتێبخانە هەموویان لە کۆمپایلکردندا دەمێننەوە؛ تەنیا و ناوەکان لەدەست دەچن. | Keep secrets and key decisions on a server, not in the app.نهێنی و بڕیارە سەرەکییەکان لەسەر بهێڵەوە، نەک لە . |
| "Obfuscation makes my secret safe."« نهێنییەکەم سەلامەت دەکات.» | It only slows a reader down; a and patience still reveal the behaviour.تەنیا خوێنەر خاو دەکاتەوە؛ و ئارامگرتن هێشتا ڕەفتارەکە دەردەخەن. | Use obfuscation as an extra layer only, never as the real protection. تەنیا وەک چینێکی زیادە بەکار بهێنە، هەرگیز وەک پاراستنی ڕاستەقینە نا. |
| Running an unknown program to "see what it does".جێبەجێکردنی بەرنامەیەکی نەناسراو بۆ «بینینی ئەوەی چی دەکات». | It may be malware and can harm your computer and your data.لەوانەیە بێت و زیان بە و بگەیەنێت. | Do dynamic analysis only in an isolated, offline . تەنیا لە جیاکراوی دەرهێڵدا بکە. |
| Testing someone else's app or website without asking.تاقیکردنەوەی یان کەسێکی تر بەبێ پرسین. | Without written permission it can be a crime, even with good intentions.بەبێ مۆڵەتی نووسراو دەکرێت تاوان بێت، تەنانەت بە نیازی باشیشەوە. | Get written permission, or report through responsible disclosure.مۆڵەتی نووسراو وەربگرە، یان لە ڕێگەی ڕاپۆرتی بکە. |
Exercisesڕاهێنانەکان
For each task, say whether it is static analysis or dynamic analysis: (a) reading a program's bytecode with javap -c; (b) running an unknown file in a and watching which it contacts; (c) searching a file's text for web addresses without running it.
بۆ هەر ئەرکێک، بڵێ ئایا یان : (أ) خوێندنەوەی بەرنامەیەک بە javap -c؛ (ب) جێبەجێکردنی نەناسراو لە و بینینی ئەوەی پەیوەندی بە کام دەکات؛ (ج) گەڕان بەدوای ناونیشانی وێب لە دەقی فایلێکدا بەبێ جێبەجێکردنی.
Show answerوەڵامەکە پیشان بدە
- (a) Static — you read the code without running it.
- (b) Dynamic — the file runs and you watch its behaviour.
- (c) Static — searching the text without running the file is static analysis.
- (أ) — کۆدەکە دەخوێنیتەوە بەبێ جێبەجێکردنی.
- (ب) — فایلەکە جێبەجێ دەبێت و ڕەفتاری دەبینیت.
- (ج) — گەڕان بەناو دەقەکەدا بەبێ جێبەجێکردنی فایلەکە .
Which of these is a responsible, lawful use of reverse engineering, and which is not? (a) decompiling a file format so your own program can open it; (b) a security team studying a device, with the owner's written permission, to find weaknesses; (c) removing a paid app's licence check so you can use it free.
کامیان بەکارهێنانێکی بەرپرسیارانە و یاساییی ، کامیان نا؟ (أ) دیکۆمپایلکردنی فۆرماتی فایلێک بۆ ئەوەی بەرنامەکەی خۆت بتوانێت بیکاتەوە؛ (ب) تیمێکی کە بە مۆڵەتی نووسراوی خاوەنەکە لە ئامێرێک دەکۆڵێتەوە بۆ دۆزینەوەی لاوازی؛ (ج) لابردنی پشکنینی مۆڵەتی پارەدراو بۆ ئەوەی بەخۆڕایی بەکاری بهێنیت.
Hintئاماژە
Ask: is it for interoperability or defence, with permission — or does it break a licence?
بپرسە: ئایا بۆ یان بەرگرییە، بە مۆڵەت — یان مۆڵەتێک دەشکێنێت؟
Show answerوەڵامەکە پیشان بدە
- (a) Responsible — reverse engineering for is a classic, lawful use (as EU Directive 2009/24/EC allows).
- (b) Responsible — with the owner's written permission, this is security testing, close to .
- (c) Not allowed — removing a licence check to use software for free breaks the licence and the law. This lesson never shows how to do it.
- (أ) بەرپرسیارانە — بۆ بەکارهێنانێکی کلاسیکی و یاساییە (وەک ئاراستەی ئەوروپی 2009/24/EC ڕێگەی دەدات).
- (ب) بەرپرسیارانە — بە مۆڵەتی نووسراوی خاوەنەکە، ئەمە تاقیکردنەوەی ، نزیک لە .
- (ج) ڕێپێنەدراو — لابردنی پشکنینی مۆڵەت بۆ بەکارهێنانی بە خۆڕایی مۆڵەتەکە و یاساکە دەشکێنێت. ئەم وانەیە هەرگیز پیشان نادات چۆن دەکرێت.
Write a three-line Python function of your own and run dis.dis on it, as in the lesson. Find the bytecode step that loads a number you used. Then explain, in one sentence, why your comment does not appear in the output.
سێ دێڕی Pythonـی خۆت بنووسە و dis.disـی لەسەر جێبەجێ بکە، وەک لە وانەکەدا. ئەو هەنگاوەی بدۆزەرەوە کە ژمارەیەکی بەکارهێنراوت بار دەکات. پاشان بە ڕستەیەک ڕوون بکەرەوە بۆچی لە دەرئەنجامەکەدا دەرناکەوێت.
Show answerوەڵامەکە پیشان بدە
A number is loaded by a LOAD_CONST step (for example LOAD_CONST 5). Your comment does not appear because comments are only for humans: the drops them, so they are never part of the .
ژمارەیەک بە هەنگاوی LOAD_CONST بار دەکرێت (بۆ نموونە LOAD_CONST 5). دەرناکەوێت چونکە تەنیا بۆ مرۆڤن: فڕێیان دەدات، بۆیە هەرگیز بەشێک لە نین.
Summaryپوختە
- Reverse engineering means studying a finished product to learn how it works — the opposite of forward engineering.
- It is used for , finding weaknesses, , recovering lost and checking what an app sends.
- Compiling keeps the logic and drops only comments and names, so tools like
disandjavap -cread the bytecode back. - Static analysis reads a program without running it; dynamic analysis runs it in a and watches it.
- The tool categories are disassemblers, decompilers, debuggers, sandboxes and network monitors — free examples include Ghidra, radare2, x64dbg and Wireshark.
- Defenders analyse malware safely in an isolated lab and share ; obfuscation and packing only slow analysts down.
- Reverse engineering is legal within limits that differ by country: read the licence, check the law where you live, and report weaknesses responsibly. Because anything on the user's device can be read, security by obscurity fails.
- واتە لێکۆڵینەوە لە بەرهەمێکی تەواوکراو بۆ زانینی چۆنیەتیی کارکردنی — پێچەوانەی .
- بۆ ، دۆزینەوەی لاوازی، ، گەڕاندنەوەی ونبوو و پشکنینی ئەوەی دەینێرێت بەکار دێت.
- کۆمپایلکردن لۆجیک دەهێڵێتەوە و تەنیا و ناوەکان فڕێ دەدات، بۆیە ئامرازی وەک
disوjavap -cدەخوێننەوە. - بەرنامەیەک دەخوێنێتەوە بەبێ جێبەجێکردنی؛ لە جێبەجێی دەکات و تەماشای دەکات.
- پۆلەکانی ئامراز ، ، ، و چاودێری — نموونەی بێبەرانبەر Ghidra، radare2، x64dbg و Wireshark لەخۆ دەگرن.
- بەرگریکەران بە سەلامەتی لە تاقیگەیەکی جیاکراوەدا شی دەکەنەوە و هاوبەش دەکەن؛ و پێچانەوە تەنیا شیکەرەوان خاو دەکەنەوە.
- لە چوارچێوەیەکدا یاساییە کە بە وڵات دەگۆڕێت: مۆڵەتەکە بخوێنەوە، یاسای شوێنی خۆت بپشکنە و لاوازییەکان بە بەرپرسیارانە ڕاپۆرت بکە. لەبەر ئەوەی هەر شتێک لەسەر ئامێری بەکارهێنەر دەخوێندرێتەوە، شکست دەهێنێت.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
Related lecturesوانە پەیوەندیدارەکان
- Malware Today: Infostealers, Banking Trojans, RATs, Cryptojacking and Moreنەرمەواڵەی زیانبەخشی ئەمڕۆ: نەرمەواڵە زانیاریدزەکان، ئەسپەکانی ترۆیای بانکی، RAT، کریپتۆجاکینگ و زیاتر
- Ransomware: WannaCry, NotPetya and Recent Attacksبارمتەواڵە: WannaCry، NotPetya و هێرشە نوێیەکان
- Security by Obscurity, by Legislation, and the Trade-off Triangleئاسایش بە شاردنەوە، ئاسایش بە یاسا و سێگۆشەی هاوسەنگی
- Incident Response: Six Phasesوەڵامدانەوەی ڕووداو: شەش قۆناغ
- Security Operations Centres and Threat Huntingناوەندی کارەکانی ئاسایش و ڕاوکردنی هەڕەشە
- Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
- Cyber Ethics and Ethical Hackingئەخلاقی سایبەری و هاککردنی ئەخلاقی
- Computer-Crime Laws: Budapest, the CFAA, the UK and the Law at Homeیاساکانی تاوانی سایبەری: بوداپێست، CFAA، بەریتانیا و یاسا لە وڵاتی خۆمان
- Intellectual Property, Plagiarism and Software Licencesموڵکی هزری، دزیی زانستی و مۆڵەتەکانی بەکارهێنان
- Compiling and Running: javac, Bytecode and the JVMکۆمپایلکردن و جێبەجێکردن: javac، بایتکۆد و ئامێری گریمانەیی Java
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- Ghidra (NSA): software reverse engineering framework, Apache 2.0
- Ghidra (Wikipedia): released at RSA Conference, March 2019; decompiler, Apache 2.0
- radare2 (GitHub): UNIX-like reverse-engineering framework, LGPLv3
- x64dbg: open-source (GPLv3) debugger for Windows
- Wireshark: about the network protocol analyzer
- Python docs: the dis module (CPython bytecode disassembler)
- Oracle: the javap command (Java 17)
- EU Directive 2009/24/EC on the legal protection of computer programs (Art. 5(3), 6, 8)
- 17 U.S.C. §1201: circumvention, reverse engineering (f) and security testing (j)
- 37 CFR §201.40: DMCA exemptions, incl. good-faith security research (b)(18)
- US Copyright Office: Section 1201 rulemaking (2024 final rule; tenth proceeding under way)
- CISA: Malware Next-Generation Analysis (static and dynamic analysis, STIX IoCs)
- MITRE ATT&CK T1027.002: Software Packing (UPX, VMProtect, Themida)
- Android developers: shrink, obfuscate and optimize with R8
- OWASP Mobile Top 10 (2023) M7: Insufficient Binary Protection
- OWASP MASVS-RESILIENCE: obfuscation must not replace proper security architecture
- NIST CSRC Glossary: sandbox
- Umeå University: Reverse Engineering (5DV240) course syllabus (static/dynamic analysis, obfuscation, malware/firmware)
- Samba (Wikipedia): 1992 origins, SMB learned by watching network traffic (interoperability)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.