Chapterبەش 3 · Lectureوانە 3.2
Cyber Ethics and Ethical Hackingئەخلاقی سایبەری و هاککردنی ئەخلاقی
What is right, what is legal, and what to do when they differ. Cyber ethics; ethical hacking and penetration testing, always with written permission and a clear scope; white-, black- and grey-hat hackers; the codes of ethics of EC-Council, ISC2 and ACM; the law on testing without permission; and the MyFitnessPal case for discussion.
چی ڕاستە، چی یاساییە و چی بکەین کاتێک ئەم دووانە جیاوازن. ؛ و ، هەمیشە بە مۆڵەتی نووسراو و سنوورێکی ڕوون؛ ، و ؛ یاسا ئەخلاقییەکانی EC-Council، ISC2 و ACM؛ یاسا دەربارەی تاقیکردنەوە بەبێ مۆڵەت؛ و نموونەی MyFitnessPal بۆ گفتوگۆ.
What you will learnچی فێر دەبیت
- Tell an ethical question from a legal one, and explain why a security professional needs both.
- Explain what makes hacking ethical, and list what a penetration-test authorisation contains.
- Compare white-, black- and grey-hat hackers, and say why a grey hat's testing is usually illegal.
- Summarise the EC-Council, ISC2 and ACM codes of ethics and apply them to everyday cases.
- پرسیاری ئەخلاقی لە پرسیاری یاسایی جیا بکەیتەوە و ڕوونی بکەیتەوە بۆچی پسپۆڕی پێویستی بە هەردووکیانە.
- ڕوونی بکەیتەوە چی هاککردن دەکاتە ئەخلاقی و ئەو شتانە بژمێریت کە ڕێگەپێدانی تێیدایە.
- ، و بەراورد بکەیت و بڵێیت بۆچی تاقیکردنەوەی کڵاو خۆڵەمێشی زۆرجار نایاساییە.
- یاسا ئەخلاقییەکانی EC-Council، ISC2 و ACM کورت بکەیتەوە و لەسەر نموونەی ڕۆژانە جێبەجێیان بکەیت.
Right, legal, or both?ڕاستە، یاساییە یان هەردووکیان؟
This lesson continues the chapter on ethics and law, which opens with Digital citizenship. The lecture's subtitle says what the chapter is about: navigating the intersection of morality and law in the digital realm. In plain words: finding your way at the place where right and wrong meet what the law allows, on computers and networks.
ئەم وانەیە بەشی ئەخلاق و یاسا درێژە پێدەدات، کە بە هاووڵاتیبوونی دیجیتاڵی دەست پێ دەکات. ناونیشانی لاوەکیی وانەکە دەڵێت ئەم بەشە دەربارەی چییە: ڕێگەدۆزینەوە لەو شوێنەی ئەخلاق و یاسا لە جیهانی دیجیتاڵیدا یەکتر دەگرنەوە. بە زمانێکی سادە: زانینی ڕێگەی دروست لەو خاڵەی چاکە و خراپە لەگەڵ ئەوەی یاسا ڕێگەی پێ دەدات لە و بەیەک دەگەن.
Many cybersecurity challenges have ethical and legal implications. An implication is a possible later effect of an action or a decision. So before acting, a security professional asks two separate questions:
زۆرێک لە بەربەستەکانی کاریگەریی ئەخلاقی و یاساییان هەیە. «کاریگەری» لێرەدا واتە ئەنجامێکی ئەگەریی کارێک یان بڕیارێک لە داهاتوودا. بۆیە پسپۆڕی پێش ئەوەی کارێک بکات دوو پرسیاری جیاواز دەکات:
- Ethical: Is it right? For example: is it right to collect people's personal information in order to improve security?
- Legal: Does the law allow it? For example: do our security measures break any law, such as a data-protection law?
- ئەخلاقی: ئایا ڕاستە؟ بۆ نموونە: ئایا دروستە زانیاریی کەسیی خەڵک کۆ بکەینەوە بۆ ئەوەی باشتر بکەین؟
- یاسایی: ئایا یاسا ڕێگەی پێ دەدات؟ بۆ نموونە: ئایا ڕێکارەکانی ئێمە هیچ یاسایەک دەشکێنن، وەک یاسایەکی ؟
Professionals must deal with these challenges carefully: they protect users and, at the same time, they comply with the law. To comply means to do what you have to do, or what you are asked to do.
پسپۆڕانی ئەم بوارە دەبێت بە وریاییەوە مامەڵە لەگەڵ ئەم بەربەستانەدا بکەن: دەپارێزن و لە هەمان کاتدا پێچەوانەی یاسا ناکەن. «comply» واتە ئەو کارە بکەیت کە دەبێت بیکەیت، یان داوات لێ کراوە بیکەیت.
When ethics and law disagreeکاتێک ئەخلاق و یاسا یەک ناگرنەوە
The two questions do not always give the same answer. The table shows the four possible mixes.
ئەم دوو پرسیارە هەمیشە یەک وەڵامیان نییە. خشتەکە چوار تێکەڵەی ئەگەری پیشان دەدات.
| Situationدۆخ | Ethical?ئەخلاقییە؟ | Legal?یاساییە؟ |
|---|---|---|
| A company's own security team tests its servers with written permissionتیمی کۆمپانیایەک بە مۆڵەتی نووسراو خۆی تاقی دەکاتەوە | Yesبەڵێ | Yesبەڵێ |
| An app collects far more data about its users than it needs, in a country with no data-protection law زۆر زیاتر لە پێویست دەربارەی کۆ دەکاتەوە، لە وڵاتێکدا کە یاسای نییە | Doubtfulگوماناوی | Yes, thereبەڵێ، لەوێ |
| A student tests a stranger's website for holes 'to help', without askingخوێندکارێک بەبێ پرسین کەسێکی نەناسراو بۆ دۆزینەوەی کون تاقی دەکاتەوە «بۆ یارمەتیدان» | Good intent, wrong methodنیازی باش، ڕێگەی هەڵە | Noنەخێر |
| Someone sells stolen passwordsکەسێک دزراو دەفرۆشێت | Noنەخێر | Noنەخێر |
Why both matter: trust and penaltiesبۆچی هەردووکیان گرنگن: متمانە و سزا
The notes give one short reason for each side: ethical behaviour builds trust, and legal adherence avoids penalties. If a company protects its users' privacy, the users trust it. Legal adherence means being law-abiding: following the law in what you do.
تێبینییەکان بۆ هەر لایەک هۆیەکی کورت دەدەن: ڕەفتاری ئەخلاقی متمانە دروست دەکات و ڕێ لە سزا دەگرێت. ئەگەر کۆمپانیایەک خۆی بپارێزێت، متمانەی پێ دەکەن. «legal adherence» واتە یاساپەروەری: کارەکانت بەپێی یاسا بن.
The lecture's example is a hard one: a company deciding whether to disclose (reveal) a breach, or to keep quiet and risk damage to its name. Imagine a mobile operator, Aram Mobile, whose customer database is stolen. It has two choices:
نموونەی وانەکە نموونەیەکی قورسە: کۆمپانیایەک بڕیار دەدات ئاشکرا بکات، یان بێدەنگ بێت و ناوبانگی بخاتە مەترسییەوە. وا دابنێ کۆمپانیایەکی مۆبایل بە ناوی ئارام مۆبایل کڕیارەکانی دزراوە. دوو ڕێگەی لەبەردەمدایە:
- Tell the customers now. The news hurts its name today, but customers can change their passwords, watch their accounts and stop using the service until it is safe.
- Stay silent. Customers are harmed without knowing it, and when the truth comes out later they stop trusting the company completely.
- ئێستا کڕیاران ئاگادار بکاتەوە. هەواڵەکە ئەمڕۆ زیان بە ناوبانگی دەگەیەنێت، بەڵام کڕیاران دەتوانن خۆیان بگۆڕن، چاودێریی هەژمارەکانیان بکەن و تا سەلامەت دەبێتەوە خزمەتگوزارییەکە بەکار نەهێنن.
- بێدەنگ بێت. کڕیاران بێ ئەوەی بزانن زیانیان پێ دەگات و کاتێک دواتر ڕاستییەکە دەردەکەوێت، بە تەواوی متمانەیان بە کۆمپانیاکە نامێنێت.
Ethics points to the first choice. In many places the law does too: Europe's GDPR and the United States' HIPAA set deadlines for telling the authorities and the people affected. You will meet those rules in Europe's GDPR and HIPAA and China's laws.
ئەخلاق ڕێگەی یەکەم پیشان دەدات. لە زۆر شوێن یاساش هەمان شت دەڵێت: ئەوروپا و ئەمریکا ماوەی دیاریکراو دادەنێن بۆ ئاگادارکردنەوەی دەسەڵاتداران و ئەو کەسانەی زیانیان پێ گەیشتووە. ئەم ڕێسایانە لە GDPRـی ئەوروپا و HIPAA و یاساکانی چین دەبینیت.
Cyber ethicsئەخلاقی سایبەری
The moral principles that guide how people and organisations behave in the digital world, for example respecting and and not misusing technical power. Something can be legal and still be unethical.
ئەو بنەما ئەخلاقییانەن کە ڕەفتاری خەڵک و دامەزراوەکان لە جیهانی دیجیتاڵیدا ڕێنمایی دەکەن، بۆ نموونە ڕێزگرتن لە و و خراپ بەکارنەهێنانی دەسەڵاتی تەکنیکی. شتێک دەکرێت یاسایی بێت و هێشتا نائەخلاقی بێت.
The notes define cyber ethics as the moral principles that guide individuals and organisations in the digital world. It deals with topics such as:
تێبینییەکان بەم شێوەیە دەناسێنن: ئەو بنەما ڕەوشتییانەی ڕێنمایی تاک و ڕێکخراوەکان دەکەن لە جیهانی دیجیتاڵیدا. مامەڵە لەگەڵ بابەتی وەک ئەمانەدا دەکات:
- Online privacy: whose data is it, who may see it, and for what purpose?
- Intellectual property theft: copying someone else's creations of the mind (source code, designs, inventions, music, brand names) without permission. See What is intellectual property? and Plagiarism and infringement.
- Ethical hacking: using attackers' skills to protect, with permission (the next screen).
- لە سەرهێڵدا: هی کێیە، کێ دەتوانێت بیبینێت و بۆ چ مەبەستێک؟
- دزینی : لەبەرگرتنەوەی داهێنانی هزریی کەسێکی تر (، دیزاین، داهێنان، مۆسیقا، ناوی بازرگانی) بەبێ مۆڵەت. بڕوانە موڵکی هزری چییە؟ و دزیی زانستی و پێشێلکردن.
- : بەکارهێنانی شارەزایی بۆ پاراستن، بە مۆڵەت (پەردەی داهاتوو).
The notes' example: choosing not to use malware tools, even if they could help your personal research. Why say no? Tools from criminal markets often support criminals, may hide malware that infects you, and the EC-Council code tells members not to use software obtained illegally or unethically. Learn with legal practice labs and well-known open tools, on machines you own.
نموونەی تێبینییەکان: بڕیاردان بە بەکارنەهێنانی ئامرازەکانی ، تەنانەت ئەگەر سوودیان بۆ توێژینەوەی کەسیت هەبێت. بۆچی «نا»؟ ئامرازەکانی بازاڕی تاوانکاران زۆرجار پاڵپشتی تاوانکاران دەکەن، لەوانەیە تێدا شاردرابێتەوە کە خۆت تووش دەکات و یاسای ئەخلاقیی EC-Council بە ئەندامەکانی دەڵێت ئەو بەکار نەهێنن کە بە شێوەی نایاسایی یان نائەخلاقی بەدەست هاتووە. لە تاقیگەی ڕاهێنانی یاسایی و ئامرازی کراوەی ناسراودا فێربە، لەسەر ئەو ئامێرانەی خۆت خاوەنیانیت.
Ethical hackingهاککردنی ئەخلاقی
Testing a system's defences with the owner's written permission, using the same methods as attackers, to find and recommend fixes before criminals find them.
تاقیکردنەوەی بەرگرییەکانی سیستەمێکە بە مۆڵەتی نووسراوی خاوەنەکەی و بە هەمان ڕێگاکانی ، بۆ دۆزینەوەی و پێشنیارکردنی چارەسەر پێش ئەوەی تاوانباران بیاندۆزنەوە.
Ethical hacking is the authorised testing of a system's defences to find its vulnerabilities and to recommend fixes. It is a proactive approach: you act in advance, before malicious attackers find the same holes.
تاقیکردنەوەی ڕێگەپێدراوی بەرگرییەکانی سیستەمێکە بۆ دۆزینەوەی و پێشنیارکردنی چارەسەر. ڕێگەیەکی پێشوەختەیە (proactive): پێش ئەوەی هەمان کون بدۆزنەوە، تۆ کار دەکەیت.
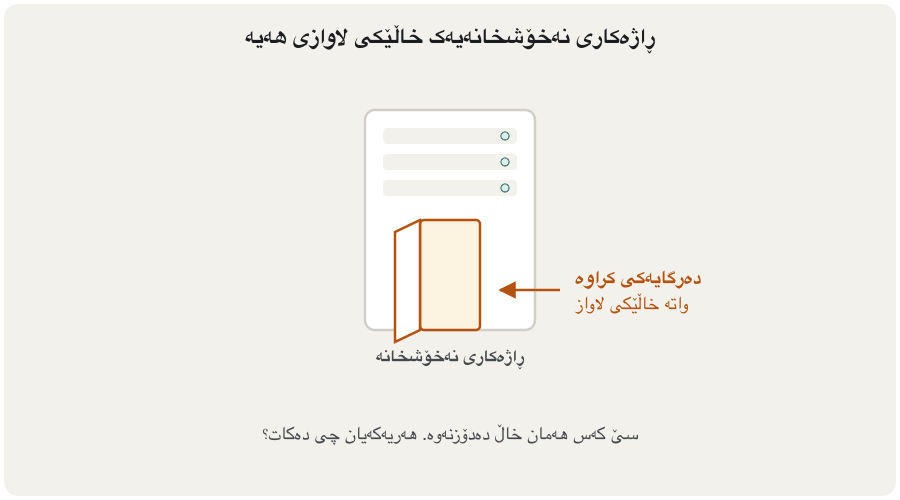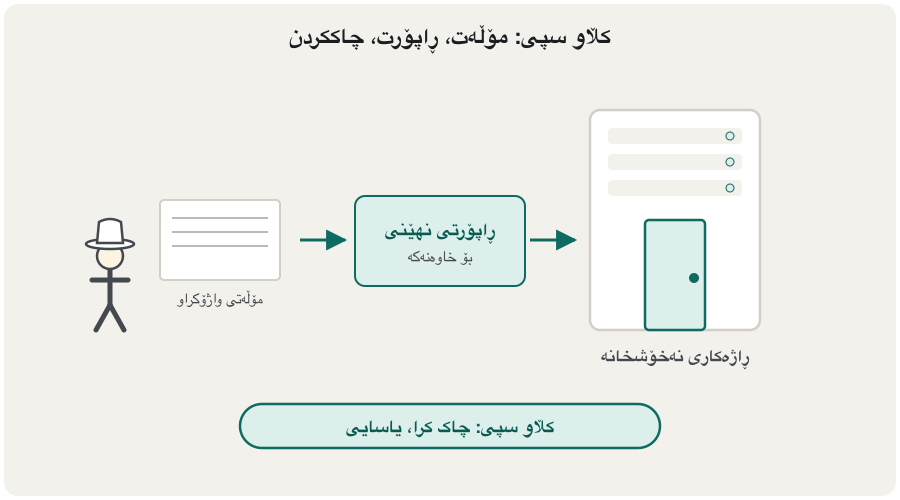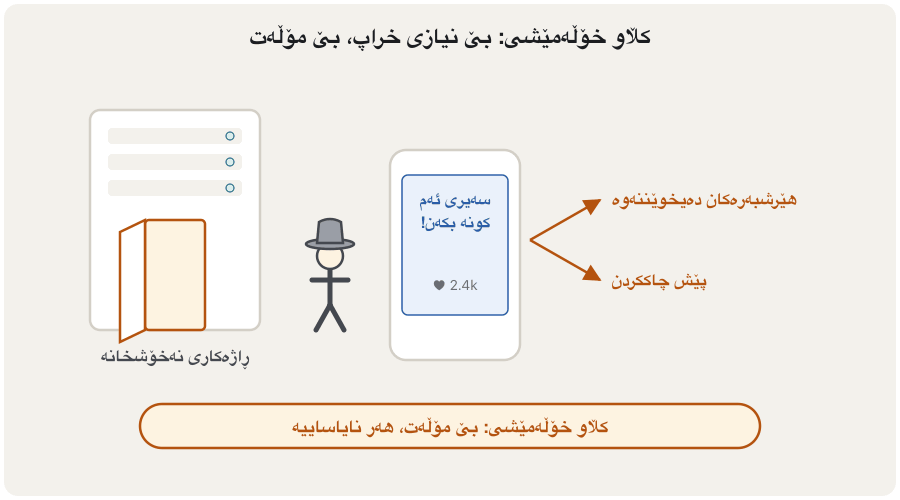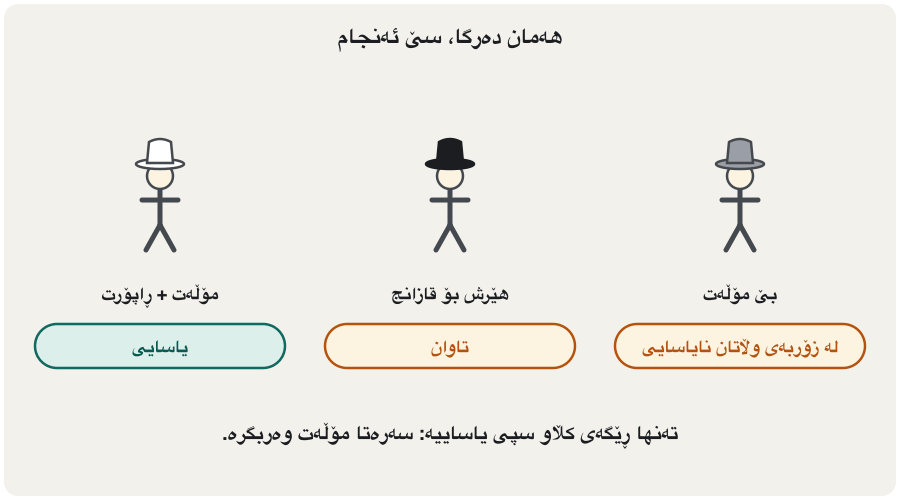
The notes joke that ethical hacking is like 'white magic': the same knowledge an attacker has, used to protect instead of to harm. What turns hacking into ethical hacking is not the skill. It is three things together: the owner's permission, a clear scope (what may be tested), and an honest report that helps fix the problems.
تێبینییەکان بە گاڵتەوە دەڵێن وەک «سحری سپی»یە: هەمان زانیاریی ، بەڵام بۆ پاراستن نەک زیانگەیاندن. ئەوەی هاککردن دەکاتە شارەزایی نییە. سێ شتە پێکەوە: مۆڵەتی خاوەنەکە، سنوورێکی ڕوون (چی تاقی دەکرێتەوە) و ڕاستگۆیانە کە یارمەتی چاککردنی کێشەکان دەدات.
A shop owner in the bazaar asks a locksmith: 'Try to open my shop at night and tell me which lock is weak.' He writes it on paper and signs it. The locksmith tries, writes a list of weak locks and gives it to the owner. If the same locksmith opened a neighbour's shop without asking, it would be a break-in, even if he only wanted to help.
دوکاندارێک لە بازاڕ بە کلیلسازێک دەڵێت: «بە شەو هەوڵ بدە دوکانەکەم بکەیتەوە و پێم بڵێ کام قوفڵ لاوازە.» ئەمە لەسەر کاغەز دەنووسێت و واژۆی دەکات. کلیلسازەکە هەوڵ دەدات، لیستی قوفڵە لاوازەکان دەنووسێت و دەیداتە خاوەن دوکانەکە. ئەگەر هەمان کلیلساز بەبێ پرسین دوکانی دراوسێکەی بکردایەتەوە، ئەوە شکاندنی دوکان بوو، تەنانەت ئەگەر تەنها ویستبێتی یارمەتی بدات.
Where the analogy stops workingسنووری ئەم نموونەیە
In cyberspace you can damage a system without touching anything, and many laws treat even 'only looking' inside a system without permission as a crime.
لە دەتوانیت بێ دەستلێدان زیان بە سیستەمێک بگەیەنیت و زۆر یاسا تەنانەت «تەنها سەیرکردن»ی ناو سیستەمێک بەبێ مۆڵەت بە تاوان دادەنێن.
Penetration testingتاقیکردنەوەی دزەکردن
An authorised, planned attack on a system, done by testers who follow a written scope and rules, to see whether real attackers could get in and how far they could go.
هێرشێکی ڕێگەپێدراو و پلاندانراوە بۆ سەر سیستەمێک، کە تاقیکەرەوەکان بەپێی سنوور و ڕێسای نووسراو ئەنجامی دەدەن، بۆ ئەوەی بزانن ئایا ڕاستەقینە دەتوانێت بچێتە ژوورەوە و تا کوێ دەگات.
The notes' example: companies hire Certified Ethical Hackers (CEH) to perform penetration tests. CEH is a certificate of the EC-Council. A penetration test answers one question: could real attackers penetrate (get into) our systems, and how far could they go? Through these skilled testers the company makes sure its systems are safe and have no weak point through which attackers could get in.
نموونەی تێبینییەکان: کۆمپانیاکان هاکەری ئەخلاقیی بڕوانامەدار (CEH) بەکرێ دەگرن بۆ ئەنجامدانی . CEH بڕوانامەیەکی EC-Councilـە. وەڵامی یەک پرسیار دەداتەوە: ئایا دەتوانن دزە بکەنە ناو سیستەمەکانمانەوە و هەتا کوێ دەڕۆن؟ کۆمپانیاکە لە ڕێگەی ئەم تاقیکەرە شارەزایانەوە دڵنیا دەبێتەوە کە سیستەمەکانی سەلامەتن و هیچ تێدا نییە کە لێیەوە بچنە ژوورەوە.
The UK's National Cyber Security Centre (NCSC) adds three useful points. A penetration test gives assurance: it checks that your own process for finding and fixing vulnerabilities really works; it is not the main way to find them. A good report lists each problem, its risk level and a fix. And a test shows only what was found on the test day, inside the agreed scope: a clean report is not a promise for next year.
سەنتەری نیشتیمانیی بەریتانیا (NCSC) سێ خاڵی بەسوود زیاد دەکات. دڵنیایی دەدات: دەپشکنێت ئایا ڕێگەی خۆت بۆ دۆزینەوە و چاککردنی بەڕاستی کار دەکات؛ ڕێگەی سەرەکیی دۆزینەوەیان نییە. باش هەموو کێشەیەک، ئاستی و چارەسەرەکەی دەنووسێت. هەروەها تاقیکردنەوەکە تەنها ئەوە پیشان دەدات کە لە ڕۆژی تاقیکردنەوەکەدا و لە ناو سنووری ڕێککەوتووەکەدا دۆزراوەتەوە: پاک بەڵێن نییە بۆ ساڵی داهاتوو.
A professional tester explains the steps of a penetration test: research, scanning, trying weaknesses, taking test data out, and the most important part, the report.
پیشەیی هەنگاوەکانی ڕوون دەکاتەوە: لێکۆڵینەوە، پشکنین، تاقیکردنەوەی ، دەرهێنانی تاقیکاری و گرنگترین بەشیان، واتە .
Plays 2:18-3:24: the steps of a penetration test, ending with 'report writing is the most important part'. Stops before the next viewer question.
لە 2:18 تا 3:24 پەخش دەبێت: هەنگاوەکانی ، کە بەم ڕستەیە کۆتایی دێت: «نووسینی گرنگترین بەشە». پێش پرسیاری بینەری دواتر ڕادەوەستێت.
Penetration testingتاقیکردنەوەی دزەکردن
Permission, scope and rulesمۆڵەت، سنوور و ڕێساکان
The owner's homework on this topic makes the main point clearly: organisations use penetration testing to find vulnerabilities, but it must be done ethically. Ethical testers must follow the rules that the organisation sets, such as:
ئەرکی ماڵەوەی خاوەنی تێبینییەکان لەم بارەیەوە خاڵە سەرەکییەکە بە ڕوونی دەڵێت: ڕێکخراوەکان بەکار دەهێنن بۆ دۆزینەوەی ، بەڵام دەبێت بە شێوەیەکی ئەخلاقی ئەنجام بدرێت. تاقیکەرانی ئەخلاقی دەبێت پەیڕەوی ئەو ڕێسایانە بکەن کە ڕێکخراوەکە دایناون، وەک:
- getting written consent (permission) before starting;
- respecting privacy: personal data seen during the test stays secret;
- doing no harm to the organisation or its users.
- وەرگرتنی (مۆڵەت) پێش دەستپێکردن؛
- ڕێزگرتن لە : هەر لە کاتی تاقیکردنەوەکەدا ببینرێت نهێنی دەمێنێتەوە؛
- زیان نەگەیاندن بە ڕێکخراوەکە یان .
The limits of a test (its boundaries) depend on the organisation's size and rules. But honesty, legality and responsibility must always come first.
سنووری تاقیکردنەوەکە بەندە بە قەبارە و ڕێساکانی ڕێکخراوەکە. بەڵام ڕاستگۆیی، یاساپەروەری و بەرپرسیارێتی هەمیشە دەبێت لە پێشەوە بن.
In practice the rules are written in a short signed document, often called the rules of engagement. The picture shows what it usually contains.
لە ڕاستیدا ڕێساکان لە بەڵگەنامەیەکی کورتی واژۆکراودا دەنووسرێن کە زۆرجار پێی دەڵێن «ڕێساکانی کارکردن» (rules of engagement). وێنەکە پیشان دەدات زۆرجار چی تێدایە.
White, black and grey hatsکڵاوی سپی، ڕەش و خۆڵەمێشی
Hackers are often sorted by the colour of an imaginary hat. The names come from old cowboy films, where the hero wore a white hat and the villain a black one. (Two related words, cracker and hacktivist, are explained in Crackers, hackers and hats.) The notes compare the three kinds:
زۆرجار بەپێی ڕەنگی کڵاوێکی خەیاڵی پۆلێن دەکرێن. ناوەکان لە فیلمە کۆنەکانی کاوبۆیەوە هاتوون، کە پاڵەوانەکە کڵاوی سپی و خراپەکارەکە کڵاوی ڕەشی لەسەر دەکرد. (دوو وشەی پەیوەندیدار، کراکەر (cracker) و ، لە کراکەر، هاکەر و کڵاوەکان ڕوون کراونەتەوە.) تێبینییەکان بەم شێوەیە سێ جۆرەکە بەراورد دەکەن:
| Aspectلایەن | White-hatکڵاو سپی | Black-hatکڵاو ڕەش | Grey-hatکڵاو خۆڵەمێشی |
|---|---|---|---|
| Whoکێ | Ethical hackers who work to secure systems کە بۆ پاراستنی سیستەمەکان کار دەکەن | Malicious people who exploit vulnerabilities for personal gainکەسانی خراپەکار کە بۆ قازانجی خۆیان بەکار دەهێنن | They find vulnerabilities without permission, but without malicious intentبەبێ مۆڵەت دەدۆزنەوە، بەڵام بێ نیازی خراپ |
| Permissionمۆڵەت | Yes, alwaysبەڵێ، هەمیشە | Noنەخێر | Noنەخێر |
| Exampleنموونە | Reporting holes through Google's bug bounty programmeڕاپۆرتدانی کون لە ڕێگەی گووگڵەوە | Running ransomware campaignsبەڕێوەبردنی هەڵمەتی | Exposing holes in a government website to push for better securityئاشکراکردنی کونەکانی حکوومی بۆ پاڵنان بەرەو باشتر |
| Legal?یاساییە؟ | Yesبەڵێ | No: a crimeنەخێر: تاوانە | Usually no, even with good intentزۆرجار نەخێر، تەنانەت بە نیازی باشیش |
The animation shows the same open door found by three different people.
ئەنیمەیشنەکە هەمان دەرگای کراوە پیشان دەدات کە سێ کەسی جیاواز دەیدۆزنەوە.
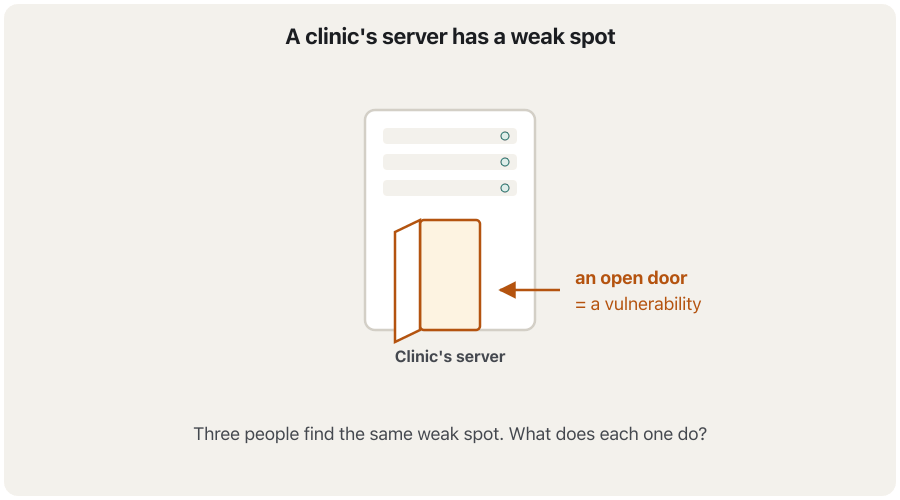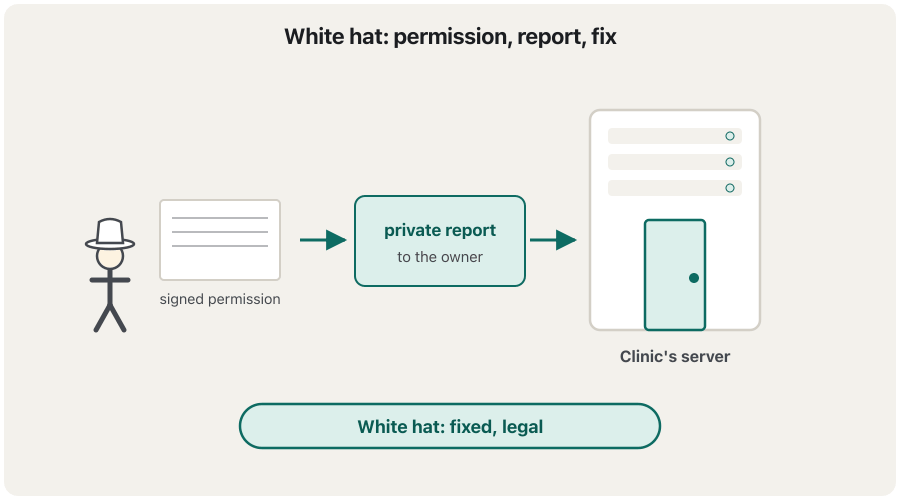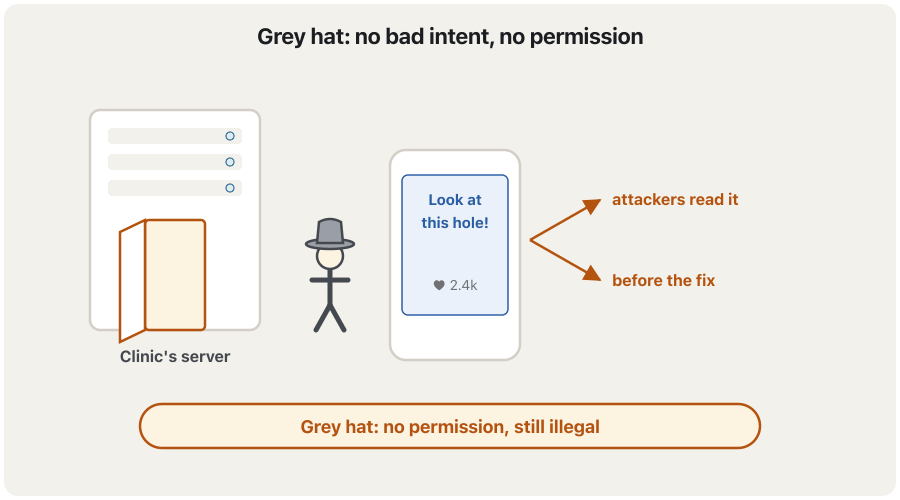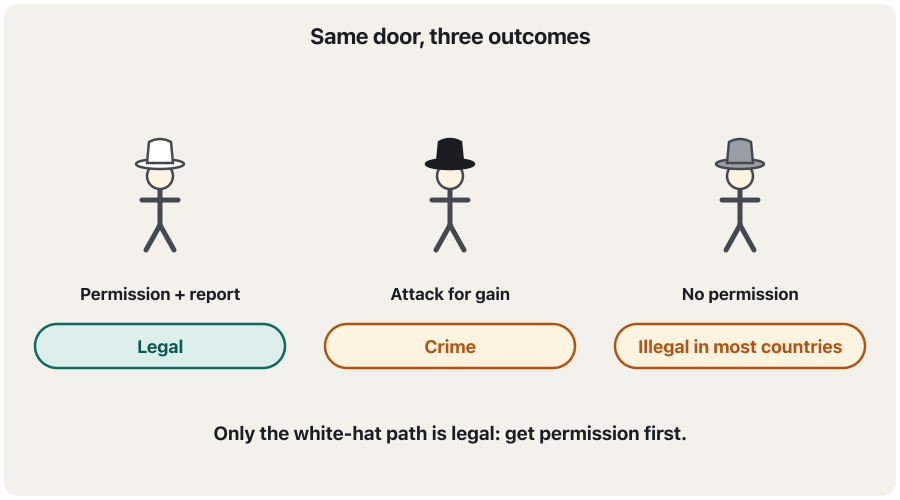
Who hackers are, and the difference between white hat (allowed, ethical), grey hat and black hat (criminal) hackers, with famous examples.
کێن و جیاوازیی نێوان کڵاوسپی (ڕێگەپێدراو و ئەخلاقی)، کڵاوخۆڵەمێشی و کڵاوڕەش (تاوانکار)، لەگەڵ چەند نموونەیەکی بەناوبانگ.
Plays 0:34-4:32: who hackers are, then white, grey and black hats. Stops before the TunnelBear sponsor.
لە 0:34 تا 4:32 پەخش دەبێت: کێن، پاشان ، و . پێش ڕیکلامی سپۆنسەرەکە (TunnelBear) ڕادەوەستێت.
Grey hats: good intent is not permissionکڵاو خۆڵەمێشییەکان: نیازی باش مۆڵەت نییە
The owner adds a note on grey hats: they are harmful or helpful according to their own mood and needs, they are not employees of any company, and most of the time they are not harmful. The white-hat example, bug bounties, is the legal road for the same curiosity: see Responsible Disclosure and Bug Bounties. Ransomware is explained in Ransomware.
خاوەنی تێبینییەکان تێبینییەک دەربارەی کڵاو خۆڵەمێشییەکان زیاد دەکات: بەپێی ئارەزوو و پێویستیی خۆیان زیانبەخش یان سوودبەخشن، لە هیچ کۆمپانیایەکدا کارمەند نین و زۆرجار زیانبەخش نین. نموونەی کڵاو سپییەکان، واتە ، ڕێگە یاساییەکەیە بۆ هەمان حەزی گەڕان: بڕوانە ئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ. لە نەرمەواڵەی بارمتەگر ڕوون کراوەتەوە.
Professional ethicsئەخلاقی پیشەیی
Professional ethics in cybersecurity are the standards that make security professionals act responsibly and keep users' trust. The notes' example: not misusing admin privileges for personal gain. An administrator can often see salaries, messages or customers' records. Being able to look is not a reason to look: read only what your job needs.
ئەخلاقی پیشەیی لە ئەو ستانداردانەن کە وا لە پسپۆڕانی دەکەن بە بەرپرسیارییەوە کار بکەن و متمانەی بپارێزن. نموونەی تێبینییەکان: بەکارنەهێنانی بەڕێوەبەر بە خراپی بۆ قازانجی کەسی. بەڕێوەبەرێک زۆرجار دەتوانێت مووچە، نامە یان تۆماری کڕیاران ببینێت. توانای سەیرکردن هۆ نییە بۆ سەیرکردن: تەنها ئەوە بخوێنەرەوە کە کارەکەت پێویستی پێیەتی.
The EC-Council code of ethicsیاسای ئەخلاقیی EC-Council
The EC-Council, the organisation behind the CEH certificate, has a code of ethics to keep its members professional and honest (integrity). The lecture sums it up in three main rules that every expert in the field needs:
EC-Council، ئەو ڕێکخراوەی بڕوانامەی CEH دەدات، یاسایەکی ئەخلاقیی هەیە بۆ ئەوەی ئەندامەکانی پیشەیی و ڕاستگۆ بن (integrity). وانەکە ئەم یاسایە لە سێ ڕێسای سەرەکیدا کورت دەکاتەوە کە هەموو شارەزایەکی ئەم بوارە پێویستیەتی:
- Act honourably: be honest with clients and employers.
- Avoid illegal activity: simply, do nothing illegal.
- Report unethical behaviour: if you see a colleague doing something wrong or strange, tell the right people directly, quietly or openly.
- بە شەرەفەوە ڕەفتار بکە: لەگەڵ کڕیار و خاوەنکار ڕاستگۆ بە.
- خۆت لە کاری نایاسایی بپارێزە: بە سادەیی، هیچ کارێکی نایاسایی مەکە.
- ڕاپۆرتی ڕەفتاری نائەخلاقی بدە: ئەگەر هاوکارێکت بینی کارێکی هەڵە یان سەیر دەکات، ڕاستەوخۆ بە کەسانی پەیوەندیدار بڵێ، بە بێدەنگی یان بە ئاشکرا.
The ISC2 code of ethicsیاسای ئەخلاقیی ISC2
(ISC)², today written ISC2, is a global organisation that trains and certifies cybersecurity professionals (it gives, for example, the CISSP certificate). Its code of ethics guides members to act with integrity, professionalism and responsibility. Every member must follow it, and ISC2 has an ethics committee that handles complaints against members. Its four canons (core principles) say:
(ISC)²، کە ئەمڕۆ بە شێوەی ISC2 دەنووسرێت، ڕێکخراوێکی جیهانییە کە پسپۆڕانی ڕادەهێنێت و بڕوانامەیان پێ دەدات (بۆ نموونە بڕوانامەی CISSP). یاسا ئەخلاقییەکەی ڕێنمایی ئەندامان دەکات کە بە ڕاستگۆیی، پیشەیی و بەرپرسیارێتییەوە کار بکەن. هەموو ئەندامێک دەبێت پەیڕەوی بکات و ISC2 لیژنەیەکی ئەخلاقیی هەیە کە سکاڵاکان لەسەر ئەندامان وەردەگرێت. چوار بنەما سەرەکییەکەی دەڵێن:
- Protect society, the common good, necessary public trust and confidence, and the infrastructure.
- Act honourably, honestly, justly, responsibly and legally.
- Provide diligent and competent service to principals: work carefully and well for your employer and clients (diligent = careful and hard-working).
- Advance and protect the profession.
- کۆمەڵگە بپارێزە، لەگەڵ بەرژەوەندیی گشتی، ئەو متمانە و دڵنیاییەی خەڵک کە پێویستە و ژێرخان.
- بە شەرەف، ڕاستگۆیی، دادپەروەری، بەرپرسیارێتی و بەپێی یاسا ڕەفتار بکە.
- خزمەتی بەپەرۆش و لێهاتوو پێشکەش بە خاوەنکاران بکە: بە وردی و باشی بۆ خاوەنکار و کڕیارەکانت کار بکە.
- پیشەکە پێش بخە و بیپارێزە.
The ACM code, and what all three agree onیاسای ACM و ئەوەی هەر سێکیان لەسەری ڕێککەوتوون
A third code is useful because it covers all computing work, not only security. The ACM (Association for Computing Machinery) Code of Ethics (2018) includes: avoid harm (1.2); respect privacy (1.6); honour confidentiality (1.7); access computing and communication resources only when authorised or when compelled by the public good (2.8); and design systems that are robustly and usably secure (2.9). Even the 'public good' exception does not change the law of your country: in most places getting into a system without permission is still a crime.
یاسایەکی سێیەم بەسوودە چونکە هەموو کارێکی کۆمپیوتەری دەگرێتەوە، نەک تەنها . یاسای ئەخلاقیی ACM (Association for Computing Machinery، کۆمەڵەی پسپۆڕانی )، وەشانی ٢٠١٨، ئەمانەی تێدایە: زیان مەگەیەنە (١.٢)؛ ڕێز لە بگرە (١.٦)؛ نهێنی بپارێزە (١.٧)؛ تەنها کاتێک دەست بگەیەنە سەرچاوەکانی و پەیوەندی کە ڕێگەت پێدراوە یان بەرژەوەندیی گشتی ناچارت دەکات (٢.٨)؛ و سیستەم دیزاین بکە کە بە شێوەیەکی بەهێز و بەکارهێنراو سەلامەت بێت (٢.٩). تەنانەت بەدەرکردنی «بەرژەوەندیی گشتی» یاسای وڵاتەکەت ناگۆڕێت: لە زۆربەی شوێنەکان چوونە ناو سیستەمێک بەبێ مۆڵەت هەر تاوانە.
Read side by side, the three codes agree on the same core: protect people, obey the law, be honest, keep secrets, work only with permission and within your skills.
ئەگەر سێ یاساکە لە تەنیشت یەکەوە بخوێنیتەوە، لەسەر هەمان ناوەڕۆک ڕێککەوتوون: خەڵک بپارێزە، پابەندی یاسا بە، ڕاستگۆ بە، نهێنی بپارێزە، تەنها بە مۆڵەت و لە سنووری شارەزایی خۆتدا کار بکە.
What the law says about testing without permissionیاسا دەربارەی تاقیکردنەوە بەبێ مۆڵەت چی دەڵێت
Codes of ethics are promises inside a profession. Laws are enforced by the police and the courts, for everyone. Almost every country makes unauthorised access a crime. Two examples:
یاسا ئەخلاقییەکان بەڵێنن لە ناو پیشەیەکدا. یاساکان پۆلیس و دادگا جێبەجێیان دەکەن، بۆ هەموو کەس. نزیکەی هەموو وڵاتێک بە تاوان دادەنێت. دوو نموونە:
- United States: the Computer Fraud and Abuse Act (CFAA) makes accessing a computer without authorisation, or beyond your authorisation, a crime. See Computer-crime laws.
- European Union: Directive 2013/40/EU tells every EU country to punish illegal access to information systems, illegal system interference, illegal data interference, illegal interception, and making or selling tools for these crimes.
- ئەمریکا: یاسای ساختەکاری و خراپ بەکارهێنانی کۆمپیوتەر () دەستڕاگەیشتن بە بەبێ ڕێگەپێدان، یان زیاتر لە ڕێگەپێدانەکەت، بە تاوان دادەنێت. بڕوانە یاساکانی تاوانی کۆمپیوتەری.
- یەکێتیی ئەوروپا: ڕێنمایی 2013/40/EU داوا لە هەموو وڵاتێکی ئەندام دەکات سزای ئەمانە بدات: دەستڕاگەیشتنی نایاسایی بە ، دەستتێوەردانی نایاسایی لە سیستەم، دەستتێوەردانی نایاسایی لە ، گوێگرتن و ڕێگرتنی نایاسایی و دروستکردن یان فرۆشتنی ئامراز بۆ ئەم تاوانانە.
What applies in Iraq and the Kurdistan Region is explained, with its sources, in The law at home.
ئەوەی لە عێراق و هەرێمی کوردستان جێبەجێ دەکرێت، لەگەڵ سەرچاوەکانی، لە یاسا لە وڵاتی خۆماندا ڕوون کراوەتەوە.
A case to discuss: MyFitnessPal, 2018نموونەیەک بۆ گفتوگۆ: MyFitnessPal، ٢٠١٨
The owner's homework gives a real case. The American company Under Armour owned an app called MyFitnessPal. In February 2018 attackers got into its data. On 29 March 2018 the company announced that about 150 million user accounts were affected: usernames, e-mail addresses and hashed passwords (stored in a scrambled form, not as plain text). Payment card data and ID numbers were not taken. All users had to change their passwords. The company did not publish how the attackers got in.
ئەرکی ماڵەوەی خاوەنی تێبینییەکان نموونەیەکی ڕاستەقینە دەهێنێتەوە. کۆمپانیای ئەمریکیی Under Armour خاوەنی بوو بە ناوی MyFitnessPal. لە شوباتی ٢٠١٨دا دزەیان کردە ناو . لە ٢٩ی ئازاری ٢٠١٨دا کۆمپانیاکە ڕایگەیاند کە نزیکەی ١٥٠ ملیۆن زیانیان پێ گەیشتووە: ، ناونیشانی و (بە شێوەیەکی تێکدراو هەڵگیرابوون، نەک وەک دەقی ئاسایی). زانیاریی کارتی پارەدان و ژمارەی ناسنامە نەبران. هەموو ناچار بوون بگۆڕن. کۆمپانیاکە بڵاوی نەکردەوە چۆن چوونە ژوورەوە.
Discussing the case: who could have tested it?گفتوگۆ لەسەر نموونەکە: کێ دەیتوانی تاقیی بکاتەوە؟
The homework then gives the owner's opinion: ethically, ethical hackers should have prevented this in advance. But if the company has not set up any group for this purpose, doing such work may cause legal problems. In other words, an outsider who tests the app without an invitation breaks the law, even to help. The cause of this breach was never published, so 'ethical hackers would have stopped it' is an opinion to discuss, not a known fact.
پاشان ئەرکی ماڵەوەکە ڕای خاوەنەکەی دەدات: لە ڕووی ئەخلاقییەوە دەبوو پێشوەختە ڕێیان لەمە بگرتایە. بەڵام کاتێک کۆمپانیاکە هیچ گروپێکی بۆ ئەم مەبەستە دانەنابێت، ئەنجامدانی کارێکی ئاوها لەوانەیە ببێتە هۆی کێشەی یاسایی. بە واتایەکی تر، کەسێکی دەرەکی کە بەبێ بانگهێشت تاقی دەکاتەوە یاسا دەشکێنێت، تەنانەت بۆ یارمەتیدانیش. هۆکاری ئەم هەرگیز بڵاو نەکرایەوە، بۆیە « ڕێیان لێ دەگرت» ڕایەکە بۆ گفتوگۆ، نەک ڕاستییەکی سەلمێنراو.
Answer in two or three sentences each: (a) Who could have searched MyFitnessPal for weaknesses legally before 2018? (b) A user notices something strange in the app's login page. What may she do, and what may she not do? (c) What should a company like this have in place so that outsiders can help without breaking the law?
وەڵامی هەریەکەیان بە دوو یان سێ ڕستە بدەرەوە: (أ) کێ دەیتوانی پێش ٢٠١٨ بە شێوەیەکی یاسایی بەدوای لە MyFitnessPal بگەڕێت؟ (ب) شتێکی سەیر لە پەڕەی ئەپەکەدا دەبینێت. چی دەتوانێت بکات و چی ناتوانێت؟ (ج) کۆمپانیایەکی وەک ئەمە دەبێت چی ئامادە کردبێت بۆ ئەوەی کەسانی دەرەکی بتوانن بەبێ شکاندنی یاسا یارمەتی بدەن؟
Hintئاماژە
Think of the three legal routes: the company's own staff, hired testers, and an open programme.
بیر لە سێ ڕێگە یاساییەکە بکەرەوە: کارمەندانی کۆمپانیاکە، تاقیکەرانی بەکرێگیراو و بەرنامەیەکی کراوە.
Show answerوەڵامەکە پیشان بدە
(a) The company's own security team, or testers it hired with written permission and a scope (a penetration test), or researchers in a bug bounty programme that the company opened. (b) She may report what she saw through the company's official channel, with a short description and a screenshot. She may not try to break in further, guess other people's passwords or download data to 'prove' the problem. (c) A vulnerability disclosure policy with a contact address (for example a security.txt file), a promise not to sue good-faith reporters (a safe harbour), and, if it can afford it, a bug bounty programme. These are taught in Responsible Disclosure and Bug Bounties.
(أ) تیمی کۆمپانیاکە خۆی، یان ئەو تاقیکەرانەی بە مۆڵەتی نووسراو و سنوورێکی دیاریکراو بەکرێی گرتوون ()، یان توێژەران لە کە کۆمپانیاکە کردبێتییەوە. (ب) دەتوانێت لە ڕێگەی کەناڵی فەرمیی کۆمپانیاکەوە ڕاپۆرتی ئەوە بدات کە بینیویەتی، لەگەڵ وەسفێکی کورت و وێنەیەکی پەردە. ناتوانێت هەوڵی زیاتری دزەکردن بدات، خەڵکی تر بە مەزەندە تاقی بکاتەوە یان دابەزێنێت بۆ «سەلماندنی» کێشەکە. (ج) لەگەڵ ناونیشانێکی پەیوەندی (بۆ نموونە فایلی security.txt)، بەڵێنی سکاڵا تۆمارنەکردن لە ڕاپۆرتدەرانی نیازپاک () و ئەگەر توانای هەبێت، . ئەمانە لە ئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ دەخوێنیت.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| 'If my intent is good, testing is legal.'«ئەگەر نیازم باش بێت، تاقیکردنەوە یاساییە.» | Most laws punish access without permission whatever the reason.زۆربەی یاساکان سزای دەستڕاگەیشتن بەبێ مۆڵەت دەدەن، هۆکارەکەی هەرچی بێت. | Get written permission, or use your own lab or a bug bounty programme.مۆڵەتی نووسراو وەربگرە، یان تاقیگەی خۆت یان بەکار بهێنە. |
| Testing beyond the agreed scope 'because it was open'تاقیکردنەوە لە دەرەوەی سنووری ڕێککەوتوو «چونکە کراوە بوو» | Permission covers only what is written; the rest is unauthorised access.مۆڵەت تەنها ئەوە دەگرێتەوە کە نووسراوە؛ ئەوانی تر . | Stop, and ask the owner to extend the scope in writing.بوەستە و داوا لە خاوەنەکە بکە سنوورەکە بە نووسین فراوان بکات. |
| Taking permission from someone with no authorityوەرگرتنی مۆڵەت لە کەسێک کە دەسەڵاتی نییە | A friend or a junior employee cannot allow a test of the company.هاوڕێیەک یان کارمەندێکی بچووک ناتوانێت ڕێگە بە تاقیکردنەوەی کۆمپانیاکە بدات. | Get it signed by the system's owner or a responsible manager.با خاوەنی سیستەمەکە یان بەڕێوەبەرێکی بەرپرسیار واژۆی بکات. |
| Calling a grey hat 'legal because it is a grey area'گوتنی «کڵاو خۆڵەمێشی یاساییە چونکە ناوچەیەکی خۆڵەمێشییە» | The grey is in the ethics, not in the law.خۆڵەمێشییەکە لە ئەخلاقدایە، نەک لە یاسادا. | Treat any access without permission as illegal.هەر دەستڕاگەیشتنێک بەبێ مۆڵەت بە نایاسایی دابنێ. |
| Reading data your admin account can reach but your job does not needخوێندنەوەی ئەو هەژماری بەڕێوەبەرەکەت پێی دەگات بەڵام کارەکەت پێویستی پێی نییە | It misuses privileges and breaks users' trust. بە خراپی بەکار دەهێنێت و متمانەی دەشکێنێت. | Use access only for the task in front of you.دەستڕاگەیشتن تەنها بۆ ئەو ئەرکە بەکار بهێنە کە لەبەردەمتە. |
| Asking for money before telling a company about a holeداواکردنی پارە پێش ئەوەی کۆمپانیایەک لە کونێک ئاگادار بکەیتەوە | 'Pay me or I publish' is extortion, a crime.«پارەم بدە یان بڵاوی دەکەمەوە» باجسەندنە، کە تاوانە. | Report first; accept a reward only if the company's programme offers one.سەرەتا ڕاپۆرت بدە؛ خەڵات تەنها ئەگەر بەرنامەی کۆمپانیاکە پێشکەشی بکات وەربگرە. |
Exercisesڕاهێنانەکان
For each person say white, black or grey hat, and whether the action is legal: (a) Shilan, hired by a bank with a signed scope, finds a flaw in its app and writes a report. (b) Soran breaks into an online shop and sells its customers' card numbers. (c) Dilan, without asking, scans her university's servers for open ports and e-mails the IT office what she found. (d) Rezan reports a bug through a company's bug bounty programme, inside its rules.
بۆ هەر کەسێک بڵێ کڵاو سپی، ڕەش یان خۆڵەمێشی و ئایا کارەکە یاساییە: (أ) شیلان، کە بانکێک بە سنوورێکی واژۆکراو بەکرێی گرتووە، کەموکورتییەک لە ئەپەکەیدا دەدۆزێتەوە و دەنووسێت. (ب) سۆران دزە دەکاتە ناو فرۆشگایەکی سەرهێڵ و ژمارەی کارتی کڕیارەکانی دەفرۆشێت. (ج) دیلان، بەبێ پرسین، زانکۆکەی بۆ پۆرتی کراوە دەپشکنێت و ئەوەی دۆزیویەتییەوە بە بۆ نووسینگەی IT دەنێرێت. (د) ڕێزان لە ڕێگەی کۆمپانیایەکەوە و لە ناو ڕێساکانیدا ڕاپۆرتی دەدات.
Show answerوەڵامەکە پیشان بدە
- (a) White hat, legal: permission, scope and a report.
- (b) Black hat, a crime: access without permission for personal gain.
- (c) Grey hat: no bad intent, but scanning systems without permission is unauthorised and can be illegal; she should have asked first.
- (d) White hat, legal: the programme's rules are his permission.
- (أ) کڵاو سپی، یاسایی: مۆڵەت، سنوور و .
- (ب) کڵاو ڕەش، تاوان: دەستڕاگەیشتن بەبێ مۆڵەت بۆ قازانجی کەسی.
- (ج) کڵاو خۆڵەمێشی: نیازی خراپی نییە، بەڵام پشکنینی سیستەم بەبێ مۆڵەت ڕێگەپێنەدراوە و دەکرێت نایاسایی بێت؛ دەبوو سەرەتا بپرسێت.
- (د) کڵاو سپی، یاسایی: ڕێساکانی بەرنامەکە مۆڵەتی ئەون.
Dilan Clinic wants a penetration test of its patient-booking website next month. List at least six things the signed authorisation must contain, with one example for each.
نەخۆشخانەی دیلان دەیەوێت مانگی داهاتوو بۆ نۆرەگرتنی نەخۆشەکانی بکرێت. لانیکەم شەش شت بنووسە کە ڕێگەپێدانە واژۆکراوەکە دەبێت تێیدا بێت، بۆ هەریەکەیان نموونەیەک.
Show answerوەڵامەکە پیشان بدە
- Who allows it: the clinic's director, who owns the system (name, role, signature).
- Scope in: the booking website and its login page. Scope out: the hospital's medical devices and staff e-mail.
- Dates and hours: 10–14 of next month, 22:00–06:00, when few patients book.
- Methods: allowed: scanning and testing the login form; forbidden: denial-of-service, phishing staff, changing real records.
- Contacts and a stop rule: the IT manager's phone number; stop at once if the site slows down.
- Data: patient data seen by accident is not copied, is kept secret and is deleted after the test.
- Report: delivered to the director within one week, with each problem, its risk and a fix.
- کێ ڕێگە دەدات: بەڕێوەبەری نەخۆشخانەکە، کە خاوەنی سیستەمەکەیە (ناو، ڕۆڵ، واژۆ).
- ناو سنوور: نۆرەگرتن و پەڕەی . دەرەوەی سنوور: ئامێرە پزیشکییەکانی نەخۆشخانە و کارمەندان.
- ڕێکەوت و کاتژمێر: ١٠ تا ١٤ی مانگی داهاتوو، ٢٢:٠٠ تا ٠٦:٠٠، کاتێک نەخۆشی کەم نۆرە دەگرن.
- ڕێگەکان: ڕێگەپێدراو: پشکنین و تاقیکردنەوەی فۆرمی ؛ قەدەغە: ، فیشینگی کارمەندان، گۆڕینی تۆماری ڕاستەقینە.
- پەیوەندی و ڕێسای وەستان: ژمارەی تەلەفۆنی بەڕێوەبەری IT؛ ئەگەر خاو بوو یەکسەر بوەستە.
- : نەخۆشان کە بە ڕێکەوت دەبینرێت کۆپی ناکرێت، نهێنی دەمێنێتەوە و دوای تاقیکردنەوەکە دەسڕدرێتەوە.
- : لە ماوەی یەک هەفتەدا دەدرێتە بەڕێوەبەر، لەگەڵ هەموو کێشەیەک، و چارەسەرەکەی.
The lecture asks: 'Is it right to collect personal information to improve security?' Give one case where the answer is yes and one where it is no, and say for each whether a law might also apply.
وانەکە دەپرسێت: «ئایا دروستە زانیاریی کەسی کۆ بکەینەوە بۆ باشترکردنی ؟» نموونەیەک بهێنەرەوە کە وەڵامەکەی بەڵێ بێت و نموونەیەک کە نەخێر بێت و بۆ هەریەکەیان بڵێ ئایا لەوانەیە یاسایەکیش بیگرێتەوە.
Show answerوەڵامەکە پیشان بدە
Yes: a company keeps a log of who signed in to its payroll system and when, so it can detect stolen accounts. The data is limited to the purpose, staff are told about it, and data-protection laws usually allow such security logs. No: the same company secretly reads employees' private messages 'to find threats'. It goes far beyond the purpose, breaks their privacy, and in many countries breaks privacy or labour laws as well.
بەڵێ: کۆمپانیایەک هەڵدەگرێت کە کێ و کەی چووە ناو سیستەمی مووچەوە، بۆ ئەوەی هەژماری دزراو بدۆزێتەوە. سنووردارە بە مەبەستەکەوە، کارمەندان ئاگادار کراونەتەوە و یاساکانی زۆرجار ڕێگە بەم جۆرە ئاسایشییانە دەدەن. نەخێر: هەمان کۆمپانیا بە نهێنی نامە تایبەتەکانی کارمەندان دەخوێنێتەوە «بۆ دۆزینەوەی ». ئەمە زۆر لە مەبەستەکە تێدەپەڕێت، ئەوان دەشکێنێت و لە زۆر وڵاتدا یاسای یان یاسای کاریش دەشکێنێت.
In the computer lab Hana finds a sheet of paper with a classmate's e-mail address and password on it. The password is crossed out but still readable. What is the ethical thing to do, what must she not do, and what does the law say about using it?
هانا لە تاقیگەی پارچە کاغەزێک دەدۆزێتەوە کە ناونیشانی و هاوپۆلێکی لەسەر نووسراوە. هێڵی بەسەردا هاتووە، بەڵام هێشتا دەخوێنرێتەوە. کاری ئەخلاقی چییە، چی نابێت بکات و یاسا دەربارەی بەکارهێنانی چی دەڵێت؟
Hintئاماژە
Think about whose account it is, and what "permission" means.
بیر لەوە بکەرەوە هەژمارەکە هی کێیە و «مۆڵەت» واتای چییە.
Show answerوەڵامەکە پیشان بدە
- Ethical: give the paper back privately to the classmate (or to the teacher or IT staff), and tell her to change the password at once, also on every other site where she used it, and to turn on multi-factor sign-in.
- Must not: try the password 'just to see', photograph it, share it, or keep it. Crossed out does not mean it no longer works.
- Law: signing in to someone else's account without permission is unauthorised access, a crime in most countries, even if nothing is changed.
- ئەخلاقی: کاغەزەکە بە نهێنی بداتەوە بە هاوپۆلەکەی (یان بە مامۆستا یان کارمەندی IT) و پێی بڵێت یەکسەر بگۆڕێت، لە هەموو ئەو شوێنانەی تریشدا کە بەکاری هێناوە و پشتڕاستکردنەوەی فرەهۆکاری چالاک بکات.
- نابێت: «تەنها بۆ سەیرکردن» تاقی بکاتەوە، وێنەی بگرێت، بە کەسی بدات یان هەڵیبگرێت. هێڵ بەسەردا هاتن واتای ئەوە نییە کە ئیتر کار ناکات.
- یاسا: چوونە ناو هەژماری کەسێکی تر بەبێ مۆڵەت ، کە لە زۆربەی وڵاتاندا تاوانە، تەنانەت ئەگەر هیچ شتێک نەگۆڕدرێت.
Summary and reviewکورتە و پێداچوونەوە
- Every security decision has an ethical question (is it right?) and a legal one (does the law allow it?). Ethics builds trust; obeying the law avoids penalties.
- Cyber ethics covers privacy, intellectual property and ethical hacking.
- Ethical hacking and penetration testing need the owner's written permission, a clear scope, no harm, respect for privacy and an honest report.
- White hats work with permission; black hats attack for gain; grey hats act without permission and without bad intent, which is still illegal in most countries.
- EC-Council (act honourably, avoid illegal activity, report unethical behaviour), ISC2 (four canons) and ACM (avoid harm, access only when authorised) agree on the same core.
- Laws such as the US CFAA and the EU's Directive 2013/40/EU make unauthorised access a crime; good intent is not permission.
- هەموو بڕیارێکی پرسیارێکی ئەخلاقی (ئایا ڕاستە؟) و پرسیارێکی یاسایی (ئایا یاسا ڕێگە دەدات؟) لەخۆ دەگرێت. ئەخلاق متمانە دروست دەکات؛ ڕێ لە سزا دەگرێت.
- ، و دەگرێتەوە.
- و پێویستیان بە مۆڵەتی نووسراوی خاوەنەکە، سنوورێکی ڕوون، زیان نەگەیاندن، ڕێزگرتن لە و ڕاستگۆیانە هەیە.
- کڵاو سپییەکان بە مۆڵەت کار دەکەن؛ کڵاو ڕەشەکان بۆ قازانج هێرش دەکەن؛ کڵاو خۆڵەمێشییەکان بەبێ مۆڵەت و بێ نیازی خراپ کار دەکەن، کە لە زۆربەی وڵاتاندا هەر نایاساییە.
- EC-Council (بە شەرەفەوە ڕەفتار بکە، خۆت لە کاری نایاسایی بپارێزە، ڕاپۆرتی ڕەفتاری نائەخلاقی بدە)، ISC2 (چوار بنەما) و ACM (زیان مەگەیەنە، تەنها بە ڕێگەپێدان دەست بگەیەنە) لەسەر هەمان ناوەڕۆک ڕێککەوتوون.
- یاساکانی وەک ئەمریکا و ڕێنمایی 2013/40/EUـی ئەوروپا بە تاوان دادەنێن؛ نیازی باش مۆڵەت نییە.
What are the two questions behind every security decision?دوو پرسیارەکەی پشت هەموو بڕیارێکی ئاسایش چین؟
Is it right (ethics)? Does the law allow it (law)?
ئایا ڕاستە (ئەخلاق)؟ ئایا یاسا ڕێگەی پێ دەدات (یاسا)؟
Name four things a penetration-test authorisation contains.چوار شت ناو ببە کە ڕێگەپێدانی تاقیکردنەوەی دزەکردن تێیدایە.
Any four of: who allows it, the scope, dates and hours, allowed and forbidden methods, contacts and a stop rule, data handling, the report.
هەر چوارێک لەمانە: کێ ڕێگە دەدات، سنوور، ڕێکەوت و کاتژمێر، ڕێگە ڕێگەپێدراو و قەدەغەکان، پەیوەندی و ڕێسای وەستان، مامەڵەکردن لەگەڵ ، .
Why is a grey hat's test usually illegal?بۆچی تاقیکردنەوەی کڵاو خۆڵەمێشی زۆرجار نایاساییە؟
Because the law punishes access without permission, whatever the intent.
چونکە یاسا سزای دەستڕاگەیشتن بەبێ مۆڵەت دەدات، نیازەکە هەرچی بێت.
Give the four ISC2 canons in short.چوار بنەماکەی ISC2 بە کورتی بڵێ.
Protect society; act honourably, honestly, justly, responsibly and legally; serve principals diligently and competently; advance and protect the profession.
کۆمەڵگە بپارێزە؛ بە شەرەف، ڕاستگۆیی، دادپەروەری، بەرپرسیارێتی و بەپێی یاسا ڕەفتار بکە؛ بە پەرۆش و لێهاتوویی خزمەتی خاوەنکاران بکە؛ پیشەکە پێش بخە و بیپارێزە.
Videoڤیدیۆ
Watch a videoسەیری ڤیدیۆیەک بکە
A video that viewers liked a lot and praised in their comments, chosen for this lesson.ڤیدیۆیەک کە بینەران زۆریان پێ خۆش بووە و لە کۆمێنتەکانیاندا ستایشیان کردووە، بۆ ئەم وانەیە هەڵبژێردراوە.
In Sorani: the three kinds of hackers (white, grey and black hat), then what ethical hacking means, with simple slides.
بە سۆرانی: سێ جۆرەکەی (، و )، پاشان واتای چییە، بە سادە.
Plays 0:30-4:30 in Sorani: the 'Types of Hackers' slide (to about 2:51), then 'Ethical hacking'. Stops before the Linux and Kali-tools part.
بە سۆرانی، لە 0:30 تا 4:30 پەخش دەبێت: «جۆرەکانی » (تا نزیکەی 2:51)، پاشان «». پێش بەشی Linux و ئامرازەکانی Kali ڕادەوەستێت.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
Related lecturesوانە پەیوەندیدارەکان
- Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
- Computer-Crime Laws: Budapest, the CFAA, the UK and the Law at Homeیاساکانی تاوانی سایبەری: بوداپێست، CFAA، بەریتانیا و یاسا لە وڵاتی خۆمان
- Who Attacks, and Why?کێ هێرش دەکات و بۆچی؟
- Europe's GDPR: Rights, Breach Notification and FinesGDPRـی ئەوروپا: ماف، ئاگادارکردنەوەی دزەکردنی دراوە و سزای دارایی
- Jobs and Careers in ITکار و پیشە لە بواری IT
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- ISC2 Code of Ethics (preamble and the four canons)
- EC-Council Code of Ethics (18 points)
- ACM Code of Ethics and Professional Conduct (2018), as published by an ACM chapter
- NCSC (UK): Penetration testing guidance (scoping, reporting, limits)
- NIST CSRC Glossary: penetration testing (SP 800-115 and others)
- NIST SP 800-115, Technical Guide to Information Security Testing and Assessment (2008)
- Directive 2013/40/EU on attacks against information systems (article list)
- BleepingComputer: US DOJ will no longer prosecute ethical hackers under CFAA (19 May 2022)
- The Irish Times: Under Armour says 150 million MyFitnessPal accounts breached (30 March 2018)
- Security Affairs: Under Armour data breach affected about 150 million MyFitnessPal users (30 March 2018)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.