Chapterبەش 4 · Lectureوانە 4.3
Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
How ransomware works and why most attacks now steal data before they lock it (double extortion); the real stories of WannaCry, NotPetya and three recent cases, told with checked facts; whether a victim should pay; and the defence checklist that would have stopped each attack.
چۆن کار دەکات و بۆچی زۆربەی ئێستا پێش قفڵکردن دەدزن ()؛ چیرۆکی ڕاستەقینەی WannaCry، NotPetya و سێ ڕووداوی نوێ بە ڕاستیی پشکنراوەوە؛ ئایا قوربانی پارە بدات؛ هەروەها ئەو لیستەی بەرگری کە ڕێگەی لە هەریەک لەم دەگرت.
What you will learnچی فێر دەبیت
- Explain what ransomware does and describe the five stages of a typical attack.
- Explain double extortion and why a backup alone does not solve it.
- Tell the stories of WannaCry and NotPetya correctly, and say why one was a worm and the other a wiper.
- Use recent cases to show how attackers get in, and why paying is not advised.
- List the main ransomware defences and match each one to the attack it would have stopped.
- ڕوونی بکەیتەوە چی دەکات و پێنج قۆناغەکەی ئاسایی وەسف بکەیت.
- ڕوون بکەیتەوە و بۆچی تەنها چارەسەری ناکات.
- چیرۆکی WannaCry و NotPetya بە دروستی بگێڕیتەوە و بڵێیت بۆچی یەکێکیان بوو و ئەوی تریان .
- بە ڕووداوە نوێیەکان پیشان بدەیت چۆن دێنە ژوورەوە و بۆچی ئامۆژگاری ناکرێت پارە بدرێت.
- بەرگرییە سەرەکییەکانی دژی ڕیز بکەیت و هەریەکەیان بە ئەو ببەستیتەوە کە ڕێگەی لێ دەگرت.
What ransomware doesنەرمەواڵەی بارمتەگر چی دەکات
that locks or encrypts your and then demands money (a ransom) to give them back.
کە فایلەکانت قفڵ یان شفرە دەکات و پاشان پارە (پارەی ئازادکردن) داوا دەکات بۆ ئەوەی بیانگەڕێنێتەوە.
Ransomware is malware that holds your files hostage. It encrypts them: it scrambles every file with a secret key, so the files are still on the disk but nobody can open them. Then a note appears on the screen: pay, usually in a cryptocurrency such as Bitcoin, and you will receive the key that unlocks them. There is often a countdown, and the price goes up when it reaches zero.
جۆرێکە لە کە فایلەکانت بە بارمتە دەگرێت. فایلەکان شفرە دەکات: هەر فایلێک بە کلیلێکی نهێنی تێکدەدات، بۆیە فایلەکان هێشتا لەسەر دیسکەکەن بەڵام کەس ناتوانێت بیانکاتەوە. پاشان نامەیەک لەسەر شاشەکە دەردەکەوێت: پارە بدە، زۆرجار بە وەک Bitcoin، ئینجا ئەو کلیلەت پێ دەدرێت کە فایلەکان دەکاتەوە. زۆرجار کاتژمێرێکی پێچەوانە هەیە و کاتێک دەگاتە سفر نرخەکە بەرز دەبێتەوە.
Imagine a thief who slips into a shop in the bazaar at night. He does not take the goods. He puts a new lock on every cupboard, takes the only key with him and leaves a note: "Pay me and I will send you the key." The goods are still there, but the shopkeeper cannot sell anything. Today's thieves also photograph the account books and threaten to show them to everyone.
بیهێنە پێش چاوت دزێک بە شەو دزە دەکاتە ناو دوکانێکی بازاڕ. کاڵاکان نابات. قفڵێکی نوێ لە هەموو دۆڵابێک دەدات، تاکە کلیلەکە لەگەڵ خۆی دەبات و نامەیەک بەجێ دەهێڵێت: «پارەم بدە، کلیلەکەت بۆ دەنێرم.» کاڵاکان هێشتا لەوێن، بەڵام دوکاندار ناتوانێت هیچ بفرۆشێت. دزەکانی ئەمڕۆ وێنەی دەفتەری حیسابەکانیش دەگرن و هەڕەشە دەکەن کە بە هەمووانی پیشان دەدەن.
Where the analogy stops workingسنووری ئەم نموونەیە
A real lock can be broken with a hammer. Good encryption cannot be broken in any useful time, so without the key (or a backup) the files really are lost. And criminals often do not keep their word.
قفڵی ڕاستەقینە بە چەکوش دەشکێت. بەڵام باش لە هیچ ماوەیەکی بەسووددا ناشکێت، بۆیە بەبێ کلیلەکە (یان ) فایلەکان بە ڕاستی لەدەست دەچن. هەروەها تاوانباران زۆرجار بە قسەی خۆیان ناکەن.
What ransomware doesنەرمەواڵەی بارمتەگر چی دەکات
Who gets hit, and how oftenکێ دەکرێتە ئامانج و چەند جار
Ransomware mostly targets organisations — hospitals, factories, schools, city councils — because they cannot work without their data and may pay quickly. The FBI's report for 2025 counts ransomware among the most-reported threats to critical infrastructure: more than 3,600 complaints, with critical manufacturing, healthcare and government facilities hit hardest.
زیاتر ڕێکخراوەکان دەکاتە ئامانج — نەخۆشخانە، کارگە، قوتابخانە و شارەوانی — چونکە بەبێ ناتوانن کار بکەن و لەوانەیە بە خێرایی پارە بدەن. ڕاپۆرتی FBI بۆ ساڵی 2025 دەڵێت یەکێکە لەو زۆرترین ڕاپۆرتیان لەسەرە دژی : زیاتر لە 3,600 سکاڵا، کە زۆرترینیان لە پیشەسازیی گرنگ، تەندروستی و دامەزراوە حکومییەکاندا بوون.
Read such numbers carefully. The reported ransomware losses for 2025 were only about $32 million, because they count just what victims told the FBI: lost business, staff time and the cost of rebuilding are left out, and many victims report nothing at all.
ئەم جۆرە ژمارانە بە وریاییەوە بخوێنەوە. زیانی ڕاپۆرتکراوی بۆ ساڵی 2025 تەنها نزیکەی 32 ملیۆن دۆلار بوو، چونکە تەنها ئەوە دەژمێرێت کە قوربانییەکان بە FBIـیان گوتووە: کاری لەدەستچوو، کاتی کارمەندان و تێچووی دووبارە دروستکردنەوە تێیدا نین و زۆر قوربانیش هیچ ڕاپۆرت ناکەن.
How a ransomware attack unfoldsهێرشێکی نەرمەواڵەی بارمتەگر چۆن ڕوودەدات
A ransomware attack is rarely one quick click. It is a project that can take days or weeks. The cases in this lesson, and CISA's #StopRansomware Guide, show the same five stages:
بە دەگمەن تەنها یەک کرتەی خێرایە. پڕۆژەیەکە کە لەوانەیە چەند ڕۆژ یان چەند هەفتەیەک بخایەنێت. ڕووداوەکانی ئەم وانەیە و ڕێنمایی #StopRansomwareـی CISA هەمان پێنج قۆناغ پیشان دەدەن:
- Get inچوونە ژوورەوە
The attackers find one open door: a phishing e-mail, a stolen or guessed password on a remote-access server without MFA, or an internet-facing system that was never patched.
یەک دەرگای کراوە دەدۆزنەوە: ، دزراو یان مەزەندەکراو لەسەر کە MFAـی نییە، یان سیستەمێکی ڕووەو کە هەرگیز نەکراوە.
- Spread and look aroundبڵاوبوونەوە و گەڕان
Inside, they move from computer to computer, collect administrator passwords and look for the backups.
لە ناوەوە لە دەچن بۆ یەکێکی تر، بەڕێوەبەر کۆ دەکەنەوە و بەدوای دەگەڕێن.
- Steal a copyدزینی کۆپییەک
They copy valuable data to their own servers. This prepares the second threat: publishing it.
بەنرخ کۆپی دەکەن بۆ خۆیان. ئەمە دووەم ئامادە دەکات: بڵاوکردنەوەی.
- Encryptشفرەکردن
Often at night or at a weekend, they encrypt as many computers as possible at the same moment, and they delete or encrypt every backup they can reach.
زۆرجار بە شەو یان لە پشووی کۆتایی هەفتەدا، لە یەک کاتدا هەرچەندی بتوانن شفرە دەکەن و هەر بگەنە سەری دەیسڕنەوە یان شفرەی دەکەن.
- Demandداواکردن
A ransom note explains how to pay in cryptocurrency and threatens to publish the stolen data.
نامەی بارمتەکە ڕوون دەکاتەوە چۆن بە پارە بدرێت و هەڕەشە دەکات کە بڵاو دەکاتەوە.
How a ransomware attack unfoldsهێرشێکی نەرمەواڵەی بارمتەگر چۆن ڕوودەدات
The early stages are a chanceقۆناغە سەرەتاییەکان دەرفەتن
The attackers are often inside for days before anything is encrypted. The British Library's own report says they probably had access at least three days before the attack became visible. Spotting the early stages — strange logins, new administrator accounts, large uploads at night — can stop the attack before the files are locked.
زۆرجار چەند ڕۆژێک لە ناوەوەن پێش ئەوەی هیچ شتێک شفرە بکرێت. ڕاپۆرتی خودی کتێبخانەی بەریتانی دەڵێت بە ئەگەری زۆر لانیکەم سێ ڕۆژ پێش دەرکەوتنی دەستیان پێی ڕاگەیشتبوو. ناسینەوەی قۆناغە سەرەتاییەکان — نائاسایی، هەژمارێکی نوێی بەڕێوەبەر، ناردنی بڕێکی زۆر بە شەو — دەتوانێت پێش قفڵبوونی فایلەکان ڕابگرێت.
How a ransomware attack unfoldsهێرشێکی نەرمەواڵەی بارمتەگر چۆن ڕوودەدات
Double extortion: lock and leakبارمتەگرتنی دووقات: قفڵکردن و بڵاوکردنەوە
Early ransomware only locked files. Organisations learned to restore from backups and stopped paying. So the gangs added a second threat: before encrypting, they steal a copy of the data and say "pay, or we publish it". CISA calls this double extortion. Now a good backup solves only half of the problem: you get your files back, but the stolen copy is still in criminal hands.
سەرەتا تەنها فایلەکانی قفڵ دەکرد. ڕێکخراوەکان فێر بوون لە فایلەکان بگەڕێننەوە و ئیتر پارەیان نەدا. بۆیە دەستەکان دووەمیان زیاد کرد: پێش شفرەکردن کۆپییەکی دەدزن و دەڵێن «پارە بدە، دەنا بڵاوی دەکەینەوە». CISA ناوی ئەمە دەنێت . ئێستا باش تەنها نیوەی کێشەکە چارەسەر دەکات: فایلەکانت دەگەڕێنەوە، بەڵام کۆپییە دزراوەکە هێشتا لە دەستی تاوانباراندایە.
A method in which criminals first copy the victim's , then encrypt it, and demand money twice: to unlock the files and not to publish the stolen data.
شێوازێکی کە تێیدا تاوانباران سەرەتا قوربانییەکە کۆپی دەکەن، پاشان شفرەی دەکەن و بە دوو شێوە داوای پارە دەکەن: بۆ کردنەوەی فایلەکان و بۆ بڵاونەکردنەوەی دراوە دزراوەکان.
The trick works for the criminals. In its report on April–June 2026, the incident-response firm Coveware found data theft in 76% of the ransomware cases it handled. Paying is falling out of fashion, though: the share of victims who paid reached a record low, and when only data had been stolen just 15% paid.
ئەم فێڵە بۆ تاوانباران کار دەکات. کۆمپانیای Coveware، کە یارمەتیی قوربانییان دەدات لە کاتی ، لە ڕاپۆرتەکەیدا بۆ نیسان تا حوزەیرانی 2026 لە سەدا 76ی ئەو ڕووداوانەی کە کاری لەسەر کردبوون دزینی دۆزیەوە. بەڵام پارەدان کەم دەبێتەوە: ڕێژەی ئەو قوربانییانەی پارەیان دا گەیشتە نزمترین ئاستی خۆی؛ کاتێک تەنها دزرابوو، تەنها لە سەدا 15یان پارەیان دا.
Many gangs also rent their ransomware to other criminals, who carry out the attacks and share the profit. This business model is called ransomware-as-a-service. Rhysida, the group behind two of the recent cases in this lesson, works this way. How criminals run malware as a business is explained in Malware today is a business.
زۆر دەستەش بە کرێ دەدەن بە تاوانبارانی تر کە ئەنجام دەدەن و قازانجەکە دابەش دەکەن. ئەم شێوازە بازرگانییە ناوی . Rhysida، ئەو دەستەیەی لە پشت دوو ڕووداوی نوێی ئەم وانەیەوەیە، بەم شێوەیە کار دەکات. تاوانباران چۆن وەک بازرگانی بەڕێوە دەبەن لە نەرمەواڵەی زیانبەخشی ئەمڕۆ بازرگانییە ڕوون کراوەتەوە.
WannaCry (2017): the worm that hit hospitalsWannaCry (2017): ئەو کرمەی بەر نەخۆشخانەکان کەوت
On 12 May 2017 a ransomware called WannaCry spread around the world in a single day. In the first days it infected about 200,000 computers (Europol's count) in more than 150 countries — in hospitals, companies and government offices — freezing their files. Each infected computer showed a note asking for about $300 in Bitcoin.
لە 12ی ئایاری 2017دا بە ناوی WannaCry لە یەک ڕۆژدا بە جیهاندا بڵاو بووەوە. لە یەکەم ڕۆژەکاندا نزیکەی 200,000 لە زیاتر لە 150 وڵاتدا گرت (ژمارەکەی Europol) — لە نەخۆشخانە، کۆمپانیا و فەرمانگە حکومییەکاندا — و فایلەکانیانی بەستەڵەک کرد. هەر تووشبوو نامەیەکی پیشان دەدا کە داوای نزیکەی 300 دۆلاری بە Bitcoin دەکرد.
WannaCry was also a worm: it did not wait for anyone to click. It searched networks for Windows computers that still ran an old file-sharing service (SMBv1) and used a flaw in it to copy itself to the next machine. Microsoft had published the patch for that flaw (MS17-010) on 14 March 2017 — two months before the attack. Every computer WannaCry infected was one that had not been updated.
WannaCry هەروەها بوو: چاوەڕێی کرتەی کەسی نەدەکرد. لە بەدوای ئەو دەگەڕا کە Windowsـیان لەسەر بوو و هێشتا خزمەتگوزارییەکی کۆنی هاوبەشکردنی فایل (SMBv1) تێیاندا کاری دەکرد و ئەو خزمەتگوزارییەی بەکار دەهێنا بۆ ئەوەی خۆی کۆپی بکات بۆ ئامێری داهاتوو. Microsoft لە 14ی ئازاری 2017دا (MS17-010) بڵاو کردبووەوە — دوو مانگ پێش . هەر WannaCry گرتبێتی، بۆ نەکرابوو.
How WannaCry spread in May 2017: 200,000 computers in 150 countries, a $300-600 Bitcoin ransom, and the leaked NSA tool EternalBlue that attacked SMB.
بڵاوبوونەوەی WannaCry لە ئایاری 2017: 200 هەزار لە 150 وڵاتدا، بارمتەی 300 تا 600 دۆلار بە Bitcoin، هەروەها EternalBlue، ئامرازە دزەکراوەکەی NSA دژی SMB.
Plays 0:00-2:17: the outbreak, the ransom, EternalBlue, SMB and the Shadow Brokers leak; stops before the Windows XP part. Microsoft's patch came on 14 March 2017, a month before the leak.
لە 0:00 تا 2:17 پەخش دەبێت: بڵاوبوونەوەکە، پارەی بارمتەکە، EternalBlue، SMB و دزەپێکردنەکەی Shadow Brokers؛ پێش بەشی Windows XP ڕادەوەستێت. ئاگادار بە: Microsoft لە 14ی ئازاری 2017 دەرچوو، مانگێک پێش دزەپێکردنەکە.
WannaCry (2017): the worm that hit hospitalsWannaCry (2017): ئەو کرمەی بەر نەخۆشخانەکان کەوت
WannaCry and the NHSWannaCry و NHS
In England's National Health Service (NHS), at least 81 of 236 hospital trusts and 595 GP practices were affected, and about 19,000 appointments were cancelled. No NHS organisation paid the ransom. The UK's National Audit Office concluded that the attack could have been prevented by basic IT security practice: installing updates, and managing the firewalls that face the internet. The US government later attributed WannaCry to North Korea.
لە خزمەتگوزاریی تەندروستیی نیشتیمانیی ئینگلتەرا (NHS)، لانیکەم 81 لە 236 دەستەی نەخۆشخانە و 595 نۆرینگەی پزیشکی گشتی تووش بوون و نزیکەی 19,000 چاوپێکەوتنی نەخۆش هەڵوەشێنرایەوە. هیچ ڕێکخراوێکی NHS بارمتەکەی نەدا. نووسینگەی نیشتیمانیی وردبینیی بەریتانیا گەیشتە ئەو ئەنجامەی کە دەکرا بە کارە سەرەتاییەکانی IT ڕێگە لە بگیرێت: دامەزراندنی و بەڕێوەبردنی ئەو ڕوویان لە . حکومەتی ئەمریکا دواتر WannaCryـی دایە پاڵ کۆریای باکوور.
WannaCry (2017): the worm that hit hospitalsWannaCry (2017): ئەو کرمەی بەر نەخۆشخانەکان کەوت
EternalBlue: a leaked exploitEternalBlue: ئێکسپلۆیتێکی دزەکردوو
The tool WannaCry used to spread is called EternalBlue. An exploit is a piece of code that takes advantage of one particular vulnerability. EternalBlue attacks a flaw in SMBv1, the old Windows service for sharing files and printers over a network. It was developed by the US National Security Agency (NSA) and leaked to the public in 2017 by a group calling itself the Shadow Brokers. Criminals then built it into WannaCry, and six weeks later NotPetya used it too.
ئەو ئامرازەی WannaCry بۆ بڵاوبوونەوە بەکاری دەهێنا ناوی EternalBlueـە. پارچە کۆدێکە کە سوود لە دیاریکراو وەردەگرێت. EternalBlue هێرش دەکاتە سەر لە SMBv1، خزمەتگوزارییە کۆنەکەی Windows بۆ هاوبەشکردنی فایل و چاپەر لە . ئاژانسی ئاسایشی نیشتیمانیی ئەمریکا (NSA) دروستی کردبوو و لە ساڵی 2017دا گرووپێک کە خۆی ناو دەنا Shadow Brokers بڵاوی کردەوە. پاشان تاوانباران خستیانە ناو WannaCryـەوە و شەش هەفتە دواتر NotPetyaـش بەکاری هێنا.
A piece of code or a method that takes advantage of a specific to make a system do something it should not, such as run the attacker's program. EternalBlue was a famous exploit.
پارچە کۆدێک یان شێوازێکە کە دیاریکراو دەقۆزێتەوە بۆ ئەوەی سیستەمێک کارێک بکات کە نابێت بیکات، وەک جێبەجێکردنی بەرنامەی . EternalBlue ئێکسپلۆیتێکی بەناوبانگ بوو.
NotPetya (2017): ransomware in disguiseNotPetya (2017): نەرمەواڵەی بارمتەگری ساختە
Six weeks after WannaCry, on 27 June 2017, another attack began in Ukraine. NotPetya arrived through an update of M.E.Doc, a tax-accounting program used by many Ukrainian businesses. The attackers had hidden it inside the software update itself, so the companies installed it themselves, trusting their supplier. This is a supply-chain attack.
شەش هەفتە دوای WannaCry، لە 27ی حوزەیرانی 2017دا، تر لە ئۆکرانیا دەستی پێکرد. NotPetya لە ڕێگەی M.E.Docـەوە هات، بەرنامەیەکی ژمێریاریی باج کە زۆرێک لە کۆمپانیاکانی ئۆکرانیا بەکاریان دەهێنا. لە ناو خودی شاردبوویانەوە، بۆیە کۆمپانیاکان خۆیان دایانمەزراند، چونکە متمانەیان بە دابینکەرەکەیان هەبوو. ئەمە .
Inside each network NotPetya spread on its own, again with EternalBlue. Multinational companies with an office in Ukraine were infected worldwide — among them the shipping company Maersk, the drug maker Merck, FedEx and Saint-Gobain. Global losses are estimated at more than $10 billion.
لە ناو هەر NotPetya خۆی بڵاو دەبووەوە، دیسان بە EternalBlue. کۆمپانیا نێودەوڵەتییەکان کە نووسینگەیەکیان لە ئۆکرانیا هەبوو لە سەرتاسەری جیهاندا تووش بوون — لەوانە کۆمپانیای گواستنەوەی دەریایی Maersk، کۆمپانیای دەرمانسازیی Merck، FedEx و Saint-Gobain. زیانی جیهانی بە زیاتر لە 10 ملیار دۆلار مەزەندە دەکرێت.
NotPetya showed a ransom note, but it was really a wiper: malware built to destroy. Its encryption could not be undone, so victims who paid got nothing back. The attackers collected only about $10,000 — a sign that money was not the goal. In February 2018 the United States and the United Kingdom attributed the attack to the Russian military; Russia denied it.
NotPetya نامەی بارمتەی پیشان دەدا، بەڵام لە ڕاستیدا بوو: کە بۆ لەناوبردن دروست کرابوو. هەڵنەدەوەشایەوە، بۆیە ئەو قوربانییانەی پارەیان دا هیچیان بۆ نەگەڕایەوە. تەنها نزیکەی 10,000 دۆلاریان کۆ کردەوە — نیشانەیەک کە پارە ئامانج نەبوو. لە شوباتی 2018دا ئەمریکا و شانشینی یەکگرتوو دایە پاڵ سوپای ڕووسیا؛ ڕووسیا ئەمەی ڕەت کردەوە.
built to destroy for good, often while pretending to be . There is no key that brings the files back, so only help.
جۆرێکە لە کە بۆ لەناوبردنی هەمیشەیی دروست کراوە و زۆرجار خۆی وەک پیشان دەدات. هیچ کلیلێک نییە فایلەکان بگەڕێنێتەوە، بۆیە تەنیا یارمەتی دەدەن.
NotPetya step by step: the poisoned M.E.Doc update, the worm spreading with EternalBlue, the fake ransom note of a wiper, and Maersk and Merck.
NotPetya هەنگاو بە هەنگاو: ژەهراویی M.E.Doc، کە بە EternalBlue بڵاو بووەوە، نامەی بارمتەی ساختەی ، هەروەها Maersk و Merck.
Plays 8:37-13:34: the poisoned M.E.Doc update, the worm spreading with Mimikatz and EternalBlue, a wiper posing as ransomware, and the global damage.
لە 8:37 تا 13:34 پەخش دەبێت: ژەهراویی M.E.Doc، کە بە Mimikatz و EternalBlue بڵاو بووەوە، کە خۆی وەک نیشان دەدا، هەروەها زیانە جیهانییەکە.
Three recent casesسێ ڕووداوی نوێ
The course notes list three newer attacks. Here they are with the facts checked against reliable reports. Notice what they share: in every case data was stolen and systems were disrupted.
تێبینییەکانی کۆرسەکە سێ نوێتر ڕیز دەکەن. ئەمانە لێرەدان، بە ڕاستییەکانیانەوە کە لەگەڵ ڕاپۆرتە متمانەپێکراوەکاندا بەراورد کراون. سەرنج بدە چییان هاوبەشە: لە هەموویاندا دزرا و سیستەمەکان تێکچوون.
| Caseڕووداو | What happenedچی ڕوویدا | Impactکاریگەری | Recoveryچاکبوونەوە |
|---|---|---|---|
| British Library (October 2023)کتێبخانەی بەریتانی (تشرینی یەکەمی 2023) | The Rhysida gang got in, probably through a remote-access server that had no MFA, then encrypted and destroyed systems.دەستەی Rhysida چووە ژوورەوە، بە ئەگەری زۆر لە ڕێگەی کە MFAـی نەبوو، پاشان سیستەمەکانی شفرە کرد و تێکی دان. | The Library refused to pay. About 600 GB of its data was published; the catalogue and most online services were down for months.کتێبخانەکە ڕازی نەبوو پارە بدات. نزیکەی 600 GB لە بڵاو کرایەوە؛ کەتەلۆگەکە و زۆربەی خزمەتگوزارییە ئۆنلاینەکانی چەند مانگێک وەستان. | The main catalogue came back, read-only, on 15 January 2024. Rebuilding took most of 2024.کەتەلۆگە سەرەکییەکە لە 15ی کانوونی دووەمی 2024دا گەڕایەوە، . دووبارە دروستکردنەوە زۆربەی ساڵی 2024ی خایاند. |
| Blue Yonder (November 2024)Blue Yonder (تشرینی دووەمی 2024) | Ransomware hit the hosted services of Blue Yonder, whose software plans staff shifts, stock and deliveries for big retailers. بەر خزمەتگوزارییە میوانداریکراوەکانی Blue Yonder کەوت، کە دەوامی کارمەندان، کۆگا و گەیاندن بۆ فرۆشگا گەورەکان پلان دەکات. | Starbucks had to schedule and pay staff by hand; Morrisons and Sainsbury's had problems with stock systems.Starbucks ناچار بوو دەوام و مووچەی کارمەندان بە دەست ڕێک بخات؛ Morrisons و Sainsbury'sـیش کێشەیان لە سیستەمەکانی کۆگادا هەبوو. | Outside security firms helped restore services; some customers were back to normal within days.کۆمپانیاکانی دەرەوەی یارمەتیی گەڕاندنەوەی خزمەتگوزارییەکانیان دا؛ هەندێک کڕیار لە چەند ڕۆژێکدا گەڕانەوە دۆخی ئاسایی. |
| Rhysida (2023–2024)دەستەی Rhysida (2023–2024) | A ransomware-as-a-service group active since May 2023. Victims include the Chilean Army (May 2023) and the City of Columbus, Ohio (July 2024).دەستەیەکی کە لە ئایاری 2023ەوە چالاکە. لە قوربانییەکانی: سوپای چیلی (ئایاری 2023) و شاری Columbus لە Ohio (تەممووزی 2024). | Stolen data was leaked: internal army documents, and about 3.1 TB from Columbus in August 2024. بڵاو کرایەوە: بەڵگەنامە ناوخۆییەکانی سوپا و نزیکەی 3.1 TB لە Columbus لە ئابی 2024دا. | Columbus did not pay. It told about 500,000 people that their personal data may have been exposed.Columbus پارەی نەدا. ئاگاداری نزیکەی 500,000 کەسی کردەوە کە لەوانەیە ئاشکرا بووبێت. |
Three recent casesسێ ڕووداوی نوێ
Behind the headlinesلە پشت سەردێڕەکانەوە
The reports add details that matter for defence:
ڕاپۆرتەکان وردەکاریی تر زیاد دەکەن کە بۆ بەرگری گرنگن:
- British Library. Old software that would not run on new hardware slowed the rebuild. The gang put the stolen data up for auction at 20 bitcoin (about $745,000 at the time), then published most of it.
- Blue Yonder. A new gang, Termite, later claimed the attack and said it had stolen about 680 GB.
- Rhysida. CISA says the group usually gets in with stolen but valid passwords on VPNs that have no MFA. For Columbus it claimed 6.5 TB and asked buyers for 30 bitcoin; nobody bought. The city says it never received a ransom demand.
- کتێبخانەی بەریتانی. کۆن کە لەسەر نوێ کار ناکات دووبارە دروستکردنەوەی خاو کردەوە. دەستەکە خستە هەراجەوە بە 20 بیتکۆین (ئەو کاتە نزیکەی 745,000 دۆلار)، پاشان زۆربەی بڵاو کردەوە.
- Blue Yonder. دواتر دەستەیەکی نوێ بە ناوی Termite بەرپرسیارێتیی گرتە ئەستۆ و گوتی نزیکەی 680 GBـی دزیوە.
- Rhysida. CISA دەڵێت ئەم دەستەیە بە زۆری بە دزراو بەڵام دروست لەسەر VPNـی بێ MFA دەچێتە ژوورەوە. بۆ Columbus گوتی 6.5 TBـی هەیە و 30 بیتکۆینی لە کڕیاران داوا کرد؛ کەس نەیکڕی. شارەوانییەکە دەڵێت هەرگیز داوای بارمتەی پێ نەگەیشتووە.
Should a victim pay?ئایا قوربانی پارە بدات؟
Paying can look like the fastest way out, but police and national agencies advise against it. The UK's National Cyber Security Centre (NCSC) and UK law enforcement do not encourage or support paying a ransom. Their reasons:
پارەدان لەوانەیە وەک خێراترین ڕێگای دەربازبوون دەربکەوێت، بەڵام پۆلیس و ئاژانسە نیشتیمانییەکانی ئامۆژگاری دەکەن نەیدەیت. ناوەندی نیشتیمانیی بەریتانیا (NCSC) و دەزگاکانی جێبەجێکردنی یاسای بەریتانیا هانی پارەدانی بارمتە نادەن و پشتگیریی ناکەن. هۆکارەکانیان:
- There is no guarantee that you will get your data or computers back.
- Your computers are still infected, and the way the attackers got in is still open.
- You are funding criminal groups, and their next attack.
- You are more likely to be targeted again.
- Some "ransomware" cannot be undone at all: NotPetya was a wiper.
- A stolen copy of the data can still be published or sold after payment.
- هیچ گەرەنتییەک نییە کە یان بۆ بگەڕێتەوە.
- هێشتا تووشبوون و ئەو ڕێگایەی پێیدا هاتنە ژوورەوە هێشتا کراوەیە.
- پارە دەدەیت بە دەستە تاوانکارەکان و بە داهاتوویان.
- ئەگەری ئەوە زیاتر دەبێت کە دیسان بکرێیتە ئامانج.
- هەندێک «» هەرگیز هەڵناوەشێتەوە: NotPetya بوو.
- کۆپییە دزراوەکەی دوای پارەدانیش هێشتا دەکرێت بڵاو بکرێتەوە یان بفرۆشرێت.
The real answer is preparation, so that paying is never the only choice. That is the next screen.
وەڵامی ڕاستەقینە خۆئامادەکردنە، بۆ ئەوەی پارەدان هەرگیز تاکە بژاردە نەبێت. ئەمە بابەتی پەڕەی داهاتووە.
The defence checklistلیستی بەرگری
Every case in this lesson had a door that a known measure would have closed. CISA's #StopRansomware Guide lists the measures. These are the most important ones, each with the case that shows why it matters:
هەر ڕووداوێکی ئەم وانەیە دەرگایەکی هەبوو کە ڕێکارێکی ناسراو دایدەخست. ڕێنمایی #StopRansomwareـی CISA ئەم ڕێکارانە ڕیز دەکات. ئەمانە گرنگترینەکانن، هەریەکەیان لەگەڵ ئەو ڕووداوەی پیشان دەدات بۆچی گرنگە:
| Measureڕێکار | What to doچی بکەیت | Why — the caseبۆچی — ڕووداوەکە |
|---|---|---|
| Offline, tested backups ئۆفلاین و تاقیکراو | Keep backups offline or immutable, encrypted and tested; keep ready-made system images to rebuild computers quickly. ئۆفلاین یان نەگۆڕ، شفرەکراو و تاقیکراو بهێڵەوە؛ وێنەی ئامادەی سیستەم هەڵبگرە بۆ ئەوەی بە خێرایی دووبارە دروست بکەیتەوە. | Ransomware hunts for backups it can reach; the British Library's restore was slow. بەدوای ئەو دەگەڕێت کە دەگاتە سەریان؛ گەڕاندنەوەی کتێبخانەی بەریتانی خاو بوو. |
| Phishing-resistant MFAMFAـی بەرگەگر لە بەرامبەر | Use it on e-mail, VPN and every remote-access server — including new ones.لەسەر ، VPN و هەموو بەکاری بهێنە — نوێکانیشەوە. | British Library: a server without MFA. Rhysida: VPN logins without MFA.کتێبخانەی بەریتانی: بێ MFA. Rhysida: VPN بێ MFA. |
| Patch first what faces the internetیەکەم ئەوە بکە کە ڕووی لە | Patch internet-facing systems and known exploited vulnerabilities first; replace systems that no longer get updates.سەرەتا ئەو سیستەمانە بکە کە ڕوویان لە ، هەروەها کە ئێستا بەکار دەهێنرێن؛ ئەو سیستەمانە بگۆڕە کە ئیتر وەرناگرن. | WannaCry: the patch was two months old.WannaCry: دوو مانگ پێشتر بڵاو کرابووەوە. |
| Close the remote doorsدەرگا دوورەکان دابخە | Do not expose remote desktop (RDP) to the internet; switch off SMBv1 and block port 445 at the edge.ڕێگە مەدە Remote Desktop (RDP) ڕووی لە بێت؛ SMBv1 بکوژێنەوە و پۆرتی 445 لە لێواری دابخە. | WannaCry, and many ransomware entries through remote access.WannaCry و زۆرێک لە چوونە ژوورەوەکانی لە ڕێگەی . |
The defence checklistلیستی بەرگری
More defences: limit the damageبەرگریی زیاتر: زیانەکە سنووردار بکە
Four more measures from CISA's guide limit how far attackers get and how fast you recover. The FBI's report for 2025 gives the same advice and adds two points: remove default passwords, and use detection tools (EDR) that notice an attacker moving from computer to computer.
چوار ڕێکاری تری ڕێنماییەکەی CISA سنوور بۆ ئەوە دادەنێن کە تا کوێ دەڕۆن و تۆ چەند خێرا چاک دەبیتەوە. ڕاپۆرتی FBI بۆ ساڵی 2025 هەمان ئامۆژگاری دەدات و دوو خاڵ زیاد دەکات: لابە، هەروەها ئامرازی دۆزینەوە (EDR) بەکار بهێنە کە هەست بە دەکەن کە لە دەچێت بۆ یەکێکی تر.
| Measureڕێکار | What to doچی بکەیت | Why — the caseبۆچی — ڕووداوەکە |
|---|---|---|
| Segment the network | Split the network into zones, so one infected computer cannot reach everything. بکە بە چەند ناوچەیەک، بۆ ئەوەی تووشبوو نەگاتە هەموو شتێک. | NotPetya and WannaCry spread through whole company networks.NotPetya و WannaCry بە هەموو کۆمپانیاکاندا بڵاو بوونەوە. |
| Least privilege | Give each account only the rights it needs; use separate administrator accounts.تەنها ئەو مافانە بدە بە هەر هەژمارێک کە پێویستییەتی؛ هەژماری جیای بەڕێوەبەر بەکار بهێنە. | Attackers collect administrator passwords to spread. بەڕێوەبەر کۆ دەکەنەوە بۆ بڵاوبوونەوە. |
| Awareness and filtering و پاڵاوتن | Train staff to spot and report phishing; filter e-mail attachments; switch off Office macros in e-mailed files.کارمەندان ڕابهێنە بۆ ناسینەوە و ڕاپۆرتکردنی ؛ بپاڵێوە؛ macroـی Office لەو فایلانەدا بکوژێنەوە کە بە دێن. | Phishing is one of the common ways in (see Social engineering). یەکێکە لە ڕێگا باوەکانی چوونە ژوورەوە (بڕوانە ئەندازیاریی کۆمەڵایەتی). |
| A practised response planپلانێکی ڕاهێنراوی وەڵامدانەوە | Write an incident response plan, keep paper and offline copies, and practise it.پلانێکی بنووسە، کۆپیی کاغەزی و ئۆفلاینی هەڵبگرە و ڕاهێنانی لەسەر بکە. | During an attack the network and e-mail may be down.لە کاتی لەوانەیە و کار نەکەن. |
The defence checklistلیستی بەرگری
Recovering without payingگەڕاندنەوە بەبێ پارەدان
The animation shows why the offline copy matters. The ransomware locks every file it can reach — including a backup disk that was still plugged in. The disk that was unplugged is the one that saves the day: the team cleans and rebuilds the computer and restores the files from it. No key is needed.
جووڵەکە پیشان دەدات بۆچی کۆپیی ئۆفلاین گرنگە. هەموو ئەو فایلانە قفڵ دەکات کە دەیانگاتێ — بە دیسکێکی کە هێشتا بەستراو بوو. ئەو دیسکەی جیا کرابووەوە ئەوەیە کە ڕزگاری دەکات: تیمەکە پاک دەکاتەوە و دووبارە دروستی دەکاتەوە و فایلەکان لەو دیسکەوە دەگەڕێنێتەوە. هیچ کلیلێک پێویست نییە.
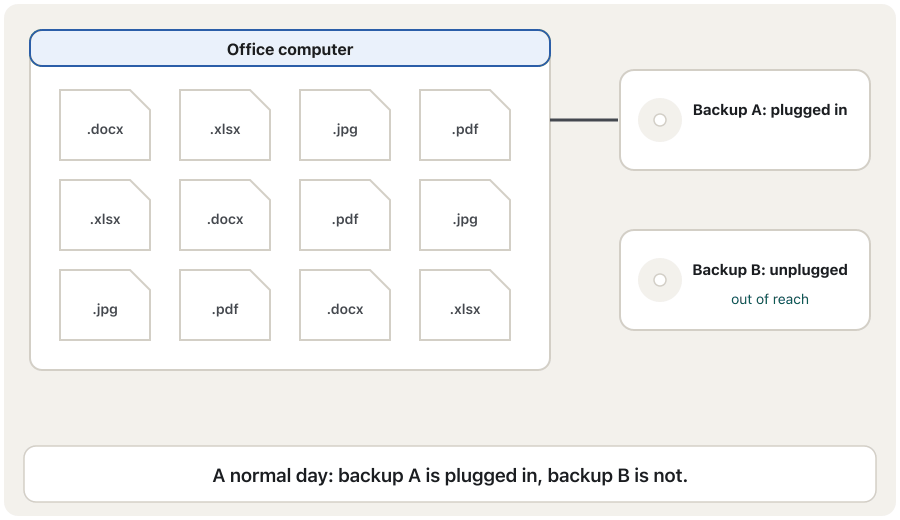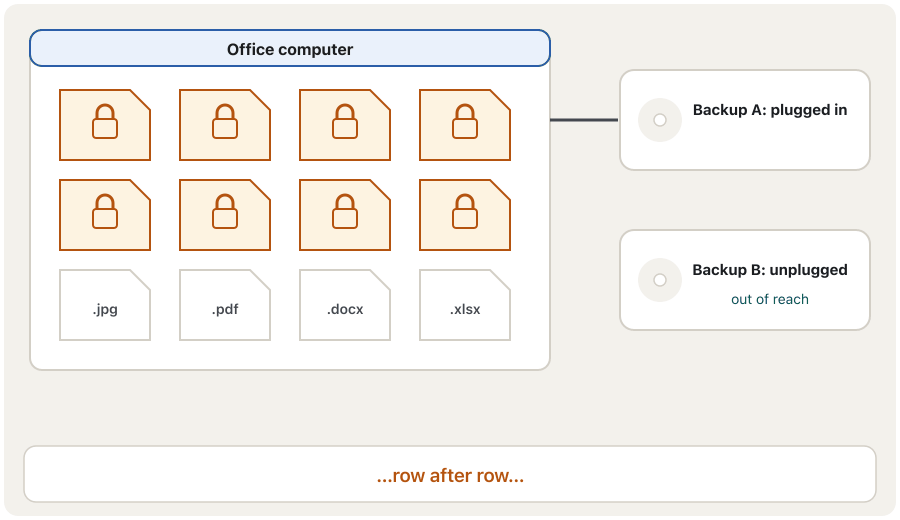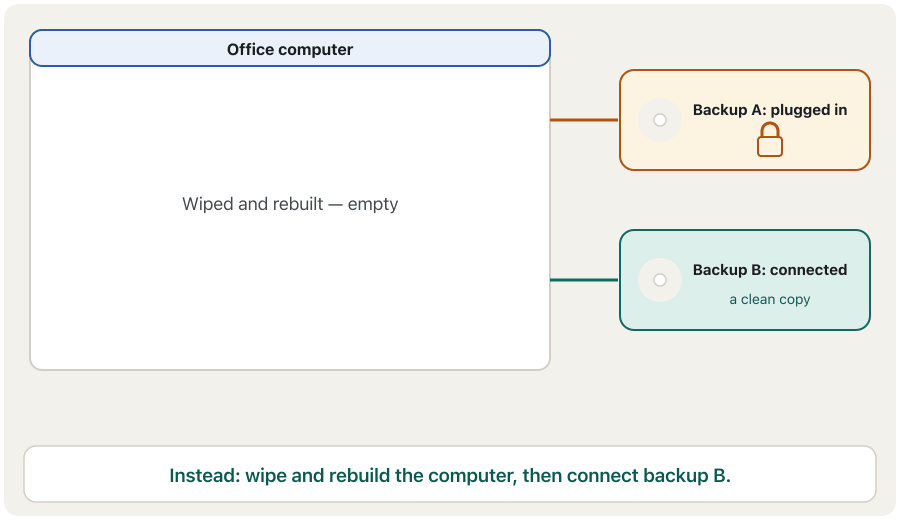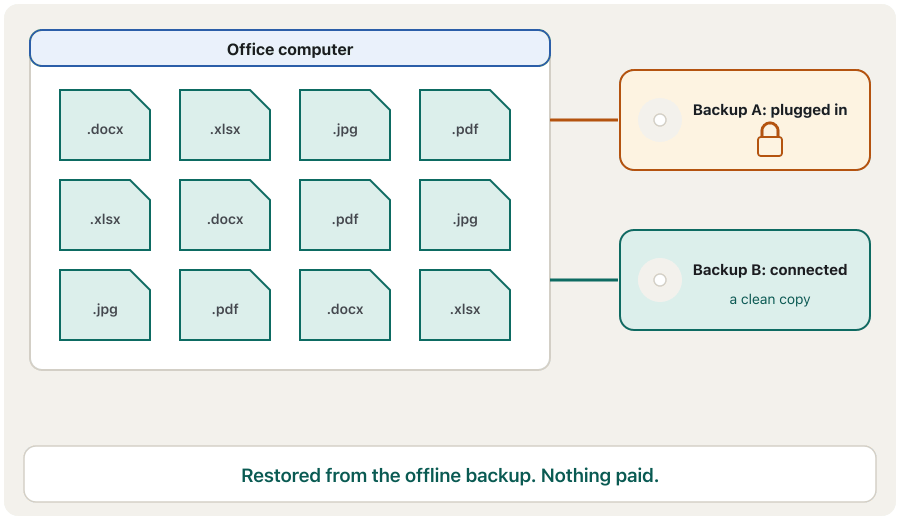
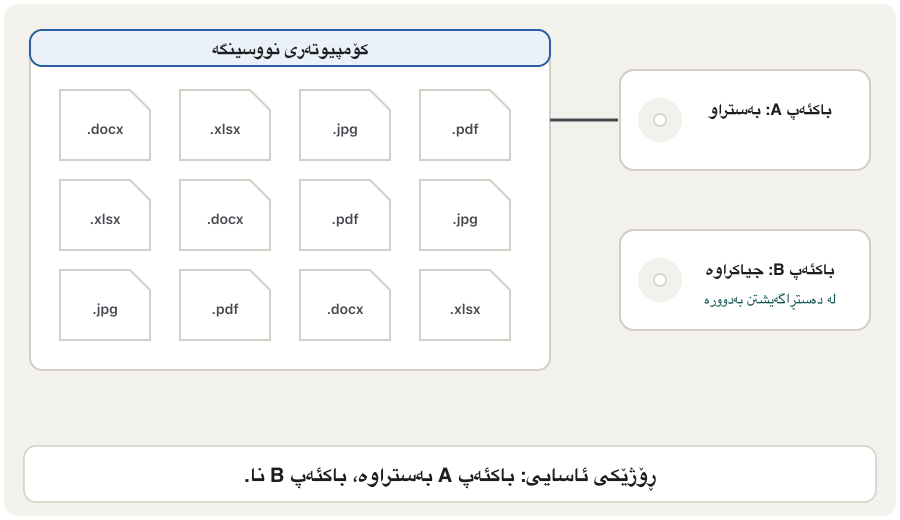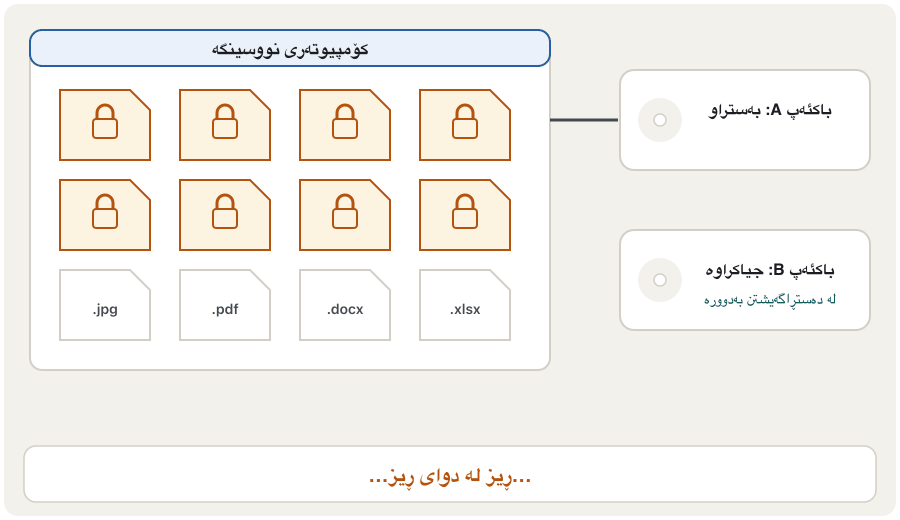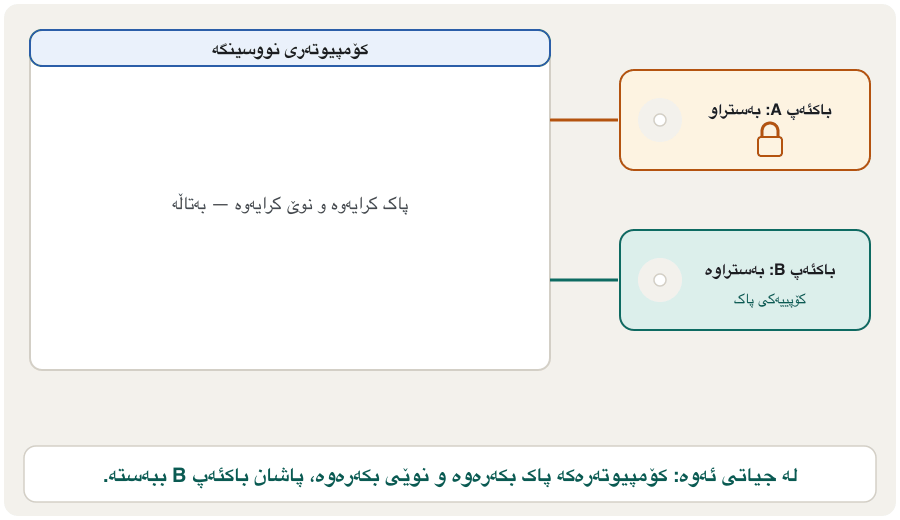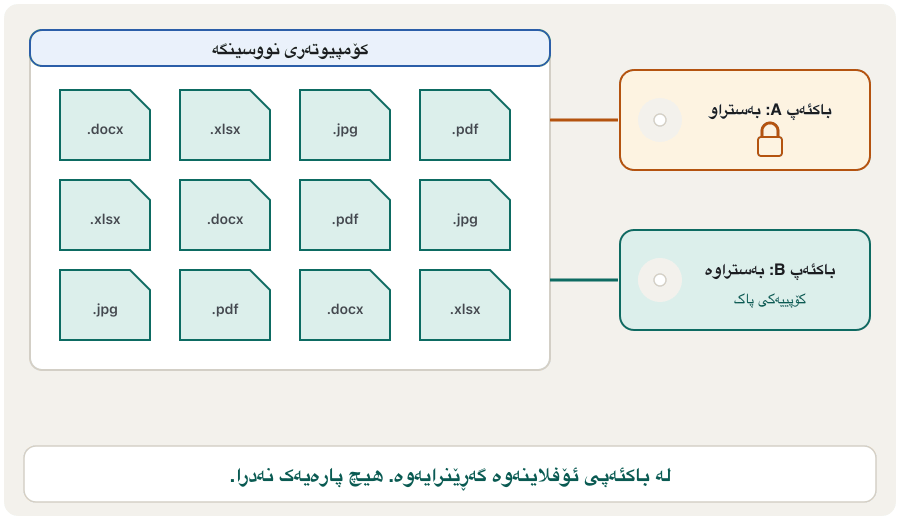
Two warnings from CISA's checklist: restore the most important services first, and make sure both the backup and the rebuilt system are clean, so the attack does not start again. And remember double extortion: restoring brings the files back, but it does not undo the theft.
دوو ئاگاداری لە لیستەکەی CISA: سەرەتا گرنگترین خزمەتگوزارییەکان بگەڕێنەوە؛ هەروەها دڵنیا ببەوە کە هەم و هەم سیستەمە نوێکراوەکە پاکن، بۆ ئەوەی دووبارە دەست پێ نەکاتەوە. هەروەها لەبیر مەکە: گەڕاندنەوە فایلەکان دەگەڕێنێتەوە، بەڵام دزییەکە هەڵناوەشێنێتەوە.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| "We have backups, so ransomware can't hurt us."« هەیە، بۆیە زیانمان پێ ناگەیەنێت.» | Backups the network can reach get encrypted too, and stolen data can still be leaked.ئەو دەیانگاتێ ئەوانیش شفرە دەکرێن و هێشتا دەکرێت بڵاو بکرێتەوە. | Keep an offline or immutable copy, test restores, and protect against data theft too.کۆپییەکی ئۆفلاین یان نەگۆڕ هەڵبگرە، گەڕاندنەوە تاقی بکەرەوە و هەروەها دژی دزینی خۆت بپارێزە. |
| "Paying gets our files back."«پارەدان فایلەکانمان بۆ دەگەڕێنێتەوە.» | There is no guarantee; a wiper such as NotPetya cannot be decrypted; you fund criminals and may be hit again.هیچ گەرەنتییەک نییە؛ وەک NotPetya ناکرێت؛ پارە دەدەیت بە تاوانباران و لەوانەیە دیسان لێت بدرێتەوە. | Prepare so that paying is never the only choice; get expert and law-enforcement help.خۆت ئامادە بکە بۆ ئەوەی پارەدان هەرگیز تاکە بژاردە نەبێت؛ یارمەتی لە پسپۆڕان و دەزگاکانی یاسا وەربگرە. |
| "Ransomware only comes in through e-mail attachments."« تەنها لە ڕێگەی دێت.» | WannaCry spread as a worm with no click; Rhysida uses stolen VPN passwords.WannaCry وەک بەبێ کرتە بڵاو بووەوە؛ Rhysida دزراوی VPN بەکار دەهێنێت. | Patch, close exposed remote access and use MFA, as well as training staff. بکە، ئەو دەرگایانەی دابخە کە ڕوویان لە و MFA بەکار بهێنە، لەگەڵ ڕاهێنانی کارمەنداندا. |
| "Once the files are restored, the incident is over."«کە فایلەکان گەڕێنرانەوە، ڕووداوەکە تەواو بووە.» | The attackers' way in, and the data they stole, are still there.ڕێگای چوونە ژوورەوەی و ئەو دزیویانە هێشتا ماون. | Find and close the entry point, reset passwords, check what was stolen and learn the lessons.خاڵی چوونە ژوورەوە بدۆزەرەوە و دایبخە، بگۆڕە، بپشکنە چی دزراوە و وانەکان فێر ببە. |
| "Old systems are fine as long as they still work."«سیستەمە کۆنەکان باشن تا ئەو کاتەی هێشتا کار دەکەن.» | WannaCry hit unpatched and unsupported Windows computers.WannaCry بەر Windowsـی و بێپشتگیری کەوت. | Update, isolate or replace systems that no longer receive security patches.ئەو سیستەمانەی ئیتر وەرناگرن نوێیان بکەرەوە، جیایان بکەرەوە یان بیانگۆڕە. |
Exercisesڕاهێنانەکان
Dilan runs a small clinic. All patient records are on one server. The only backup is a USB disk that is always plugged into that server. Staff log in from home with only a password. Windows updates are installed "when someone remembers". Name the three biggest ransomware risks and one fix for each.
دیلان نۆرینگەیەکی بچووک بەڕێوە دەبات. هەموو تۆمارەکانی نەخۆشان لەسەر یەک . تاکە دیسکێکی USBـیە کە هەمیشە بەو بەستراوە. کارمەندان لە ماڵەوە تەنها بە دەچنە ژوورەوە. Windows «هەر کاتێک کەسێک بیری کەوتەوە» دادەمەزرێنرێن. سێ گەورەترین ناو ببە و بۆ هەریەکەیان چارەسەرێک بنووسە.
Show answerوەڵامەکە پیشان بدە
- Connected backup — ransomware on the server will encrypt it too. Fix: a second copy that is offline (unplugged after each backup) or immutable, encrypted, and tested by a real restore.
- Remote login with only a password — a stolen or guessed password is enough to get in (British Library, Rhysida). Fix: phishing-resistant MFA on remote access.
- Irregular updates — known flaws stay open (WannaCry). Fix: automatic updates and a fixed patch day, internet-facing systems first.
- بەستراو — لەسەر ئەویش شفرە دەکات. چارەسەر: کۆپییەکی دووەم کە ئۆفلاین بێت (دوای هەر جیا بکرێتەوە) یان نەگۆڕ بێت، شفرەکراو بێت و بە گەڕاندنەوەیەکی ڕاستەقینە تاقی کرابێتەوە.
- چوونە ژوورەوە لە دوورەوە تەنها بە — دزراو یان مەزەندەکراو بەسە بۆ چوونە ژوورەوە (کتێبخانەی بەریتانی، Rhysida). چارەسەر: MFAـی بەرگەگر لە بەرامبەر بۆ .
- ناڕێک — کە ناسراون کراوە دەمێننەوە (WannaCry). چارەسەر: خۆکار و ڕۆژێکی دیاریکراو بۆ ، سەرەتا ئەو سیستەمانەی ڕوویان لە .
Compare the two attacks of 2017: how each one got in or spread, what it really was, and whether paying could help.
دوو 2017 بەراورد بکە: هەریەکەیان چۆن هاتە ژوورەوە یان بڵاو بووەوە، لە ڕاستیدا چی بوو و ئایا پارەدان یارمەتی دەدا.
Show answerوەڵامەکە پیشان بدە
| Featureتایبەتمەندی | WannaCry | NotPetya |
|---|---|---|
| Dateڕێکەوت | 12 May 201712ی ئایاری 2017 | 27 June 201727ی حوزەیرانی 2017 |
| Way in / spreadچوونە ژوورەوە / بڵاوبوونەوە | Worm through the SMBv1 flaw (EternalBlue) on unpatched Windows لە ڕێگەی SMBv1 (EternalBlue) لەسەر Windowsـی | A poisoned M.E.Doc software update, then EternalBlue inside networks ژەهراویی M.E.Doc، پاشان EternalBlue لە ناو |
| What it really wasلە ڕاستیدا چی بوو | Ransomware (about $300 in Bitcoin per computer) (نزیکەی 300 دۆلار بە Bitcoin بۆ هەر ) | A wiper disguised as ransomware بە ڕووکەشی |
| Could paying help?ئایا پارەدان یارمەتی دەدا؟ | Not advised, and no guaranteeئامۆژگاری ناکرێت و هیچ گەرەنتییەکی نییە | No — the data could not be decryptedنەخێر — مەحاڵ بوو |
Your college's computers show a ransom note asking for 5 bitcoin and threatening to publish student records. The offline backups are safe. Put these actions in a sensible order: restore from the offline backups; disconnect the infected computers from the network; find and close the way in; report to the IT security team and the authorities; tell the students whose data may have been stolen.
کۆلێژەکەت نامەیەکی بارمتە پیشان دەدەن کە داوای 5 بیتکۆین دەکات و هەڕەشە دەکات تۆمارەکانی قوتابیان بڵاو دەکاتەوە. سەلامەتن. ئەم کارانە بە ڕیزبەندییەکی ژیرانە دابنێ: گەڕاندنەوە لە ؛ جیاکردنەوەی لە ؛ دۆزینەوە و داخستنی ڕێگای چوونە ژوورەوە؛ ڕاپۆرتدان بە تیمی IT و دەسەڵاتەکان؛ ئاگادارکردنەوەی ئەو قوتابیانەی لەوانەیە دزرابێت.
Show answerوەڵامەکە پیشان بدە
- Disconnect the infected computers, so the encryption stops spreading.
- Report to the IT security team and the authorities (they may also know of a free decryption key).
- Find and close the way in (a stolen password, a missing patch…), or the attack will repeat.
- Restore from the offline backups onto clean, rebuilt systems.
- Tell the affected students, as the law and ethics require — the stolen copy may still be published.
- جیا بکەرەوە، بۆ ئەوەی شفرەکردنەکە بڵاو نەبێتەوە.
- ڕاپۆرت بدە بە تیمی IT و دەسەڵاتەکان (لەوانەیە ئەوان کلیلێکی بێبەرانبەری بناسن).
- ڕێگای چوونە ژوورەوە بدۆزەرەوە و دایبخە ( دزراو، دانەمەزراو…)، دەنا دووبارە دەبێتەوە.
- لە بیگەڕێنەوە بۆ سەر سیستەمی پاک و نوێکراوە.
- ئاگاداری قوتابییە زیانلێکەوتووەکان بکەرەوە، وەک یاسا و ئەخلاق داوای دەکەن — لەوانەیە کۆپییە دزراوەکە هێشتا بڵاو بکرێتەوە.
Paying is not on the list: the backups make it unnecessary, and paying would not delete the stolen copy. The full response cycle is in A ransomware incident, phase by phase.
پارەدان لە لیستەکەدا نییە: پێویستی ناهێڵن و پارەدانیش کۆپییە دزراوەکە ناسڕێتەوە. هەموو خولی لە هێرشێکی نەرمەواڵەی بارمتەگر، قۆناغ بە قۆناغـدایە.
Summary and reviewپوختە و پێداچوونەوە
- Ransomware encrypts files and demands payment, usually in cryptocurrency. Most attacks now also steal data first: double extortion.
- An attack has stages — get in, spread, steal, encrypt, demand — and the early ones can be spotted.
- WannaCry (May 2017) was a worm using EternalBlue against unpatched Windows; the patch had existed for two months. It hit more than 150 countries and the NHS.
- NotPetya (June 2017) came through a poisoned software update and was a wiper: paying could not help.
- Recent cases (British Library, Blue Yonder, Rhysida) show the same pattern: missing MFA or an exposed service, data stolen, months of recovery.
- Defence: offline tested backups, phishing-resistant MFA, fast patching, no exposed remote desktop, segmentation, least privilege, training and a practised response plan. Paying is not advised.
- فایلەکان شفرە دەکات و داوای پارە دەکات، زۆرجار بە . لە زۆربەی ئێستادا سەرەتا دەدزرێت و پاشان شفرەکردن دێت: .
- چەند قۆناغێکی هەیە — چوونە ژوورەوە، بڵاوبوونەوە، دزین، شفرەکردن، داواکردن — و قۆناغە سەرەتاییەکان دەکرێت بناسرێنەوە.
- WannaCry (ئایاری 2017) بوو کە EternalBlueـی دژی Windowsـی بەکار دەهێنا؛ دوو مانگ بوو هەبوو. زیاتر لە 150 وڵات و NHSـی گرتەوە.
- NotPetya (حوزەیرانی 2017) لە ڕێگەی ژەهراویی هات و بوو: پارەدان یارمەتیی نەدەدا.
- ڕووداوە نوێیەکان (کتێبخانەی بەریتانی، Blue Yonder، Rhysida) هەمان شێوە پیشان دەدەن: MFA نەبوون یان خزمەتگوزارییەکی ئاشکرا، دزینی ، چەند مانگ چاکبوونەوە.
- بەرگری: ئۆفلاین و تاقیکراو، MFAـی بەرگەگر لە بەرامبەر ، خێرا، هیچ Remote Desktopـێکی ئاشکرا، ، ، ڕاهێنان و پلانێکی ڕاهێنراوی وەڵامدانەوە. ئامۆژگاری ناکرێت پارە بدرێت.
What is double extortion?بارمتەگرتنی دووقات چییە؟
The attackers both encrypt the files and steal a copy, then demand payment for the key and for not publishing the data.
هەم فایلەکان شفرە دەکەن و هەم کۆپییەک دەدزن، پاشان هەم بۆ کلیلەکە و هەم بۆ بڵاونەکردنەوەی داوای پارە دەکەن.
Why could WannaCry spread without anyone clicking?بۆچی WannaCry دەیتوانی بەبێ کرتەی کەس بڵاو ببێتەوە؟
It was a worm: it used the SMBv1 flaw to copy itself to every unpatched Windows computer it could reach.
بوو: SMBv1ـی بەکار دەهێنا بۆ ئەوەی خۆی کۆپی بکات بۆ هەر Windowsـی کە پێی بگات.
What made NotPetya different from real ransomware?چی NotPetyaـی لە نەرمەواڵەی بارمتەگری ڕاستەقینە جیا دەکردەوە؟
It was a wiper: its encryption could not be reversed, so the ransom note was only a disguise.
بوو: هەڵنەدەگەڕایەوە، بۆیە نامەی بارمتەکە تەنها ڕووپۆشێک بوو.
Why must one backup be offline or immutable?بۆچی دەبێت باکئەپێک ئۆفلاین یان نەگۆڕ بێت؟
Ransomware deletes or encrypts every backup it can reach; only a copy out of its reach survives.
هەر بیگاتێ دەیسڕێتەوە یان شفرەی دەکات؛ تەنها کۆپییەک کە لە دەستڕاگەیشتنی بەدوور بێت دەمێنێتەوە.
Videoڤیدیۆ
Watch a videoسەیری ڤیدیۆیەک بکە
A video that viewers liked a lot and praised in their comments, chosen for this lesson.ڤیدیۆیەک کە بینەران زۆریان پێ خۆش بووە و لە کۆمێنتەکانیاندا ستایشیان کردووە، بۆ ئەم وانەیە هەڵبژێردراوە.
Learn what ransomware does to your files and data, and how backups, updates and training protect you from it.
فێر دەبیت چی بە و دەکات و چۆن ، و ڕاهێنان لێی دەتپارێزن.
Whole video (4:11): ransomware, data loss vs data breach (double extortion), prevention.
هەموو ڤیدیۆکە (4:11): ، جیاوازیی لەدەستدانی و ()، هەروەها ڕێگرتن لێی.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
Related lecturesوانە پەیوەندیدارەکان
- Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
- Backup and Recoveryباکئەپ و گەڕاندنەوەی دراوە
- Security and Online Safetyئاسایش و سەلامەتی لە ئینتەرنێتدا
- Malware Today: Infostealers, Banking Trojans, RATs, Cryptojacking and Moreنەرمەواڵەی زیانبەخشی ئەمڕۆ: نەرمەواڵە زانیاریدزەکان، ئەسپەکانی ترۆیای بانکی، RAT، کریپتۆجاکینگ و زیاتر
- Incident Response: Six Phasesوەڵامدانەوەی ڕووداو: شەش قۆناغ
- Real Incidents: From MoneyGram to GPS Spoofingڕووداوە ڕاستەقینەکان: لە MoneyGramـەوە تا هەڵخەڵەتاندنی GPS
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- CISA: #StopRansomware Guide (prevention best practices and response checklist)
- CISA Alert TA17-132A: Indicators Associated With WannaCry Ransomware (12 May 2017, revised 2018)
- Al Jazeera: Ransomware attack hit 200,000 victims in 150 countries (Europol, 14 May 2017)
- UK National Audit Office: Investigation — WannaCry cyber attack and the NHS (2017)
- NATO CCDCOE Cyber Law Toolkit: NotPetya (2017)
- SecurityWeek: Details and lessons learned from the ransomware attack on the British Library
- Euronews: British Library puts catalogue back online after 2023 cyber attack (16 January 2024)
- Computing: Ransomware attack on Blue Yonder disrupts Starbucks, Sainsbury's, Morrisons (November 2024)
- BleepingComputer: Blue Yonder SaaS giant breached by Termite ransomware gang (December 2024)
- CISA Advisory AA23-319A: #StopRansomware — Rhysida Ransomware
- BleepingComputer: Rhysida ransomware leaks documents stolen from Chilean Army (2023)
- Infosecurity Magazine: Columbus ransomware attack exposes data of 500,000 residents
- Malwarebytes: City of Columbus tries to silence security researcher (Rhysida auction and leak, 2024)
- UK NCSC: Ransomware — what it is and how to stay protected (position on paying)
- FBI Internet Crime Complaint Center: 2024 IC3 Annual Report
- FBI Internet Crime Complaint Center: 2025 IC3 Annual Report (ransomware and critical infrastructure, pp. 15–17)
- Coveware: Adverse cyber extortions are more common than commonly advised (Q2 2026 quarterly report)
- The Register: Rhysida claims British Library ransomware attack, auctions data (20 November 2023)
- WOSU: Hackers take credit for Columbus ransomware attack, request $1.9 million in bitcoin (1 August 2024)
- Security Boulevard: No ransom demand by Rhysida before Columbus data leak — city IT chief (September 2024)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.