Chapterبەش 7 · Lectureوانە 7.1
Network Defences: Firewalls, Segmentation, Monitoring and SIEMبەرگرییەکانی ڕایەڵە: ئاگرەدیوار، بەشبەشکردنی ڕایەڵە، چاودێریی ئاسایش و SIEM
How organisations defend the network itself: firewall rules and kinds of firewall, IDS and IPS, network segmentation into zones, VPNs, continuous monitoring and SIEM correlation — and the two network attacks they must stop, denial of service (DoS/DDoS) and man-in-the-middle.
ڕێکخراوەکان چۆن بەرگری لە خودی دەکەن: یاساکانی و جۆرەکانی، IDS و IPS، بۆ چەند ناوچەیەک، ، بەردەوام و بەستنەوەی ڕووداوەکان لە — هەروەها ئەو دوو هێرشەی کە دەبێت ڕابگیرێن: (DoS/DDoS) و .
What you will learnچی فێر دەبیت
- Read a firewall rule table and explain deny by default.
- Compare packet-filter, stateful, next-generation, web-application and host firewalls, and IDS with IPS.
- Design simple network zones and explain how segmentation limits a breach.
- Explain what continuous monitoring and a SIEM add, and where SOAR fits.
- Recognise DoS/DDoS and man-in-the-middle attacks and name their defences.
- خشتەی یاساکانی بخوێنیتەوە و ڕوون بکەیتەوە.
- ، ، ، و سەر ئامێر بەراورد بکەیت، هەروەها IDS لەگەڵ IPS.
- ناوچەی سادەی دیزاین بکەیت و ڕوونی بکەیتەوە چۆن دزەکردن سنووردار دەکات.
- ڕوونی بکەیتەوە بەردەوام و چی زیاد دەکەن و لە کوێدا جێی دەبێتەوە.
- هێرشەکانی /DDoS و بناسیتەوە و بەرگرییەکانیان ناو ببەیت.
Defending the network itselfبەرگریکردن لە خودی ڕایەڵە
Almost every attack in this course travels over a network: a phishing e-mail, a worm, a stolen password typed into a login page from far away. So defenders protect the network itself, in several layers. Some layers block traffic, some watch it and raise an alarm, and some divide the network into rooms so that one break-in does not open every door.
نزیکەی هەموو هێرشێکی ئەم کۆرسە بە ناو دەڕوات: ئیمەیڵێکی ، ، دزراو کە لە دوورەوە لە پەڕەیەکی دەنووسرێت. بۆیە بەرگریکاران خودی لە چەند چینێکدا دەپارێزن. هەندێک چین هاتوچۆ ڕادەگرن، هەندێکیان چاودێری دەکەن و ئاگادار دەکەنەوە. هەندێکی تریش دابەش دەکەن بۆ چەند ژوورێک، بۆ ئەوەی یەک دزەکردن هەموو دەرگاکان نەکاتەوە.
The course notes name two network defences: continuous monitoring and network segmentation, with SIEM tools to collect what is seen. This lesson teaches them and adds the tools they work with — firewalls, intrusion detection and prevention, VPNs — and two network attacks they must stop: denial of service and man-in-the-middle.
تێبینییەکانی کۆرسەکە دوو بەرگریی ناو دەبەن: بەردەوام و ، لەگەڵ ئامرازەکانی بۆ کۆکردنەوەی ئەوەی دەبینرێت. ئەم وانەیە ئەوانە فێر دەکات و ئەو ئامرازانەی لەگەڵیاندا کار دەکەن زیاد دەکات — ، دۆزینەوە و ڕێگریکردن لە دزەکردن، — هەروەها دوو هێرشی کە دەبێت ڕابگیرێن: و .
Defending the network itselfبەرگریکردن لە خودی ڕایەڵە
Layers, like a university campusچینەکان، وەک زانکۆیەک
A large university has one main gate where guards check who comes in and where they are going. Inside, the library, the labs and the finance office have their own locked doors, and cameras record the corridors. If a thief gets past the gate, he still cannot walk into the finance office, and the cameras show where he went. A network is defended the same way: a firewall at the gate, segmentation for the inner doors, and monitoring for the cameras.
زانکۆیەکی گەورە یەک دەروازەی سەرەکیی هەیە کە پاسەوانەکان تێیدا دەپشکنن کێ دێتە ژوورەوە و بۆ کوێ دەچێت. لە ناوەوە کتێبخانە، تاقیگەکان و ژووری دارایی هەریەکەیان دەرگای داخراوی خۆیان هەیە و کامێرا ڕاڕەوەکان تۆمار دەکات. ئەگەر دزێک لە دەروازەکە تێپەڕی، هێشتا ناتوانێت بچێتە ژووری داراییەوە و کامێراکان پیشانی دەدەن بۆ کوێ چووە. بە هەمان شێوە دەپارێزرێت: لە دەروازەدا، بۆ دەرگاکانی ناوەوە و لە جیاتی کامێراکان.
Where the analogy stops workingسنووری ئەم نموونەیە
A guard can judge a stranger's face; a firewall only sees addresses, ports and (in newer firewalls) applications. A thief with a real student card walks in — like an attacker with a stolen password.
پاسەوان دەتوانێت لە ڕووخساری کەسێکی نامۆ وردبێتەوە؛ تەنها ناونیشان، و (لە نوێیەکاندا) دەبینێت. دزێک کە کارتی ڕاستەقینەی قوتابیی پێیە دێتە ژوورەوە — وەک کە دزراوی پێیە.
No single layer is enough. This is defence in depth: each layer catches some of what the others miss.
هیچ چینێک بە تەنها بەس نییە. ئەمە بەرگریی چەندچینـە: هەر چینێک هەندێک لەوە دەگرێت کە چینەکانی تر لەدەستی دەدەن.
What a firewall doesئاگرەدیوار چی دەکات
A program or device that checks network traffic and decides what may go in and out of a private . It works like a guarded door.
بەرنامە یان ئامێرێکە کە هاتوچۆی دراوە دەپشکنێت و بڕیار دەدات چی بۆی هەیە بچێتە ژوورەوە و بچێتە دەرەوەی تایبەت. وەک دەرگایەکی پاسەوانکراو کار دەکات.
A firewall sits between two networks — usually between the Internet and an organisation's network — or on a single computer. It looks at each piece of traffic (each packet) and compares it with a list of rules. Each rule says, for example: from where, to which address, to which port, and then allow or block. The list of rules is the firewall's policy.
لە نێوان دوو دادەنرێت — زۆرجار لە نێوان و ڕێکخراوێکدا — یان لەسەر یەک . سەیری هەر پارچەیەکی هاتوچۆ (هەر ) دەکات و لەگەڵ لیستێکی یاسا بەراوردی دەکات. هەر یاسایەک بۆ نموونە دەڵێت: لە کوێوە، بۆ کام ناونیشان، بۆ کام و پاشان ڕێگەبدە یان ڕابگرە. لیستی یاساکان سیاسەتی .
- Rules are checked from top to bottom, and in most firewalls the first rule that matches decides. So the order of the rules matters.
- The last rule should be deny by default: anything not expressly allowed is blocked. NIST's firewall guide recommends this for traffic in both directions.
- Outbound rules matter too: a PC that should never send e-mail directly, or talk to unknown servers abroad, should be stopped from doing it. This blocks much malware from "calling home".
- Every decision can be logged. The firewall's logs are one of the most useful sources for monitoring, as you will see below.
- یاساکان لە سەرەوە بۆ خوارەوە دەپشکنرێن و لە زۆربەی یەکەم یاسا کە دەگونجێت بڕیار دەدات. بۆیە ڕیزبەندیی یاساکان گرنگە.
- دوا یاسا دەبێت بێت: هەر شتێک بە ئاشکرا ڕێگەی پێ نەدرابێت ڕادەگیرێت. ڕێبەری NIST ئەمە بۆ هاتوچۆ لە هەردوو ئاراستەدا پێشنیار دەکات.
- یاساکانی دەرچوونیش گرنگن: کە هەرگیز نابێت ڕاستەوخۆ ئیمەیڵ بنێرێت یان قسە لەگەڵ نەناسراو لە دەرەوەی وڵات بکات، دەبێت ڕێگەی لێ بگیرێت. ئەمە ڕێ لە زۆر دەگرێت کە «پەیوەندی بە ماڵەوە بکات».
- هەموو بڕیارێک دەکرێت لە تۆمار بکرێت. یەکێکن لە بەسوودترین سەرچاوەکان بۆ ، وەک لە خوارەوە دەیبینیت.
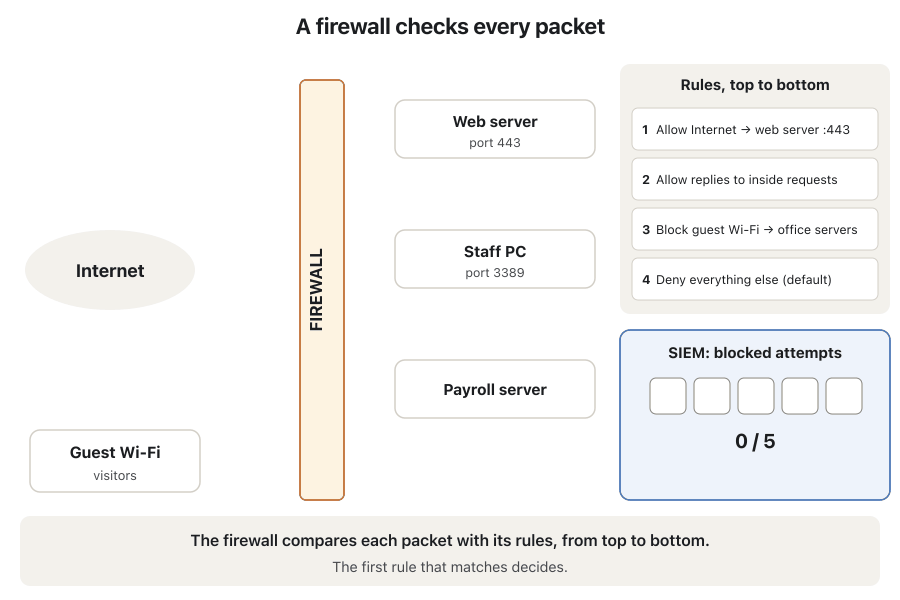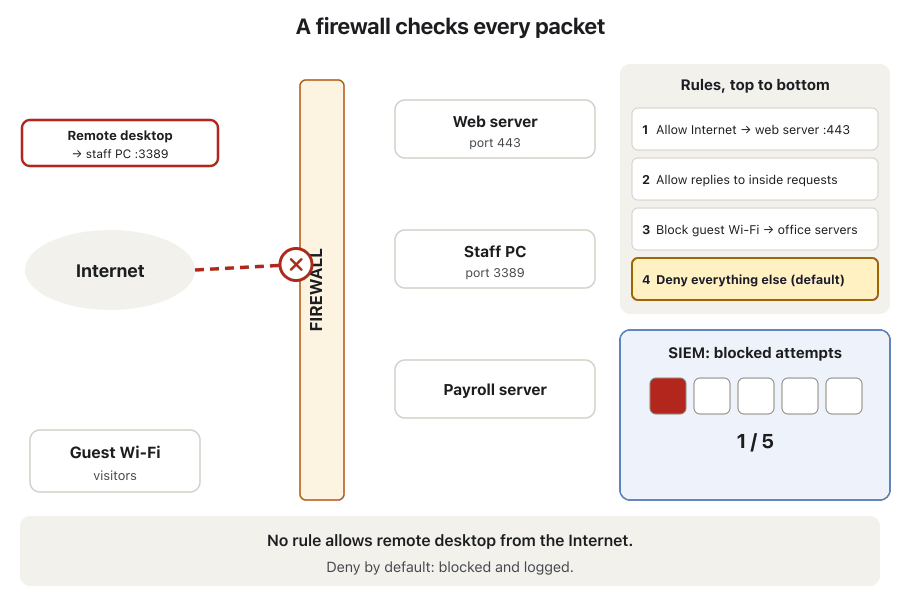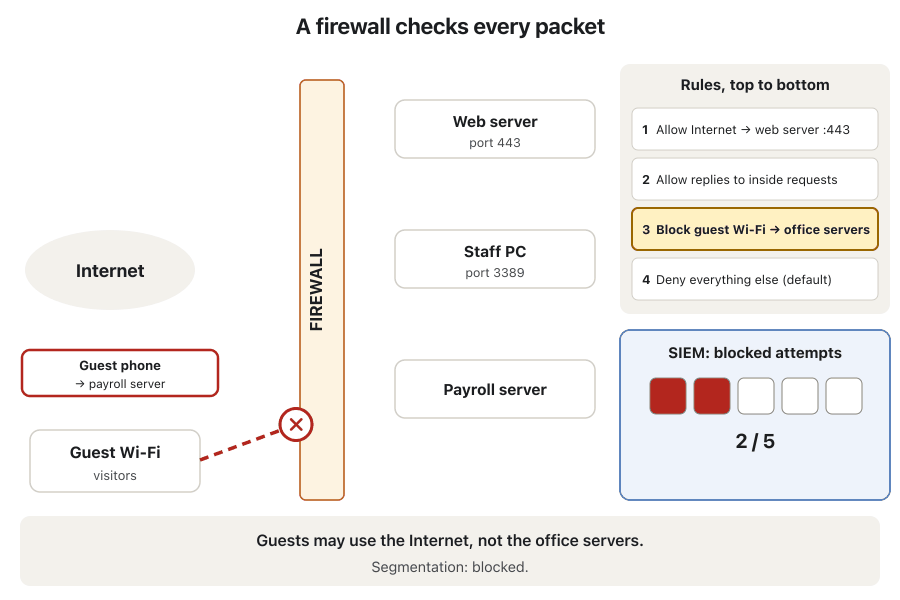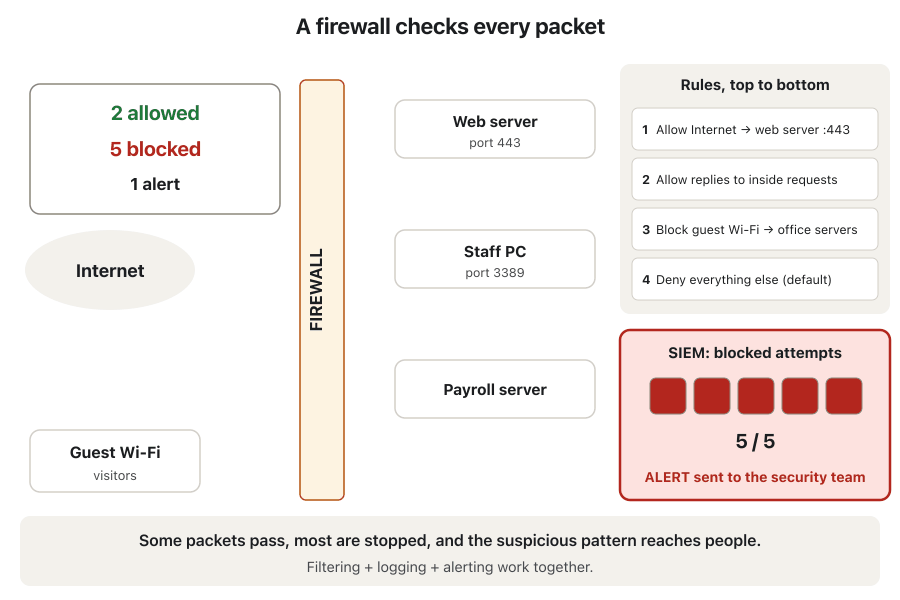
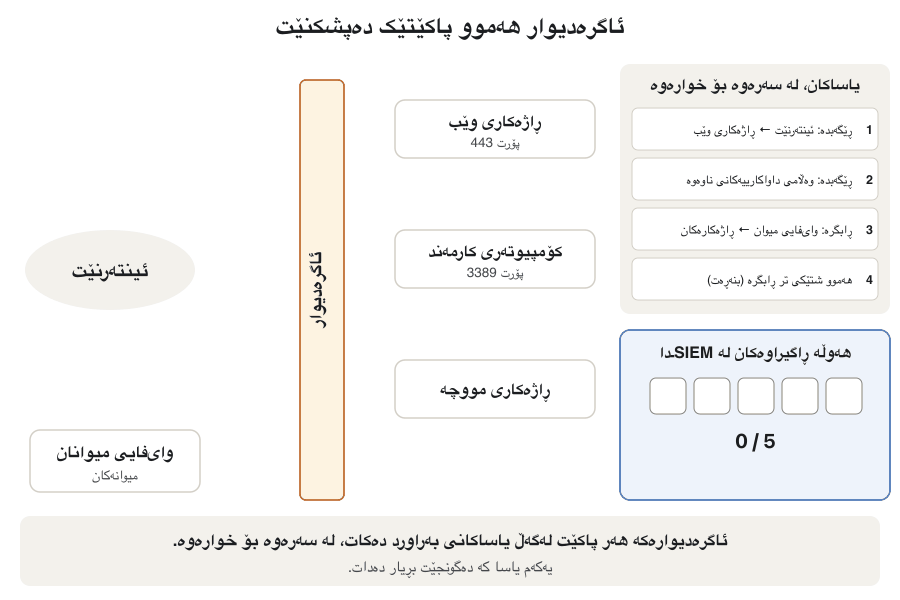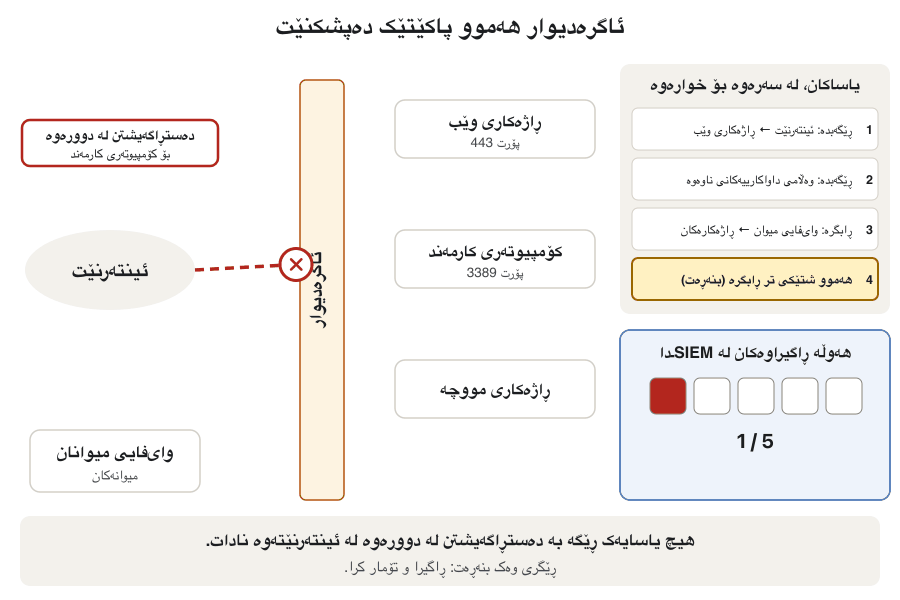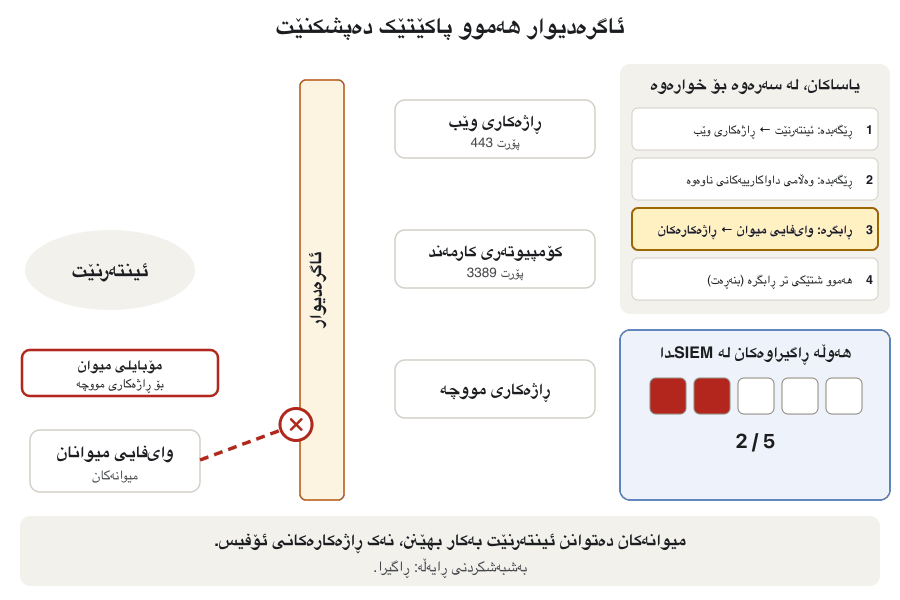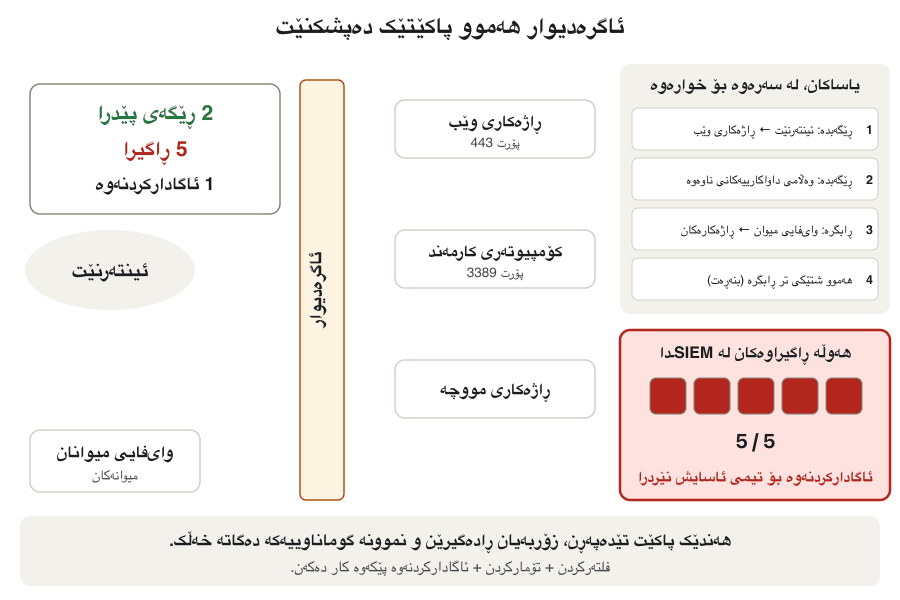
What a firewall does, how its rules allow or block traffic, how a stateful firewall remembers connections, and what newer all-in-one firewalls add.
چی دەکات، ڕێساکانی چۆن ڕێگە بە هاتوچۆ دەدەن یان دەیوەستێنن، بە چۆن پەیوەندییەکان لەبیر دەگرێت، هەروەها چی زیاد دەکەن.
Rules at 2:00, stateful firewalls at 4:11, all-in-one (UTM) firewalls at 6:30.
ڕێساکان لە 2:00، بە لە 4:11، (UTM) لە 6:30.
What a firewall doesئاگرەدیوار چی دەکات
Reading a rule tableخوێندنەوەی خشتەی یاساکان
Real firewalls show their policy as a table. Here is a small office's inbound policy, written in plain words. Read it from the top:
ڕاستەقینە سیاسەتەکەیان وەک خشتە پیشان دەدەن. ئەمە سیاسەتی هاتنە ژوورەوەی ئۆفیسێکی بچووکە، بە وشەی سادە نووسراوە. لە سەرەوە دەستی پێ بکە:
| # | Fromلە | Toبۆ | Port / service / خزمەتگوزاری | Actionبڕیار |
|---|---|---|---|---|
| 1 | Anywhereهەر شوێنێک | Web server | 443 (HTTPS) | Allowڕێگەبدە |
| 2 | Staff network کارمەندان | Database server | database port onlyتەنها | Allowڕێگەبدە |
| 3 | Guest Wi-Fi میوانان | Any office serverهەر ئۆفیس | anyهەموو | Blockڕابگرە |
| 4 | Anywhereهەر شوێنێک | Anywhereهەر شوێنێک | anyهەموو | Block (default)ڕابگرە (بنەڕەت) |
Kinds of firewallجۆرەکانی ئاگرەدیوار
Firewalls have grown smarter over the years. Each newer kind can see more about the traffic, so it can make better decisions — but it also needs more computing power and more care to set up.
بە درێژایی ساڵان زیرەکتر بوون. هەر جۆرێکی نوێتر دەتوانێت زیاتر دەربارەی هاتوچۆکە ببینێت، بۆیە بڕیاری باشتر دەدات — بەڵام هێزی ژمێرکاریی زیاتر و وریایی زیاتری لە ڕێکخستندا دەوێت.
| Kindجۆر | What it looks atسەیری چی دەکات | Good atباشە بۆ | Blind toنایبینێت |
|---|---|---|---|
| Each packet alone: source and destination address, port, protocolهەر بە تەنها: ناونیشانی سەرچاوە و مەبەست، ، | Fast, simple rulesخێرا، یاسای سادە | Whether a packet belongs to a real conversation; what is insideئایا سەر بە گفتوگۆیەکی ڕاستەقینەیە؛ چی لە ناویدایە | |
| Also remembers each open connection in a state tableهەروەها هەر پەیوەندییەکی کراوە لە خشتەیەکی تایبەتدا (state table) لە بیر دەکات | Lets replies back in automatically; drops fake "replies" nobody asked forوەڵامەکان بە شێوەی خۆکار ڕێگە پێ دەدات؛ «وەڵامی» ساختە کە کەس داوای نەکردووە فڕێ دەدات | Attacks hidden inside allowed trafficئەو هێرشانەی لە ناو هاتوچۆی ڕێگەپێدراودا شاردراونەتەوە | |
| (NGFW) | The application and often the user behind the traffic و زۆرجار ئەو بەکارهێنەرەی لە پشت هاتوچۆکەیە | "Allow the accounting app, block file-sharing apps, even on port 443"; often has a built-in IPS and malware checks«ڕێگە بە ئەپی ژمێریاری بدە، ئەپەکانی هاوبەشکردنی فایل ڕابگرە، تەنانەت لەسەر 443»؛ زۆرجار و پشکنینی تێدایە | Badly written rules; stolen passwordsیاسای خراپ نووسراو؛ دزراو |
| (WAF) | The content of web requests to one websiteناوەڕۆکی داواکارییەکانی وێب بۆ یەک | Blocking SQL injection and XSS patternsڕاگرتنی شێوازەکانی و | Flaws it has no pattern for; not a replacement for secure codeهەر کە شێوازی بۆ نییە؛ جێگرەوەی کۆدی سەلامەت نییە |
| Host-based (personal) firewall سەر ئامێر (کەسی) | Traffic of one computerهاتوچۆی یەک | Protecting a laptop on hotel or café Wi-Fiپاراستنی لەسەر هوتێل یان کافێ | Everything else on the networkهەموو شتێکی تری سەر |
Organisations usually combine them: an NGFW at the Internet edge, internal firewalls between zones, a WAF in front of the public website (see Injection attacks) and a host firewall switched on in every laptop.
ڕێکخراوەکان زۆرجار تێکەڵیان دەکەن: لە لێواری ، ناوخۆیی لە نێوان ناوچەکاندا، لە پێش گشتییەکەوە (بڕوانە هێرشەکانی تێخزاندن) و سەر ئامێر کە لە هەموو هەڵکراوە.
IDS and IPS: the alarm and the guardIDS و IPS: زەنگی ئاگادارکەرەوە و پاسەوان
A firewall decides by rules about where traffic goes. Some attacks travel along allowed paths: a request to the public website that carries an attack, or a staff laptop that suddenly talks like infected malware. To catch these, organisations add intrusion detection and prevention.
بەپێی یاسا بڕیار دەدات کە هاتوچۆ بۆ کوێ دەڕوات. هەندێک هێرش بە ڕێگا ڕێگەپێدراوەکاندا دەڕۆن: داواکارییەک بۆ گشتییەکە کە هێرشێکی تێدایە، یان کارمەندێک کە لەناکاو وەک قسە دەکات. بۆ گرتنی ئەمانە، ڕێکخراوەکان دۆزینەوە و ڕێگریکردن لە دزەکردن زیاد دەکەن.
| Aspectلایەن | IDS — | IPS — |
|---|---|---|
| Where it sitsلە کوێ دادەنرێت | Beside the traffic: it receives a copyلە تەنیشت هاتوچۆکەوە: کۆپییەک وەردەگرێت | Inside the path: all traffic goes through itلە ناو ڕێگاکەدا: هەموو هاتوچۆیەک بە ناویدا تێدەپەڕێت |
| What it doesچی دەکات | Raises an alert for people to checkئاگادارکردنەوە دەدات بۆ ئەوەی خەڵک بیپشکنن | Blocks the bad traffic at once (and alerts)یەکسەر هاتوچۆ خراپەکە ڕادەگرێت (و ئاگادار دەکاتەوە) |
| If it is wrongئەگەر هەڵە بکات | A false alarm wastes an analyst's timeئاگادارکردنەوەی هەڵە کاتی شیکەرەوەیەک بەفیڕۆ دەدات | A false alarm blocks real customersئاگادارکردنەوەی هەڵە کڕیارە ڕاستەقینەکان ڕادەگرێت |
| Everyday pictureوێنەی ڕۆژانە | A shop's camera with an alarm bellکامێرای دوکانێک لەگەڵ زەنگی ئاگادارکەرەوە | A guard at the door who stops the thiefپاسەوانێک لە دەرگاکەدا کە دزەکە ڕادەگرێت |
Both can watch the network (network-based) or run on one computer (host-based). Modern endpoint tools (EDR) do host-based detection on laptops and servers; see Malware.
هەردووکیان دەتوانن چاودێریی بکەن (لەسەر ) یان لەسەر یەک کار بکەن (لەسەر ئامێر). ئامرازە نوێیەکانی پاراستنی ئامێر () دۆزینەوەی سەر ئامێر لەسەر و دەکەن؛ بڕوانە نەرمەواڵەی زیانبەخش.
IDS and IPS: the alarm and the guardIDS و IPS: زەنگی ئاگادارکەرەوە و پاسەوان
How an IDS recognises attacks — and how attackers hideIDS چۆن هێرش دەناسێتەوە — و هێرشبەرەکان چۆن خۆیان دەشارنەوە
- Signature-based detection compares traffic with patterns of known attacks, like antivirus. It is accurate for known attacks, but blind to new ones.
- Anomaly-based detection first learns what is normal (a baseline) and then flags what is unusual: a printer that suddenly sends gigabytes to another country. It can catch new attacks, but it makes more false positives, the same trade-off you met in False alarms and misses.
- هاتوچۆ لەگەڵ شێوازی هێرشە ناسراوەکان بەراورد دەکات، وەک . بۆ هێرشە ناسراوەکان وردە، بەڵام هێرشە نوێیەکان نابینێت.
- سەرەتا فێر دەبێت چی ئاساییە (بنەمای ئاسایی) و پاشان ئەوەی نائاساییە نیشانە دەکات: کە لەناکاو گیگابایت دەنێرێت بۆ وڵاتێکی تر. دەتوانێت هێرشی نوێ بگرێت، بەڵام زیاتر دروست دەکات؛ هەمان هاوسەنگییە کە لە ئاگادارکردنەوەی هەڵە و لەدەستچووندا بینیت.
Attackers know about IDSs and try to slip past them. Two old tricks: flooding the IDS with so much traffic, or so many fake alerts, that it cannot inspect everything and the real attack hides in the noise; and sending the attack along a path no sensor watches, for example by splitting the traffic over different routes (asymmetric routing), so no single sensor sees the whole conversation. Defenders place sensors where all traffic must pass, give the IDS enough capacity, raise an alarm when it starts dropping packets, and add host-based detection (EDR) as a second view.
IDS دەناسن و هەوڵ دەدەن لێی دەرباز ببن. دوو فێڵی کۆن هەن: نوقمکردن — ئەوەندە هاتوچۆ، یان ئەوەندە ئاگادارکردنەوەی ساختە، دەنێرن کە IDS نەتوانێت هەمووی بپشکنێت و هێرشە ڕاستەقینەکە لە ناو ژاوەژاوەکەدا ون ببێت؛ هەروەها ناردنی هێرشەکە بە ڕێگایەکدا کە هیچ چاودێریی ناکات، بۆ نموونە بە دابەشکردنی هاتوچۆکە بەسەر چەند ڕێگایەکی جیاوازدا (asymmetric routing)، بۆ ئەوەی هیچ هەموو گفتوگۆکە نەبینێت. بەرگریکاران لەو شوێنانە دادەنێن کە هەموو هاتوچۆیەک دەبێت پێیاندا تێپەڕێت، توانای پێویست دەدەنە IDS، کاتێک دەست دەکات بە فڕێدانی ئاگادار دەکەنەوە و دۆزینەوەی سەر ئامێر () وەک دیمەنێکی دووەم زیاد دەکەن.
Network segmentation: rooms with locked doorsبەشبەشکردنی ڕایەڵە: ژووری دەرگا داخراو
Dividing a into separate parts, such as guest Wi-Fi, staff computers and servers, with rules between them, so that an attacker who gets into one part cannot easily reach the others.
دابەشکردنی بۆ چەند بەشێکی جیا، وەک میوانان، کۆمپیوتەری کارمەندان و ، بە ڕێسا لە نێوانیاندا، بۆ ئەوەی کە دەچێتە ناو بەشێکەوە بە ئاسانی نەگاتە بەشەکانی تر.
A flat network is one big room: every device can talk to every other device. If one laptop is infected, the attacker can reach the payroll server, the backups and the cameras. Segmentation splits the network into zones and puts rules between them. The course gives it two purposes:
تەخت یەک ژووری گەورەیە: هەموو ئامێرێک دەتوانێت قسە لەگەڵ هەموو ئامێرێکی تر بکات. ئەگەر یەک تووش ببێت، دەتوانێت بگاتە مووچە، و کامێراکان. دابەش دەکات بۆ چەند ناوچەیەک و یاسا لە نێوانیاندا دادەنێت. کۆرسەکە دوو ئامانجی بۆ دیاری دەکات:
- Isolation — a smaller attack surface. Sensitive systems and data are kept apart from less secure areas, so a breach in one zone stays in that zone. The attacker cannot simply move sideways (security people call this lateral movement).
- Control and visibility. Traffic between zones must pass a firewall or filter, so the team decides exactly who may talk to whom — and every crossing can be logged and watched.
- جیاکردنەوە — بچووکتر. سیستەم و هەستیارەکان لە ناوچە کەمتر پارێزراوەکان جیا دەکرێنەوە، بۆیە دزەکردن لە ناوچەیەکدا لە هەمان ناوچەدا دەمێنێتەوە. ناتوانێت بە ئاسانی بە لادا بجووڵێت (پسپۆڕانی ئاسایش پێی دەڵێن ).
- کۆنترۆڵ و بینین. هاتوچۆی نێوان ناوچەکان دەبێت بە یان فلتەرێکدا تێپەڕێت، بۆیە تیمەکە بە وردی بڕیار دەدات کێ دەتوانێت قسە لەگەڵ کێ بکات — هەروەها هەموو تێپەڕینێک دەکرێت تۆمار بکرێت و چاودێری بکرێت.
Network segmentation: rooms with locked doorsبەشبەشکردنی ڕایەڵە: ژووری دەرگا داخراو
Zones: DMZ, VLANs and microsegmentationناوچەکان: DMZ، VLAN و بەشبەشکردنی ورد
- A DMZ (demilitarised zone) is a small zone for servers that the Internet must reach, such as the public website. It is exposed, so it gets the least trust.
- Zones are built with separate subnets or VLANs (virtual networks that share the same switches) and with firewall rules between them.
- A device that cannot be patched — an old machine that runs a factory line, a medical scanner — is put in its own small zone, where almost nothing can reach it.
- Taken to the limit, every system gets its own tiny zone (microsegmentation), the network form of zero trust.
- ناوچەیەکی بچووکە بۆ هەر کە دەبێت پێی بگات، وەک گشتییەکە. ئاشکرایە، بۆیە کەمترین متمانەی پێ دەدرێت.
- ناوچەکان بە ژێرڕایەڵەی جیاواز یان بە ( مەجازی کە لەگەڵ ئەوانی تر هەمان بەکار دەهێنێت) و بە یاسای لە نێوانیاندا دروست دەکرێن.
- ئامێرێک کە ناتوانرێت بکرێت — ئامێرێکی کۆن کە هێڵێکی کارگە بەڕێوە دەبات، سکانەرێکی پزیشکی — دەخرێتە ناوچەیەکی بچووکی تایبەت بە خۆی، کە نزیکەی هیچ شتێک ناگاتێ.
- ئەگەر تا کۆتایی ببرێت، هەر سیستەمێک ناوچەیەکی زۆر بچووکی خۆی هەیە (بەشبەشکردنی ورد)، کە شێوەی متمانەی سفرـە.
VPNs: a protected tunnel across the InternetVPN: تونێلێکی پارێزراو بە ناو ئینتەرنێتدا
A VPN (virtual private network) builds an encrypted tunnel between two points across the Internet: a member of staff working from home and the office, or two branches of a bank. What a VPN is and how the tunnel is made is explained in Private networks: VPN; here we look at its security role.
تونێلێکی شفرەکراو لە نێوان دوو خاڵدا بە ناو دروست دەکات: کارمەندێک کە لە ماڵەوە کار دەکات و ئۆفیسەکە، یان دوو لقی بانکێک. چییە و تونێلەکە چۆن دروست دەکرێت لە ڕایەڵە تایبەتەکان: VPN ڕوون کراوەتەوە؛ لێرە سەیری ڕۆڵی ئاسایشیی دەکەین.
- It protects data in transit. Anyone listening on the café Wi-Fi or along the way sees only scrambled data. This is a defence against eavesdropping and man-in-the-middle attacks (below).
- It is a door into the network. The VPN gateway faces the whole Internet and lets people inside. That makes it a favourite target: VPN products appear again and again in CISA's list of exploited vulnerabilities.
- So the VPN gateway must be patched first when a fix appears (see Which one first?), every VPN account needs MFA, and old unused accounts must be removed. A single legacy VPN account without MFA was the way into Colonial Pipeline in 2021 (see the Colonial Pipeline case).
- لە کاتی گواستنەوەدا دەپارێزێت. هەر کەسێک لەسەر کافێکە یان لە ڕێگادا گوێ بگرێت تەنها تێکەڵکراو دەبینێت. ئەمە بەرگرییە دژی و (لە خوارەوە).
- دەرگایەکە بۆ ناو . دەروازەی ڕووی لە هەموو و ڕێگە بە خەڵک دەدات بچنە ژوورەوە. ئەمە دەیکات بە ئامانجێکی دڵخواز: بەرهەمەکانی جار لە دوای جار لە CISAـدا دەردەکەون.
- بۆیە دەبێت دەروازەی یەکەم جار بکرێت کاتێک چارەسەرێک دەردەچێت (بڕوانە کامیان یەکەم؟)، هەموو هەژمارێکی پێویستی بە MFA هەیە و هەژمارە کۆنە بەکارنەهێنراوەکان دەبێت لاببرێن. تەنها یەک هەژماری کۆنی بەبێ MFA ڕێگای چوونە ناو Colonial Pipeline بوو لە ساڵی 2021دا (بڕوانە ڕووداوی Colonial Pipeline).
In Kurdish (Sorani): what a VPN (virtual private network) is and what people use one for.
بە کوردیی سۆرانی: ( تایبەتی گریمانەیی) چییە و خەڵک بۆ چی بەکاری دەهێنن.
Kurdish (Sorani) introduction to what a VPN is, by the ZagrosByte (CyberKurd) channel; it does not cover this screen's points on patching the VPN gateway and MFA.
ناساندنێکی کوردی (سۆرانی) بۆ ئەوەی چییە، لە کەناڵی ZagrosByte (CyberKurd)ـەوە؛ خاڵەکانی ئەم شاشەیە دەربارەی و ناگرێتەوە.
Continuous monitoring: watching all the timeچاودێریی ئاسایشی بەردەوام: چاودێری لە هەموو کاتێکدا
Firewalls and segmentation prevent. But no prevention is perfect, so defenders also watch. The course names two benefits of continuous monitoring:
و ڕێگری دەکەن. بەڵام هیچ ڕێگرییەک تەواو نییە، بۆیە بەرگریکاران چاودێریش دەکەن. کۆرسەکە دوو سوودی بەردەوام ناو دەبات:
- Real-time visibility: the team sees what is happening on its systems now, so it can detect and respond to threats promptly.
- Proactive threat detection: an attack is caught early — the first strange login, the first scan of the network — before it causes significant damage.
- بینینی ڕاستەوخۆ: تیمەکە دەبینێت ئێستا چی لەسەر سیستەمەکانی ڕوو دەدات، بۆیە دەتوانێت بە خێرایی بدۆزێتەوە و وەڵامیان بداتەوە.
- دۆزینەوەی پێشوەختەی : هێرش زوو دەگیرێت — یەکەم نامۆ، یەکەم پشکنینی — پێش ئەوەی زیانی گەورە بگەیەنێت.
What is watched? Mostly logs: records that systems write about what happened, when and by whom. Typical sources are the firewall, the IDS/IPS, VPN and Wi-Fi logins, servers, e-mail filters, antivirus/EDR on laptops and cloud accounts. Teams first learn what is normal for their network, because an attack usually shows up as something unusual.
سەیری چی دەکرێت؟ زۆربەی جار : تۆمارانێک کە سیستەمەکان دەینووسن دەربارەی ئەوەی چی ڕووی دا، کەی و لەلایەن کێوە. سەرچاوە باوەکان ، IDS/IPS، و ، ، فلتەرەکانی ئیمەیڵ، / لەسەر و هەژمارەکانی هەورن. تیمەکان سەرەتا فێر دەبن چی بۆ ئاساییە، چونکە هێرش زۆرجار وەک شتێکی نائاسایی دەردەکەوێت.
SIEM: collecting and connecting the cluesSIEM: کۆکردنەوە و بەستنەوەی سەرەداوەکان
A system that collects from many computers, network devices and programs in one place, links related events together and raises alerts about possible attacks.
سیستەمێکە کە لە زۆر کۆمپیوتەر، ئامێری ڕایەڵە و بەرنامەوە لە یەک شوێندا کۆ دەکاتەوە، ڕووداوە پەیوەندیدارەکان پێکەوە دەبەستێتەوە و دەربارەی هێرشە ئەگەرییەکان ئاگادارکردنەوە دەدات.
A large organisation produces millions of log lines a day — far too many for people to read. A SIEM (security information and event management) tool collects security data from many sources into one place and analyses it to detect suspicious activity. In order, it:
ڕێکخراوێکی گەورە ڕۆژانە ملیۆنان دێڕی بەرهەم دەهێنێت — زۆر زیاترە لەوەی خەڵک بیخوێننەوە. ئامرازێکی ئاسایش لە زۆر سەرچاوەوە لە یەک شوێندا کۆ دەکاتەوە و شیکاریی بۆ دەکات بۆ دۆزینەوەی چالاکیی گوماناوی. بە ڕیز:
- Collectsکۆ دەکاتەوە
Receives logs from firewalls, servers, VPN, laptops, cloud services.
لە ، ، ، و خزمەتگوزارییەکانی هەورەوە وەردەگرێت.
- Normalisesیەکدەست دەکات
Turns many different formats into one, with the same time zone.
زۆر شێوازی جیاواز دەکات بە یەک شێواز، بە هەمان .
- Correlatesدەیانبەستێتەوە بە یەکەوە
Connects events that are harmless alone but suspicious together, using rules.
بە یاسا ڕووداوەکان بە یەکەوە دەبەستێتەوە کە بە تەنها بێزیانن بەڵام پێکەوە گوماناوین.
- Alertsئاگادار دەکاتەوە
Raises an alert, with the evidence attached, for an analyst to check.
دەدات، لەگەڵ بەڵگەکان، بۆ ئەوەی شیکەرەوەیەک بیپشکنێت.
- Storesهەڵیدەگرێت
Keeps the logs for months, so investigators can look back later.
بۆ چەند مانگێک هەڵدەگرێت، بۆ ئەوەی لێکۆڵەرەوەکان دواتر سەیری ڕابردوو بکەن.
SIEM: collecting and connecting the cluesSIEM: کۆکردنەوە و بەستنەوەی سەرەداوەکان
Correlation rules and automatic actionsیاساکانی بەستنەوە و هەنگاوی خۆکار
An example correlation rule: "Six failed logins to one account, then a successful login from a country where the company has no staff, then a large download — within one hour." Each event alone is common; together they look like a stolen password. The SIEM can also trigger actions based on predefined rules, which the course mentions as automated incident response.
نموونەیەکی یاسای بەستنەوە: «شەش سەرنەکەوتوو بۆ یەک هەژمار، پاشان سەرکەوتوو لە وڵاتێکەوە کە کۆمپانیاکە هیچ کارمەندێکی تێدا نییە، پاشان دابەزاندنێکی گەورە — هەمووی لە یەک کاتژمێردا.» هەر ڕووداوێک بە تەنها باوە؛ پێکەوە وەک دزراو دەردەکەون. دەتوانێت بەپێی یاسای پێشوەختە هەنگاوی خۆکاریش بنێت، کە کۆرسەکە وەک خۆکار ناوی دەبات.
DoS and DDoS: drowning a serviceڕێگەگرتن لە خزمەتگوزاری و DDoS: نوقمکردنی خزمەتگوزارییەک
Some attackers do not want to steal anything. They want a service to stop working: the bank's app on salary day, a ministry's website, an online exam. A denial-of-service (DoS) attack floods a server or network with so much traffic or so many requests that real users cannot get through. It attacks availability, the A of the CIA triad.
هەندێک نایانەوێت هیچ شتێک بدزن. دەیانەوێت خزمەتگوزارییەک لە کار بکەوێت: ئەپی بانکەکە لە ڕۆژی مووچەدا، وەزارەتێک، تاقیکردنەوەیەکی ئۆنلاین. هێرشی (DoS) یان بە ئەوەندە هاتوچۆ یان داواکاری نوقم دەکات کە بەکارهێنەرە ڕاستەقینەکان ناتوانن تێپەڕن. هێرش دەکاتە سەر ، واتە Aـی سێگۆشەی CIA.
- In a DoS the flood comes from one source (or a few). Blocking that address usually stops it.
- In a DDoS (distributed denial of service) it comes from thousands of devices at once — usually a botnet of infected PCs, cameras and routers (see Botnets). Blocking one address does not help, and the attack traffic is mixed with real users.
- لە لافاوەکە لە یەک سەرچاوەوە دێت (یان چەند دانەیەک). ڕاگرتنی ئەو ناونیشانە زۆرجار دەیوەستێنێت.
- لە (DDoS) لە هەزاران ئامێرەوە پێکەوە دێت — زۆرجار لە ، کامێرا و تووشبوو (بڕوانە بۆتنێتەکان). ڕاگرتنی یەک ناونیشان سوودی نییە و هاتوچۆی هێرشەکە لەگەڵ بەکارهێنەرە ڕاستەقینەکاندا تێکەڵ دەبێت.
How DoS and DDoS floods knock a server offline, how to spot one, and three defences: rate limiting, a web application firewall and load balancing.
چۆن DoS و DDoS بە لافاوی لە کار دەخەن، چۆن دەیانناسیتەوە و سێ بەرگری: ، و دابەشکردنی فشار.
DoS vs DDoS at 3:58; how to identify one at 5:13; defences from 6:00 (rate limiting 6:24, WAF 7:03, load balancer 7:47).
جیاوازیی DoS و DDoS لە 3:58؛ چۆن دەیناسیتەوە لە 5:13؛ ڕێگاکانی بەرگری لە 6:00 ( 6:24، 7:03، دابەشکەری فشار 7:47).
DoS and DDoS: drowning a serviceڕێگەگرتن لە خزمەتگوزاری و DDoS: نوقمکردنی خزمەتگوزارییەک
Three kinds of DDoSسێ جۆری DDoS
| Type (CISA)جۆر (CISA) | What is used upچی تەواو دەکرێت | Everyday pictureوێنەی ڕۆژانە |
|---|---|---|
| Volumetricقەبارەیی | The bandwidth of the connection پەیوەندییەکە | So many cars that the road to the shop is jammedئەوەندە ئۆتۆمبێل کە ڕێگای دوکانەکە قەرەباڵغ دەبێت |
| Protocolپەیوەست بە | The connection tables of servers, firewalls and load balancersخشتەکانی پەیوەندیی ، و ئامێرەکانی دابەشکردنی بار | Hundreds of people ring the shop's phone and never speak, so all lines are busyسەدان کەس تەلەفۆن بۆ دوکانەکە دەکەن و هەرگیز قسە ناکەن، بۆیە هەموو هێڵەکان گیراون |
| Applicationئاستی | The server's work on expensive pages (search, login)کاری لەسەر پەڕە گرانەکان (گەڕان، ) | Hundreds of fake customers each ask the shopkeeper for a complicated price listسەدان کڕیاری ساختە هەریەکەیان داوای لیستێکی نرخی ئاڵۆز لە دوکاندارەکە دەکەن |
DoS and DDoS: drowning a serviceڕێگەگرتن لە خزمەتگوزاری و DDoS: نوقمکردنی خزمەتگوزارییەک
Defending against DDoSبەرگری دژی DDoS
Defences are prepared before an attack: a DDoS protection service or a CDN that absorbs and filters floods far from your server; rate limiting (no single address may send more than a set number of requests); spare bandwidth, load balancing and backup servers; firewall rules and an IPS that drop known attack traffic; a CAPTCHA on pages that bots abuse; and a response plan with the provider's phone number. During an attack, confirm it is really an attack (not a busy day), call the provider and the ISP, keep the logs as evidence, tell users what is happening, and keep watching your other systems — CISA warns that a flood is sometimes a distraction for a second attack.
بەرگرییەکان پێش هێرش ئامادە دەکرێن: خزمەتگوزارییەکی پاراستنی DDoS یان کە لافاوەکان دوور لە هەڵدەمژێت و فلتەریان دەکات؛ (هیچ ناونیشانێک نابێت لە ژمارەیەکی دیاریکراو زیاتر داواکاری بنێرێت)؛ زیادە، دابەشکردنی بار و یەدەگ؛ یاساکانی و کە هاتوچۆی هێرشە ناسراوەکان فڕێ دەدەن؛ لەسەر ئەو پەڕانەی بۆتەکان خراپ بەکاریان دەهێنن؛ هەروەها پلانی وەڵامدانەوە لەگەڵ ژمارەی تەلەفۆنی دابینکەرەکە. لە کاتی هێرشدا، دڵنیا ببەرەوە کە بەڕاستی هێرشە (نەک ڕۆژێکی قەرەباڵغ)، پەیوەندی بە دابینکەرەکە و دابینکەری بکە، وەک بەڵگە بپارێزە و بە بەکارهێنەران بڵێ چی ڕوو دەدات. هەروەها چاودێریی سیستەمەکانی ترت بەردەوام بێت، چونکە CISA ئاگادار دەکاتەوە کە لافاوەکە هەندێک جار تەنها سەرقاڵکردنە بۆ هێرشێکی دووەم.
Man-in-the-middle: someone on the lineهێرشی کەسی ناوەڕاست: کەسێک لەسەر هێڵەکە
In a man-in-the-middle attack the attacker secretly sits between two sides — you and your bank, a laptop and the office — and passes their messages on, reading and perhaps changing them. You met the idea in Passive and active attacks. On a network it can happen when:
لە بە نهێنی لە نێوان دوو لایەندا دادەنیشێت — تۆ و بانکەکەت، و ئۆفیسەکە — و نامەکانیان دەگوازێتەوە، دەیانخوێنێتەوە و لەوانەیە بیانگۆڕێت. بیرۆکەکەت لە هێرشە ناچالاک و چالاکەکاندا بینی. لەسەر دەتوانێت ڕوو بدات کاتێک:
- you join a fake Wi-Fi hotspot with a friendly name ("Free Airport WiFi") that the attacker controls;
- a home or office router is hacked or still has its default password;
- on a local network, a device lies about its address so that others send it their traffic (for example ARP spoofing; how ARP works is in DNS and ARP).
- دەچیتە سەر ساختەی بە ناوێکی دۆستانە («Free Airport WiFi») کە کۆنترۆڵی دەکات؛
- ماڵ یان ئۆفیس هاک کراوە یان هێشتا بەکار دەهێنێت؛
- لەسەر ناوخۆیی، ئامێرێک درۆ دەربارەی ناونیشانەکەی دەکات بۆ ئەوەی ئەوانی تر هاتوچۆکەیان بۆ ئەو بنێرن (بۆ نموونە ؛ چۆن کار دەکات لە DNS و ARPدا ڕوون کراوەتەوە).
Man-in-the-middle: someone on the lineهێرشی کەسی ناوەڕاست: کەسێک لەسەر هێڵەکە
Stopping a man in the middleڕاگرتنی هێرشی کەسی ناوەڕاست
The strongest defence is encryption with checked identity: HTTPS (TLS) encrypts the conversation and the browser checks the website's certificate, so a middleman can neither read the data nor pretend to be the bank (see Certificates and TLS). Add a VPN on networks you do not trust, MFA or passkeys so that a stolen password is not enough, strong Wi-Fi security (WPA3) at home and work, and switches and IDS rules that detect address lies on the local network.
بەهێزترین بەرگری لەگەڵ ناسنامەی پشکنراوـە: () گفتوگۆکە شفرە دەکات و بڕوانامەی دەپشکنێت، بۆیە کەسی ناوەڕاست نە دەتوانێت بخوێنێتەوە و نە خۆی وەک بانکەکە نیشان بدات (بڕوانە بڕوانامەکان و TLS). لەسەر هەر کە متمانەت پێی نییە زیاد بکە، MFA یان بۆ ئەوەی دزراو بەس نەبێت، ئاسایشی بەهێزی (WPA3) لە ماڵ و کار، هەروەها و یاساکانی IDS کە درۆی ناونیشان لەسەر ناوخۆیی دەدۆزنەوە.
How the layers work togetherچینەکان چۆن پێکەوە کار دەکەن
Each defence in this lesson stops some attacks and misses others. That is why they are used together:
هەر بەرگرییەکی ئەم وانەیە هەندێک هێرش ڕادەگرێت و هەندێکی تر لەدەست دەدات. بۆیە پێکەوە بەکار دەهێنرێن:
| Defenceبەرگری | Stops or showsڕادەگرێت یان پیشان دەدات | Does not stopڕاناگرێت |
|---|---|---|
| Firewall | Traffic to ports and places that are not allowedهاتوچۆ بۆ ئەو و شوێنانەی ڕێگەپێنەدراون | Attacks along allowed paths; logins with stolen passwordsهێرش بە ڕێگا ڕێگەپێدراوەکاندا؛ بە دزراو |
| IDS / IPS | Known attack patterns and unusual trafficشێوازی هێرشە ناسراوەکان و هاتوچۆی نائاسایی | Brand-new attacks with no pattern; encrypted traffic it cannot readهێرشی تەواو نوێ کە شێوازی نییە؛ هاتوچۆی شفرەکراو کە ناتوانێت بیخوێنێتەوە |
| Segmentation | An attacker or worm moving sidewaysجووڵەی یان بە لادا | The first break-in inside a zoneیەکەم دزەکردن لە ناو ناوچەیەکدا |
| VPN | Eavesdropping on untrusted networks لەسەر نامتمانەپێکراو | Phishing, malware, a flaw in the VPN itself، ، لە خودی |
| Monitoring and SIEM و | Unusual behaviour, even with valid passwordsڕەفتاری نائاسایی، تەنانەت بە دروستیش | Nothing by itself: someone must read and act on the alertsبە تەنها هیچ: کەسێک دەبێت ئاگادارکردنەوەکان بخوێنێتەوە و کاریان لەسەر بکات |
| DDoS protectionپاراستنی DDoS | Floods against availabilityلافاو دژی | Data theft and break-insدزینی و دزەکردن |
Monitoring is only useful when people act on what it finds. Who reads the alerts, and what they do next, is the subject of the next two lessons: Incident response and Security operations centres.
تەنها کاتێک بەسوودە کە خەڵک کار لەسەر ئەوە بکەن کە دەیدۆزێتەوە. کێ ئاگادارکردنەوەکان دەخوێنێتەوە و دوای ئەوە چی دەکات، بابەتی دوو وانەی داهاتووە: وەڵامدانەوەی ڕووداو و ناوەندی کارەکانی ئاسایش.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| "We have a firewall, so we are secure."« هەیە، کەواتە سەلامەتین.» | Many attacks use allowed paths or stolen passwordsزۆر هێرش ڕێگا ڕێگەپێدراوەکان یان دزراو بەکار دەهێنن | Add segmentation, MFA, monitoring and patching، MFA، و زیاد بکە |
| An "allow any" rule added "just for testing" and forgottenیاسای «ڕێگە بە هەموو شتێک بدە» کە «تەنها بۆ تاقیکردنەوە» زیاد کراوە و لەبیر کراوە | It quietly opens the whole networkبە بێدەنگی هەموو دەکاتەوە | Review firewall rules regularly; deny by defaultبە ڕێکوپێکی پێداچوونەوە بە یاساکانی بکە؛ |
| Only filtering incoming trafficتەنها فلتەرکردنی هاتوچۆی هاتنە ژوورەوە | Malware inside "calls home" and data leaves freely لە ناوەوە «پەیوەندی بە ماڵەوە دەکات» و بە ئازادی دەڕواتە دەرەوە | Filter outbound traffic tooهاتوچۆی دەرچوونیش فلتەر بکە |
| A flat network where guests, staff and servers share one zone تەخت کە میوانان، کارمەندان و یەک ناوچە بەکار دەهێنن | One infected phone can reach everythingیەک مۆبایلی تووشبوو دەتوانێت بگاتە هەموو شتێک | Separate zones with rules between themناوچەی جیاواز لەگەڵ یاسا لە نێوانیاندا |
| Collecting logs that nobody readsکۆکردنەوەی کە کەس نایخوێنێتەوە | Attacks are recorded but not stoppedهێرشەکان تۆمار دەکرێن بەڵام ناوەستێنرێن | Tune alerts and give someone the job of answering themئاگادارکردنەوەکان ڕێک بخە و ئەرکی وەڵامدانەوەیان بدە بە کەسێک |
| Clicking through certificate warnings on public Wi-Fiپشتگوێخستنی ئاگادارکردنەوەی بڕوانامە لەسەر گشتی | That is how a man-in-the-middle succeeds بەم شێوەیە سەردەکەوێت | Stop, leave the network, use mobile data or a VPNبوەستە، لە دەربچۆ، مۆبایل یان بەکار بهێنە |
| Treating the VPN gateway as "just a tunnel"مامەڵەکردن لەگەڵ دەروازەی وەک «تەنها تونێلێک» | It is an exposed device and a favourite targetئامێرێکی ئاشکرایە و ئامانجێکی دڵخوازە | Patch it first, require MFA, remove old accountsیەکەم جار بکە، MFA داوا بکە، هەژمارە کۆنەکان لاببە |
Exercisesڕاهێنانەکان
Use the rule table from Reading a rule table. For each packet say which rule decides and whether it passes: (a) a customer's browser to the web server on port 443; (b) a staff laptop to the database server on the database port; (c) a guest phone to the web server's admin page inside the office; (d) someone on the Internet to the database server on the database port.
خشتەی یاساکانی خوێندنەوەی خشتەی یاساکان بەکار بهێنە. بۆ هەر بڵێ کام یاسا بڕیار دەدات و ئایا تێدەپەڕێت: (أ) کڕیارێک بۆ لەسەر 443؛ (ب) کارمەندێک بۆ لەسەر ؛ (ج) مۆبایلی میوانێک بۆ پەڕەی بەڕێوەبردنی لە ناو ئۆفیسدا؛ (د) کەسێک لەسەر بۆ لەسەر .
Show answerوەڵامەکە پیشان بدە
- (a) Rule 1 — allowed.
- (b) Rule 2 — allowed.
- (c) Rule 3 — blocked: guests may not reach any office server.
- (d) Rule 4 — blocked by default: rule 2 allows only the staff network, so the Internet cannot reach the database.
- (أ) یاسای 1 — ڕێگەی پێ دەدرێت.
- (ب) یاسای 2 — ڕێگەی پێ دەدرێت.
- (ج) یاسای 3 — ڕادەگیرێت: میوانان ناتوانن بگەنە هیچ ئۆفیس.
- (د) یاسای 4 — بە بنەڕەت ڕادەگیرێت: یاسای 2 تەنها ڕێگە بە کارمەندان دەدات، بۆیە ناگاتە .
A clinic has: a public appointment website, reception PCs, doctors' laptops, a patient-records database, an old X-ray machine that cannot be updated, and free Wi-Fi for patients. Group them into zones and write two rules in plain words.
نۆرینگەیەک ئەمانەی هەیە: گشتیی کاتی سەردان، پێشوازی، پزیشکان، تۆماری نەخۆشان، ئامێرێکی کۆنی تیشکی X کە ناتوانرێت نوێ بکرێتەوە و بێبەرانبەر بۆ نەخۆشان. بیانخە ناو چەند ناوچەیەکەوە و دوو یاسا بە وشەی سادە بنووسە.
Show answerوەڵامەکە پیشان بدە
One good design: DMZ — the appointment website; staff zone — reception PCs and doctors' laptops; server zone — the patient-records database; device zone — the X-ray machine alone; guest zone — patient Wi-Fi, Internet only. Example rules: "The website may reach the records database only on the database port, for appointment data"; "Nothing may reach the X-ray machine except the one doctors' viewing station"; "Guest Wi-Fi may reach only the Internet".
دیزاینێکی باش: — کاتی سەردان؛ ناوچەی کارمەندان — پێشوازی و پزیشکان؛ ناوچەی — تۆماری نەخۆشان؛ ناوچەی ئامێر — تەنها ئامێری تیشکی X؛ ناوچەی میوانان — نەخۆشان، تەنها . نموونەی یاساکان: « تەنها لەسەر دەگاتە تۆمارەکان، بۆ کاتی سەردان»؛ «هیچ شتێک ناگاتە ئامێری تیشکی X جگە لە یەک وێستگەی بینینی پزیشکان»؛ « میوانان تەنها دەگاتە ».
For each case, choose IDS (alert only) or IPS (block), and give a reason: (a) a new, untested rule on a hospital network; (b) a well-known attack pattern against the public website that is always malicious; (c) a factory network where a wrong block could stop a production line.
بۆ هەر حاڵەتێک IDS (تەنها ئاگادارکردنەوە) یان IPS (ڕاگرتن) هەڵبژێرە و هۆکارێک بڵێ: (أ) یاسایەکی نوێی تاقینەکراوە لەسەر نەخۆشخانەیەک؛ (ب) شێوازێکی ناسراوی هێرش دژی گشتییەکە کە هەمیشە خراپەکارانەیە؛ (ج) کارگە کە ڕاگرتنێکی هەڵە دەتوانێت هێڵێکی بەرهەمهێنان ڕابگرێت.
Show answerوەڵامەکە پیشان بدە
- (a) IDS first: false positives would only cost an analyst's time while the rule is tested.
- (b) IPS: the pattern is certain and blocking it at once protects the site.
- (c) Mostly IDS, with blocking only for very certain patterns: availability of the line is critical, so a wrong block is expensive.
- (أ) سەرەتا IDS: تەنها کاتی شیکەرەوەیەک دەبەن لە کاتێکدا یاساکە تاقی دەکرێتەوە.
- (ب) IPS: شێوازەکە دڵنیایە و ڕاگرتنی یەکسەری دەپارێزێت.
- (ج) زۆرتر IDS. ڕاگرتن تەنها بۆ شێوازە زۆر دڵنیاکان: هێڵەکە گرنگە، بۆیە ڕاگرتنێکی هەڵە گرانە.
Your college publishes exam results online twice a year, and last year the site went down from a DDoS. Write a short plan: three things to prepare before results day and three things to do during an attack.
کۆلێژەکەت ساڵی دوو جار ئەنجامی تاقیکردنەوەکان ئۆنلاین بڵاو دەکاتەوە و ساڵی ڕابردوو بە DDoS کەوت. پلانێکی کورت بنووسە: سێ شت بۆ ئامادەکردن پێش ڕۆژی ئەنجامەکان و سێ شت بۆ کردن لە کاتی هێرشدا.
Show answerوەڵامەکە پیشان بدە
Before: put the results site behind a DDoS-protection service or CDN; add rate limiting and a CAPTCHA on the search page; agree a response plan with the ISP and provider, with phone numbers and who decides. Also consider a simple static results page that is cheap to serve. During: confirm it is an attack (traffic from many unusual sources, not just students); call the provider/ISP and switch on stronger filtering; keep the logs as evidence and post updates for students on another channel (for example the college's social media page).
پێش: ئەنجامەکان بخە پشت خزمەتگوزارییەکی پاراستنی DDoS یان ؛ و لەسەر پەڕەی گەڕان زیاد بکە؛ لەگەڵ دابینکەری و دابینکەری پاراستنەکە لەسەر پلانێکی وەڵامدانەوە ڕێک بکەوە، لەگەڵ ژمارەی تەلەفۆن و ئەوەی کێ بڕیار دەدات. هەروەها بیر لە پەڕەیەکی سادەی جێگیری ئەنجامەکان بکەرەوە کە پێشکەشکردنی هەرزانە. لە کاتی هێرشدا: دڵنیا ببەرەوە کە هێرشە (هاتوچۆ لە زۆر سەرچاوەی نائاساییەوە، نەک تەنها قوتابیان)؛ پەیوەندی بە دابینکەرەکەوە بکە و فلتەرکردنی بەهێزتر هەڵبکە؛ وەک بەڵگە بپارێزە و هەواڵی نوێ بۆ قوتابیان لە ڕێگایەکی ترەوە بڵاو بکەرەوە (بۆ نموونە پەڕەی کۆلێژەکە لەسەر ).
(a) Give the two benefits of continuous monitoring named in the course. (b) Give the two purposes of network segmentation. (c) What does a SIEM tool do, in two sentences?
(أ) ئەو دوو سوودەی بەردەوام بنووسە کە کۆرسەکە ناویان دەبات. (ب) دوو ئامانجی بنووسە. (ج) ئامرازی چی دەکات، بە دوو ڕستە؟
Show answerوەڵامەکە پیشان بدە
- (a) Real-time visibility into system activity, so threats are detected and answered promptly; proactive threat detection before significant damage.
- (b) Isolation of sensitive systems and data from less secure areas, limiting a breach (a smaller attack surface); better control and visibility of traffic.
- (c) It collects and analyses security data from many sources to detect suspicious activity. It raises alerts and can trigger automated response actions (often through SOAR) based on predefined rules.
- (أ) بینینی ڕاستەوخۆی چالاکیی سیستەمەکان، بۆ ئەوەی بە خێرایی بدۆزرێنەوە و وەڵام بدرێنەوە؛ دۆزینەوەی پێشوەختەی پێش زیانی گەورە.
- (ب) جیاکردنەوەی سیستەم و هەستیارەکان لە ناوچە کەمتر پارێزراوەکان بۆ سنووردارکردنی دزەکردن ( بچووکتر)؛ کۆنترۆڵ و بینینی باشتری هاتوچۆ.
- (ج) ئاسایش لە زۆر سەرچاوەوە کۆ دەکاتەوە و شیکاریی بۆ دەکات بۆ دۆزینەوەی چالاکیی گوماناوی. ئاگادار دەکاتەوە و دەتوانێت بەپێی یاسای پێشوەختە هەنگاوی وەڵامدانەوەی خۆکار بنێت (زۆرجار لە ڕێگەی ).
Summaryپوختە
- A firewall allows or blocks traffic by rules, top to bottom, with deny by default in both directions. Kinds: packet filter, stateful, next-generation, WAF, host firewall.
- An IDS watches and alerts; an IPS sits in the path and blocks. Signatures catch known attacks; anomaly detection catches new ones with more false positives.
- Segmentation splits the network into zones (DMZ, staff, servers, guests): it isolates breaches and gives control and visibility.
- A VPN encrypts traffic across untrusted networks, but its gateway is an exposed door: patch it first and require MFA.
- Continuous monitoring gives real-time visibility and early detection; a SIEM collects, correlates and alerts, and SOAR can act automatically.
- DoS/DDoS floods attack availability (volumetric, protocol, application); man-in-the-middle attacks are stopped by TLS with checked certificates, VPNs on untrusted Wi-Fi and never ignoring certificate warnings.
- بەپێی یاسا، لە سەرەوە بۆ خوارەوە، ڕێگە بە هاتوچۆ دەدات یان ڕایدەگرێت، لەگەڵ لە هەردوو ئاراستەدا. جۆرەکان: ، ، ، ، سەر ئامێر.
- IDS چاودێری دەکات و ئاگادار دەکاتەوە؛ IPS لە ناو ڕێگاکەدایە و ڕادەگرێت. واژووەکان هێرشە ناسراوەکان دەگرن؛ هێرشە نوێیەکان دەگرێت بەڵام زیاترە.
- دابەش دەکات بۆ چەند ناوچەیەک (، کارمەندان، ، میوانان): دزەکردن جیا دەکاتەوە و کۆنترۆڵ و بینین دەدات.
- هاتوچۆ بە ناو نامتمانەپێکراودا شفرە دەکات، بەڵام دەروازەکەی دەرگایەکی ئاشکرایە: یەکەم جار بکە و MFA داوا بکە.
- بەردەوام بینینی ڕاستەوخۆ و دۆزینەوەی زوو دەدات؛ کۆ دەکاتەوە، دەیانبەستێتەوە بە یەکەوە و ئاگادار دەکاتەوە و دەتوانێت بە شێوەی خۆکار کار بکات.
- لافاوەکانی /DDoS هێرش دەکەنە سەر (قەبارەیی، ، )؛ بە لەگەڵ بڕوانامەی پشکنراو، لەسەر نامتمانەپێکراو و هەرگیز پشتگوێنەخستنی ئاگادارکردنەوەی بڕوانامە ڕادەگیرێت.
Why should the last firewall rule be "deny everything"?بۆچی دەبێت دوا یاسای ئاگرەدیوار «هەموو شتێک ڕابگرە» بێت؟
So that anything nobody thought about is blocked automatically. Only traffic that was expressly allowed can pass.
بۆ ئەوەی هەر شتێک کە کەس بیری لێ نەکردبێتەوە بە شێوەی خۆکار ڕابگیرێت. تەنها ئەو هاتوچۆیەی بە ئاشکرا ڕێگەی پێ دراوە دەتوانێت تێپەڕێت.
What is the main difference between an IDS and an IPS?جیاوازیی سەرەکیی نێوان IDS و IPS چییە؟
An IDS only detects and alerts; an IPS sits inline and can block traffic, so its false positives can block real users.
IDS تەنها دەدۆزێتەوە و ئاگادار دەکاتەوە؛ IPS لە ناو ڕێگاکەدایە و دەتوانێت هاتوچۆ ڕابگرێت، بۆیە دەتوانن بەکارهێنەرە ڕاستەقینەکان ڕابگرن.
Why is blocking one IP address useless against a DDoS?بۆچی ڕاگرتنی یەک ناونیشانی IP دژی DDoS بێسوودە؟
Because the traffic comes from thousands of devices in a botnet at once; filtering and absorbing the flood (DDoS protection, CDN, rate limiting) is needed.
چونکە هاتوچۆکە لە هەزاران ئامێری پێکەوە دێت؛ فلتەرکردن و هەڵمژینی لافاوەکە (پاراستنی DDoS، ، ) پێویستە.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Incident Response: Six Phasesوەڵامدانەوەی ڕووداو: شەش قۆناغ
Related lecturesوانە پەیوەندیدارەکان
- The Internet and the Webئینتەرنێت و وێب
- Types of Networks: LAN, WAN and Moreجۆرەکانی ڕایەڵە: ڕایەڵەی ناوچەیی، ڕایەڵەی فراوان و زیاتر
- Finding and Rating Vulnerabilities: Scanning, OWASP and CVSSدۆزینەوە و هەڵسەنگاندنی خاڵە لاوازەکان: پشکنین، OWASP و CVSS
- Incident Response: Six Phasesوەڵامدانەوەی ڕووداو: شەش قۆناغ
- Security Operations Centres and Threat Huntingناوەندی کارەکانی ئاسایش و ڕاوکردنی هەڕەشە
- Malware: Viruses, Worms, Trojans, Ransomware and Spywareنەرمەواڵەی زیانبەخش: ڤایرۆسەکانی کۆمپیوتەر، کرمەکان، ئەسپەکانی ترۆیا، نەرمەواڵەی بارمتەگر و نەرمەواڵەی سیخوڕی
- Encryption, Hashing and Digital Signaturesشفرەکردن، هاشکردن و واژووە دیجیتاڵییەکان
- Injection Attacks: SQL Injection and Cross-Site Scriptingهێرشەکانی تێخزاندن: تێخزاندنی SQL و XSS
- Confidentiality, Integrity and Availabilityبەنهێنی مانەوە، دروستی و بەردەستبوون
- Network Hardware: NICs, Switches and Routersڕەقەواڵەی ڕایەڵە: کارتی ڕایەڵە، سویچ و ڕێدۆز
- IP Addresses and MAC Addressesناونیشانەکانی IP و ناونیشانەکانی MAC
- Case Studies: Equifax, Colonial Pipeline and Capital Oneلێکۆڵینەوەی ڕووداو: Equifax، Colonial Pipeline و Capital One
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- NIST SP 800-41 Rev. 1: Guidelines on Firewalls and Firewall Policy
- NIST SP 800-215: Guide to a Secure Enterprise Network Landscape (NGFW, microsegmentation, ZTNA)
- NIST SP 800-94: Guide to Intrusion Detection and Prevention Systems (IDPS)
- NIST SP 800-61 Rev. 3: Incident Response Recommendations (Detect function: monitoring, SIEM and SOAR)
- CISA, FBI and MS-ISAC: Understanding and Responding to Distributed Denial-of-Service Attacks (v2.0, March 2024)
- CISA: Understanding Denial-of-Service Attacks (a flood can distract from a second attack; what to do during an attack)
- CISA: Known Exploited Vulnerabilities Catalog
- OWASP Top 10:2025
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.