Chapterبەش 3 · Lectureوانە 3.3
Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
What to do after finding a vulnerability: private, full and coordinated disclosure; Project Zero's days; a vulnerability's journey from discovery to report, fix and public advisory; security.txt and disclosure policies; CVE IDs; CERTs as coordinators; bug bounty programmes, platforms, scope and safe harbour; and the lecture's hospital dilemma worked through.
دوای دۆزینەوەی چی بکەیت: ئاشکراکردنی تایبەت، تەواو و هەماهەنگکراو؛ ڕۆژی Project Zero؛ گەشتی لە دۆزینەوەوە بۆ ڕاپۆرت، چاککردن و ئاگاداریی گشتی؛ security.txt و سیاسەتەکانی ئاشکراکردن؛ ناسنامەکانی ؛ وەک هەماهەنگکار؛ بەرنامەکانی ، پلاتفۆرم، سنوور و ؛ و نموونەی نەخۆشخانەی وانەکە بە شیکردنەوە.
What you will learnچی فێر دەبیت
- Compare private, full and coordinated disclosure, and explain why coordinated disclosure is the normal choice.
- Work out disclosure dates with Project Zero's rule.
- Find and write a security.txt contact, and say when to ask a CERT to coordinate.
- Explain how bug bounty programmes work: scope, rewards by severity and safe harbour.
- Analyse an unauthorised discovery in a hospital system: ethical aspects, legal aspects and recommended actions.
- ئاشکراکردنی تایبەت، تەواو و هەماهەنگکراو بەراورد بکەیت و ڕوونی بکەیتەوە بۆچی ئاشکراکردنی هەماهەنگکراو هەڵبژاردنی ئاساییە.
- ڕێکەوتەکانی ئاشکراکردن بە یاسای Project Zero () بدۆزیتەوە.
- پەیوەندیی security.txt بدۆزیتەوە و بنووسیت و بڵێیت کەی داوا لە بکرێت هەماهەنگی بکات.
- ڕوونی بکەیتەوە بەرنامەکانی چۆن کار دەکەن: سنوور، خەڵات بەپێی ئاستی مەترسی و .
- دۆزینەوەیەکی بێ ڕێگەپێدان لە سیستەمی نەخۆشخانەیەکدا شی بکەیتەوە: لایەنی ئەخلاقی، لایەنی یاسایی و ڕێکارە پێشنیارکراوەکان.
You found a hole: what now?کونێکت دۆزییەوە: ئێستا چی؟
The lecture gives a short case study. A cybersecurity professional discovers a vulnerability in a widely used piece of software. Should they disclose it publicly, or notify the vendor (the company that makes the software)? What are the legal and ethical considerations? This lesson answers that question step by step.
وانەکە نموونەیەکی کورت دەهێنێتەوە. پسپۆڕێکی لە بەربڵاودا دەدۆزێتەوە. ئایا بە ئاشکرا بڵاوی بکاتەوە، یان فرۆشیار (ئەو کۆمپانیایەی دروست دەکات) ئاگادار بکاتەوە؟ بیرکردنەوە یاسایی و ئەخلاقییەکان چین؟ ئەم وانەیە هەنگاو بە هەنگاو وەڵامی ئەم پرسیارە دەداتەوە.
There are three ways to handle a vulnerability you have found:
سێ ڕێگە هەیە بۆ مامەڵەکردن لەگەڵ کە دۆزیوتەتەوە:
| Wayڕێگە | What happensچی ڕوودەدات | Problemکێشە |
|---|---|---|
| Private disclosureئاشکراکردنی تایبەت | You tell only the vendor. The vendor decides whether the public ever hears about it.تەنها فرۆشیار ئاگادار دەکەیتەوە. فرۆشیار بڕیار دەدات خەڵک هەرگیز دەبیستێت یان نا. | Some vendors stay silent and never fix.هەندێک فرۆشیار بێدەنگ دەبن و هەرگیز چاکی ناکەن. |
| Full disclosure | You publish all the details at once, before a fix exists.یەکسەر هەموو وردەکارییەکان بڵاو دەکەیتەوە، پێش ئەوەی چارەسەر هەبێت. | Attackers can use the hole before users can protect themselves. دەتوانن پێش ئەوەی خۆیان بپارێزن کونەکە بەکار بهێنن. |
| Responsible (coordinated) disclosure (هەماهەنگکراو) | You report privately, give the vendor time to fix, then the details are published.بە نهێنی ڕاپۆرت دەدەیت، کات دەدەیتە فرۆشیار بۆ چاککردن، پاشان وردەکارییەکان بڵاو دەکرێنەوە. | It needs patience and trust on both sides.پێویستی بە ئارامگرتن و متمانەی هەردوو لا هەیە. |
Responsible disclosureئاشکراکردنی بەرپرسیارانە
Reporting a privately to the organisation that can fix it and giving it time to release a before the details are made public. Today it is usually called coordinated vulnerability disclosure.
بریتییە لە ڕاپۆرتدانی بە نهێنی بۆ ئەو دامەزراوەیەی دەتوانێت چاکی بکات و پێدانی کات پێی بۆ ئەوەی بڵاو بکاتەوە پێش ئەوەی وردەکارییەکان ئاشکرا بکرێن. ئەمڕۆ زۆرجار پێی دەوترێت «ئاشکراکردنی هەماهەنگکراوی خاڵی لاواز».
Responsible disclosure is the practice of reporting a vulnerability to the affected parties so they can fix it before it is made public. Lecture 4 says the same in one line: report the vulnerability to the affected vendor, with time to patch it, before public release.
بریتییە لە ڕاپۆرتدانی بەو لایەنانەی کاریگەرییان لەسەرە، بۆ ئەوەی پێش ئاشکرابوونی چاکی بکەن. وانەی چوارەم هەمان شت بە یەک دێڕ دەڵێت: ڕاپۆرتی بدە بە فرۆشیاری پەیوەندیدار و کاتی پێ بدە، پێش بڵاوکردنەوەی گشتی.
Two ideas sit behind it. Responsibility: if weak points become public, who answers for the harm? The finder must not be the one who opened the door for attackers. Cooperation: researchers and the people in charge of companies, organisations and institutions must work together to protect users. This cooperation is what keeps the risk to users as small as possible.
دوو بیرۆکە لە پشتییەوەن. بەرپرسیارێتی: ئەگەر ئاشکرا بوون، کێ وەڵامی زیانەکە دەداتەوە؟ دۆزەرەوەکە نابێت ئەو کەسە بێت کە دەرگای بۆ کردەوە. هاوکاری: توێژەران و بەرپرسانی کۆمپانیا، ڕێکخراو و دامەزراوەکان دەبێت پێکەوە کار بکەن بۆ پاراستنی . ئەم هاوکارییە ئەوەیە کە سەر بە کەمترین ئاست دەهێڵێتەوە.
Today most experts call it coordinated vulnerability disclosure (CVD). CERT/CC, one of the oldest coordination centres, describes CVD as collecting information from the people who find vulnerabilities, coordinating how it is shared among everyone involved, and disclosing the vulnerabilities and their fixes to them and to the public. 'Coordinated' says the important part: finder, vendor and sometimes a coordinator agree on the timing together.
ئەمڕۆ زۆربەی شارەزایان پێی دەڵێن ئاشکراکردنی هەماهەنگکراوی (CVD). CERT/CC، کە یەکێکە لە کۆنترین سەنتەرەکانی هەماهەنگی، CVD بەم شێوەیە وەسف دەکات: کۆکردنەوەی زانیاری لەو کەسانەی دەدۆزنەوە، هەماهەنگیکردنی چۆنیەتیی بەشکردنی لە نێوان هەموو لایەنەکاندا و ئاشکراکردنی و چارەسەرەکانیان بۆ ئەوان و بۆ خەڵک. وشەی «هەماهەنگکراو» بەشە گرنگەکە دەڵێت: دۆزەرەوە، فرۆشیار و هەندێک جار هەماهەنگکارێک پێکەوە لەسەر کات ڕێک دەکەون.
Full disclosure: fast, but riskyئاشکراکردنی تەواو: خێرا، بەڵام مەترسیدار
Publishing all the details of a at once, before a fix exists. It warns users fast but also helps attackers, so most researchers prefer .
بریتییە لە بڵاوکردنەوەی یەکسەری هەموو وردەکارییەکانی ، پێش ئەوەی چارەسەرێک هەبێت. بەکارهێنەران بە خێرایی ئاگادار دەکاتەوە بەڵام یارمەتیی دەدات، بۆیە زۆربەی توێژەران بەباشتر دەزانن.
In full disclosure the vulnerability details are made public immediately. Lecture 4 names both sides: it increases the risk of exploitation, but it also raises awareness: users learn at once that they are in danger, and the vendor is pushed to act.
لە دا وردەکارییەکانی یەکسەر ئاشکرا دەکرێن. وانەی چوارەم هەردوو لایەنەکەی دەڵێت: مەترسیی بەکارهێنانی کونەکە زیاد دەکات، بەڵام هۆشیاریش بەرز دەکاتەوە: یەکسەر دەزانن لە مەترسیدان و فرۆشیار ناچار دەکرێت کار بکات.
| Questionپرسیار | Full disclosure | Coordinated disclosureئاشکراکردنی هەماهەنگکراو |
|---|---|---|
| When are details public?وردەکارییەکان کەی ئاشکرا دەبن؟ | At onceیەکسەر | After the fix, or after an agreed deadlineدوای چاککردن، یان دوای ماوەیەکی ڕێککەوتوو |
| Can attackers use it before a fix?ئایا دەتوانن پێش چاککردن بەکاری بهێنن؟ | Yesبەڵێ | Much less likelyزۆر کەمتر ئەگەری هەیە |
| Pressure on the vendorفشار لەسەر فرۆشیار | Very highزۆر بەرز | A deadline gives steady pressureماوەیەکی دیاریکراو فشارێکی بەردەوام دروست دەکات |
| When is it used today?ئەمڕۆ کەی بەکار دێت؟ | Rarely: when a vendor ignores reports, or when attackers are already using the holeبە دەگمەن: کاتێک فرۆشیار گوێ بە ڕاپۆرتەکان نادات، یان پێشتر کونەکە بەکار دەهێنن | The normal, recommended wayڕێگە ئاسایی و پێشنیارکراوەکە |
Deadlines: Project Zero's daysکۆتا وادەکان: ڕۆژی Project Zero
The notes' example: Google's Project Zero gives companies 90 days to patch before publicising the vulnerability. Project Zero is a Google team that hunts for vulnerabilities in software made by many companies (and in Google's own). When it finds a security problem, it tells the software's owner, a company or a single person, and gives 90 days, about three months, to fix it.
نموونەی تێبینییەکان: Project Zeroـی گووگڵ ٩٠ ڕۆژ دەداتە کۆمپانیاکان بۆ ئامادەکردنی پێش ئاشکراکردنی . Project Zero تیمێکی گووگڵە کە بەدوای دەگەڕێت لە زۆر کۆمپانیادا (و لە هی گووگڵ خۆیشیدا). کاتێک کێشەیەکی دەدۆزێتەوە، خاوەنی ئاگادار دەکاتەوە، کۆمپانیا بێت یان تاکە کەسێک و ٩٠ ڕۆژ، واتە نزیکەی سێ مانگ، مۆڵەتی دەداتێ بۆ چاککردن.
The rule in one line, and two exceptionsیاساکە بە یەک دێڕ و دوو بەدەرکراو
is the day the fix is released and the day the details are published (normal bugs, no grace period; no fix by day 90 counts as ). Example: a fix on day 83 gives .
ئەو ڕۆژەیە کە چارەسەرەکە بڵاو دەکرێتەوە و ئەو ڕۆژەیە کە وردەکارییەکان بڵاو دەکرێنەوە (بۆ ، بەبێ ماوەی زیادە؛ ئەگەر تا ڕۆژی ٩٠ چارەسەر نەبوو، وەک هەژمار دەکرێت). نموونە: چارەسەرێک لە ڕۆژی ٨٣ دەکاتە .
Two exceptions change the dates. A vendor that will have a fix within 14 more days may ask for a grace period; the details then come out on day 120. If attackers are already exploiting the bug against real users, the deadline is only 7 days (a fix inside those 7 days still gets the 30-day wait). Since July 2025 Project Zero has also run a transparency trial: soon after reporting, it lists each new report's vendor, product, date and deadline, but no technical details.
دوو بەدەرکراو ڕێکەوتەکان دەگۆڕن. فرۆشیارێک کە لە ماوەی ١٤ ڕۆژی تردا چارەسەری دەبێت دەتوانێت داوای ماوەی زیادە بکات؛ ئەوکات وردەکارییەکان لە ڕۆژی ١٢٠دا بڵاو دەکرێنەوە. ئەگەر ئێستا کونەکە دژی بەکار دەهێنن، کۆتا وادە تەنها ٧ ڕۆژە (چارەسەرێک لە ناو ئەو ٧ ڕۆژەدا هێشتا ٣٠ ڕۆژی چاوەڕوانیی دوای خۆی هەیە). لە تەممووزی ٢٠٢٥ەوە Project Zero تاقیکردنەوەیەکی ڕوونیش دەکات: زوو دوای ناردنی هەر ڕاپۆرتێکی نوێ، فرۆشیار، بەرهەم، ڕێکەوت و کۆتا وادەکەی لە لیستێکدا دادەنێت، بەڵام هیچ وردەکارییەکی تەکنیکی نا.
A vulnerability's journeyگەشتی خاڵێکی لاواز
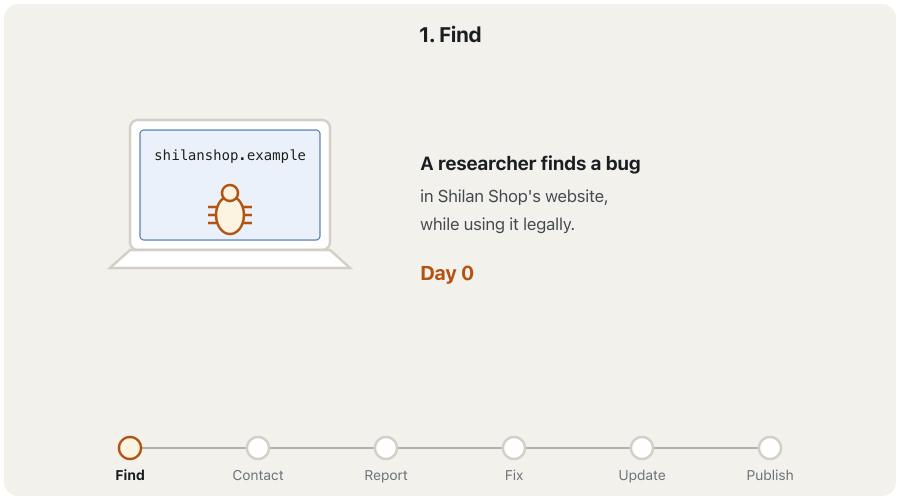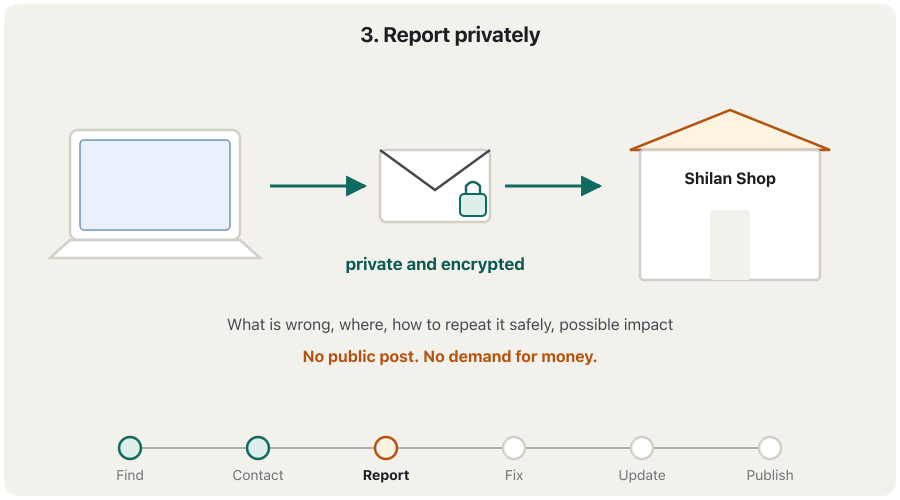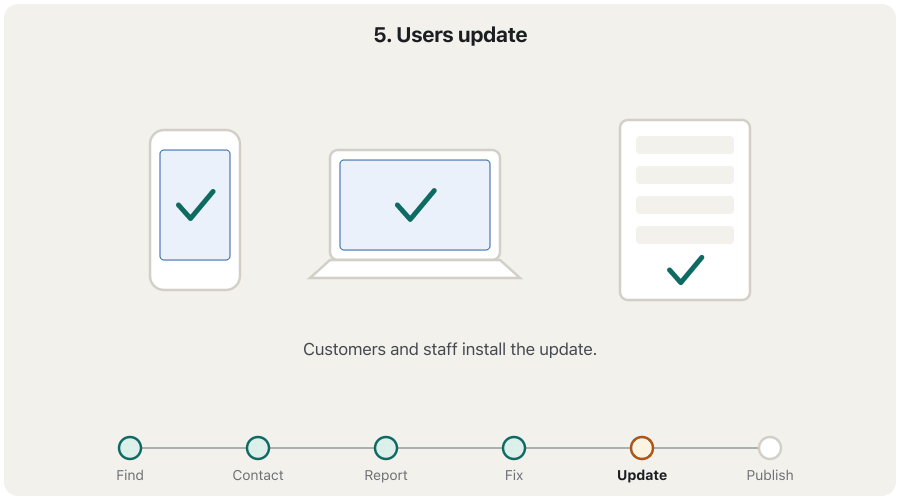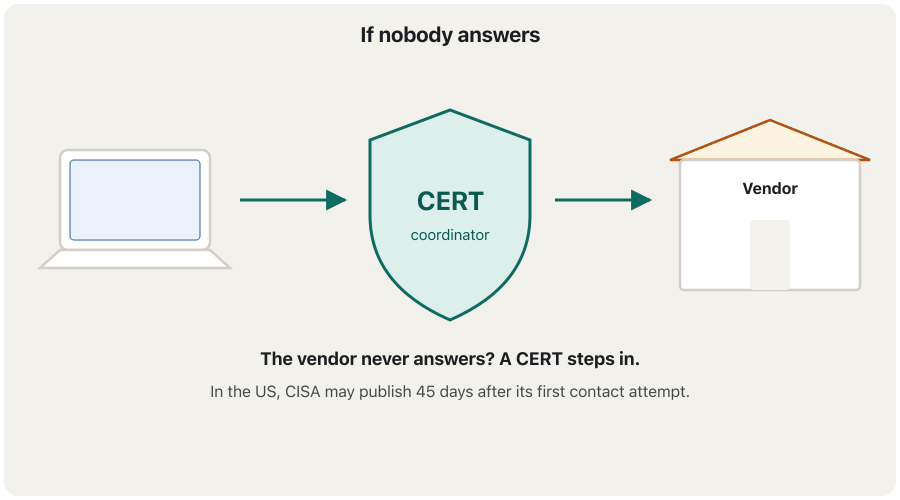
Here is the whole road of a well-handled vulnerability, from the moment it is found to the moment everyone can read about it. The animation follows one bug in a fictional online shop, Shilan Shop.
ئەمە هەموو ڕێگەی باش مامەڵەکراوە، لەو ساتەی دەدۆزرێتەوە تا ئەو ساتەی هەموو کەس دەتوانێت دەربارەی بخوێنێتەوە. ئەنیمەیشنەکە بەدوای لە فرۆشگایەکی سەرهێڵی خەیاڵیدا دەچێت، بە ناوی فرۆشگای شیلان.
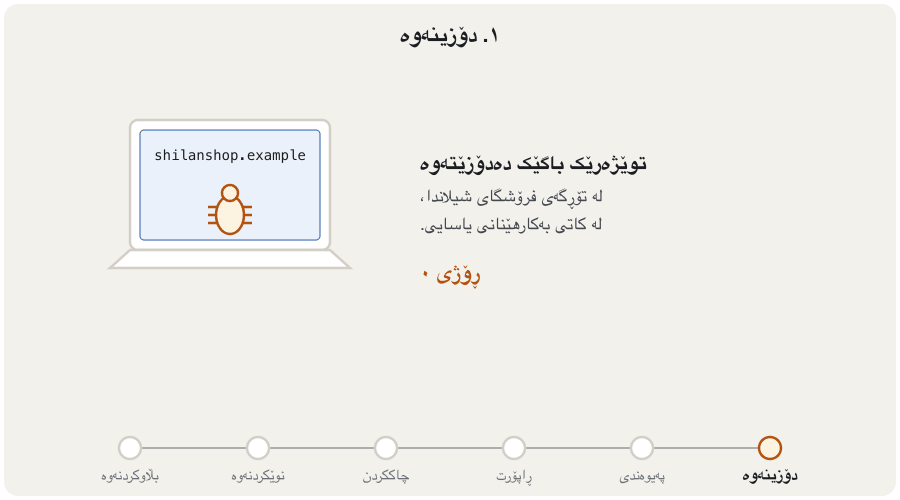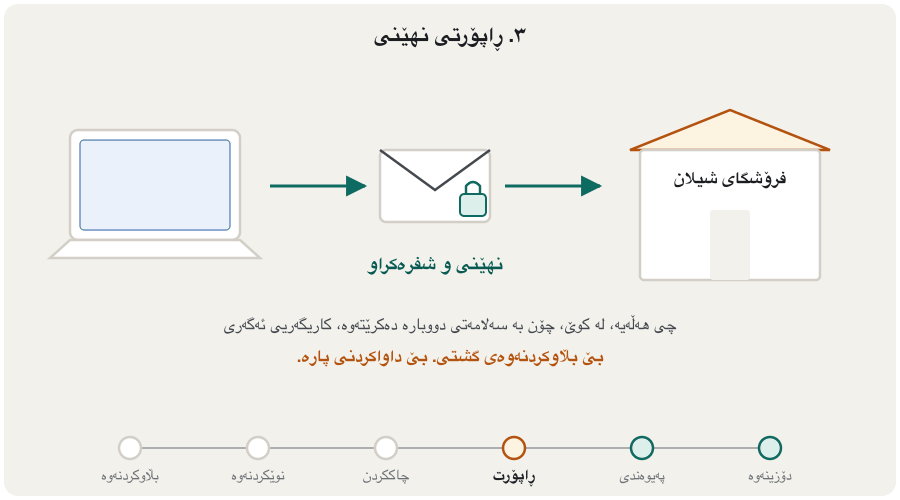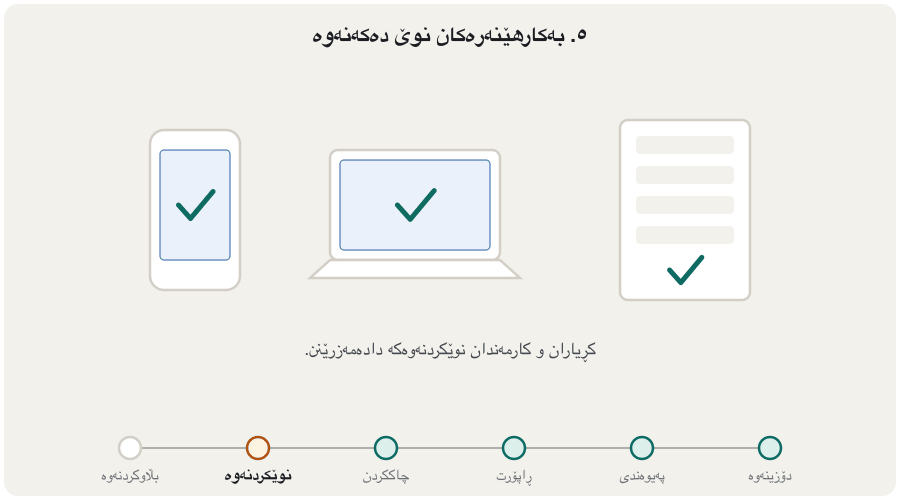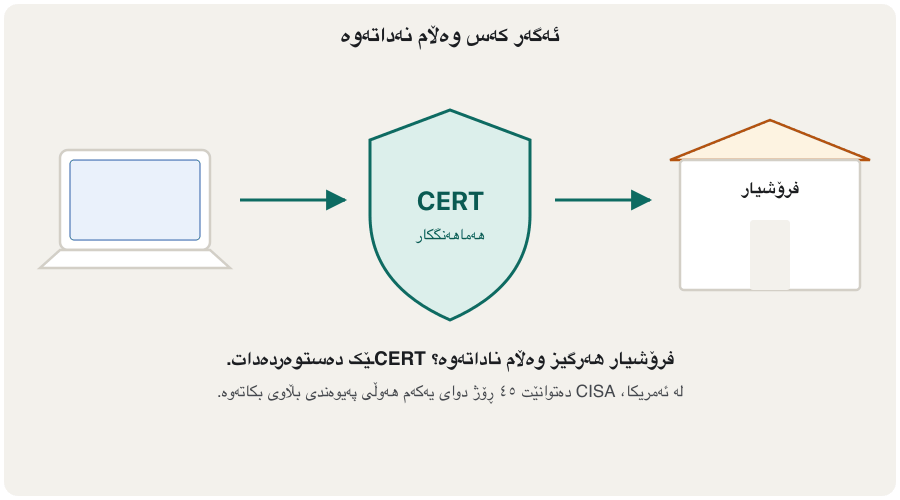
- Findدۆزینەوە
A researcher finds the bug, legally: in a bug bounty's scope, in her own copy of the software, or while using the site normally.
توێژەرێک بە شێوەی یاسایی دەدۆزێتەوە: لە ناو سنووری ، لە کۆپییەکی خۆیدا، یان لە کاتی بەکارهێنانی ئاسایی .
- Find the contactدۆزینەوەی پەیوەندی
She looks for the vendor's security contact: a
security.txtfile or a disclosure policy page.بەدوای پەیوەندیی فرۆشیاردا دەگەڕێت: فایلی
security.txtیان پەڕەی . - Report privatelyڕاپۆرتی نهێنی
She sends a clear report: what is wrong, where, how to reproduce it safely, and its possible impact. No public posts.
ڕوون دەنێرێت: چی هەڵەیە، لە کوێ، چۆن بە سەلامەتی دووبارە دەکرێتەوە و کاریگەرییە ئەگەرییەکەی. هیچ بڵاوکردنەوەیەکی گشتی نییە.
- Confirm and fixپشتڕاستکردنەوە و چاککردن
The vendor confirms, fixes and tests a patch. A CVE ID is reserved for it.
فرۆشیار پشتڕاستی دەکاتەوە، چاکی دەکات و تاقی دەکاتەوە. ناسنامەیەکی بۆی دیاری دەکرێت.
- Users updateبەکارهێنەرەکان نوێ دەکەنەوە
The patch is released and users install it.
بڵاو دەکرێتەوە و دایدەمەزرێنن.
- Publish and creditبڵاوکردنەوە و سوپاس
An advisory is published with the affected and fixed versions, and the researcher is thanked (and paid, if there is a bug bounty).
ئاگادارییەک بڵاو دەکرێتەوە لەگەڵ وەشانە زیانلێکەوتوو و چاککراوەکان و سوپاسی توێژەرەکە دەکرێت (و پارەی پێ دەدرێت، ئەگەر هەبێت).
Finding the right door: security.txt and disclosure policiesدۆزینەوەی دەرگای ڕاست: security.txt و سیاسەتەکانی ئاشکراکردن
The hardest step is often the second one: whom do I tell? An e-mail to 'info@' may be lost, and calling a random employee can look like a threat. RFC 9116 (2022) gives a simple answer: an organisation puts a small text file at a fixed address on its website, /.well-known/security.txt, that says where to send security reports.
قورسترین هەنگاو زۆرجار هەنگاوی دووەمە: کێ ئاگادار بکەمەوە؟ بۆ «info@» لەوانەیە ون بێت و پەیوەندیکردن بە کارمەندێکی هەڕەمەکی دەکرێت وەک هەڕەشە دەربکەوێت. RFC 9116 (٢٠٢٢) وەڵامێکی سادە دەدات: ڕێکخراوێک فایلێکی دەقیی بچووک لە ناونیشانێکی جێگیری دادەنێت، /.well-known/security.txt، کە دەڵێت بۆ کوێ بنێردرێن.
Contact: mailto:security@shilanshop.example
Contact: https://shilanshop.example/report-a-bug
Expires: 2027-09-30T23:00:00z
Encryption: https://shilanshop.example/pgp-key.txt
Policy: https://shilanshop.example/disclosure-policy
Acknowledgments: https://shilanshop.example/thanks
Preferred-Languages: en, ckb
Explain the codeڕوونکردنەوەی کۆدەکە
- Lineدێڕی 1-2
Contact (required): where to send reports, in order of preference. It may appear more than once.
Contact (پێویستە): بۆ کوێ بنێردرێن، بە ڕیزی پێشەنگی. دەکرێت زیاتر لە جارێک بێت.
- Lineدێڕی 3
Expires (required, once): after this date the file is out of date, so nobody trusts an old address.
Expires (پێویستە، یەک جار): دوای ئەم ڕێکەوتە فایلەکە کۆن دەبێت، بۆ ئەوەی کەس متمانە بە ناونیشانێکی کۆن نەکات.
- Lineدێڕی 4-7
Optional: a key for encrypted reports, the disclosure policy, a thank-you page, and the languages the team reads.
هەڵبژاردەیی: کلیلێک بۆ شفرەکراو، سیاسەتی ئاشکراکردن، پەڕەی سوپاس و ئەو زمانانەی تیمەکە دەیانخوێنێتەوە.
The file must be served over HTTPS, and the RFC recommends signing it so readers can check it is genuine. The Policy line points to the organisation's vulnerability disclosure policy (VDP): a public page that says what researchers may test, how to report, how fast the team answers, and that good-faith reporters will not be sued. A VDP usually pays no money; a bug bounty does.
فایلەکە دەبێت لە ڕێگەی HTTPSـەوە بنێردرێت و RFCـەکە پێشنیار دەکات واژۆی دیجیتاڵی بکرێت بۆ ئەوەی خوێنەران بپشکنن ڕاستەقینەیە. دێڕی Policy ئاماژە بە (VDP)ـی ڕێکخراوەکە دەکات: پەڕەیەکی گشتی کە دەڵێت توێژەران چی تاقی بکەنەوە، چۆن ڕاپۆرت بدەن، تیمەکە بە چ خێراییەک وەڵام دەداتەوە و سکاڵا لە ڕاپۆرتدەرانی نیازپاک تۆمار ناکرێت. VDP زۆرجار پارە نادات؛ دەیدات.
A public page where an organisation tells researchers how to report a to it, what they may test, how it will answer, and that it will not take legal action against good-faith reporters. Unlike a , it usually pays no money.
پەڕەیەکی گشتییە کە دامەزراوەیەک تێیدا بە توێژەران دەڵێت چۆن ڕاپۆرتی بدەن، چی تاقی بکەنەوە، چۆن وەڵام دەداتەوە و سکاڵای یاسایی لە ڕاپۆرتدەرانی نیازپاک ناکات. بە پێچەوانەی ، زۆرجار هیچ پارەیەک نادات.
CVE: one name for each vulnerabilityCVE: یەک ناو بۆ هەر خاڵێکی لاواز
A public list that gives each known a unique ID, such as CVE-2017-5638, so that vendors, scanners and news all talk about the same flaw.
لیستێکی گشتییە کە ناسنامەیەکی تایبەت دەدات بە هەر ناسراو، وەک CVE-2017-5638، بۆ ئەوەی دروستکەران، ئامرازەکانی پشکنین و هەواڵەکان هەموو باسی هەمان کێشە بکەن.
When a vulnerability is published, everyone needs to know they are talking about the same problem. The CVE Program (Common Vulnerabilities and Exposures) identifies, defines and catalogues publicly disclosed vulnerabilities: there is one CVE Record for each vulnerability. Each record has an ID such as CVE-2021-44228: the year it was assigned, then a number. That one is Log4Shell, a flaw in the Apache Log4j2 logging library, published on 10 December 2021 with the highest severity score, 10.0.
کاتێک بڵاو دەکرێتەوە، هەموو کەس پێویستە بزانێت باسی هەمان کێشە دەکەن. بەرنامەی (Common Vulnerabilities and Exposures) هەر کە بە ئاشکرا بڵاو کرابێتەوە دەناسێنێت، پێناسە دەکات و پۆلێن دەکات: بۆ هەر یەک تۆماری CVE هەیە. هەر تۆمارێک ناسنامەیەکی وەک CVE-2021-44228ـی هەیە: ئەو ساڵەی دیاری کراوە، پاشان ژمارەیەک. ئەمەیان Log4Shellـە، کەموکورتییەک لە کتێبخانەی تۆمارکردنی Apache Log4j2، کە لە ١٠ی کانوونی یەکەمی ٢٠٢١دا بە بەرزترین نمرەی مەترسی، ١٠.٠، بڵاو کرایەوە.
IDs are given by CVE Numbering Authorities (CNAs): organisations around the world, many of them software vendors, each allowed to number the vulnerabilities in its own area. The program was started in 1999 by the non-profit MITRE, and it is sponsored by the US agency CISA. In a coordinated disclosure, the vendor or the coordinator reserves the ID before publication, so the advisory, the patch notes and the security tools all use the same name. How CVE IDs are then used to find and patch systems is taught in CVE IDs: following one flaw through its life.
ناسنامەکان لەلایەن دەسەڵاتەکانی ژمارەدانی CVE (CNA)ـەوە دەدرێن: ڕێکخراوی جۆراوجۆر لە سەرانسەری جیهان، زۆربەیان فرۆشیاری ، کە هەریەکەیان ڕێگەی پێدراوە ناوچەی خۆی ژمارە بدات. بەرنامەکە لە ١٩٩٩دا لەلایەن ڕێکخراوی ناقازانجیی MITREـەوە دەستی پێکرد و دەزگای ئەمریکیی CISA پاڵپشتیی دەکات. لە ئاشکراکردنی هەماهەنگکراودا، فرۆشیار یان هەماهەنگکار پێش بڵاوکردنەوە ناسنامەکە دیاری دەکات، بۆ ئەوەی ئاگادارییەکە، تێبینییەکانی و ئامرازەکانی هەموویان هەمان ناو بەکار بهێنن. چۆنیەتیی بەکارهێنانی ناسنامەکانی CVE بۆ دۆزینەوە و سیستەمەکان لە ناسنامەکانی CVE: بەدواداچوونی یەک کێشە بە درێژایی ژیانی فێر دەبیت.
When nobody answers: CERTs and coordinatorsکاتێک کەس وەڵام ناداتەوە: CERT و هەماهەنگکاران
The lecture's advice: if the organisation has no clear reporting process, report the vulnerability to a cybersecurity mediator or a CERT (Computer Emergency Response Team) that can act as an intermediary. A CERT knows how to reach vendors, can check the report, and speaks for the researcher, so the researcher does not have to deal with an angry company alone.
ئامۆژگاریی وانەکە: ئەگەر ڕێکخراوەکە پرۆسەیەکی ڕوونی ڕاپۆرتدانی نەبوو، ڕاپۆرتی بدە بە ناوبژیوانێکی یان (تیمی وەڵامدانەوەی فریاکەوتنی کۆمپیوتەر) کە دەتوانێت ببێتە ناوەند. دەزانێت چۆن بگاتە فرۆشیاران، دەتوانێت بپشکنێت و لە جیاتی توێژەرەکە قسە دەکات، بۆ ئەوەی توێژەرەکە بە تەنها ڕووبەڕووی کۆمپانیایەکی تووڕە نەبێتەوە.
A team that receives reports of cyber incidents and , helps victims respond and shares warnings. Many countries have a national CERT, which can also pass a researcher's report to an organisation that has no security contact.
تیمێکە کە ڕاپۆرتی ڕووداوە سایبەرییەکان و وەردەگرێت، یارمەتیی قوربانییان دەدات بۆ وەڵامدانەوە و ئاگادارکردنەوە بڵاو دەکاتەوە. زۆر وڵات CERTـی نیشتیمانییان هەیە کە دەتوانێت ڕاپۆرتی توێژەرێک بگەیەنێتە دامەزراوەیەک کە هیچ پەیوەندییەکی بۆ کێشەکانی ئاسایش نییە.
Coordinators: the US, Europe and Iraqهەماهەنگکاران: ئەمریکا، ئەوروپا و عێراق
- United States: CISA. Anyone can report through CISA's system. CISA contacts the vendor, checks the details, helps get a CVE ID and publishes an advisory. If the vendor does not respond, CISA may publish as early as 45 days after its first attempt to contact it, even without a patch.
- European Union: under the NIS2 directive each country names a national CSIRT as its coordinator for vulnerability disclosure, and ENISA, the EU's cybersecurity agency, runs a European Vulnerability Database (EUVD) for published vulnerabilities.
- Iraq: the government's Cyber Events Response Team, IQ-CERT, is listed by the UN's Cyber Policy Portal as Iraq's national CERT, set up in 2018. Its website did not open in October 2026, and we found no public page saying whether members of the public can report vulnerabilities to it. A researcher in Iraq or the Kurdistan Region can first try the vendor's own contact, then a national CERT, or an international coordinator such as CISA for products used worldwide.
- ئەمریکا: CISA. هەر کەسێک دەتوانێت لە ڕێگەی سیستەمی CISAـەوە ڕاپۆرت بدات. CISA پەیوەندی بە فرۆشیارەوە دەکات، وردەکارییەکان دەپشکنێت، یارمەتیی وەرگرتنی ناسنامەی دەدات و ئاگادارییەک بڵاو دەکاتەوە. ئەگەر فرۆشیار وەڵام نەداتەوە، CISA دەتوانێت زووترین ٤٥ ڕۆژ دوای یەکەم هەوڵی پەیوەندیکردن بڵاوی بکاتەوە، تەنانەت بەبێ .
- یەکێتیی ئەوروپا: بەپێی ڕێنمایی NIS2، هەر وڵاتێک CSIRTـێکی نیشتیمانی دیاری دەکات وەک هەماهەنگکاری ئاشکراکردنی و ENISA، دەزگای یەکێتیی ئەوروپا، بنکەدراوەیەکی ئەوروپی (EUVD) بەڕێوە دەبات کە هەر بڵاو کرابێتەوە تێیدا تۆمار دەکرێت.
- عێراق: تیمی وەڵامدانەوەی ڕووداوە سایبەرییەکانی حکوومەت، IQ-CERT، لە دەروازەی سیاسەتی سایبەریی نەتەوە یەکگرتووەکاندا وەک نیشتیمانیی عێراق تۆمار کراوە کە لە ٢٠١٨دا دامەزراوە. لە تشرینی یەکەمی ٢٠٢٦دا نەدەکرایەوە. هیچ پەڕەیەکی گشتیمان نەدۆزییەوە کە بڵێت ئایا خەڵکی ئاسایی دەتوانن پێی ڕابگەیەنن یان نا. توێژەرێک لە عێراق یان هەرێمی کوردستان دەتوانێت سەرەتا پەیوەندیی خودی فرۆشیار تاقی بکاتەوە، پاشان نیشتیمانی، یان هەماهەنگکارێکی نێودەوڵەتیی وەک CISA بۆ ئەو بەرهەمانەی لە هەموو جیهاندا بەکار دێن.
Bug bountiesخەڵاتی دۆزینەوەی باگ
A programme in which a company pays a reward to outside researchers who find in its systems and report them privately, following published rules about what may be tested.
بەرنامەیەکە کە تێیدا کۆمپانیایەک خەڵات دەدات بەو توێژەرە دەرەکییانەی لە سیستەمەکانیدا دەدۆزنەوە و بە نهێنی ڕاپۆرتیان دەدەن، بەپێی ڕێسایەکی بڵاوکراوە کە دیاری دەکات چی دەتوانرێت تاقی بکرێتەوە.
Two English words first. A bug is a problem or mistake in software; a security hole is a bug that an attacker can use. A bounty is a reward, usually money. So a bug bounty is a reward that a company pays to people, usually ethical (white-hat) hackers and security researchers, who find problems in its website, app or software, especially security holes, and report them.
سەرەتا دوو وشەی ئینگلیزی. کێشە یان هەڵەیەکە لە ؛ کونی (security hole) کە دەتوانێت بەکاری بهێنێت. bounty واتە خەڵات، زۆرجار پارە. کەواتە خەڵاتێکە کە کۆمپانیایەک دەیدات بەو کەسانەی، زۆرجار و توێژەرانی ، کێشە لە ، یان دەدۆزنەوە (بە تایبەتی کونی ) و ڕاپۆرتیان دەدەن.
A shopkeeper in the bazaar is not sure whether his shop has a hidden way in: a loose back window, a weak lock on the store room. He tells the bazaar: 'Anyone who finds a secret way into my shop and tells me first, quietly, gets a reward. The more dangerous the way in, the bigger the reward.' Many sharp eyes now help him, and he pays only for real finds.
دوکاندارێک لە بازاڕ دڵنیا نییە دوکانەکەی ڕێگەیەکی شاراوەی هاتنە ژوورەوەی هەیە یان نا: پەنجەرەیەکی شلی پشتەوە، قوفڵێکی لاوازی کۆگا. بە بازاڕ دەڵێت: «هەر کەسێک ڕێگەیەکی نهێنی بۆ ناو دوکانەکەم بدۆزێتەوە و سەرەتا بە بێدەنگی پێم بڵێت، خەڵاتی دەدەمێ. هەتا ڕێگەکە مەترسیدارتر بێت، خەڵاتەکە گەورەترە.» ئێستا چاوی تیژی زۆر یارمەتیی دەدەن و تەنها پارەی دۆزینەوەی ڕاستەقینە دەدات.
Where the analogy stops workingسنووری ئەم نموونەیە
In a real programme the rules also say which doors you may try and how; trying a door that is not on the list is not covered.
لە بەرنامەیەکی ڕاستەقینەدا ڕێساکان ئەوەش دەڵێن کام دەرگا تاقی بکەیتەوە و چۆن؛ تاقیکردنەوەی دەرگایەک کە لە لیستەکەدا نییە ناگیرێتەوە.
Bug bountiesخەڵاتی دۆزینەوەی باگ
How a bug bounty worksخەڵاتی دۆزینەوەی باگ چۆن کار دەکات
How it works: the hacker reports the bug privately to the company; the company checks it, fixes it, and pays a reward that depends on how dangerous the bug is. Big companies such as Google, Apple, Meta and Microsoft, and even banks, run such programmes and invite white-hat hackers to test their systems. Google, for example, paid just under $12 million to more than 600 researchers in 2024, and more than $17 million to 747 researchers in 2025.
چۆن کار دەکات: هاکەرەکە ڕاپۆرتی بە نهێنی دەدات بە کۆمپانیاکە؛ کۆمپانیاکە دەیپشکنێت، چاکی دەکات و خەڵاتێک دەدات کە بەندە بە ئەوەی چەند مەترسیدارە. کۆمپانیا گەورەکانی وەک گووگڵ، ئەپڵ، مێتا و مایکرۆسۆفت و تەنانەت بانکەکانیش ئەم جۆرە بەرنامانە بەڕێوە دەبەن و بانگهێشت دەکەن سیستەمەکانیان تاقی بکەنەوە. بۆ نموونە گووگڵ لە ٢٠٢٤دا کەمێک کەمتر لە ١٢ ملیۆن دۆلاری بە زیاتر لە ٦٠٠ توێژەر داوە و لە ٢٠٢٥دا زیاتر لە ١٧ ملیۆن دۆلاری بە ٧٤٧ توێژەر.
What is new compared with the traditional way? Before, a company relied only on its own staff and perhaps one hired testing firm. With a bug bounty it uses hundreds or thousands of outside testers as well. This is crowdsourcing: getting help from many people around the world, not only from inside the company. In short, companies pay people to find security problems so that they are fixed before criminals find them.
چی نوێیە بە بەراورد لەگەڵ ڕێگە کۆنەکە؟ پێشتر کۆمپانیایەک تەنها پشتی بە کارمەندانی خۆی و لەوانەیە کۆمپانیایەکی تاقیکردنەوەی بەکرێگیراو دەبەست. بە سەدان یان هەزاران تاقیکەری دەرەکیش بەکار دەهێنێت. ئەمە crowdsourcingـە: وەرگرتنی یارمەتی لە خەڵکێکی زۆر لە سەرانسەری جیهان، نەک تەنها لە ناو کۆمپانیاکەوە. بە کورتی، کۆمپانیاکان پارە بە خەڵک دەدەن بۆ دۆزینەوەی کێشەکانی بۆ ئەوەی پێش ئەوەی تاوانکاران بیاندۆزنەوە چاک بکرێن.
This is the white-hat example from the hat table in Cyber Ethics and Ethical Hacking: 'working in Google's bug bounty program' is how curiosity becomes legal work.
ئەمە هەمان نموونەی کڵاو سپییە لە خشتەی کڵاوەکان لە ئەخلاقی سایبەری و هاککردنی ئەخلاقی: «کارکردن لە گووگڵدا» ئەو ڕێگەیەیە کە حەزی گەڕان دەکاتە کارێکی یاسایی.
Bug bountiesخەڵاتی دۆزینەوەی باگ
Platforms, programmes and scopeپلاتفۆرم، بەرنامە و سنوور
Many companies run their programmes through platforms such as HackerOne and Bugcrowd. The platform hosts the rules, receives the reports, helps the company check them, and pays the researchers. The lecture names HackerOne as a recognised place to report through.
زۆر کۆمپانیا بەرنامەکانیان لە ڕێگەی پلاتفۆرمی وەک HackerOne و Bugcrowdـەوە بەڕێوە دەبەن. پلاتفۆرمەکە ڕێساکان دادەنێت، وەردەگرێت، یارمەتیی کۆمپانیاکە دەدات بیانپشکنێت و پارە بە توێژەران دەدات. وانەکە HackerOne وەک شوێنێکی ناسراو بۆ ڕاپۆرتدان ناو دەهێنێت.
| Wordوشە | Meaningواتا |
|---|---|
| Bug bounty programme | Pays rewards for valid, previously unknown vulnerabilities. Duplicates and already-known issues are not paid.پاداشت دەدات بۆ هەر دروست و پێشتر نەناسراو. ڕاپۆرتی دووبارە و کێشەی پێشتر ناسراو پارەیان پێ نادرێت. |
| Vulnerability disclosure policy (VDP) (VDP) | A public channel to report; usually no cash reward.کەناڵێکی گشتی بۆ ڕاپۆرتدان؛ زۆرجار خەڵاتی پارەیی نییە. |
| Private programmeبەرنامەی تایبەت | Invite-only: a few selected researchers.تەنها بە بانگهێشت: چەند توێژەرێکی هەڵبژێردراو. |
| Public programmeبەرنامەی گشتی | Any registered researcher may take part.هەر توێژەرێکی تۆمارکراو دەتوانێت بەشداری بکات. |
| Scope (in / out)سنوور (ناو / دەرەوە) | The list of systems you may test (in scope) and must not touch (out of scope). Findings out of scope are not rewarded and are not protected.لیستی ئەو سیستەمانەی دەتوانیت تاقییان بکەیتەوە (ناو سنوور) و ئەوانەی نابێت دەستیان لێ بدەیت (دەرەوەی سنوور). دۆزینەوەی دەرەوەی سنوور نە خەڵاتی هەیە نە پاراستن. |
| Severity and rewardئاستی مەترسی و خەڵات | Rewards are set in advance by severity: a critical bug pays far more than a minor one.خەڵاتەکان پێشوەختە بەپێی ئاستی مەترسی دیاری دەکرێن: زۆر مەترسیدار زۆر زیاتر لە بچووک پارەی پێ دەدرێت. |
Safe harbour: the researcher's protection and rulesپەناگەی یاسایی: پاراستن و ڕێساکانی توێژەر
A promise in the rules of a or : research done in good faith and inside the rules is treated as authorised, and the organisation will not take legal action against the researcher. It does not cover testing outside the scope, or extortion.
بەڵێنێکە لە ڕێساکانی یان : ئەو توێژینەوەیەی بە نیازپاکی و لە ناو ڕێساکاندا کراوە بە ڕێگەپێدراو دادەنرێت و دامەزراوەکە سکاڵای یاسایی لە توێژەرەکە تۆمار ناکات. تاقیکردنەوە لە دەرەوەی سنووری دیاریکراو یان داواکردنی پارە بە هەڕەشە ناگرێتەوە.
A good programme does more than pay. It promises not to take legal action against researchers who follow its rules. This promise is called a safe harbour. HackerOne's Gold Standard Safe Harbor (2022), for example, says that good-faith research is treated as authorised, and the organisation will not pursue legal action against researchers who qualify. Good faith means accessing systems only to test, investigate or fix a flaw, avoiding harm, and using what you learn mainly to improve security. It does not cover research done to extort money, and it does not widen the scope.
بەرنامەیەکی باش لە پارەدان زیاتر دەکات. بەڵێن دەدات سکاڵای یاسایی لەو توێژەرانە تۆمار نەکات کە پەیڕەوی ڕێساکانی دەکەن. ئەم بەڵێنە پێی دەوترێت . بۆ نموونە پەناگەی یاسایی ستانداردی ئاڵتوونیی HackerOne (٢٠٢٢) دەڵێت توێژینەوەی نیازپاک وەک ڕێگەپێدراو هەژمار دەکرێت و ڕێکخراوەکە سکاڵای یاسایی لەسەر ئەو توێژەرانە تۆمار ناکات کە مەرجەکانیان تێدایە. نیازپاکی واتە دەستگەیاندن بە سیستەمەکان تەنها بۆ تاقیکردنەوە، لێکۆڵینەوە یان چاککردنی کەموکورتییەک، دوورکەوتنەوە لە زیان و بەکارهێنانی ئەوەی فێری دەبیت بە شێوەیەکی سەرەکی بۆ باشترکردنی . ئەو توێژینەوەیە ناگرێتەوە کە بۆ داواکردنی پارە بە هەڕەشە کراوە و سنوورەکەش فراوان ناکات.
How bug-bounty platforms work: companies set rules, researchers who follow them are rewarded, and safe harbour protects good-faith research.
چۆن کار دەکەن: کۆمپانیاکان ڕێسا دادەنێن، ئەو توێژەرانەی پەیڕەوی دەکەن پاداشت وەردەگرن و توێژینەوەی نیازپاک دەپارێزێت.
Plays 3:46-4:47 only: platforms, rules, rewards and the safe-harbour promise for good-faith research.
تەنها لە 3:46 تا 4:47 پەخش دەبێت: ، ڕێساکان، پاداشتەکان و بەڵێنی بۆ توێژینەوەی نیازپاک.
The researcher's do and don't listلیستی بیکە و مەیکەی توێژەر
The OWASP Vulnerability Disclosure Cheat Sheet gives researchers a clear list:
پەڕەی ئامۆژگارییەکانی OWASP دەربارەی ئاشکراکردنی لیستێکی ڕوون دەداتە توێژەران:
| Doبیکە | Don'tمەیکە |
|---|---|
| Test only with legal permission, inside the scope and rulesتەنها بە مۆڵەتی یاسایی و لە ناو سنوور و ڕێساکاندا تاقی بکەرەوە | Go out of scope 'just to look'بۆ «تەنها سەیرکردن» لە سنوور دەرچوون |
| Report through the official channel, with clear steps, evidence and impactلە ڕێگەی کەناڵی فەرمییەوە ڕاپۆرت بدە، بە هەنگاو، بەڵگە و کاریگەریی ڕوون | Demand payment before giving the detailsداواکردنی پارە پێش دانی وردەکارییەکان |
| Remove (redact) personal data from your report لە لابدە | Make silence a condition for money: that is extortionبێدەنگی بکەیتە مەرجی پارە: ئەوە باجسەندنە |
| Be patient and professional; agree the publication date with the vendorئارام و پیشەیی بە؛ لەسەر ڕێکەوتی بڵاوکردنەوە لەگەڵ فرۆشیار ڕێک بکەوە | Publish angrily without thinking of the usersبە تووڕەیی بڵاوکردنەوە بێ بیرکردنەوە لە |
| Check the programme's safe-harbour terms and your local law و مەرجەکانی لە بەرنامەکەدا و یاسای ناوخۆی خۆت بپشکنە | Assume a platform's rules protect you outside their scopeوا دابنێیت ڕێساکانی پلاتفۆرمێک لە دەرەوەی سنوورەکەیان دەتپارێزن |
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
The lecture ends with an interactive exercise. A hacker finds a vulnerability in a healthcare system but is not authorised to test it. Should they report it? Discuss the ethical and legal aspects. The next five screens give the lecture's structured answer, checked against today's law.
وانەکە بە ڕاهێنانێکی کارلێک کۆتایی دێت. هاکەرێک لە سیستەمێکی تەندروستیدا دەدۆزێتەوە، بەڵام ڕێگەی پێنەدراوە تاقیی بکاتەوە. ئایا ڕاپۆرتی بدات؟ لایەنە ئەخلاقی و یاساییەکان تاوتوێ بکە. پێنج پەردەی داهاتوو وەڵامە ڕێکخراوەکەی وانەکە دەدەن، کە بەرامبەر یاسای ئەمڕۆ پشکنراوە.
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
Ethical aspectsلایەنە ئەخلاقییەکان
- Do no harm. Reporting the hole can prevent harm to patients whose sensitive medical data could be exposed or misused. Ethical hacking serves the public interest.
- Responsible disclosure. Report to the affected party (the hospital) through proper channels so it can fix the issue before anyone exploits it. Making it public before the hospital can respond would expose the system to attacks.
- Impact on stakeholders. Doing nothing (inaction) is also a choice: an unreported hole may be found by criminals and harm patients, the hospital and public trust.
- Intent matters. A genuine wish to help fits ethical principles. But the hacker must not use the situation for personal gain, such as demanding payment, which could lead to accusations of extortion.
- زیان مەگەیەنە. ڕاپۆرتدانی کونەکە دەتوانێت ڕێ لە زیان بگرێت بۆ ئەو نەخۆشانەی پزیشکیی هەستیاریان لەوانەیە ئاشکرا بکرێت یان بە خراپی بەکار بهێنرێت. خزمەتی بەرژەوەندیی گشتی دەکات.
- . لە ڕێگەی کەناڵی دروستەوە ڕاپۆرت بدە بە لایەنی پەیوەندیدار (نەخۆشخانەکە) بۆ ئەوەی پێش ئەوەی کەس بەکاری بهێنێت چاکی بکات. ئاشکراکردنی پێش ئەوەی نەخۆشخانەکە بتوانێت وەڵام بداتەوە، سیستەمەکە بەرەو دەبات.
- کاریگەری لەسەر لایەنە پەیوەندیدارەکان. هیچنەکردنیش هەڵبژاردنێکە: کونێکی ڕاپۆرتنەدراو لەوانەیە تاوانکاران بیدۆزنەوە و زیان بە نەخۆشان، نەخۆشخانەکە و متمانەی گشتی بگەیەنن.
- نیاز گرنگە. ویستێکی ڕاستەقینە بۆ یارمەتیدان لەگەڵ بنەما ئەخلاقییەکان دەگونجێت. بەڵام هاکەرەکە نابێت دۆخەکە بۆ قازانجی کەسی بەکار بهێنێت، وەک داواکردنی پارە، کە دەتوانێت ببێتە هۆی تۆمەتی باجسەندن.
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
Legal aspectsلایەنە یاساییەکان
- Unauthorised access. Finding the hole may itself break laws such as the US Computer Fraud and Abuse Act (CFAA), which makes unauthorised access to or testing of computer systems a crime, whatever the intent (see Computer-crime laws). Other countries have similar laws.
- Risk of legal action. Even with good intent, reporting can expose the hacker to accusations of hacking or intrusion. This is exactly why a responsible-disclosure framework matters.
- Whistleblower protections. Some legal systems protect people who report problems in good faith.
- Privacy laws. Testing without authorisation may also break privacy laws, especially if it touches personal health information, for example HIPAA in the US or the GDPR in Europe.
- . دۆزینەوەی کونەکە خۆی لەوانەیە یاسای وەک یاسای ساختەکاری و خراپ بەکارهێنانی کۆمپیوتەری ئەمریکا () بشکێنێت، کە دەستڕاگەیشتن بە سیستەمە کۆمپیوتەرییەکان، یان تاقیکردنەوەیان، بەبێ ڕێگەپێدان بە تاوان دادەنێت، نیازەکە هەرچی بێت (بڕوانە یاساکانی تاوانی کۆمپیوتەری). وڵاتانی تریش یاسای هاوشێوەیان هەیە.
- مەترسیی سکاڵای یاسایی. تەنانەت بە نیازی باشیش، ڕاپۆرتدان دەتوانێت هاکەرەکە ڕووبەڕووی تۆمەتی هاککردن یان دزەکردن بکاتەوە. ڕێک لەبەر ئەمە چوارچێوەی گرنگە.
- پاراستنی ئاشکراکەرانی سەرپێچی. هەندێک سیستەمی یاسایی ئەو کەسانە دەپارێزن کە بە نیازپاکی ڕاپۆرتی کێشە دەدەن.
- یاساکانی . تاقیکردنەوە بەبێ ڕێگەپێدان لەوانەیە یاساکانی بشکێنێت، بە تایبەتی ئەگەر دەست بگاتە زانیاریی تەندروستیی کەسی، بۆ نموونە لە ئەمریکا یان لە ئەوروپا.
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
Two corrections: the GDPR and whistleblower protectionدوو ڕاستکردنەوە: GDPR و پاراستنی ئاشکراکەرانی سەرپێچی
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
Recommended actionsڕێکارە پێشنیارکراوەکان
- Follow a responsible-disclosure pathڕێگەیەکی ئاشکراکردنی بەرپرسیارانە بگرە
Find the proper channel: the organisation's security or IT department, or a recognised disclosure platform such as HackerOne. Do not make it public before it is fixed.
کەناڵی دروست بدۆزەرەوە: بەشی یان ITـی ڕێکخراوەکە، یان پلاتفۆرمێکی ناسراوی ئاشکراکردن وەک HackerOne. پێش چاککردن ئاشکرای مەکە.
- Document your actionsکارەکانت تۆمار بکە
Write down everything you did while discovering the hole (when, what, how), to show your ethical intent if you are questioned legally.
هەموو ئەوەی لە کاتی دۆزینەوەی کونەکەدا کردووتە بنووسە (کەی، چی، چۆن)، بۆ ئەوەی ئەگەر لە ڕووی یاساییەوە پرسیارت لێ کرا نیازە ئەخلاقییەکەت پیشان بدەیت.
- Consider a third-party mediatorبیر لە ناوبژیوانێکی لایەنی سێیەم بکەرەوە
If the hospital has no clear reporting process, report to a CERT, which can act as an intermediary.
ئەگەر نەخۆشخانەکە پرۆسەیەکی ڕوونی ڕاپۆرتدانی نەبوو، ڕاپۆرت بدە بە کە دەتوانێت ببێتە ناوەند.
- Seek legal adviceڕاوێژی یاسایی وەربگرە
A lawyer who knows cybersecurity law can help reduce the legal risks of reporting.
پارێزەرێک کە یاسای دەزانێت دەتوانێت یارمەتی بدات مەترسییە یاساییەکانی ڕاپۆرتدان کەم بکاتەوە.
Worked case: a hole in a hospital's systemنموونەی شیکراوە: کونێک لە سیستەمی نەخۆشخانەیەکدا
Key considerationsخاڵە گرنگەکان
- Ethically right, legally risky. Reporting fits ethical principles, but it can bring legal trouble if it is not handled correctly.
- Cooperation. Organisations should publish clear reporting policies that encourage responsible disclosure and protect ethical hackers from needless legal action.
- Public good and self-protection. The hacker must balance the duty to prevent harm with the need to protect themselves legally.
- لە ڕووی ئەخلاقییەوە ڕاست، لە ڕووی یاساییەوە مەترسیدار. ڕاپۆرتدان لەگەڵ بنەما ئەخلاقییەکان دەگونجێت، بەڵام ئەگەر بە دروستی مامەڵەی لەگەڵ نەکرێت دەتوانێت کێشەی یاسایی دروست بکات.
- هاوکاری. ڕێکخراوەکان دەبێت سیاسەتی ڕوونی ڕاپۆرتدان بڵاو بکەنەوە کە هانی بدات و لە سکاڵای یاسایی ناپێویست بپارێزێت.
- بەرژەوەندیی گشتی و پاراستنی خۆ. هاکەرەکە دەبێت هاوسەنگی بکات لە نێوان ئەرکی ڕێگرتن لە زیان و پێویستیی پاراستنی خۆی لە ڕووی یاساییەوە.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| Posting a bug on social media 'to warn people'بڵاوکردنەوەی لە «بۆ ئاگادارکردنەوەی خەڵک» | Attackers read it before users can update. پێش ئەوەی نوێی بکەنەوە دەیخوێننەوە. | Report privately; let the advisory warn people after the fix.بە نهێنی ڕاپۆرت بدە؛ با ئاگادارییەکە دوای چاککردن خەڵک ئاگادار بکاتەوە. |
| Thinking Project Zero always publishes on day 90وا بیرکردنەوە کە Project Zero هەمیشە لە ڕۆژی ٩٠دا بڵاو دەکاتەوە | If fixed earlier, it waits 30 days after the fix; exploited bugs get 7 days.ئەگەر زووتر چاک کرا، ٣٠ ڕۆژ دوای چارەسەرەکە چاوەڕێ دەکات؛ ٧ ڕۆژیان هەیە. | Use the rule.یاسای بەکار بهێنە. |
| Testing outside a bug bounty's scopeتاقیکردنەوە لە دەرەوەی سنووری | No reward and no safe harbour: it is unauthorised access.نە خەڵات نە : . | Read the scope first; ask if unsure.سەرەتا سنوورەکە بخوێنەرەوە؛ ئەگەر دڵنیا نەبوویت بپرسە. |
| Asking for money before giving detailsداواکردنی پارە پێش دانی وردەکاری | Can be extortion; safe harbours exclude it.دەکرێت باجسەندن بێت؛ نایگرێتەوە. | Report first; accept only the programme's published rewards.سەرەتا ڕاپۆرت بدە؛ تەنها خەڵاتە بڵاوکراوەکانی بەرنامەکە وەربگرە. |
| Calling the GDPR a hacking lawناونانی بە یاسای هاککردن | It is a data-protection law.یاسایەکی . | Name computer-misuse laws (CFAA, laws based on Directive 2013/40/EU) for access; the GDPR for personal data.بۆ دەستڕاگەیشتن یاساکانی خراپ بەکارهێنانی کۆمپیوتەر ناو ببە (، ئەو یاسایانەی لەسەر بنەمای ڕێنمایی 2013/40/EU دانراون)؛ بۆ . |
| Giving up when the vendor does not answerوازهێنان کاتێک فرۆشیار وەڵام ناداتەوە | The hole stays open for criminals.کونەکە بۆ تاوانکاران کراوە دەمێنێتەوە. | Ask a CERT or another coordinator to step in.داوا لە یان هەماهەنگکارێکی تر بکە دەستوەربدات. |
Exercisesڕاهێنانەکان
A cybersecurity professional discovers a vulnerability in widely used software. Should they disclose it publicly or notify the vendor? Give the ethical and the legal considerations, and say what they should do.
پسپۆڕێکی لە بەربڵاودا دەدۆزێتەوە. ئایا بە ئاشکرا بڵاوی بکاتەوە یان فرۆشیار ئاگادار بکاتەوە؟ بیرکردنەوە ئەخلاقی و یاساییەکان بڵێ و بڵێ چی بکات.
Show answerوەڵامەکە پیشان بدە
- Ethical: millions of users are at risk; publishing first would help attackers, while silence leaves the hole open. The responsible choice is to tell the vendor privately and give it time.
- Legal: if the flaw was found in their own copy of the software or inside a programme's scope, reporting is safe; if they tested someone else's live system without permission, they may have broken computer-misuse laws. Demanding money would be extortion.
- Action: find the vendor's security contact (
security.txt, VDP or bug bounty), send a clear private report, agree a deadline (for example 90 days), ask a CERT for help if there is no answer, and publish an advisory with a CVE ID after the fix.
- ئەخلاقی: ملیۆنان لە مەترسیدان؛ بڵاوکردنەوە پێشتر یارمەتیی دەدات، بێدەنگیش کونەکە کراوە دەهێڵێتەوە. هەڵبژاردنی بەرپرسیارانە ئەوەیە بە نهێنی فرۆشیار ئاگادار بکاتەوە و کاتی پێ بدات.
- یاسایی: ئەگەر کەموکورتییەکە لە کۆپییەکی خۆیدا یان لە ناو سنووری بەرنامەیەکدا دۆزرابێتەوە، ڕاپۆرتدان سەلامەتە؛ ئەگەر بەبێ مۆڵەت سیستەمی زیندووی کەسێکی تری تاقی کردبێتەوە، لەوانەیە یاساکانی خراپ بەکارهێنانی کۆمپیوتەری شکاندبێت. داواکردنی پارە باجسەندن دەبێت.
- کار: پەیوەندیی فرۆشیار بدۆزەرەوە (
security.txt، VDP یان )، ڕوون و نهێنی بنێرە، لەسەر ماوەیەک ڕێک بکەوە (بۆ نموونە ٩٠ ڕۆژ)، ئەگەر وەڵام نەبوو داوای یارمەتی لە بکە و دوای چاککردن ئاگادارییەک لەگەڵ ناسنامەی بڵاو بکەرەوە.
Use Project Zero's rules (no grace periods). On which day are the details published? (a) A normal bug fixed on day 25. (b) A normal bug never fixed. (c) A bug already used by attackers, fixed on day 5.
ڕێساکانی Project Zero بەکار بهێنە (بەبێ ماوەی زیادە). وردەکارییەکان لە کام ڕۆژدا بڵاو دەکرێنەوە؟ (أ) ئاسایی کە لە ڕۆژی ٢٥دا چاک کرا. (ب) ئاسایی کە هەرگیز چاک نەکرا. (ج) کە پێشتر بەکاری دەهێنن و لە ڕۆژی ٥دا چاک کرا.
Show answerوەڵامەکە پیشان بدە
(c) The 7-day deadline was met, so the 30-day window after the fix still applies.
(ج) ماوەی ٧ ڕۆژەکە پارێزرا، بۆیە ماوەی ٣٠ ڕۆژ دوای چارەسەرەکە هەر جێبەجێ دەبێت.
Write a security.txt file for a fictional university website karwan-uni.example. Reports go by e-mail to the security office; the file should expire on 30 June 2027 (less than a year ahead, as the RFC recommends); the team reads English and Kurdish.
فایلێکی security.txt بنووسە بۆ زانکۆیەکی خەیاڵی بە ناوی karwan-uni.example. بە دەچن بۆ نووسینگەی ؛ فایلەکە لە ٣٠ی حوزەیرانی ٢٠٢٧دا بەسەر دەچێت (کەمتر لە ساڵێک لە ئێستاوە، وەک RFCـەکە پێشنیاری دەکات)؛ تیمەکە ئینگلیزی و کوردی دەخوێنێتەوە.
Show answerوەڵامەکە پیشان بدە
Contact: mailto:security@karwan-uni.example
Expires: 2027-06-30T23:59:00z
Preferred-Languages: en, ckb
Contact and Expires are required; Preferred-Languages is optional but useful here. Put the file at https://karwan-uni.example/.well-known/security.txt.
Contact و Expires پێویستن؛ Preferred-Languages هەڵبژاردەییە بەڵام لێرەدا بەسوودە. فایلەکە لە https://karwan-uni.example/.well-known/security.txt دابنێ.
For each case, say where the report should go: (a) a bug in an app whose company runs a HackerOne programme that lists the app in scope; (b) a bug in a small clinic's website with no contact for security and no answer to e-mails; (c) a bug in a popular open-source library whose project page has a SECURITY.md file with an e-mail address.
بۆ هەر حاڵەتێک بڵێ بۆ کوێ بچێت: (أ) لە کە کۆمپانیاکەی بەرنامەیەکی HackerOneـی هەیە و ئەپەکە لە ناو سنووردایە؛ (ب) لە نەخۆشخانەیەکی بچووکدا کە پەیوەندیی نییە و وەڵامی نادرێتەوە؛ (ج) لە کتێبخانەیەکی سەرچاوەکراوەی بەناوبانگدا کە پەڕەی پڕۆژەکەی فایلێکی SECURITY.mdـی هەیە بە ناونیشانی .
Show answerوەڵامەکە پیشان بدە
- (a) Through the HackerOne programme, following its rules: scope, safe harbour and rewards.
- (b) To a CERT (the national CERT, or a coordinator such as CISA), which contacts the clinic.
- (c) Privately to the e-mail in
SECURITY.md, not as a public issue on the project page.
- (أ) لە ڕێگەی بەرنامەی HackerOneـەوە، بەپێی ڕێساکانی: سنوور، و خەڵات.
- (ب) بۆ ( نیشتیمانی، یان هەماهەنگکارێکی وەک CISA)، کە پەیوەندی بە نەخۆشخانەکەوە دەکات.
- (ج) بە نهێنی بۆ ئەو لە
SECURITY.mdدایە، نەک وەک بابەتێکی گشتی لە پەڕەی پڕۆژەکە.
Summary and reviewکورتە و پێداچوونەوە
- Responsible (coordinated) disclosure: report privately, give time to fix, publish after the fix. Full disclosure publishes at once: it warns fast but helps attackers.
- Project Zero: 90 days to fix; details 30 days after a fix (); 7 days for bugs already exploited.
- Find the contact in
/.well-known/security.txt(Contact and Expires are required) or the vendor's VDP; a CVE ID gives each published vulnerability one name. - No answer? A CERT (CISA, a national CSIRT, IQ-CERT in Iraq) can coordinate; CISA may publish after 45 days of vendor silence.
- Bug bounties pay outside researchers (crowdsourcing) by severity, inside a published scope; a safe harbour promises no legal action for good-faith research, but never covers extortion or out-of-scope testing.
- (هەماهەنگکراو): بە نهێنی ڕاپۆرت بدە، کات بۆ چاککردن بدە، دوای چاککردن بڵاوی بکەرەوە. یەکسەر بڵاو دەکاتەوە: خێرا ئاگادار دەکاتەوە بەڵام یارمەتیی دەدات.
- Project Zero: ٩٠ ڕۆژ بۆ چاککردن؛ وردەکاری ٣٠ ڕۆژ دوای چارەسەر ()؛ ٧ ڕۆژ بۆ .
- پەیوەندی لە
/.well-known/security.txt(Contact و Expires پێویستن) یان VDPـی فرۆشیاردا بدۆزەرەوە؛ ناسنامەی یەک ناو دەداتە هەر بڵاوکراوە. - وەڵام نییە؟ (CISA، CSIRTـی نیشتیمانی، IQ-CERT لە عێراق) دەتوانێت هەماهەنگی بکات؛ CISA دەتوانێت دوای ٤٥ ڕۆژ بێدەنگیی فرۆشیار بڵاوی بکاتەوە.
- بەپێی ئاستی مەترسی و لە ناو سنوورێکی بڵاوکراوەدا پارە دەداتە توێژەرانی دەرەکی (crowdsourcing)؛ بەڵێنی سکاڵا تۆمارنەکردن دەدات بۆ توێژینەوەی نیازپاک، بەڵام هەرگیز باجسەندن یان تاقیکردنەوەی دەرەوەی سنوور ناگرێتەوە.
What are the three ways to disclose a vulnerability?سێ ڕێگەی ئاشکراکردنی خاڵێکی لاواز چین؟
Private, full and coordinated (responsible) disclosure.
ئاشکراکردنی تایبەت، و ئاشکراکردنی هەماهەنگکراو ().
A normal bug is fixed on day 70. When does Project Zero publish?باگێکی ئاسایی لە ڕۆژی ٧٠دا چاک دەکرێت. Project Zero کەی بڵاوی دەکاتەوە؟
Day 100: .
ڕۆژی ١٠٠: .
What is the difference between a VDP and a bug bounty?جیاوازیی نێوان VDP و خەڵاتی دۆزینەوەی باگ چییە؟
Both invite reports; a bug bounty also pays rewards, a VDP usually does not.
هەردووکیان داوای ڕاپۆرت دەکەن؛ خەڵاتیش دەدات، VDP زۆرجار نایدات.
Name four recommended actions for the hacker in the hospital case.چوار ڕێکاری پێشنیارکراو بۆ هاکەرەکە لە نموونەی نەخۆشخانەکەدا ناو ببە.
Report through proper channels and do not publish before the fix; document your actions; use a CERT as mediator if needed; seek legal advice.
لە ڕێگەی کەناڵی دروستەوە ڕاپۆرت بدە و پێش چاککردن بڵاوی مەکەرەوە؛ کارەکانت تۆمار بکە؛ ئەگەر پێویست بوو وەک ناوبژیوان بەکار بهێنە؛ ڕاوێژی یاسایی وەربگرە.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Intellectual Property, Plagiarism and Software Licencesموڵکی هزری، دزیی زانستی و مۆڵەتەکانی بەکارهێنان
Related lecturesوانە پەیوەندیدارەکان
- Computer-Crime Laws: Budapest, the CFAA, the UK and the Law at Homeیاساکانی تاوانی سایبەری: بوداپێست، CFAA، بەریتانیا و یاسا لە وڵاتی خۆمان
- Threats, Vulnerabilities, Attacks and Riskهەڕەشەکان، خاڵە لاوازەکان، هێرشەکان و مەترسی
- Europe's GDPR: Rights, Breach Notification and FinesGDPRـی ئەوروپا: ماف، ئاگادارکردنەوەی دزەکردنی دراوە و سزای دارایی
- Health Data and National Rules: HIPAA and China's Cybersecurity Lawدراوەی تەندروستی و یاسا نیشتیمانییەکان: HIPAA و یاسای ئاسایشی سایبەری چین
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- OWASP Cheat Sheet Series: Vulnerability Disclosure Cheat Sheet
- CERT/CC: The CERT Guide to Coordinated Vulnerability Disclosure
- Google Project Zero: Vulnerability Disclosure Policy (90+30, 7-day in-the-wild, grace period)
- Google Project Zero: Reporting transparency (trial since 29 July 2025)
- RFC 9116: A File Format to Aid in Security Vulnerability Disclosure (security.txt)
- CISA: Coordinated Vulnerability Disclosure Process
- CVE Program: About the CVE Program (overview page source)
- NVD: CVE-2021-44228 (Apache Log4j2, published 10 December 2021, CVSS 3.1 score 10.0)
- ENISA: Vulnerability disclosure (CSIRTs Network, European Vulnerability Database)
- UNIDIR Cyber Policy Portal: Iraq, Cyber Events Response Team (CERT), established 2018
- Bugcrowd: What is a bug bounty? (bounty vs VDP, public vs private, scope)
- HackerOne Docs: Safe Harbor (Gold Standard Safe Harbor)
- Google: VRP 2025 Year in Review (31 March 2026)
- Google: Vulnerability Reward Program 2024 in review
- Directive 2013/40/EU on attacks against information systems (article list)
- Directive (EU) 2019/1937 on the protection of persons who report breaches of Union law, Chapter I (Article 4, personal scope)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.