Chapterبەش 3 · Lectureوانە 3.5
Europe's GDPR: Rights, Breach Notification and FinesGDPRـی ئەوروپا: ماف، ئاگادارکردنەوەی دزەکردنی دراوە و سزای دارایی
The EU's General Data Protection Regulation: who it protects and who must obey it (wherever they are), consent and the other lawful bases, the eight rights of a data subject, the 72-hour breach notification, accountability through DPIAs and DPOs, the two tiers of fines with worked 'whichever is higher' examples, and the Amazon and Meta cases. The seven GDPR principles are linked, not repeated.
ڕێسای گشتیی یەکێتیی ئەوروپا: کێ دەپارێزێت و کێ دەبێت پابەندی بێت (لە هەر کوێیەک بن)، و تر، هەشت مافەکەی ، لە ماوەی ٧٢ کاتژمێردا، لە ڕێگەی DPIA و DPOـەوە، دوو ئاستی سزای دارایی بە نموونەی شیکراوەی «کامیان زیاتر بێت» و دۆسیەکانی ئەمازۆن و مێتا. حەوت بنەماکەی بەستەریان بۆ دانراوە، دووبارە ناکرێنەوە.
What you will learnچی فێر دەبیت
- Decide whether the GDPR applies to an organisation, including one outside Europe.
- Choose the right lawful basis and explain what makes consent valid.
- Name the eight rights of a data subject and apply them to everyday requests.
- Apply the 72-hour breach notification rule and the duty to tell affected people.
- Compute the maximum GDPR fine with 'whichever is higher' for both tiers.
- بڕیار بدەیت ئایا ڕێکخراوێک دەگرێتەوە، لەوانە ڕێکخراوێک لە دەرەوەی ئەوروپا.
- دروست هەڵبژێریت و ڕوونی بکەیتەوە چی دروست دەکات.
- هەشت مافەکەی ناو ببەیت و لەسەر داواکاریی ڕۆژانە جێبەجێیان بکەیت.
- یاسای ٧٢ کاتژمێرەی و ئەرکی ئاگادارکردنەوەی خەڵکی زیانلێکەوتوو جێبەجێ بکەیت.
- زۆرترین سزای بە «کامیان زیاتر بێت» بۆ هەردوو ئاست بژمێریت.
Laws that protect data and peopleئەو یاسایانەی دراوە و خەڵک دەپارێزن
Good intentions are not enough to protect people's data, so many places have legal frameworks for cybersecurity: laws and regulations about cybercrime, data protection and digital rights. Digital rights are the rights people have online, and the limits on what others may do with them and their data. The lecture names three well-known examples, one from each big region:
نیازی باش بەس نییە بۆ پاراستنی خەڵک، بۆیە زۆر شوێن چوارچێوەی یاسایییان بۆ هەیە: یاسا و ڕێسا دەربارەی ، و مافە دیجیتاڵییەکان. مافە دیجیتاڵییەکان ئەو مافانەن کە خەڵک لە سەرهێڵدا هەیانە و ئەو سنوورانەن کە کەسانی تر لە مامەڵەکردن لەگەڵ خۆیان و پێیانەوە پابەندن. وانەکە سێ نموونەی ناسراو دەهێنێتەوە، هەریەکەیان لە ناوچەیەکی گەورەوە:
| Lawیاسا | Whereلە کوێ | Main focusناوەڕۆکی سەرەکی | Lessonوانە |
|---|---|---|---|
| GDPR | European Unionیەکێتیی ئەوروپا | Personal data of people in the EU خەڵک لە یەکێتیی ئەوروپادا | this lessonئەم وانەیە |
| HIPAA | United Statesئەمریکا | Health data تەندروستی | HIPAA and ChinaHIPAA و چین |
| Cybersecurity Law (with PIPL and DSL)یاسای (لەگەڵ PIPL و DSL) | Chinaچین | Network security, important data, data stored in China ، گرنگ، لە ناو چیندا | HIPAA and ChinaHIPAA و چین |
The first is the General Data Protection Regulation (GDPR), the European Union's Regulation (EU) 2016/679. A regulation is a kind of EU law that applies directly, in the same words, in every member country. The GDPR has applied since 25 May 2018.
یەکەمیان ڕێسای گشتیی ()ـە، ڕێسای (EU) 2016/679ـی یەکێتیی ئەوروپا. ڕێسا (regulation) جۆرێکە لە یاسای یەکێتیی ئەوروپا کە ڕاستەوخۆ و بە هەمان دەق لە هەموو وڵاتێکی ئەندامدا جێبەجێ دەکرێت. لە ٢٥ی ئایاری ٢٠١٨ەوە جێبەجێ دەکرێت.
What the GDPR protects, and who must obey itGDPR چی دەپارێزێت و کێ دەبێت پابەندی بێت
Purpose. The GDPR protects the personal data and privacy of individuals in the European Union (EU) and the European Economic Area (EEA: the EU countries plus Iceland, Liechtenstein and Norway). It also controls the export of personal data outside the EU: data may leave only to countries or companies that give it suitable protection.
مەبەست. و تاکەکان لە یەکێتیی ئەوروپا و ناوچەی ئابووریی ئەوروپا (وڵاتانی یەکێتیی ئەوروپا لەگەڵ ئایسلەندا، لیختنشتاین و نەرویج) دەپارێزێت. هەروەها کۆنترۆڵی ناردنە دەرەوەی بۆ دەرەوەی یەکێتیی ئەوروپا دەکات: تەنها دەتوانێت بڕوات بۆ ئەو وڵات یان کۆمپانیایانەی پاراستنی گونجاوی بۆ دابین دەکەن.
Scope. The GDPR applies to any organisation that handles the data of people in the EU, wherever the organisation is located (Article 3). In practice it applies when an organisation (1) has an office or branch in the EU, or (2) offers goods or services to people who are in the EU, even for free, or (3) monitors the behaviour of people in the EU, for example by tracking them online.
بواری جێبەجێکردن. هەر ڕێکخراوێک دەگرێتەوە کە مامەڵە لەگەڵ خەڵکی ناو یەکێتیی ئەوروپا دەکات، ڕێکخراوەکە لە هەر کوێیەک بێت (ماددەی ٣). لە ڕاستیدا کاتێک جێبەجێ دەبێت کە ڕێکخراوێک (١) نووسینگە یان لقێکی لە یەکێتیی ئەوروپا هەبێت، یان (٢) کاڵا یان خزمەتگوزاری پێشکەش بە خەڵکی ناو یەکێتیی ئەوروپا بکات، تەنانەت بە خۆڕایی، یان (٣) چاودێریی ڕەفتاری خەڵکی ناو یەکێتیی ئەوروپا بکات، بۆ نموونە بە شوێنکەوتنیان لە سەرهێڵدا.
Words you need: controller and processorوشە پێویستەکان: کۆنترۆڵکەری دراوە و چارەسەرکەری دراوە
The key words (personal data, data subject, data controller) and the seven GDPR principles are already taught in RAID and Web Security of the Database Administration course; read them there, they are not repeated here. One more word you need: a data processor is an organisation that uses personal data for a controller and only on its instructions, for example a cloud or payroll company.
وشە سەرەکییەکان (، ، ) و حەوت بنەماکەی پێشتر لە RAID و ئاسایشی وێبـی کۆرسی بەڕێوەبردنی بنکەدراوەدا وتراونەتەوە؛ لەوێ بیانخوێنەرەوە، لێرە دووبارە ناکرێنەوە. وشەیەکی تر کە پێویستە: ڕێکخراوێکە کە بۆ و تەنها بەپێی ڕێنماییەکانی ئەو بەکار دەهێنێت، بۆ نموونە کۆمپانیایەکی هەوری یان مووچە.
An organisation that uses on behalf of a and only on its instructions, for example a cloud, payroll or mailing company. Under the it must tell the controller about a without undue delay.
دامەزراوەیەکە کە لە جیاتی و تەنها بەپێی ڕێنماییەکانی ئەو بەکار دەهێنێت، بۆ نموونە کۆمپانیایەکی هەوری، مووچە یان ناردنی ئیمەیڵ. بەپێی دەبێت بەبێ دواکەوتنی ناپێویست لە ئاگادار بکاتەوە.
Sensitive data and special categoriesدراوەی کەسیی هەستیار و جۆرە تایبەتەکان
Some personal data is sensitive: if it is exposed, it can cause serious harm or embarrassment. Examples are health records, fingerprints and face scans (biometric data), bank and card details, and private photos or documents. The GDPR gives the most sensitive kinds extra protection as special categories (Article 9): health data, genetic data, biometric data used to identify someone, racial or ethnic origin, political opinions, religious beliefs, trade-union membership, and sex life or sexual orientation. They may be used only in narrow cases, for example with the person's explicit consent. Financial data is not on that list, but its exposure still hurts people, so it also needs strong protection such as encryption and strong sign-in.
هەندێک هەستیارە: ئەگەر ئاشکرا بێت، دەتوانێت زیانێکی گەورە یان شەرمەزاری دروست بکات. نموونەکان: تۆماری تەندروستی، پەنجەمۆر و وێنەی ڕووخسار ()، زانیاریی بانک و کارت و وێنە یان بەڵگەنامە تایبەتەکان. جۆرە هەرە هەستیارەکان وەک جۆرە تایبەتەکان (special categories، ماددەی ٩) پاراستنی زیاتر دەدات: تەندروستی، بۆماوەیی، کە بۆ ناسینەوەی کەسێک بەکار دێت، بنەچەی ڕەگەزی یان نەتەوەیی، بیروڕای سیاسی، باوەڕی ئایینی، ئەندامێتی لە سەندیکادا و ژیانی سێکسی یان ئاراستەی سێکسی. تەنها لە حاڵەتی تەسکدا دەکرێت بەکار بهێنرێن، بۆ نموونە بە ڕوون و ئاشکرای خاوەنەکەی. زانیاریی دارایی لەو لیستەدا نییە، بەڵام ئاشکرابوونی هێشتا زیان بە خەڵک دەگەیەنێت، بۆیە ئەویش پێویستی بە پاراستنی بەهێزە، وەک و چوونەژوورەوەی بەهێز.
Consent and the other lawful basesڕەزامەندی و بنەما یاساییەکانی تر
A person's clear and free agreement to something, such as letting an organisation use their or letting testers attack a system. Under the it must be given actively, for a specific purpose, and it can be withdrawn.
ڕازیبوونی ڕوون و ئازادی کەسێکە بە شتێک، وەک ڕێگەدان بە دامەزراوەیەک کە بەکار بهێنێت یان ڕێگەدان بە تاقیکەرەوەکان کە هێرش بکەنە سەر سیستەمێک. بەپێی دەبێت بە کردەوە و بۆ مەبەستێکی دیاریکراو بدرێت و دەتوانرێت بگەڕێنرێتەوە.
The notes' first key provision is consent: organisations must obtain explicit (clear) consent from individuals to process their data. In plain words, they must ask users' permission in advance before using their data. For consent to count, the GDPR says it must be freely given (not forced, and not tied to a service that does not need the data), specific, informed and clear; the organisation must be able to prove it; and the person can withdraw it at any time, as easily as they gave it.
یەکەم خاڵی سەرەکیی تێبینییەکان : ڕێکخراوەکان دەبێت ڕوون (بە ئاشکرا) لە تاکەکان وەربگرن بۆ بەکارهێنانی . بە زمانێکی سادە: دەبێت پێشوەختە ئیزن لە وەربگرن پێش ئەوەی بەکار بهێنن. بۆ ئەوەی حیساب بکرێت، دەڵێت دەبێت بە ئارەزووی خۆ بێت (بە زۆر نەبێت و بە خزمەتگوزارییەکەوە نەبەسترابێت کە پێویستی بەو نییە)، دیاریکراو، ئاگادارانە و ڕوون بێت؛ ڕێکخراوەکە دەبێت بتوانێت بیسەلمێنێت؛ و کەسەکە دەتوانێت هەر کاتێک بیەوێت بیکشێنێتەوە، بە هەمان ئاسانیی دانی.
The six lawful basesشەش بنەمای یاسایی
| Lawful basis (Art. 6) (ماددەی ٦) | Example: Hana's online bakeryنموونە: نانەواخانەی سەرهێڵی هانا |
|---|---|
| (a) Consent(أ) | Sending offers by e-mail to customers who ticked 'yes'ناردنی داشکاندن بە بۆ ئەو کڕیارانەی «بەڵێ»یان هەڵبژاردووە |
| (b) Contract(ب) گرێبەست | Using the address to deliver an orderبەکارهێنانی ناونیشان بۆ گەیاندنی داواکارییەک |
| (c) Legal obligation(ج) ئەرکی یاسایی | Keeping invoices because tax law requires itهەڵگرتنی پسوولەکان چونکە یاسای باج داوای دەکات |
| (d) Vital interests(د) پاراستنی ژیان | Telling a doctor about a customer's allergy in an emergencyپێگوتنی پزیشکێک دەربارەی هەستیارییەکی کڕیارێک لە کاتی فریاکەوتندا |
| (e) Public task(هـ) ئەرکی گشتی | Not for a bakery: used by public bodies such as a city councilبۆ نانەواخانە نییە: دەزگا گشتییەکان بەکاری دەهێنن، وەک شارەوانی |
| (f) Legitimate interests(و) بەرژەوەندیی ڕەوا | Keeping a short log of logins to stop fraud, if it does not override customers' rightsهەڵگرتنی کورتی چوونەژوورەوەکان بۆ ڕێگرتن لە ساختەکاری، ئەگەر بەسەر مافی کڕیاراندا زاڵ نەبێت |
The data subject's rightsمافەکانی خاوەنی دراوە
The notes' second key provision: individuals have rights over their data. The notes name four, with the owner's examples:
دووەم خاڵی سەرەکیی تێبینییەکان: تاکەکان مافیان هەیە بەسەر . تێبینییەکان چوار مافیان ناو دەهێنن، لەگەڵ نموونەکانی خاوەنەکەیان:
- Access: the user must be allowed to reach and see the data an organisation holds about them.
- Rectification (to correct something wrong): if the data is wrong, the user can ask the company to correct it.
- Erasure, the 'right to be forgotten': the user can ask for data to be deleted. The owner's example: if I close my Facebook account, Facebook should delete the account and its data completely.
- Data portability: being able to move your data. A laptop is portable, a desktop stays in its place; in the same way, the user has the right to get their data in a format they can carry from one company to another.
- : دەبێت ڕێگە بە بدرێت دەست بگەیەنێتە ئەو ڕێکخراوێک دەربارەی ئەو هەیەتی و بیبینێت.
- : ئەگەر هەڵە بێت، دەتوانێت داوا لە کۆمپانیاکە بکات ڕاستی بکاتەوە.
- ، «مافی لەبیرکردن»: دەتوانێت داوای سڕینەوەی بکات. نموونەی خاوەنی تێبینییەکان: ئەگەر هەژمارەکەم لە فەیسبووک داخست، فەیسبووک دەبێت هەژمارەکە و بە تەواوی بسڕێتەوە.
- : توانای گواستنەوەی . لاپتۆپ دەگوازرێتەوە، دێسکتۆپ لە شوێنی خۆی جێگیرە؛ بە هەمان شێوە مافی هەیە لە فۆرماتێکدا وەربگرێت کە بتوانێت لە کۆمپانیایەکەوە بیبات بۆ کۆمپانیایەکی تر.
The data subject's rightsمافەکانی خاوەنی دراوە
All eight rightsهەر هەشت مافەکە
The GDPR gives four more, so the full set is eight. The animation shows them one by one.
چوار مافی تریش دەدات، بۆیە کۆی گشتییان هەشتە. ئەنیمەیشنەکە یەک بە یەک پیشانیان دەدات.
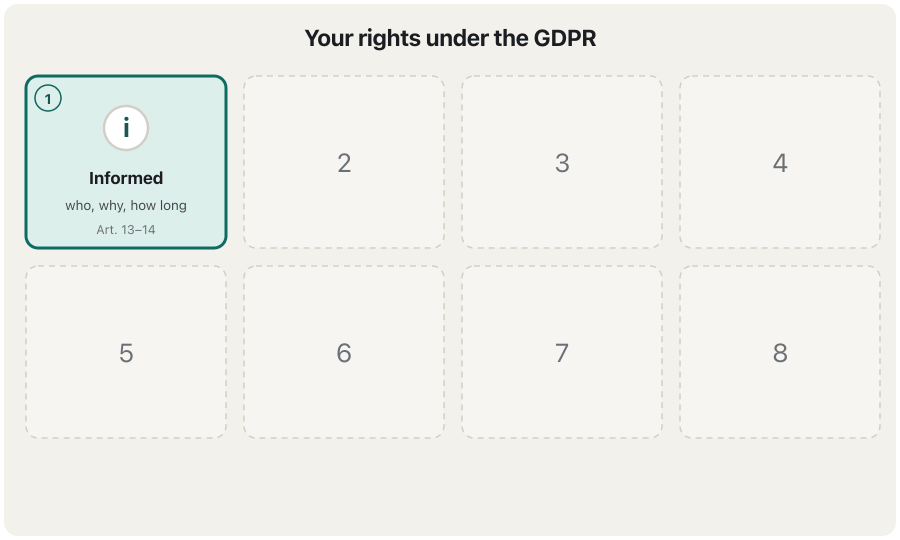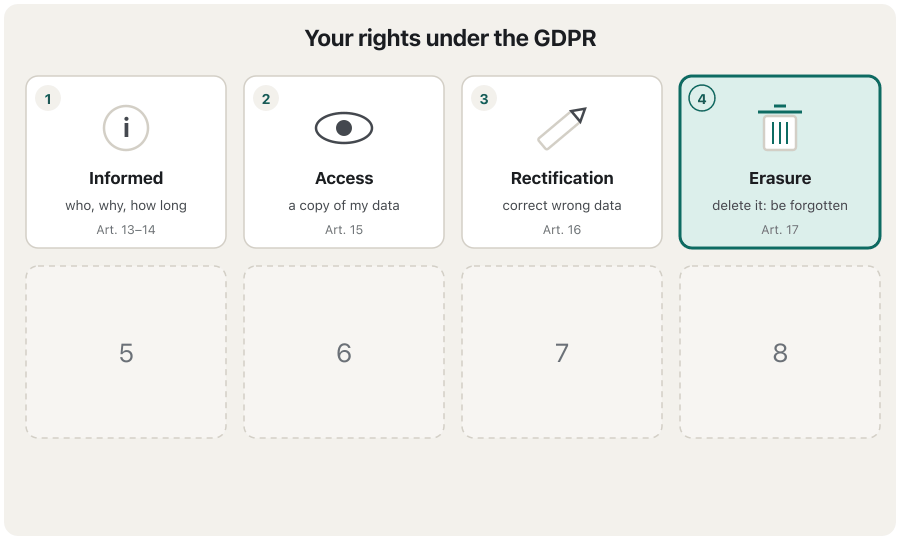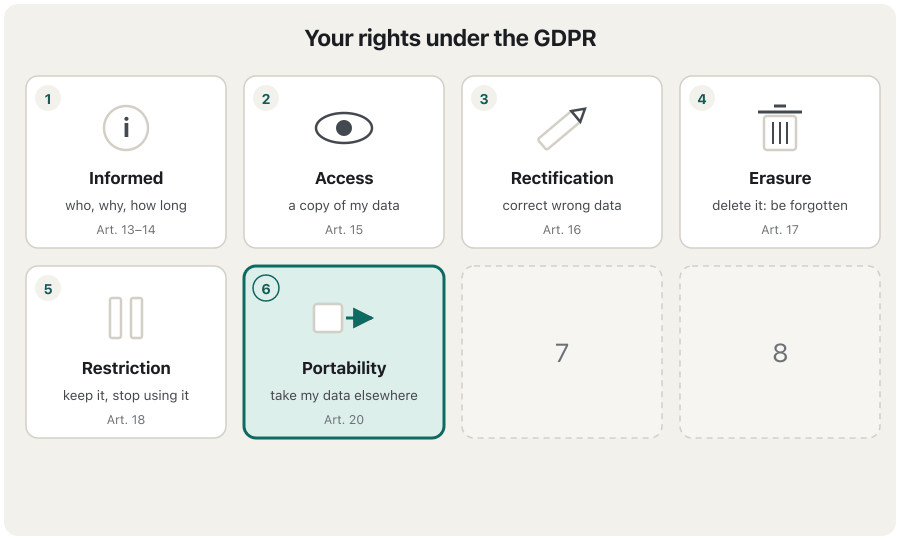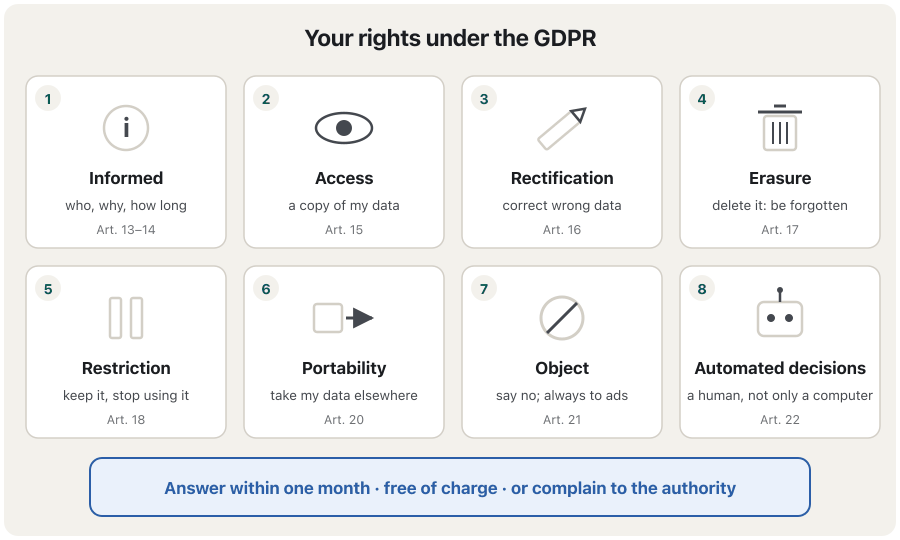
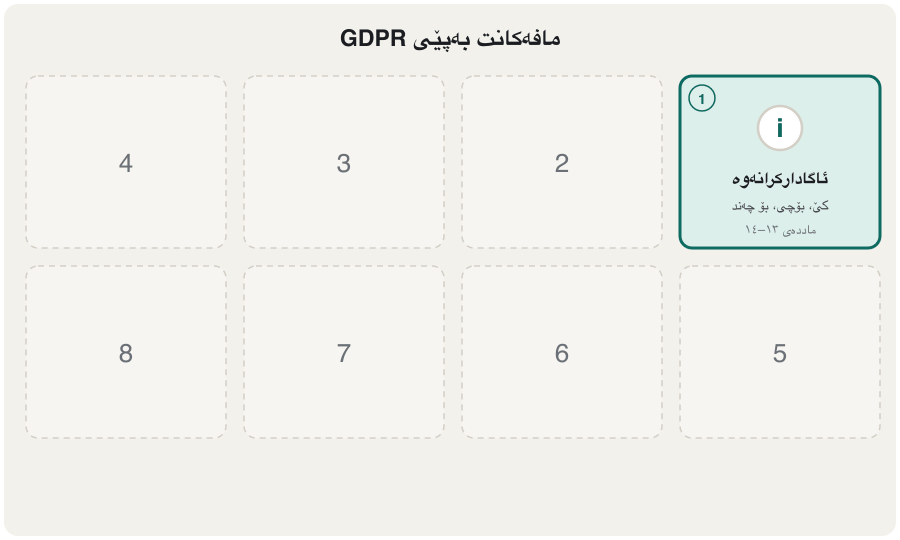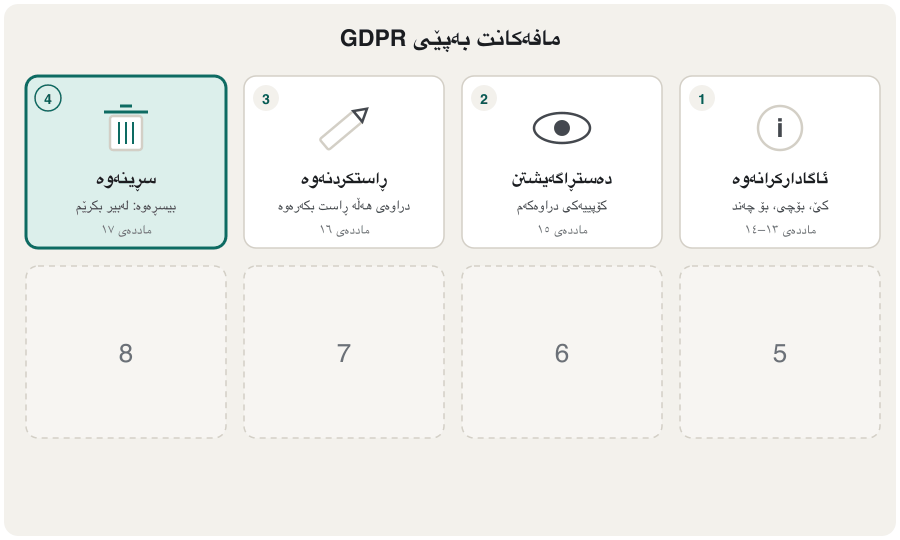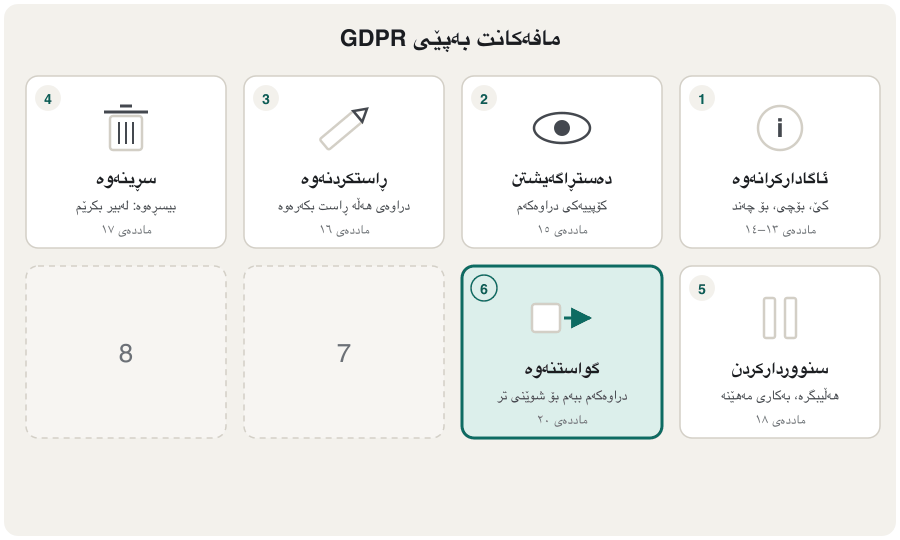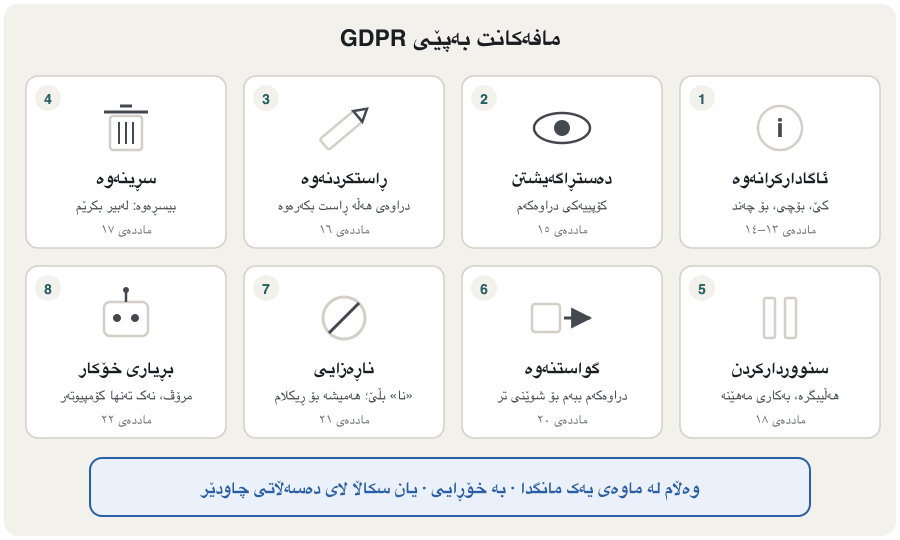
| Rightماف | Articleماددە | In one lineبە یەک دێڕ |
|---|---|---|
| Right to be informed | 13–14 | Clear words on who collects your data, why, for how long and with whom it is sharedوشەی ڕوون دەربارەی ئەوەی کێ کۆ دەکاتەوە، بۆچی، بۆ چەند و لەگەڵ کێ بەشی دەکات |
| Right of access | 15 | A copy of your data and how it is usedکۆپییەکی و چۆنیەتیی بەکارهێنانی |
| Right to rectification | 16 | Correct wrong or incomplete dataڕاستکردنەوەی هەڵە یان ناتەواو |
| Right to erasure | 17 | Delete data that is no longer needed, used unlawfully or after consent is withdrawnسڕینەوەی ئەو ئیتر پێویست نییە، بە نایاسایی بەکار هاتووە یان دوای کشاندنەوەی |
| Right to restriction | 18 | Keep the data but pause its use, for example while a mistake is checked هەڵبگرە بەڵام بەکارهێنانی ڕابگرە، بۆ نموونە تا هەڵەیەک دەپشکنرێت |
| Data portability | 20 | Get the data you gave in a common, machine-readable format, or have it sent to another company خۆت لە فۆرماتێکی باو و خوێندراو بە ئامێر وەربگرە، یان بینێرە بۆ کۆمپانیایەکی تر |
| Right to object | 21 | Say no to some uses; direct marketing must always stop«نا» بڵێ بە هەندێک بەکارهێنان؛ ڕیکلامی ڕاستەوخۆ هەمیشە دەبێت بوەستێت |
| Automated decisions | 22 | Not to be judged only by a computer when the decision has legal or similar serious effectsکاتێک بڕیارێک کاریگەریی یاسایی یان هاوشێوەی گرنگی هەیە، تەنها حوکمت لەسەر نەدات |
The data subject's rightsمافەکانی خاوەنی دراوە
Using your rights in practiceچۆن مافەکانت بەکار دەهێنیت
- Time: the organisation must answer without undue delay and within one month. For complex or many requests it may extend this by two more months, but it must tell you why within the first month.
- Cost: answering is free. Only clearly unfounded or excessive requests (for example the same request again and again) may be charged for or refused.
- Identity: the organisation may ask you to prove who you are, so that nobody else gets your data.
- Refusal: if it says no, it must give the reasons and tell you that you can complain to the data-protection authority or go to court.
- کات: ڕێکخراوەکە دەبێت بەبێ دواکەوتنی ناپێویست و لە ماوەی یەک مانگدا وەڵام بداتەوە. بۆ داواکاریی ئاڵۆز یان زۆر دەتوانێت دوو مانگی تر درێژی بکاتەوە، بەڵام دەبێت لە مانگی یەکەمدا هۆکەیت پێ بڵێت.
- تێچوو: وەڵامدانەوە بە خۆڕاییە. تەنها داواکاریی بێبنەما یان زیادەڕۆیی ئاشکرا (بۆ نموونە هەمان داواکاری بە دووبارە و سێبارە) دەکرێت پارەی لێ وەربگیرێت یان ڕەت بکرێتەوە.
- ناسنامە: ڕێکخراوەکە دەتوانێت داوات لێ بکات بیسەلمێنیت کێیت، بۆ ئەوەی کەسێکی تر وەرنەگرێت.
- ڕەتکردنەوە: ئەگەر «نا» بڵێت، دەبێت هۆکارەکان بڵێت و پێت بڵێت دەتوانیت سکاڵا لای تۆمار بکەیت یان بچیتە دادگا.
Breach notification: the 72-hour ruleئاگادارکردنەوەی دزەکردنی دراوە: یاسای ٧٢ کاتژمێر
The legal duty to tell the authorities, and often the people affected, after a . Under the the must be told within 72 hours of finding a serious breach.
ئەو ئەرکە یاساییەیە کە دوای دەسەڵاتداران و زۆرجار ئەو کەسانەی زیانیان پێگەیشتووە ئاگادار بکرێنەوە. بەپێی دەبێت لە ماوەی ٧٢ کاتژمێر دوای دۆزینەوەی دزەکردنێکی جددیدا ئاگادار بکرێتەوە.
The notes' third key provision: companies must notify the authorities within 72 hours of discovering a breach, so that users and the public are protected. Here 'the authorities' does not mean the government in general. It means the organisation's data-protection authority (in the GDPR's words, the supervisory authority): the public body that enforces the law in that country.
سێیەم خاڵی سەرەکیی تێبینییەکان: کۆمپانیاکان دەبێت لە ماوەی ٧٢ کاتژمێر دوای دۆزینەوەی دەسەڵاتداران ئاگادار بکەنەوە، بۆ ئەوەی و خەڵک پارێزراو بن. لێرەدا «دەسەڵاتداران» واتە حکوومەت بە گشتی نییە. واتە ڕێکخراوەکە (بە وشەی ، دەسەڵاتی سەرپەرشتیار): ئەو دەزگا گشتییەی یاساکە لەو وڵاتەدا جێبەجێ دەکات.
Recording the breach and telling the peopleتۆمارکردن و ئاگادارکردنەوەی ئەو کەسانەی زیانیان پێ گەیشتووە
Three more duties complete the rule. Every breach must be recorded inside the organisation, even when it is not reported. A processor that finds a breach must tell its controller without undue delay. And if the risk to people is high, Article 34 adds a second notice: tell the people affected directly, in clear and plain language, unless, for example, the data was strongly encrypted.
سێ ئەرکی تر یاساکە تەواو دەکەن. هەموو دەبێت لە ناو ڕێکخراوەکەدا تۆمار بکرێت، تەنانەت ئەگەر ڕاپۆرتیش نەکرێت. کە دەدۆزێتەوە دەبێت بەبێ دواکەوتنی ناپێویست ئاگادار بکاتەوە. هەروەها ئەگەر بۆ خەڵک بەرز بێت، ماددەی ٣٤ ئاگادارکردنەوەیەکی دووەم زیاد دەکات: ئەو کەسانەی زیانیان پێ گەیشتووە ڕاستەوخۆ ئاگادار بکەرەوە، بە زمانێکی ڕوون و سادە، مەگەر بۆ نموونە بە بەهێزی شفرە کرابێت.
The lecture adds the ethical side. After a breach, organisations have an ethical responsibility to protect user data and to notify users promptly (without delay) when there is serious danger. Failing to disclose a breach destroys trust, as you saw with Aram Mobile in Cyber Ethics and Ethical Hacking.
وانەکە لایەنی ئەخلاقی زیاد دەکات. دوای ، ڕێکخراوەکان بەرپرسیارێتیی ئەخلاقییان هەیە بپارێزن و کاتێک مەترسیی گەورە هەیە بەبێ دواکەوتن ئاگادار بکەنەوە. ئاشکرانەکردنی متمانە لەناو دەبات، وەک لە نموونەی ئارام مۆبایل لە ئەخلاقی سایبەری و هاککردنی ئەخلاقی بینیت.
Accountability: DPIAs and DPOsلێپرسینەوە: DPIA و DPO
The notes' fourth key provision is accountability (responsibility, being answerable): organisations must not only obey the GDPR, they must be able to prove that they obey it. The notes name two tools:
چوارەم خاڵی سەرەکیی تێبینییەکان (بەرپرسیارێتی، وەڵامدەرەوە بوون): ڕێکخراوەکان نەک تەنها دەبێت پابەندی بن، بەڵکو دەبێت بتوانن بیسەلمێنن کە پابەندن. تێبینییەکان دوو ئامراز ناو دەهێنن:
- Data Protection Impact Assessment (DPIA): a written check done before a new use of personal data that is likely to put people at high risk. Examples: judging people automatically (profiling) with serious effects, handling health data on a large scale, or watching a public place on a large scale with cameras. It describes the use and its purpose, asks whether it is really necessary, weighs the risks to people and lists the measures that reduce them.
- Data Protection Officer (DPO): a person the organisation appoints to advise staff, check compliance and be the contact for the authority and for the public. A DPO is required for public bodies, and for organisations whose core work is large-scale regular monitoring of people, or large-scale use of sensitive data such as health data.
- (DPIA): پشکنینێکی نووسراو کە پێش بەکارهێنانێکی نوێی دەکرێت کە ئەگەری هەیە خەڵک بخاتە مەترسیی بەرزەوە. نموونەکان: هەڵسەنگاندنی خۆکاری خەڵک (پرۆفایلسازی) بە کاریگەریی گرنگەوە، مامەڵەکردن لەگەڵ تەندروستی بە قەبارەی گەورە، یان چاودێریکردنی شوێنێکی گشتی بە کامێرا بە قەبارەی گەورە. بەکارهێنانەکە و مەبەستەکەی وەسف دەکات، دەپرسێت ئایا بەڕاستی پێویستە، سەر خەڵک دەکێشێت و ئەو ڕێکارانە دەنووسێت کە کەمیان دەکەنەوە.
- (DPO): کەسێکە ڕێکخراوەکە دیاریی دەکات بۆ ئامۆژگاریکردنی کارمەندان، پشکنینی و بوون بە پەیوەندیکار بۆ دەسەڵات و بۆ خەڵک. DPO بۆ دەزگا گشتییەکان پێویستە، هەروەها بۆ ئەو ڕێکخراوانەی کاری سەرەکییان چاودێریی بەردەوامی خەڵکە بە قەبارەی گەورە، یان بەکارهێنانی هەستیار وەک تەندروستییە بە قەبارەی گەورە.
A check that an organisation must do before starting a project that is likely to put people's at high risk, such as large-scale tracking. It describes the risks and how they will be reduced.
پشکنینێکە کە دامەزراوەیەک دەبێت پێش دەستپێکردنی پرۆژەیەک ئەنجامی بدات کە لەوانەیە خەڵک بخاتە مەترسیی زۆرەوە، وەک چاودێریکردنی بەرفراوان. مەترسییەکان و چۆنیەتیی کەمکردنەوەیان ڕوون دەکاتەوە.
Fines: 'whichever is higher'سزای دارایی: «کامیان زیاتر بێت»
The notes' fifth key provision: non-compliance can result in fines of up to €20 million or 4% of annual global turnover, whichever is higher. Annual global turnover is the total money a company earns in one year from all its business worldwide (for a group, the whole group, in the previous financial year). Whichever is higher means the maximum fine is the bigger of the two numbers.
پێنجەم خاڵی سەرەکیی تێبینییەکان: پابەندنەبوون دەتوانێت ببێتە هۆی سزای دارایی تا ٢٠ ملیۆن یۆرۆ یان ٤٪ی داهاتی ساڵانەی جیهانی، کامیان زیاتر بێت. داهاتی ساڵانەی جیهانی کۆی ئەو پارەیەیە کە کۆمپانیایەک لە یەک ساڵدا لە هەموو کارەکانی لە سەرانسەری جیهاندا بەدەستی دەهێنێت (بۆ گروپێک، هەموو گروپەکە، لە ساڵی دارایی پێشوودا). کامیان زیاتر بێت واتە زۆرترین سزا گەورەترینی ئەو دوو ژمارەیەیە.
The upper tier (Article 83(5)), the one in the notes: is the maximum fine and the company's annual worldwide turnover.
ئاستی بەرز (ماددەی ٨٣(٥))، ئەوەی لە تێبینییەکاندایە: زۆرترین سزایە و داهاتی ساڵانەی جیهانیی کۆمپانیاکەیە.
- Small companyکۆمپانیای بچووک
Turnover €2,000,000. 4% of it is €80,000, which is smaller than €20,000,000, so the maximum is €20 million.
داهات ٢،٠٠٠،٠٠٠ یۆرۆ. ٤٪ی دەکاتە ٨٠،٠٠٠ یۆرۆ، کە لە ٢٠،٠٠٠،٠٠٠ یۆرۆ کەمترە، بۆیە زۆرترین سزا ٢٠ ملیۆن یۆرۆیە.
- Very large companyکۆمپانیای زۆر گەورە
Turnover €80,000,000,000 (80 billion). 4% of it is €3,200,000,000, which is far more than €20 million, so the maximum is €3.2 billion.
داهات ٨٠،٠٠٠،٠٠٠،٠٠٠ یۆرۆ (٨٠ ملیار). ٤٪ی دەکاتە ٣،٢٠٠،٠٠٠،٠٠٠ یۆرۆ، کە زۆر لە ٢٠ ملیۆن یۆرۆ زیاترە، بۆیە زۆرترین سزا ٣.٢ ملیار یۆرۆیە.
The two examples in millions of euros: €20 million for the small company, €3,200 million (€3.2 billion) for the very large one. The fixed amount protects against small companies paying almost nothing; the percentage makes the biggest companies feel the fine.
دوو نموونەکە بە ملیۆن یۆرۆ: ٢٠ ملیۆن یۆرۆ بۆ کۆمپانیا بچووکەکە و ٣،٢٠٠ ملیۆن یۆرۆ (٣.٢ ملیار) بۆ کۆمپانیا زۆر گەورەکە. بڕە جێگیرەکە ڕێ لەوە دەگرێت کۆمپانیای بچووک نزیکەی هیچ نەدەن؛ ڕێژە سەدییەکە وا دەکات گەورەترین کۆمپانیاکان سزاکە هەست پێ بکەن.
Two tiers, and other powersدوو ئاست و دەسەڵاتەکانی تر
Fines are not the only tool. The authority can also give a warning (if a plan is likely to break the law), a reprimand, an order to fix something, or a temporary or permanent ban on processing, with or instead of a fine.
سزای دارایی تاکە ئامراز نییە. دەسەڵاتەکە دەتوانێت ئاگادارکردنەوە بدات (ئەگەر پلانێک ئەگەری هەبێت یاسا بشکێنێت)، سەرزەنشت، فەرمانی چاککردنی شتێک، یان قەدەغەکردنی کاتی یان هەمیشەیی بەکارهێنانی ، لەگەڵ سزای دارایی یان لە جیاتی ئەو.
Big cases: Amazon and Metaنموونە گەورەکان: ئەمازۆن و مێتا
The notes' example: Amazon was fined €746 million in 2021 for GDPR violations related to targeted advertising without proper consent. Luxembourg's data-protection authority (CNPD) decided in July 2021, made public on 30 July, that Amazon had used customers' data to choose the ads they saw without a valid legal basis.
نموونەی تێبینییەکان: ئەمازۆن لە ٢٠٢١دا ٧٤٦ ملیۆن یۆرۆ سزای دارایی درا بەهۆی سەرپێچیی پەیوەست بە ڕیکلامی ئامانجدار بەبێ دروست. لوکسەمبۆرگ (CNPD) لە تەممووزی ٢٠٢١دا بڕیاری دا، کە لە ٣٠ی تەممووزدا ئاشکرا کرا، کە ئەمازۆن کڕیارانی بۆ هەڵبژاردنی ئەو ڕیکلامانەی دەیانبینین بەکار هێناوە بێ ئەوەی دروستی هەبێت.
The largest fines so farگەورەترین سزاکان تا ئێستا
The largest GDPR fine so far (October 2026) is still €1.2 billion against Meta (Facebook) in May 2023, imposed by Ireland's Data Protection Commission after a binding decision of the European Data Protection Board. It was for transferring European users' personal data to the United States without enough protection, systematically and for years.
گەورەترین سزای تا ئێستا (تشرینی یەکەمی ٢٠٢٦) ١.٢ ملیار یۆرۆیە دژی مێتا (فەیسبووک) لە ئایاری ٢٠٢٣دا، کە کۆمیسیۆنی ئیرلەندا دوای بڕیارێکی پابەندکەری دەستەی ئەوروپیی دای. بەهۆی ناردنی بەکارهێنەرانی ئەوروپی بۆ ئەمریکا بەبێ پاراستنی پێویست بوو، بە شێوەیەکی ڕێکخراو و بۆ چەند ساڵێک.
A newer case shows the right about automated decisions at work. In August 2026 the Dutch authority fined Uber about €825 million because drivers' accounts were deactivated by fully automated decisions (after fraud suspicions or low ratings), and drivers were not told enough about it (Articles 22 and 13). Uber has appealed.
نموونەیەکی نوێتر مافی لە کاردا پیشان دەدات. لە ئابی ٢٠٢٦دا دەسەڵاتی هۆڵەندی نزیکەی ٨٢٥ ملیۆن یۆرۆ سزای Uberـی دا، چونکە هەژماری شۆفێرەکان بە بڕیاری تەواو خۆکار ناچالاک دەکران (دوای گومانی ساختەکاری یان هەڵسەنگاندنی نزم) و بە پێویستی ئاگادار نەدەکرانەوە (ماددەکانی ٢٢ و ١٣). Uber تانەی لێداوە.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Correct ideaبیرۆکەی دروست |
|---|---|---|
| 'The GDPR protects EU citizens.'« هاووڵاتیانی ئەوروپا دەپارێزێت.» | It protects people who are in the EU/EEA.ئەو کەسانە دەپارێزێت کە لە یەکێتیی ئەوروپا/ناوچەی ئابووریی ئەوروپادان. | Ask where the person is, not their passport.بپرسە کەسەکە لە کوێیە، نەک پاسپۆرتەکەی. |
| 'Every use of data needs consent.'«هەموو بەکارهێنانێکی پێویستە.» | Consent is one of six lawful bases. یەکێکە لە شەش . | Find the right basis: contract, legal duty, legitimate interest…بنەمای دروست بدۆزەرەوە: گرێبەست، ئەرکی یاسایی، بەرژەوەندیی ڕەوا… |
| 'Tell the government within 72 hours.'«لە ماوەی ٧٢ کاتژمێردا حکوومەت ئاگادار بکەرەوە.» | The duty is to the data-protection authority, and 72 hours is the outer limit.ئەرکەکە بەرامبەر و ٧٢ کاتژمێر دواین سنوورە. | Notify the DPA without undue delay; tell people too if the risk is high.بەبێ دواکەوتنی ناپێویست ئاگادار بکەرەوە؛ ئەگەر بەرز بوو خەڵکیش ئاگادار بکەرەوە. |
| 'The fine is €20 million or 4%, whichever is lower.'«سزاکە ٢٠ ملیۆن یۆرۆ یان ٤٪ـە، کامیان کەمتر بێت.» | It is whichever is higher, and it is a maximum.کامیان زیاتر بێت، هەروەها زۆرترینە. | Take the higher of the two numbers, and remember the lower tier (€10 M / 2%).ژمارە گەورەترەکەی دووانەکە وەربگرە و ئاستە نزمەکە لەبیر بێت (١٠ ملیۆن / ٢٪). |
| 'Erasure means everything must go.'«سڕینەوە واتە هەموو شتێک دەبێت بڕوات.» | Data needed by law, for legal claims or public health may stay.ئەو یاسا، داوای یاسایی یان تەندروستیی گشتی پێویستی پێیەتی دەتوانێت بمێنێتەوە. | Erase what is no longer needed and explain what stays.ئەوەی ئیتر پێویست نییە بیسڕەوە و ڕوونی بکەرەوە چی دەمێنێتەوە. |
Exercisesڕاهێنانەکان
For each company, compute the maximum fine. (a) Upper tier, turnover €150 million. (b) Upper tier, turnover €1.5 billion. (c) Lower tier, turnover €900 million.
بۆ هەر کۆمپانیایەک زۆرترین سزا بژمێرە. (أ) ئاستی بەرز، داهات ١٥٠ ملیۆن یۆرۆ. (ب) ئاستی بەرز، داهات ١.٥ ملیار یۆرۆ. (ج) ئاستی نزم، داهات ٩٠٠ ملیۆن یۆرۆ.
Show answerوەڵامەکە پیشان بدە
All amounts in millions of euros: (a) €20 million, (b) €60 million, (c) €18 million.
هەموو بڕەکان بە ملیۆن یۆرۆن: (أ) ٢٠ ملیۆن، (ب) ٦٠ ملیۆن، (ج) ١٨ ملیۆن یۆرۆ.
Name the right in each case: (a) Karwan wants a copy of everything a bank stores about him. (b) Lana's surname is misspelt in her university record. (c) Soran is tired of advertising e-mails from a shop. (d) An online loan is refused by an algorithm in seconds, and Dilan wants a person to look at it.
لە هەر حاڵەتێکدا مافەکە ناو ببە: (أ) کاروان کۆپییەکی هەموو ئەو شتانەی دەوێت کە بانکێک دەربارەی ئەو هەڵیگرتووە. (ب) نازناوی لانا لە تۆماری زانکۆکەیدا بە هەڵە نووسراوە. (ج) سۆران لە ڕیکلامی دوکانێک بێزار بووە. (د) قەرزێکی سەرهێڵ لە چەند چرکەیەکدا لەلایەن ڕەت دەکرێتەوە و دیلان دەیەوێت مرۆڤێک سەیری بکات.
Show answerوەڵامەکە پیشان بدە
- (a) Right of access (Article 15).
- (b) Right to rectification (16).
- (c) Right to object (21): for direct marketing the shop must always stop. If he had consented, he can also withdraw consent.
- (d) The right about automated decisions (22): to get human review and to contest the decision.
- (أ) (ماددەی ١٥).
- (ب) (١٦).
- (ج) (٢١): بۆ ڕیکلامی ڕاستەوخۆ دوکانەکە هەمیشە دەبێت بوەستێت. ئەگەر دابێت، دەتوانێت بیکشێنێتەوە.
- (د) مافی پەیوەست بە (٢٢): پێداچوونەوەی مرۆیی وەربگرێت و ناڕەزایی لەسەر بڕیارەکە دەرببڕێت.
On Friday at 18:00 the IT team of a German online shop confirms that attackers copied 20,000 customers' names and plain-text passwords. Write the steps of the next days, with deadlines.
ڕۆژی هەینی کاتژمێر ٦ی ئێوارە تیمی ITـی فرۆشگایەکی سەرهێڵی ئەڵمانی پشتڕاست دەکاتەوە کە ناو و بێ هاشی ٢٠،٠٠٠ کڕیاریان کۆپی کردووە. هەنگاوەکانی ڕۆژانی داهاتوو لەگەڵ کاتی کۆتاییان بنووسە.
Show answerوەڵامەکە پیشان بدە
Contain the attack, reset all passwords, keep evidence, and record the breach.
سنووردار بکە، هەموو نوێ بکەرەوە، بەڵگە بپارێزە و تۆمار بکە.
Notify the data-protection authority without undue delay, at the latest by Monday 18:00 (72 hours).
بەبێ دواکەوتنی ناپێویست ئاگادار بکەرەوە، لانی دواتر تا دووشەممە کاتژمێر ٦ی ئێوارە (٧٢ کاتژمێر).
Plain-text passwords are a high risk, so tell the 20,000 customers directly and soon, in plain language: what happened, what you did, and that they must change the same password on other sites.
بێ هاش بەرزە، بۆیە زوو و ڕاستەوخۆ ٢٠،٠٠٠ کڕیارەکە بە زمانێکی سادە ئاگادار بکەرەوە: چی ڕوویدا، چیت کرد و دەبێت هەمان لە تریشدا بگۆڕن.
Fix the cause: store passwords only as salted, slow hashes.
هۆکارەکە چاک بکە: تەنها وەک هاشی خاو و خوێدار هەڵبگرە.
Summary and reviewکورتە و پێداچوونەوە
- The GDPR (EU, since 25 May 2018) protects the personal data of people in the EU/EEA and applies to any organisation, anywhere, that offers them goods or services or monitors them.
- Every use of personal data needs one of six lawful bases; consent must be free, specific, informed, clear, provable and easy to withdraw.
- Eight rights: informed, access, rectification, erasure, restriction, portability, object, and protection from purely automated decisions; answer within one month, free.
- Breach: notify the data-protection authority without undue delay and where feasible within 72 hours; tell the people affected if the risk is high; record every breach.
- Accountability: be able to prove compliance (DPIA before high-risk processing, a DPO when required).
- Fines: up to €20 M or 4% of worldwide turnover (upper tier) or €10 M or 2% (lower tier), whichever is higher, set case by case; Amazon's €746 M (2021) was annulled on appeal in 2026; Meta's €1.2 billion (2023) is the largest so far; Uber was fined about €825 M in 2026 for automated decisions (under appeal).
- (یەکێتیی ئەوروپا، لە ٢٥ی ئایاری ٢٠١٨ەوە) خەڵکی ناو یەکێتیی ئەوروپا/ناوچەی ئابووریی ئەوروپا دەپارێزێت و هەر ڕێکخراوێک لە هەر شوێنێک دەگرێتەوە کە کاڵا یان خزمەتگوزارییان پێشکەش دەکات یان چاودێرییان دەکات.
- هەموو بەکارهێنانێکی پێویستی بە یەکێک لە شەش هەیە؛ دەبێت ئازاد، دیاریکراو، ئاگادارانە، ڕوون، سەلمێنراو و ئاسان بۆ کشاندنەوە بێت.
- هەشت ماف: ئاگادارکرانەوە، دەستڕاگەیشتن، ڕاستکردنەوە، سڕینەوە، سنووردارکردن، گواستنەوە، ناڕەزایی و پاراستن لە بڕیاری تەواو خۆکار؛ وەڵام لە ماوەی یەک مانگدا، بە خۆڕایی.
- : بەبێ دواکەوتنی ناپێویست و ئەگەر بکرێت لە ماوەی ٧٢ کاتژمێردا ئاگادار بکەرەوە؛ ئەگەر بەرز بوو ئەو کەسانەی زیانیان پێ گەیشتووە ئاگادار بکەرەوە؛ هەموو تۆمار بکە.
- : بتوانیت بسەلمێنیت (DPIA پێش بەکارهێنانی مەترسیداری بەرز، DPO کاتێک پێویستە).
- سزای دارایی: تا ٢٠ ملیۆن یۆرۆ یان ٤٪ی داهاتی جیهانی (ئاستی بەرز) یان ١٠ ملیۆن یان ٢٪ (ئاستی نزم)، کامیان زیاتر بێت، حاڵەت بە حاڵەت دیاری دەکرێت؛ ٧٤٦ ملیۆنەکەی ئەمازۆن (٢٠٢١) لە ٢٠٢٦دا لە تانەدا هەڵوەشێنرایەوە؛ ١.٢ ملیارەکەی مێتا (٢٠٢٣) گەورەترینە تا ئێستا؛ Uber لە ٢٠٢٦دا نزیکەی ٨٢٥ ملیۆن یۆرۆ بەهۆی سزا درا (تانەی لێدراوە).
Does the GDPR apply to a company in Erbil? Explain.ئایا GDPR کۆمپانیایەک لە هەولێر دەگرێتەوە؟ ڕوونی بکەرەوە.
Only if it offers goods or services to people in the EU, monitors them, or has an EU establishment.
تەنها ئەگەر کاڵا یان خزمەتگوزاری پێشکەش بە خەڵکی ناو یەکێتیی ئەوروپا بکات، چاودێرییان بکات یان لقێکی لە یەکێتیی ئەوروپا هەبێت.
Name the six lawful bases.شەش بنەمای یاسایی ناو ببە.
Consent, contract, legal obligation, vital interests, public task, legitimate interests.
، گرێبەست، ئەرکی یاسایی، پاراستنی ژیان، ئەرکی گشتی، بەرژەوەندیی ڕەوا.
Whom must a company tell after a breach, and when?کۆمپانیایەک دوای دزەکردنێکی دراوە دەبێت کێ ئاگادار بکاتەوە و کەی؟
The data-protection authority without undue delay (where feasible within 72 hours) if there is a risk; the people affected too if the risk is high.
بەبێ دواکەوتنی ناپێویست (ئەگەر بکرێت لە ماوەی ٧٢ کاتژمێردا) ئەگەر هەبێت؛ ئەگەر بەرز بوو ئەو کەسانەش کە زیانیان پێ گەیشتووە.
What is the maximum upper-tier fine for a company with €1 billion turnover?زۆرترین سزای ئاستی بەرز بۆ کۆمپانیایەک بە داهاتی ١ ملیار یۆرۆ چەندە؟
: €40 million.
: ٤٠ ملیۆن یۆرۆ.
Videoڤیدیۆ
Watch a videoسەیری ڤیدیۆیەک بکە
A video that viewers liked a lot and praised in their comments, chosen for this lesson.ڤیدیۆیەک کە بینەران زۆریان پێ خۆش بووە و لە کۆمێنتەکانیاندا ستایشیان کردووە، بۆ ئەم وانەیە هەڵبژێردراوە.
What the EU GDPR does: rules for any organisation handling EU people's data, consent, protection, breach reports in 72 hours, access, deletion and fines.
ئەوروپا چی دەکات: ڕێسا بۆ هەر دامەزراوەیەک دادەنێت کە ئەوروپییەکان بەکاردەهێنێت؛ ڕەزامەندی، ، ئاگادارکردنەوە لە لە 72 کاتژمێردا، مافی بینین و سڕینەوە و سزا.
Plays 0:06-3:44: a short overview of the GDPR. Skips the channel plug at the start and stops before the Brilliant sponsor.
لە 0:06 تا 3:44 پەخش دەبێت: ناساندنێکی کورتی . ڕیکلامە کورتەکەی کەناڵەکە لە سەرەتادا تێدەپەڕێنێت و پێش ڕیکلامی سپۆنسەرەکە (Brilliant) ڕادەوەستێت.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Health Data and National Rules: HIPAA and China's Cybersecurity Lawدراوەی تەندروستی و یاسا نیشتیمانییەکان: HIPAA و یاسای ئاسایشی سایبەری چین
Related lecturesوانە پەیوەندیدارەکان
- Health Data and National Rules: HIPAA and China's Cybersecurity Lawدراوەی تەندروستی و یاسا نیشتیمانییەکان: HIPAA و یاسای ئاسایشی سایبەری چین
- AI in Cybersecurity: Bias, Privacy, Surveillance and Deepfakesژیریی دەستکرد لە ئاسایشی سایبەردا: لاسەنگی، تایبەتێتی، چاودێری و دیپفەیکەکان
- Cyber Ethics and Ethical Hackingئەخلاقی سایبەری و هاککردنی ئەخلاقی
- Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
- Cloud Databasesبنکەدراوە هەورییەکان
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- European Commission: Sanctions (warnings, reprimands, bans and fines under the GDPR)
- European Commission: Dealing with requests from individuals (one month, free of charge)
- GDPR Art. 3: Territorial scope
- GDPR Art. 6: Lawfulness of processing (six lawful bases)
- GDPR Art. 7: Conditions for consent
- GDPR Art. 12: Transparent information and modalities (deadlines)
- GDPR Art. 17: Right to erasure
- GDPR Art. 20: Right to data portability
- GDPR Art. 33: Notification of a personal data breach to the supervisory authority
- GDPR Art. 34: Communication of a personal data breach to the data subject
- GDPR Art. 35: Data protection impact assessment
- GDPR Art. 37: Designation of the data protection officer
- GDPR Art. 83: General conditions for imposing administrative fines (two tiers, factors)
- GDPR Art. 99: Entry into force and application (25 May 2018)
- Lewis Silkin: Amazon hit with huge €746m fine for targeted advertising breach (30 July 2021)
- Decision Marketing: Court shoots down €746m 'flawed' Amazon GDPR fine (16 March 2026)
- Chronicle.lu: Luxembourg court annuls CNPD ruling in Amazon data protection case (March 2026)
- EDPB: national news (GDPR fines reported by national authorities, checked 23 October 2026)
- CNPD: Administrative Court ruling in the case between Amazon and the CNPD (judgment of 12 March 2026, news of 13 March 2026)
- EDPB national news: Dutch DPA fines Uber EUR 824 990 000 for unlawful automated decision-making and insufficient information on profiling (8 October 2026)
- GDPR Recital 32: Conditions for consent (silence, pre-ticked boxes or inactivity are not consent)
- EDPB press release '1.2 billion euro fine for Facebook as a result of EDPB binding decision' (22 May 2023), as republished by Moldova's National Centre for Personal Data Protection
- Pearl Cohen: Dutch Data Protection Authority fines Uber €825 million for fully automated deactivation of drivers (decision of 21 August 2026)
- PPC Land: Luxembourg court annuls Amazon’s €746m GDPR fine, sends case back to regulator (Tribunal 18 March 2025; Administrative Court 12 March 2026, case 52757C)
- GDPR Art. 9: Processing of special categories of personal data
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.