Chapterبەش 4 · Lectureوانە 4.4
Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
Why attackers target people instead of machines; the levers they pull (trust, fear, urgency, curiosity); the eight classic types from baiting to vishing; modern tricks such as smishing, QR-code phishing, business e-mail compromise, MFA fatigue and deepfakes; the real Twilio and Uber cases with corrected dates; how to spot a phishing message; and how people, processes and technology defend together.
بۆچی لە جیاتی ئامێر مرۆڤ دەکەنە ئامانج؛ ئەو ئامرازانەی دەیانجووڵێنن (متمانە، ترس، پەلە، کونجکۆڵی)؛ هەشت جۆرە کلاسیکییەکە لە تا ؛ فێڵە نوێیەکانی وەک بە ، ، ، و ؛ ڕووداوە ڕاستەقینەکانی Twilio و Uber بە ڕێکەوتی ڕاستکراوەوە؛ چۆن نامەیەکی بناسیتەوە؛ هەروەها چۆن خەڵک، ڕێکار و تەکنەلۆجیا پێکەوە بەرگری دەکەن.
What you will learnچی فێر دەبیت
- Explain what social engineering is and which human feelings it exploits.
- Recognise the eight classic types and the modern tricks (smishing, QR-code phishing, BEC, MFA fatigue, deepfakes) in a scenario.
- Tell the Twilio and Uber cases correctly and explain what they teach about MFA.
- Spot the warning signs of a phishing message and react correctly: don't click, verify, report, delete.
- Propose defences for an organisation: training, phishing-resistant MFA, verification processes and reporting.
- ڕوونی بکەیتەوە چییە و کام هەستە مرۆییانە بەکار دەهێنێت.
- هەشت جۆرە کلاسیکییەکە و فێڵە نوێیەکان ( بە ، ، BEC، ، ) لە نموونەیەکدا بناسیتەوە.
- ڕووداوەکانی Twilio و Uber بە دروستی بگێڕیتەوە و ڕوونی بکەیتەوە چی دەربارەی MFA فێر دەکەن.
- نیشانەکانی ئاگادارکردنەوەی نامەیەکی بدۆزیتەوە و بە دروستی کاردانەوەت هەبێت: کرتە مەکە، پشتڕاستی بکەرەوە، ڕاپۆرت بدە، بیسڕەوە.
- بەرگری بۆ ڕێکخراوێک پێشنیار بکەیت: ڕاهێنان، MFAـی بەرگەگر لە بەرامبەر ، ڕێکارەکانی پشتڕاستکردنەوە و ڕاپۆرتکردن.
Hacking the humanهاککردنی مرۆڤ
Tricking people, instead of computers, into giving away secrets or doing something unsafe, by playing on trust, fear, urgency or curiosity. is the best-known kind.
فریودانی خەڵکە، لە جیاتی کۆمپیوتەر، بۆ ئەوەی نهێنییەکان ئاشکرا بکەن یان کارێکی مەترسیدار بکەن، بە یاریکردن بە متمانە، ترس، پەلەپێکردن یان کونجکۆڵییان. ناسراوترین جۆریەتی.
Most attacks you have met so far go through a technical weakness: an unpatched server, a badly written web form. Social engineering goes through a person instead. The attacker manipulates someone into revealing confidential information — a password, a one-time code, a bank detail — or into doing something that harms security, such as opening a file, approving a login or holding a door open. It uses human psychology, not a technical vulnerability.
زۆربەی ئەو تا ئێستا ناسیوتن لە ڕێگەی لاوازییەکی تەکنیکییەوە دەڕۆن: ، وێبی خراپ نووسراو. لە جیاتی ئەوە بە ناو مرۆڤێکدا دەڕوات. کاریگەری لەسەر کەسێک دادەنێت بۆ ئەوەی نهێنی ئاشکرا بکات — ، ، زانیارییەکی بانکی — یان کارێک بکات کە زیان بە دەگەیەنێت، وەک کردنەوەی فایلێک، ڕەزامەندیدان بە یان کراوە هێشتنەوەی دەرگایەک. دەروونناسیی مرۆڤ بەکار دەهێنێت، نەک تەکنیکی.
So even a well-protected organisation can be broken by one convincing message — which is why every student, not only IT staff, needs to know the tricks.
بۆیە تەنانەت ڕێکخراوێکی باش پارێزراویش دەکرێت بە یەک نامەی قایلکەر بشکێت — لەبەر ئەمەیە هەموو خوێندکارێک، نەک تەنها کارمەندانی IT، پێویستە فێڵەکان بناسێت.
The owner's notes explain phishing with fishing: the fisherman does not chase the fish, he hangs a bait that looks like food and waits. A phishing message is the bait — it looks like a message from your bank or your college — and the hook is the link or the request inside it.
تێبینییەکانی خاوەنی کۆرسەکە بە ڕاوەماسی ڕوون دەکەنەوە: ڕاوچی بەدوای ماسییەکەدا ناکەوێت، بەڵکو دەنکێک هەڵدەواسێت کە لە خواردن دەچێت و چاوەڕێ دەکات. نامەی ئەو دەنکەیە — لە نامەی بانکەکەت یان کۆلێژەکەت دەچێت — و قولاپەکەش ئەو یان داواکارییەیە کە تێیدایە.
Where the analogy stops workingسنووری ئەم نموونەیە
A fish cannot check the bait, but you can: you can stop, look closely and ask the real sender by another route. That pause is the main defence taught in this lesson.
ماسی ناتوانێت دەنکەکە بپشکنێت، بەڵام تۆ دەتوانیت: دەتوانیت بوەستیت، بە وردی سەیر بکەیت و لە ڕێگەیەکی ترەوە لە نێرەرە ڕاستەقینەکە بپرسیت. ئەو وەستانە بەرگریی سەرەکییە کە ئەم وانەیە فێری دەکات.
Hacking the humanهاککردنی مرۆڤ
Identity theft: someone pretends to be youدزینی ناسنامە: کەسێک خۆی دەکات بە تۆ
Many tricks in this lesson aim at one prize: your personal data — your name, ID number, address, card details and passwords. With enough of it, a criminal can commit identity theft: pretending to be you. There are three common kinds:
زۆرێک لە فێڵەکانی ئەم وانەیە یەک ئامانجیان هەیە: تۆ — ناو، ژمارەی ناسنامە، ناونیشان، زانیاریی کارت و . بە بڕێکی بەس لەم زانیارییانە تاوانبارێک دەتوانێت ئەنجام بدات: خۆی دەکات بە تۆ. سێ جۆری باوی هەیە:
| Kindجۆر | What the thief doesدزەکە چی دەکات | A warning signنیشانەیەکی ئاگادارکردنەوە |
|---|---|---|
| Financialدارایی | Takes loans, cards or phone contracts in your name, or empties your accounts.بە ناوی تۆوە قەرز، کارت یان گرێبەستی مۆبایل وەردەگرێت، یان هەژمارە بانکییەکانت بەتاڵ دەکات. | A bill or contract arrives that you never signed.پسوولە یان گرێبەستێکت بۆ دێت کە هەرگیز واژووت نەکردووە. |
| Criminalتاوانکاری | Gives your name and details when the police stop them, so the offence is recorded against you.کاتێک پۆلیس ڕایدەگرێت ناو و زانیارییەکانی تۆ دەدات، بۆیە تاوانەکە بە ناوی تۆوە تۆمار دەکرێت. | You are asked about a fine or a case you know nothing about.پرسیارت لێ دەکرێت دەربارەی سزا یان دۆسیەیەک کە هیچ لەبارەیەوە نازانیت. |
| Medicalپزیشکی | Uses your identity or health insurance to get treatment or medicines.ناسنامە یان بیمەی تەندروستیی تۆ بەکار دەهێنێت بۆ وەرگرتنی چارەسەر یان دەرمان. | Your medical file shows a treatment you never had — wrong data that could affect your own care.دۆسیەی پزیشکیت چارەسەرێک پیشان دەدات کە هەرگیز وەرت نەگرتووە — زانیاریی هەڵە کە دەکرێت کار لە چارەسەری خۆت بکات. |
It is common: in 2025 the FBI's complaint centre (IC3) received 31,675 identity-theft complaints. Share as little personal data as possible, use MFA, check bank statements and messages for things you did not do, and report at once to your bank and the police.
ئەمە باوە: لە ساڵی 2025دا ناوەندی سکاڵاکانی FBI (IC3) 31,675 سکاڵای وەرگرت. کەمترین هاوبەش بکە، MFA بەکار بهێنە، کەشفی حیسابی بانک و نامەکانت بپشکنە بۆ ئەو شتانەی خۆت نەتکردوون و یەکسەر ڕاپۆرت بدە بە بانکەکەت و پۆلیس.
The levers: trust, fear, urgency, curiosityئامرازەکان: متمانە، ترس، پەلە، کونجکۆڵی
The notes name the feelings that social engineers pull on. Almost every trick in this lesson uses one or more of them, often together:
تێبینییەکان ناوی ئەو هەستانە دەهێنن کە ئەندازیارانی کۆمەڵایەتی دەیانجووڵێنن. نزیکەی هەموو فێڵێکی ئەم وانەیە یەکێک یان زیاتر لەمانە بەکار دەهێنێت، زۆرجار پێکەوە:
| Leverئامراز | What the attacker doesهێرشبەر چی دەکات | A typical lineڕستەیەکی ئاسایی |
|---|---|---|
| Trustمتمانە | Pretends to be someone you already trust: your bank, your boss, IT support, a delivery company.خۆی وەک کەسێک دەناسێنێت کە پێشتر متمانەت پێی هەیە: بانکەکەت، بەڕێوەبەرەکەت، یارمەتیی IT، کۆمپانیای گەیاندن. | "Hi, this is Karwan from IT."«سڵاو، من کاروانم لە بەشی IT.» |
| Fearترس | Threatens a loss: a blocked account, a fine, a lost parcel.هەڕەشەی لەدەستدان دەکات: هەژمارێکی داخراو، سزایەکی دارایی، پاکەتێکی ون. | "Your account has been suspended."«هەژمارەکەت ڕاگیراوە.» |
| Urgencyپەلە | Gives no time to think or to check.کات نادات بۆ بیرکردنەوە یان پشکنین. | "Within 2 hours, or it will be closed."«لە ماوەی 2 کاتژمێردا، دەنا دادەخرێت.» |
| Curiosityکونجکۆڵی | Offers something you want to see or have.شتێک پێشکەش دەکات کە دەتەوێت بیبینیت یان هەتبێت. | "Salaries 2026 — confidential.xlsx"«مووچەکانی 2026 — نهێنی.xlsx» |
Two more levers appear in the cases below: authority (the message seems to come from a manager or the police) and helpfulness (the victim wants to help a "colleague" in trouble). To reach their goal — unauthorised access to systems or data — attackers mix these feelings with phishing or impersonation: pretending to be another person, for fun or, here, for fraud.
دوو ئامرازی تر لە ڕووداوەکانی خوارەوەدا دەردەکەون: دەسەڵات (نامەکە وا دیارە لە بەڕێوەبەرێک یان پۆلیسەوە هاتووە) و یارمەتیدان (قوربانی دەیەوێت یارمەتیی «هاوکارێک» بدات کە لە تەنگانەدایە). بۆ گەیشتن بە ئامانجەکەیان — بۆ سیستەم یان — ئەم هەستانە تێکەڵ بە یان دەکەن: خۆ وەک کەسێکی تر نیشاندان، بۆ گاڵتە یان لێرەدا بۆ فێڵ.
Pretending to be another person, device or organisation in order to be trusted, for example phoning staff and claiming to be from the IT department. In computer security it is also called masquerade.
خۆ نیشاندانە وەک کەسێک، ئامێرێک یان دامەزراوەیەکی تر بۆ ئەوەی متمانەت پێ بکرێت، بۆ نموونە پەیوەندیکردن بە کارمەندانەوە و گوتنی ئەوەی کە لە بەشی ITـەوەیت. لە ئاسایشی کۆمپیوتەردا پێی دەڵێن masquerade.
Eight classic typesهەشت جۆری کلاسیکی
The notes list eight classic types of social engineering. They differ in the channel (e-mail, phone, paper, a door, a USB stick) and in how targeted they are, but all of them pull the same levers. The next three screens explain them in groups; the table at the end puts them side by side.
تێبینییەکان هەشت جۆری کلاسیکیی ڕیز دەکەن. جیاوازن لە کەناڵدا (، تەلەفۆن، کاغەز، دەرگایەک، ) و لەوەی چەند ئامانجدارن، بەڵام هەموویان هەمان ئامرازەکان دەجووڵێنن. سێ پەڕەی داهاتوو بە کۆمەڵ ڕوونیان دەکەنەوە؛ خشتەکەی کۆتایی لە تەنیشت یەکتری دایان دەنێت.
Eight classic typesهەشت جۆری کلاسیکی
Phishing and spear phishingفیشینگ و فیشینگی ئامانجدار
Phishing casts a wide net: the same message goes to thousands of people, hoping a few will bite. A typical example is an e-mail to bank customers claiming that their account needs "urgent verification", with a link to a copy of the bank's login page. Attackers also buy search-engine adverts that imitate a well-known brand, so that a search for "Microsoft Office login" leads to a fake page — malicious advertising of this kind is explained in Malvertising: malware in the adverts.
تۆڕێکی فراوان هەڵدەدات: هەمان نامە بۆ هەزاران کەس دەچێت، بە هیوای ئەوەی چەند کەسێک بکەونە داوەکەوە. نموونەیەکی ئاسایی بۆ کڕیارانی بانک کە دەڵێت هەژمارەکەیان پێویستی بە «پشتڕاستکردنەوەی بەپەلە» هەیە، لەگەڵ بۆ کۆپییەکی لاپەڕەی بانکەکە. هەروەها ڕیکلام لە دەکڕن کە لاسایی ناوێکی ناسراو دەکەنەوە، بۆ ئەوەی گەڕان بۆ «Microsoft Office login» بگات بە لاپەڕەیەکی ساختە — ئەم جۆرە ڕیکلامە زیانبەخشە لە ڕیکلامی زیانبەخش: نەرمەواڵەی زیانبەخش لەناو ڕیکلامەکاندا ڕوون کراوەتەوە.
Spear phishing aims at one person or one team. The attacker first studies the target — job title, colleagues, current projects, often from social networks — and writes a message that only makes sense to that person. When the target is a senior manager, it is sometimes called whaling. Because the message is personal, it is far more convincing than mass phishing.
یەک کەس یان یەک تیم دەکاتە ئامانج. سەرەتا ئامانجەکە دەناسێت — ناونیشانی کار، هاوکاران، پڕۆژەکانی ئێستا، زۆرجار لە — و نامەیەک دەنووسێت کە تەنها بۆ ئەو کەسە واتای هەیە. کاتێک ئامانجەکە بەڕێوەبەرێکی باڵا بێت، هەندێک جار پێی دەوترێت whaling (ڕاوی نەهەنگ). چونکە نامەکە کەسییە، زۆر قایلکەرترە لە بە کۆمەڵ.
Learn how phishing messages trick people with urgency and fake authority, the main types (spear phishing, smishing), and how to protect yourself.
فێر دەبیت نامەکانی چۆن بە پەلەپێکردن و دەسەڵاتی ساختە خەڵک فریو دەدەن، جۆرە سەرەکییەکانی چین، وەک spear phishing و smishing و چۆن خۆت بپارێزیت.
Whole video (7:53): phishing and spear phishing.
هەموو ڤیدیۆکە (7:53): و .
Eight classic typesهەشت جۆری کلاسیکی
Vishing, pretexting and quid pro quoڤیشینگ، بیانووسازی و ئاڵوگۆڕی بەرژەوەندی
These three types work by talking: on the phone, in a chat or face to face.
ئەم سێ جۆرە بە قسەکردن کار دەکەن: لە تەلەفۆن، لە چاتێکدا یان ڕووبەڕوو.
- Vishing (voice phishing): a phone call from "your bank", "the tax office" or "tech support". A typical scam: a caller posing as support for a big software company tells a user that his computer is infected and asks for his password to "fix" it. The number shown on your phone can be faked, so it proves nothing.
- Pretexting: the attacker invents a believable situation first. A typical case: someone pretending to be from Human Resources asks employees to "confirm" their personal details because the company is "updating its records".
- Quid pro quo (Latin for "something for something"): the attacker offers a favour in return. A typical case: fake IT support offers a free software upgrade and asks for the administrator password to install it.
- : پەیوەندییەکی تەلەفۆنی لە «بانکەکەت»، «فەرمانگەی باج» یان «یارمەتیی تەکنیکی»یەوە. فێڵێکی ئاسایی: کەسێک کە خۆی وەک یارمەتیی کۆمپانیایەکی گەورەی دەناسێنێت بە دەڵێت تووش بووە و داوای دەکات بۆ ئەوەی «چاکی بکاتەوە». ئەو ژمارەیەی لەسەر مۆبایلەکەت دەردەکەوێت دەکرێت ساختە بێت، بۆیە هیچ شتێک ناسەلمێنێت.
- : سەرەتا دۆخێکی باوەڕپێکراو دادەهێنێت. نموونەیەکی ئاسایی: کەسێک کە خۆی وەک بەشی کارگێڕی دەناسێنێت داوا لە کارمەندان دەکات زانیارییە کەسییەکانیان «پشتڕاست بکەنەوە»، چونکە کۆمپانیاکە «تۆمارەکانی نوێ دەکاتەوە».
- (بە لاتینی واتە «شتێک لە بەرامبەر شتێکدا»): چاکەیەک لە بەرامبەردا پێشکەش دەکات. نموونەیەکی ئاسایی: یارمەتیی ساختەی IT بێبەرانبەری پێشکەش دەکات و بەڕێوەبەر دەخوازێت بۆ دامەزراندنی.
The defence is the same for all three: verify the person through a channel you choose — hang up and call the official number, walk to the office, check with your manager. Real banks and IT departments never ask for your password.
بەرگری بۆ هەر سێکیان یەکە: کەسەکە لە ڕێگەی کەناڵێکەوە پشتڕاست بکەرەوە کە خۆت هەڵیدەبژێریت — تەلەفۆنەکە دابخە و پەیوەندی بە ژمارە فەرمییەکەوە بکە، بڕۆ بۆ نووسینگەکە، لەگەڵ بەڕێوەبەرەکەت پشتڕاستی بکەرەوە. بانک و بەشی ITـی ڕاستەقینە هەرگیز داوای ناکەن.
Eight classic typesهەشت جۆری کلاسیکی
Baiting, dumpster diving and tailgatingتەڵەنانەوە، گەڕان لە زبڵداندا و شوێنکەوتنی دزەکی
The last three types reach into the physical world. Physical security is part of cybersecurity: a locked server room protects data as much as a firewall does.
سێ جۆرەکەی کۆتایی دەگەنە جیهانی فیزیکی. بەشێکە لە : ژووری قفڵکراوی هێندەی دەپارێزێت.
- Baiting tempts the victim with something free or curious. A typical case: USB sticks labelled "Confidential" are left near an office; an employee plugs one in to see what it is, and it installs ransomware. Online, the bait is a "free" film, game or software download.
- Dumpster diving searches what an organisation throws away: printed e-mails, staff lists, notes with passwords, old hard disks (wipe a drive before it leaves you: Before you give a drive away). A typical case: company documents are pulled out of a recycling bin outside the office.
- Tailgating (or piggybacking) means walking into a secure area right behind someone who is allowed in. A typical case: a person carrying boxes follows staff through the badge door of a data centre; once inside, he can steal or plug into anything.
- قوربانی بە شتێکی بێبەرانبەر یان سەرنجڕاکێش هان دەدات. نموونەیەکی ئاسایی: کە لەسەریان نووسراوە «نهێنی» لە نزیک نووسینگەیەک بەجێ دەهێڵرێن؛ کارمەندێک یەکێکیان دەبەستێت بۆ ئەوەی بزانێت چییە و دادەمەزرێت. لە دەنکەکە فیلم، یاری یان «بێبەرانبەر»ـە.
- ئەو شتانە دەپشکنێت کە ڕێکخراوێک فڕێیان دەدات: چاپکراو، لیستی کارمەندان، پارچە کاغەز بە ، دیسکی ڕەقی کۆن (پێش ئەوەی درایڤێک لە دەستت دەربچێت بیسڕەوە: پێش ئەوەی درایڤێک بدەیت بە کەسێکی تر). نموونەیەکی ئاسایی: بەڵگەنامەکانی کۆمپانیا لە سەتڵی بازیافتی دەرەوەی نووسینگەکە دەردەهێنرێن.
- واتە چوونە ناو شوێنێکی پارێزراو ڕاستەوخۆ بە دوای کەسێکدا کە مۆڵەتی هەیە. نموونەیەکی ئاسایی: کەسێک کە چەند سندوقێکی هەڵگرتووە بە دوای کارمەنداندا لە دەرگای کارتیی ناوەندی دەچێتە ژوورەوە؛ کە چووە ناوەوە، دەتوانێت هەر شتێک بدزێت یان ئامێرێک ببەستێتەوە.
Eight classic typesهەشت جۆری کلاسیکی
The eight types side by sideهەشت جۆرەکە لە تەنیشت یەکتر
| Typeجۆر | How it worksچۆن کار دەکات | A typical scenarioنموونەیەکی ئاسایی | Main defenceبەرگریی سەرەکی |
|---|---|---|---|
| Baiting | Tempts the victim with something free or interesting, so they click, download or plug something in.قوربانی بە شتێکی بێبەرانبەر یان سەرنجڕاکێش هان دەدات، بۆ ئەوەی کرتە بکات، دابەزێنێت یان شتێک ببەستێت. | USB sticks labelled "Confidential" are left in a car park; whoever plugs one in installs ransomware. کە لەسەریان نووسراوە «نهێنی» لە شوێنی ڕاگرتنی ئۆتۆمبێل بەجێ دەهێڵرێن؛ هەر کەسێک یەکێکیان ببەستێت دادەمەزرێنێت. | Never plug in unknown devices; block USB storage on work computers.هەرگیز ئامێری نەناسراو مەبەستە؛ لەسەر کار ڕابگرە. |
| Dumpster diving | Searches thrown-away paper and devices for passwords, records and names.لە کاغەز و ئامێرە فڕێدراوەکاندا بەدوای ، تۆمار و ناودا دەگەڕێت. | Company documents are pulled out of a recycling bin outside the office.بەڵگەنامەکانی کۆمپانیا لە سەتڵی بازیافتی دەرەوەی نووسینگەکە دەردەهێنرێن. | Shred paper; wipe old disks before disposal.کاغەز ورد بکە؛ دیسکە کۆنەکان پێش فڕێدان پاک بکەرەوە. |
| Pretexting | Invents a believable story (a pretext) to get information or access.چیرۆکێکی باوەڕپێکراو (بیانوویەک) دادەهێنێت بۆ وەرگرتنی زانیاری یان دەستڕاگەیشتن. | "HR" asks staff to confirm their personal details "to update company records".«بەشی کارگێڕی» داوا لە کارمەندان دەکات زانیارییە کەسییەکانیان پشتڕاست بکەنەوە «بۆ نوێکردنەوەی تۆمارەکانی کۆمپانیا». | Verify the request through a known contact before answering.پێش وەڵامدانەوە لە ڕێگەی پەیوەندییەکی ناسراوەوە داواکارییەکە پشتڕاست بکەرەوە. |
| Phishing | Mass e-mails or messages that trick many people into giving passwords or payment details. یان نامەی بە کۆمەڵ کە خەڵکێکی زۆر فریو دەدەن بۆ ئەوەی یان زانیاریی پارەدان بدەن. | Thousands of bank customers get "urgent account verification" e-mails with a link to a fake login page.هەزاران کڕیاری بانک «پشتڕاستکردنەوەی بەپەلەی هەژمار»یان بۆ دێت بە بۆ لاپەڕەیەکی ساختەی . | Check the real address; use the official app; report.ناونیشانی ڕاستەقینە بپشکنە؛ فەرمی بەکار بهێنە؛ ڕاپۆرت بدە. |
Eight classic typesهەشت جۆری کلاسیکی
The eight types side by side (continued)هەشت جۆرەکە لە تەنیشت یەکتر (درێژە)
| Typeجۆر | How it worksچۆن کار دەکات | A typical scenarioنموونەیەکی ئاسایی | Main defenceبەرگریی سەرەکی |
|---|---|---|---|
| Quid pro quo | Offers a service in exchange for information ("something for something").خزمەتگوزارییەک پێشکەش دەکات لە بەرامبەر زانیاریدا («شتێک بە شتێک»). | A fake "IT support" caller offers a free software upgrade in return for the administrator password.کەسێک بە ناوی ساختەی «یارمەتیی IT» بێبەرانبەری پێشکەش دەکات لە بەرامبەر بەڕێوەبەردا. | Real IT staff never need your password; call the help desk back yourself.کارمەندانی ڕاستەقینەی IT هەرگیز پێویستیان بە نییە؛ خۆت دووبارە پەیوەندی بە مێزی یارمەتییەوە بکە. |
| Spear phishing | A phishing message aimed at one person or team, using personal details to look believable.نامەیەکی کە یەک کەس یان یەک تیم دەکاتە ئامانج و زانیاریی کەسی بەکار دەهێنێت بۆ ئەوەی باوەڕپێکراو دیار بێت. | An engineer receives a "project update" that names her real project and manager, with a malicious attachment.ئەندازیارێک «نوێترین هەواڵی پڕۆژە»ی بۆ دێت کە ناوی پڕۆژە و بەڕێوەبەرە ڕاستەقینەکەی دەهێنێت، لەگەڵ زیانبەخش. | Be most careful when a message knows a lot about you; confirm by another channel.کاتێک نامەیەک زۆر شت دەربارەی تۆ دەزانێت زۆرترین وریایی بکە؛ لە ڕێگەیەکی ترەوە پشتڕاستی بکەرەوە. |
| Tailgating (piggybacking) | Gets into a secure area by walking in behind someone who is allowed in.بە ڕۆیشتن بە دوای کەسێکدا کە مۆڵەتی هەیە دەچێتە ناو شوێنێکی پارێزراو. | A visitor carrying boxes follows staff through the badge door of a server room.میوانێک کە چەند سندوقێکی هەڵگرتووە بە دوای کارمەنداندا لە دەرگای کارتیی ژووری دەچێتە ژوورەوە. | One badge, one person; politely send strangers to reception.یەک کارت، یەک کەس؛ بە ڕێزەوە کەسانی نەناسراو بنێرە بۆ پێشوازی. |
| Vishing (voice phishing) | Phone calls that impersonate a bank, a government office or tech support to get secrets.پەیوەندیی تەلەفۆنی کە خۆی وەک بانک، فەرمانگەیەکی حکومی یان یارمەتیی تەکنیکی دەناسێنێت بۆ وەرگرتنی نهێنی. | "Tech support" for a big software company calls and asks the user to read out a password.«یارمەتیی تەکنیکی»ی کۆمپانیایەکی گەورەی تەلەفۆن دەکات و داوا لە دەکات بخوێنێتەوە. | Hang up and call the official number yourself; caller ID can be faked.دایبخە و خۆت پەیوەندی بە ژمارە فەرمییەکەوە بکە؛ ژمارەی پیشاندراو دەکرێت ساختە بێت. |
Modern tricksفێڵە نوێیەکان
The eight classic types are old ideas. Attackers keep putting them into new channels: text messages, QR codes, push notifications, and voices and faces made by artificial intelligence. The notes' real cases (next screens) used several of these, so they need names.
هەشت جۆرە کلاسیکییەکە بیرۆکەی کۆنن. بەردەوام دەیانخەنە ناو کەناڵی نوێوە: ، ، ، هەروەها دەنگ و ڕووخسارێک کە بە دروست کراون. ڕووداوە ڕاستەقینەکانی تێبینییەکان (پەڕەکانی داهاتوو) چەندانێکیان لەمانە بەکار هێناوە، بۆیە پێویستە ناویان بزانین.
One more old trick in a new window is scareware. A web page or advert suddenly shows a frightening alert — "Your computer is infected! Install this cleaner now" — often with a siren and a countdown. The "cleaner" is the malware. Never install software offered in a pop-up, and never call a number shown in one: real security warnings do neither. Close the whole browser, not just the alert, and if you are worried, run the antivirus you already have.
فێڵێکی کۆنی تر لە پەنجەرەیەکی نوێدا scarewareـە (دژەڤایرۆسی ساختە). لاپەڕەیەک یان ڕیکلامێک لەپڕ ئاگادارییەکی ترسێنەر پیشان دەدات — « تووش بووە! ئێستا ئەم پاککەرەوەیە دابمەزرێنە» — زۆرجار لەگەڵ دەنگی ئاژیر و کاتژمێرێکی پێچەوانە. «پاککەرەوە»کە خۆی . هەرگیز ئەو لە پەنجەرەیەکی لەپڕدا پێشکەش دەکرێت دامەمەزرێنە و پەیوەندی بە هیچ ژمارەیەکی ناو ئاگادارییەکەوە مەکە. خودی دابخە، نەک تەنها ئاگادارییەکە. ئەگەر نیگەرانیت، ئەو پێشتر هەتە بەکار بهێنە.
Modern tricksفێڵە نوێیەکان
Smishing and QR-code phishingفیشینگ بە نامەی کورت و فیشینگی کۆدی QR
Smishing is phishing by SMS or chat message. Texts feel personal and urgent, phones hide the full link address, and people read them on the move. A typical text says a parcel is waiting, a SIM card will be blocked or a password has expired — with a short link.
Smishing لە ڕێگەی یان نامەی چاتەوە. کەسی و بەپەلە هەست دەکرێت، مۆبایل ناونیشانی تەواوی دەشارێتەوە و خەڵک لە کاتی ڕۆیشتندا دەیانخوێننەوە. نامەیەکی ئاسایی دەڵێت پاکەتێک چاوەڕێتە، سیمکارتێک دادەخرێت یان بەسەرچووە — لەگەڵ کورت.
QR-code phishing hides the link inside a QR code, so you cannot read it before you scan. The US Federal Trade Commission warned in 2023 about fake QR stickers placed over the real ones on parking meters, and about QR codes in e-mails and texts that invent a delivery problem or an account problem. The code may open a fake login page or install malware.
لە ناو دەشارێتەوە، بۆیە پێش سکانکردن ناتوانیت بیخوێنیتەوە. کۆمیسیۆنی بازرگانیی فیدراڵیی ئەمریکا (FTC) لە ساڵی 2023دا ئاگاداریی دا لە لکاندنی ساختە بەسەر کۆدە ڕاستەقینەکاندا لەسەر ئامێرەکانی پارەدانی پارکینگ؛ هەروەها لە لە ناو و نامەدا کە کێشەیەکی گەیاندن یان هەژمار دادەهێنن. لەوانەیە کۆدەکە لاپەڕەیەکی ساختەی بکاتەوە یان دابمەزرێنێت.
Defences: do not follow links in unexpected texts — open the official app or type the address yourself; before opening a scanned code, read the address your phone previews; and be suspicious of a QR sticker stuck on top of another.
بەرگرییەکان: بەدوای ناو نامە چاوەڕواننەکراوەکاندا مەڕۆ — فەرمی بکەرەوە یان خۆت ناونیشانەکە بنووسە؛ پێش کردنەوەی کۆدێکی سکانکراو ئەو ناونیشانە بخوێنەوە کە مۆبایلەکەت پیشانی دەدات؛ و گومان لەو بکە کە بەسەر کۆدێکی تردا لکێنراوە.
QR-code phishing (quishing): how a fake code sends you to a fake page, and the checks that keep you safe.
: چۆن دەتبات بۆ ساختە، هەروەها ئەو پشکنینانەی دەتپارێزن.
Whole video (8:42): quishing and its defences.
هەموو ڤیدیۆکە (8:42): و ڕێگاکانی بەرگری لێی.
Modern tricksفێڵە نوێیەکان
Business e-mail compromise (BEC)فێڵی ئیمەیڵی بازرگانی (BEC)
Business e-mail compromise (BEC) targets money, not passwords. The criminal writes as a boss or a supplier — from a hacked mailbox or a look-alike address — and asks for an urgent payment or for "new bank details" for the next invoice. It needs no malware at all. In the FBI's report for 2025, BEC caused about $3.05 billion of reported losses from 24,768 complaints — the second-largest loss of any crime type, after investment fraud.
(BEC) ئامانجی پارەیە، نەک . تاوانبارەکە وەک بەڕێوەبەرێک یان دابینکەرێک دەنووسێت — لە سندوقێکی هاککراو یان ناونیشانێکی هاوشێوە — و داوای پارەدانێکی بەپەلە یان «زانیاریی بانکیی نوێ» بۆ پسوولەی داهاتوو دەکات. هیچ پێویستی بە نییە. لە ڕاپۆرتی FBI بۆ ساڵی 2025دا، BEC نزیکەی 3.05 ملیار دۆلار زیانی ڕاپۆرتکراوی لە 24,768 سکاڵادا دروست کرد، کە دوای فێڵی وەبەرهێنان دووەم گەورەترین زیان بوو لە هەموو جۆرەکانی تاوان.
Modern tricksفێڵە نوێیەکان
Deepfakes — and the rule that beats them and BECدیپفەیکەکان — و ئەو ڕێسایەی ئەوان و BEC دەبەزێنێت
A deepfake is fake audio or video made with AI that copies a real person's face or voice. In early 2024 a finance employee of the engineering company Arup in Hong Kong joined a video call with what looked like the company's finance director and other colleagues. All of them were deepfakes. He made 15 transfers worth HK$200 million (about US$25 million). He had first suspected the invitation e-mail was phishing — the video call convinced him.
دەنگ یان ڤیدیۆیەکی ساختەیە کە بە دروست کراوە و لاسایی ڕووخسار یان دەنگی کەسێکی ڕاستەقینە دەکاتەوە. لە سەرەتای 2024دا کارمەندێکی دارایی کۆمپانیای ئەندازیاریی Arup لە هۆنگ کۆنگ بەشداریی پەیوەندییەکی ڤیدیۆیی کرد لەگەڵ کەسانێک کە لە بەڕێوەبەری دارایی و هاوکارانی تری کۆمپانیاکە دەچوون. هەموویان بوون. 15 گواستنەوەی پارەی کرد بە بڕی 200 ملیۆن دۆلاری هۆنگ کۆنگ (نزیکەی 25 ملیۆن دۆلاری ئەمریکی). سەرەتا گومانی کردبوو کە بانگهێشتکردنەکە — پەیوەندییە ڤیدیۆییەکە قایلی کرد.
Modern tricksفێڵە نوێیەکان
MFA fatigue: approving the attackerماندووکردنی MFA: ڕەزامەندیدان بە هێرشبەر
Multi-factor authentication (MFA) stops most attacks with stolen passwords. So attackers attack the second factor too. With MFA fatigue (also called push bombing) the attacker, who already has the password, logs in again and again. The victim's phone fills with "Approve sign-in?" notifications until, tired or confused, the victim taps Approve. CISA describes exactly this.
(MFA) ڕێگە لە زۆربەی ئەو دەگرێت کە بە دزراو دەکرێن. بۆیە هێرش دەکەنە سەر هۆکاری دووەمیش. لە کە پێشتر هەیە، جار لە دوای جار هەوڵی چوونە ژوورەوە دەدات. مۆبایلی قوربانی پڕ دەبێت لە «ڕەزامەندی بە چوونە ژوورەوە دەدەیت؟» تا ئەو کاتەی قوربانی لە ماندوویەتی یان سەرلێشێواوییەوە Approve دادەگرێت. CISA ڕێک ئەمە وەسف دەکات.
The fixes, from CISA: number matching (the login screen shows a number that you must type into the app, so random prompts cannot be approved) and, better, phishing-resistant MFA such as passkeys or security keys, where there is nothing to approve by mistake. And a rule for everyone: if you did not just try to log in, never approve — report it, because the prompt means someone has your password.
چارەسەرەکان، لە CISAـوە: هاوتاکردنی ژمارە (شاشەی چوونە ژوورەوە ژمارەیەک پیشان دەدات کە دەبێت لە بینووسیت، بۆیە ناکرێت ڕەزامەندی بە داواکارییە هەڕەمەکییەکان بدرێت) و باشتر لەوە، MFAـی بەرگەگر لە بەرامبەر وەک یان ، کە هیچ شتێکی تێدا نییە بە هەڵە ڕەزامەندیی پێ بدەیت. هەروەها ڕێسایەک بۆ هەمووان: ئەگەر تۆ تازە هەوڵی چوونە ژوورەوەت نەدابێت، هەرگیز ڕەزامەندی مەدە — ڕاپۆرتی بکە، چونکە ئەو داواکارییە واتای ئەوەیە کەسێک هەیە.
Real cases, told correctlyڕووداوە ڕاستەقینەکان، بە دروستی
The notes give four "recent high-profile examples". Two are real, famous cases with wrong dates; two are common tactics without a single dated incident behind them.
تێبینییەکان چوار «نموونەی ناسراوی نوێ» دەهێنن. دووانیان ڕووداوی ڕاستەقینە و ناودارن بەڵام ڕێکەوتەکانیان هەڵەیە؛ دووانەکەی تر فێڵی باون بەبێ ئەوەی یەک ڕووداوی بەرواردار لە پشتیانەوە بێت.
- Twilio (August 2022). Employees received text messages that seemed to come from Twilio's IT department: their password had expired or their schedule had changed. The links led to fake sign-in pages on domains containing words like "twilio", "okta" and "sso". Some employees entered their credentials, and the attackers used them to reach internal tools and data of 209 customers. It was part of a wider campaign, nicknamed "0ktapus", that stole 9,931 credentials from 136 organisations. Afterwards Twilio gave every employee a FIDO2 security key.
- Uber (15 September 2022). The attacker had a contractor's password — Uber believes it was bought after malware infected the contractor's personal device. He then flooded the contractor with MFA approval requests until one was accepted (MFA fatigue). Inside, he reached other accounts, internal tools such as Slack and the company's bug-bounty dashboard, and posted a message to staff. Uber linked the attacker to the Lapsus$ group.
- Twilio (ئابی 2022). کارمەندان بۆ هات کە وا دیار بوو لە بەشی ITـی Twilioـەوە هاتوون: بەسەرچووە یان خشتەی دەوامیان گۆڕاوە. دەچوون بۆ لاپەڕەی ساختەی چوونە ژوورەوە لەسەر کە وشەی وەک «twilio»، «okta» و «sso»یان تێدا بوو. هەندێک کارمەند نووسی و بەکاریان هێنا بۆ گەیشتن بە ئامرازە ناوخۆییەکان و 209 کڕیار. بەشێک بوو لە هەڵمەتێکی فراوانتر بە نازناوی «0ktapus» کە 9,931 لە 136 ڕێکخراو دزی. دواتر Twilio FIDO2ـی دا بە هەموو کارمەندێک.
- Uber (15ی ئەیلوولی 2022). گرێبەستکارێکی هەبوو — Uber پێی وایە کڕدرابوو، دوای ئەوەی ئامێرە کەسییەکەی گرێبەستکارەکەی گرتبوو. پاشان گرێبەستکارەکەی نوقمی داواکاریی ڕەزامەندیی MFA کرد تا یەکێکیان قبووڵ کرا (). لە ناوەوە گەیشتە هەژمارەکانی تر، ئامرازە ناوخۆییەکانی وەک Slack و داشبۆردی خەڵاتی دۆزینەوەی هەڵەی کۆمپانیاکە. هەروەها نامەیەکی بۆ کارمەندان بڵاو کردەوە. Uber بە گرووپی Lapsus$ـەوە بەستەوە.
Real cases, told correctlyڕووداوە ڕاستەقینەکان، بە دروستی
Two common tactics, and what was correctedدوو فێڵی باو و ئەوەی ڕاست کرایەوە
- Fake job offers on LinkedIn — a common spear-phishing tactic: fake recruiter profiles contact people in banks or tech companies with an attractive job, and the "job description" file installs malware.
- Fake cryptocurrency giveaways — a common social-media scam: fake accounts of famous people promise to double any crypto you send, or ask you to "verify your wallet" by entering its secret recovery words.
- پێشنیاری کاری ساختە لە LinkedIn — فێڵێکی باوی : پرۆفایلی ساختەی دامەزرێنەر پەیوەندی بە کارمەندانی بانک یان کۆمپانیا تەکنەلۆجییەکانەوە دەکەن بە کارێکی سەرنجڕاکێش؛ پاشان فایلی «وەسفی کار» دادەمەزرێنێت.
- بەخشینی ساختەی — فێڵێکی باوی : هەژماری ساختەی کەسە ناودارەکان بەڵێن دەدەن هەر پارەیەکی کریپتۆ بنێریت دوو هێندەی بکەنەوە، یان داوات لێ دەکەن «جزدانەکەت پشتڕاست بکەیتەوە» بە نووسینی وشە نهێنییەکانی گەڕاندنەوەی.
Spotting a phishing messageناسینەوەی نامەیەکی فیشینگ
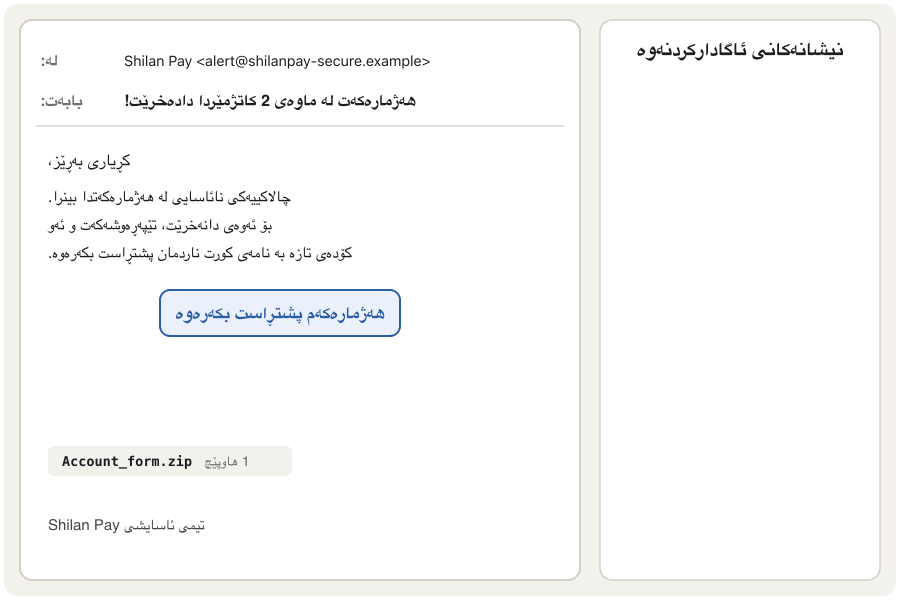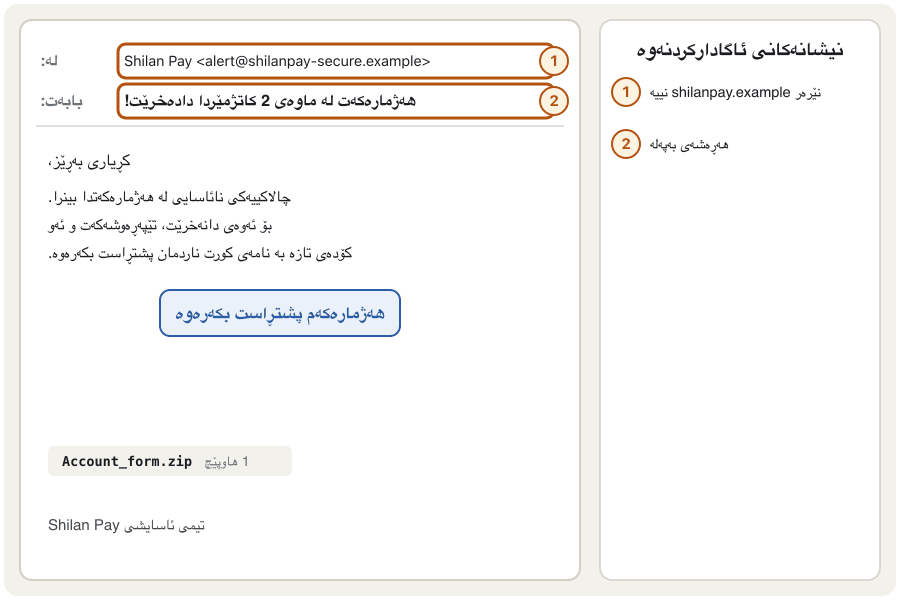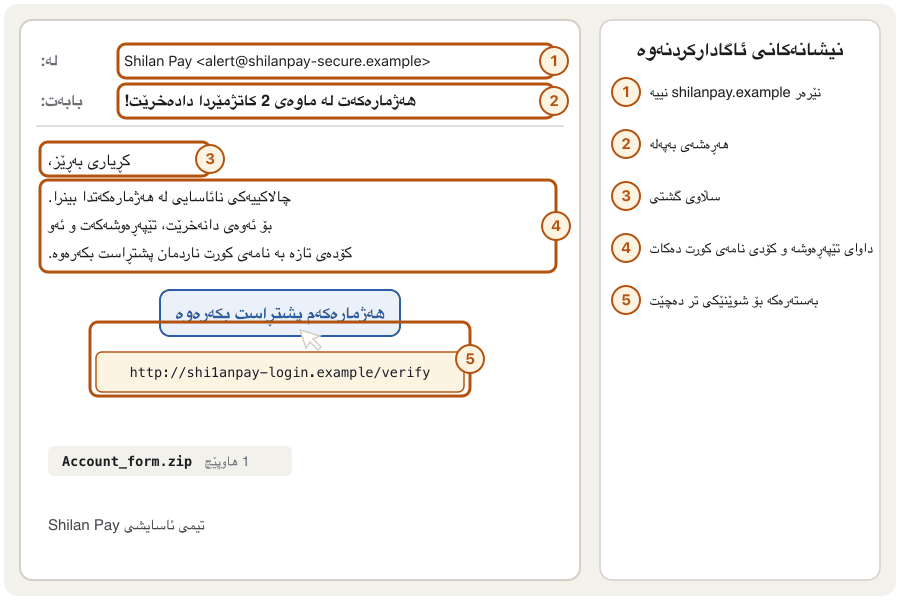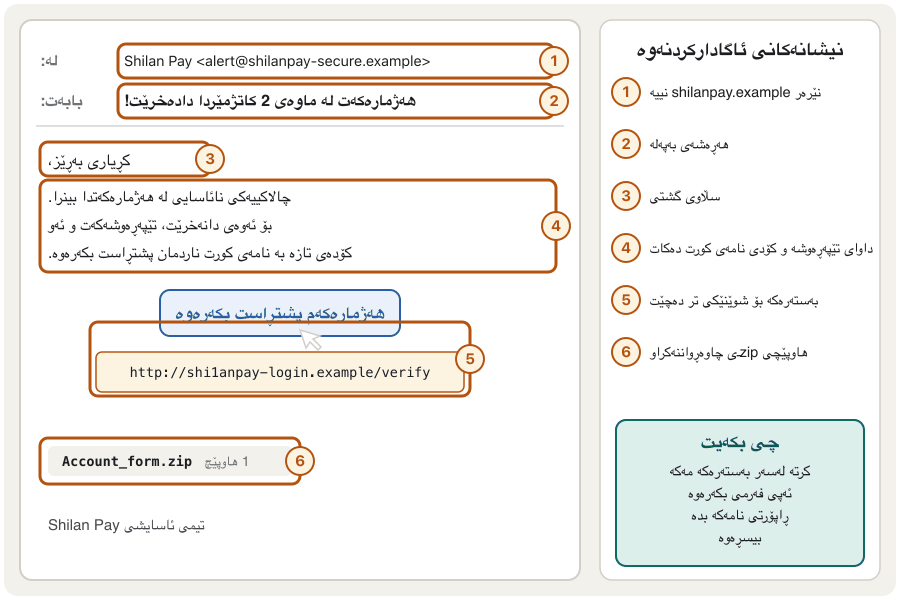
Here is a fake e-mail from a made-up payment app, Shilan Pay. Watch the warning signs light up one by one. Each sign alone may be innocent; two or three together are a strong alarm.
ئەمە ساختەیە لە پارەدانی خەیاڵی بە ناوی Shilan Pay. سەیری نیشانەکانی ئاگادارکردنەوە بکە کە یەک لە دوای یەک ڕووناک دەبنەوە. هەر نیشانەیەک بە تەنها لەوانەیە بێتاوان بێت؛ دوو یان سێیان پێکەوە ئاگادارییەکی بەهێزن.
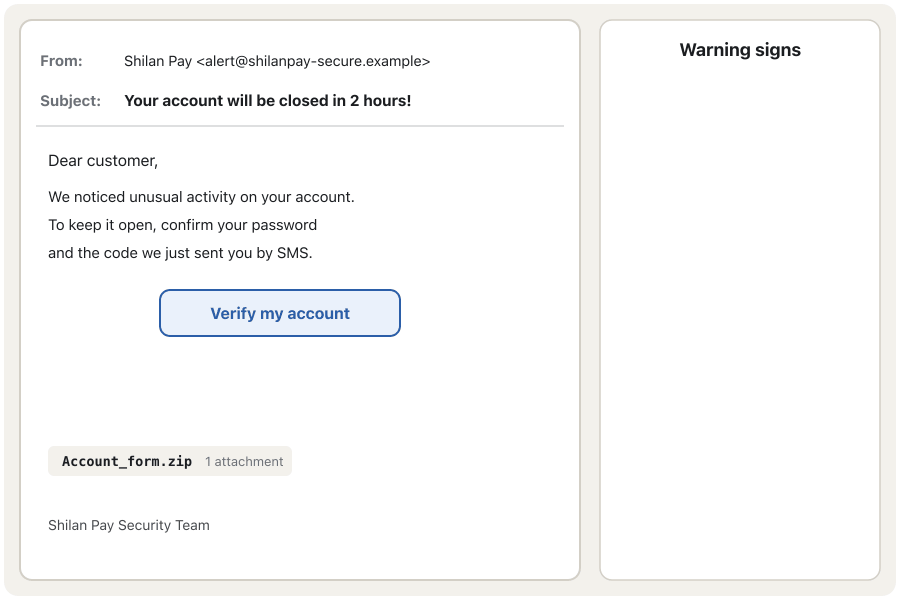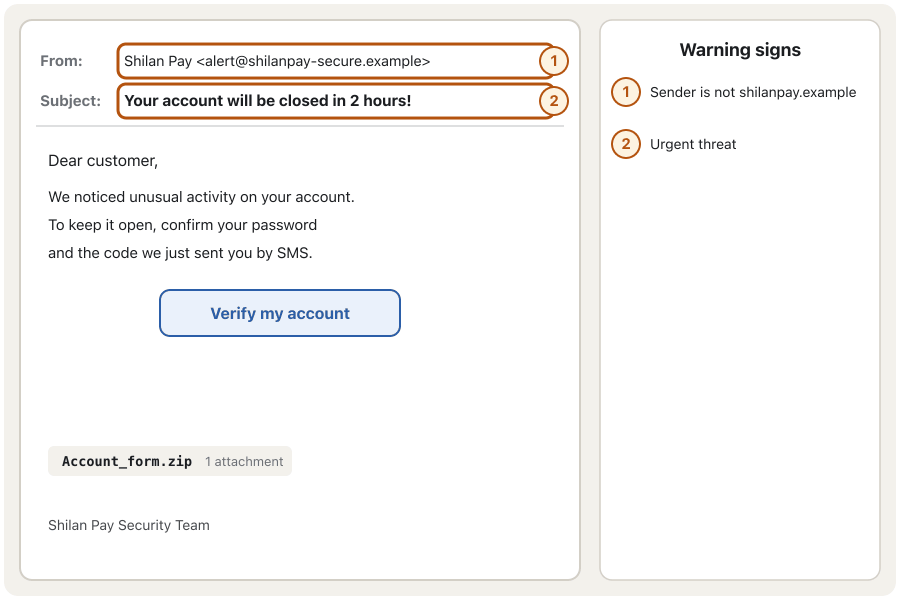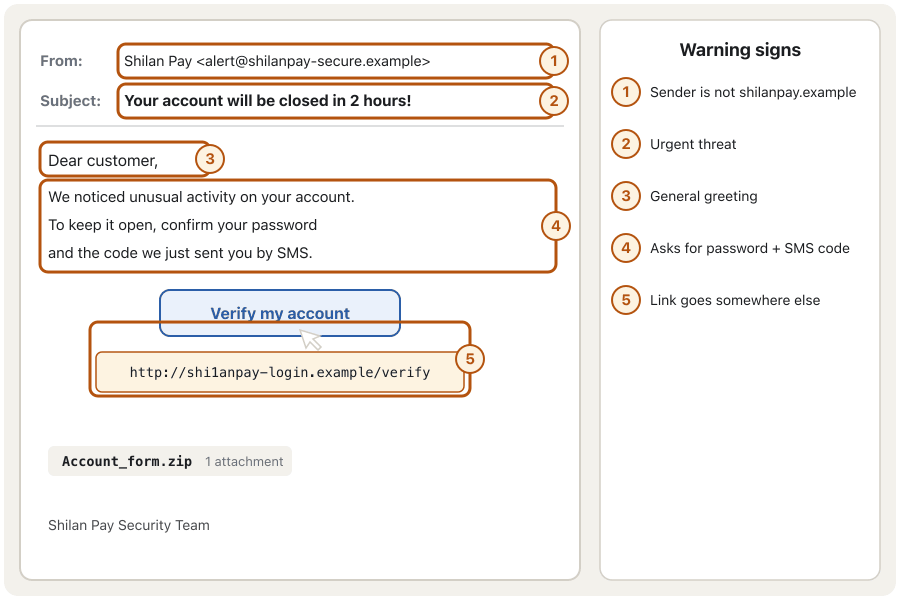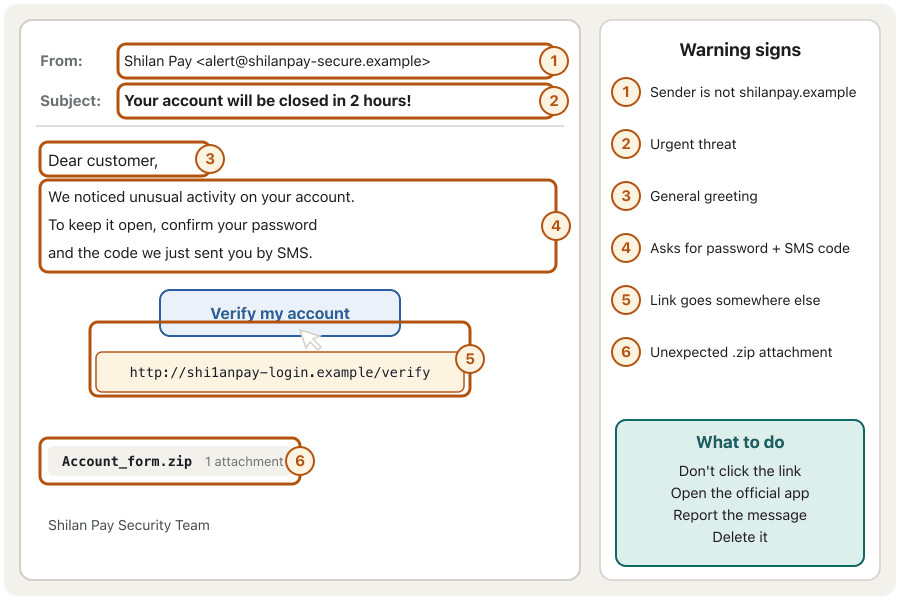
Real scam e-mails taken apart one by one: the sender address, fake links, urgency, bad grammar and what to do instead of clicking.
یەک بە یەک شی دەکرێنەوە: نێرەر، ، پەلەپێکردن، ڕێزمانی هەڵە و چی بکەیت لە جیاتی .
Whole video (10:53): reading the warning signs in real phishing e-mails.
هەموو ڤیدیۆکە (10:53): نیشانە ئاگادارکەرەوەکان لە ڕاستەقینەدا دەخوێنێتەوە.
Spotting a phishing messageناسینەوەی نامەیەکی فیشینگ
The six signs in wordsشەش نیشانەکە بە وشە
- Sender address — read the part after @. A real company writes from its own domain; look-alikes add words ("-secure") or swap letters (1 for l). The "From" line itself can be forged, because plain SMTP does not check it; SPF, DKIM and DMARC let the receiving server check it (how receivers check senders).
- Urgent or frightening subject — "within 2 hours", "account closed".
- General greeting — "Dear customer" instead of your name.
- It asks for a secret — a password, a card number or the code just sent to your phone. Real services never ask for these by e-mail.
- The link hides a different address — hover (or long-press on a phone) to see where it really goes.
- Unexpected attachment — especially zip files, programs or documents that ask you to "enable content".
- نێرەر — ئەو بەشەی دوای @ بخوێنەوە. کۆمپانیای ڕاستەقینە لە خۆیەوە دەنووسێت؛ هاوشێوەکان وشە زیاد دەکەن («-secure») یان پیت دەگۆڕن (1 لە جیاتی l). خودی هێڵی Fromـیش دەکرێت ساختە بکرێت، چونکە سادە نایپشکنێت؛ ، و ڕێگە بە وەرگر دەدەن بیپشکنێت (وەرگرەکان چۆن نێرەرەکان دەپشکنن).
- بابەتی بەپەلە یان ترسێنەر — «لە ماوەی 2 کاتژمێردا»، «هەژمار داخرا».
- سڵاوی گشتی — «کڕیاری بەڕێز» لە جیاتی ناوی خۆت.
- داوای نهێنییەک دەکات — ، ژمارەی کارت یان ئەو کۆدەی تازە بۆ مۆبایلەکەت هاتووە. خزمەتگوزارییە ڕاستەقینەکان هەرگیز بە داوای ئەمانە ناکەن.
- ناونیشانێکی جیاواز دەشارێتەوە — ماوسەکەی لەسەر ڕابگرە (یان لە مۆبایلدا پەنجەی لەسەر ڕابگرە) بۆ ئەوەی ببینیت بە ڕاستی بۆ کوێ دەچێت.
- چاوەڕواننەکراو — بە تایبەتی فایلی zip، بەرنامە یان بەڵگەنامە کە داوات لێ دەکەن «ناوەڕۆک چالاک بکەیت».
How to defend: people, process, technologyچۆن بەرگری بکەین: خەڵک، ڕێکار، تەکنەلۆجیا
The notes give four mitigation strategies. Together they cover people, processes and technology:
تێبینییەکان چوار ستراتیژی بۆ کەمکردنەوەی دەهێنن. پێکەوە خەڵک، ڕێکار و تەکنەلۆجیا دەگرنەوە:
- Education and awarenessفێرکردن و هۆشیاریی ئاسایش
Train staff and students regularly — not once — to recognise the tricks in this lesson, and teach a healthy scepticism towards unexpected messages and urgent requests. Short practice tests (phishing simulations) help people learn without blame.
کارمەندان و خوێندکاران بە بەردەوامی ڕابهێنە — نەک تەنها یەک جار — بۆ ناسینەوەی فێڵەکانی ئەم وانەیە. هەروەها گومانێکی تەندروست فێر بکە بەرامبەر نامەی چاوەڕواننەکراو و داواکاریی بەپەلە. تاقیکردنەوەی کورتی ڕاهێنان (تاقیکردنەوەکانی فیشینگ) یارمەتی خەڵک دەدەن بەبێ لۆمەکردن فێر ببن.
- Multi-factor authenticationپشتڕاستکردنەوەی فرەهۆکاری
MFA makes stolen passwords far less useful. Prefer phishing-resistant MFA (passkeys, security keys); if you use push approval, turn on number matching. See Passwords, MFA and access control.
MFA دزراو زۆر کەمسوودتر دەکات. MFAـی بەرگەگر لە بەرامبەر هەڵبژێرە (، )؛ ئەگەر ڕەزامەندیی push بەکار دەهێنیت، هاوتاکردنی ژمارە چالاک بکە. بڕوانە تێپەڕەوشەکان، MFA و کۆنترۆڵی دەستڕاگەیشتن.
- Verification processesڕێکارەکانی پشتڕاستکردنەوە
Verify identity before sharing anything sensitive: call back on a known number, never on the one in the message; require two people for payments and for changes of bank details; let reception check visitors.
پێش هاوبەشکردنی هەر شتێکی هەستیار ناسنامە پشتڕاست بکەرەوە: بە ژمارەیەکی ناسراو پەیوەندی بکەرەوە، هەرگیز بەو ژمارەیەی ناو نامەکە؛ بۆ پارەدان و گۆڕینی زانیاریی بانکی دوو کەس پێویست بکە؛ با پێشوازی میوانەکان بپشکنێت.
- Incident reportingڕاپۆرتکردنی ڕووداو
Make reporting quick and blame-free: a "report phishing" button, one phone number, thanks instead of punishment. One early report lets the security team block a fake domain for everyone.
ڕاپۆرتکردن خێرا و بێلۆمە بکە: دوگمەی «ڕاپۆرتی »، یەک ژمارەی تەلەفۆن، سوپاس لە جیاتی سزا. یەک ڕاپۆرتی زوو ڕێگە بە تیمی دەدات ساختە بۆ هەمووان دابخات.
For your own accounts, CISA's advice fits in three steps: don't click unexpected links or attachments, report the message with the report button, and delete it — without replying or using its "unsubscribe" link. Physical habits matter too: shred paper, never plug in found USB sticks, one badge per person.
بۆ هەژمارەکانی خۆت، ئامۆژگارییەکەی CISA لە سێ هەنگاودا کورت دەبێتەوە: کرتە مەکە لەسەر یان چاوەڕواننەکراو، ڕاپۆرتی بکە بە دوگمەی ڕاپۆرت و بیسڕەوە — بەبێ وەڵامدانەوە یان بەکارهێنانی «unsubscribe»ـەکەی. خووە فیزیکییەکانیش گرنگن: کاغەز ورد بکە، هەرگیز دۆزراوە مەبەستە، یەک کارت بۆ هەر کەسێک.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| "I would never fall for it."«من هەرگیز ناکەومە ئەو داوەوە.» | Spear phishing is written for you, and tiredness or stress makes anyone click. Twilio's employees were tech professionals. بۆ تۆ دەنووسرێت و ماندوویی یان فشار وا لە هەر کەسێک دەکات کرتە بکات. کارمەندانی Twilio پسپۆڕی تەکنەلۆجیا بوون. | Slow down for any request for secrets or money, and verify it.بۆ هەر داوایەکی نهێنی یان پارە هێواش ببەوە و پشتڕاستی بکەرەوە. |
| "Spelling mistakes give phishing away."«هەڵەی ڕێنووس ئاشکرا دەکات.» | AI tools now write flawless messages (CISA).ئامرازەکانی ئێستا نامەی بێهەڵە دەنووسن (CISA). | Judge by what the message asks you to do.بەپێی ئەوە هەڵیبسەنگێنە کە نامەکە داوات لێ دەکات چی بکەیت. |
| "I have MFA, so phishing can't hurt me."«MFAـم هەیە، بۆیە زیانم پێ ناگەیەنێت.» | Fake pages can capture one-time codes live (0ktapus), and push prompts can be worn down (Uber).لاپەڕە ساختەکان دەتوانن ڕاستەوخۆ بگرن (0ktapus) و داواکارییەکانی push دەکرێت بە ماندووکردن بشکێن (Uber). | Use phishing-resistant MFA where you can, and never approve a prompt you did not start.لە هەر شوێنێک توانیت MFAـی بەرگەگر لە بەرامبەر بەکار بهێنە؛ هەرگیز ڕەزامەندی بەو داواکارییە مەدە کە خۆت دەستت پێ نەکردووە. |
| "The caller ID shows my bank's number, so it's my bank."«ژمارە پیشاندراوەکە ژمارەی بانکەکەمە، کەواتە بانکەکەمە.» | Caller ID and sender names can be spoofed.ژمارەی پیشاندراو و ناوی نێرەر دەکرێت ساختە بکرێن (). | Hang up and call the number on your card or the official website.دایبخە و پەیوەندی بەو ژمارەیەوە بکە کە لەسەر کارتەکەت یان لە فەرمیی بانکەکەدایە. |
| "Reporting a click is embarrassing; I'll keep quiet."«ڕاپۆرتکردنی کرتەیەک شەرمە؛ بێدەنگ دەبم.» | Silence gives the attacker time; one report can protect everyone.بێدەنگی کات دەداتە ؛ یەک ڕاپۆرت دەتوانێت هەمووان بپارێزێت. | Report at once — the faster, the smaller the damage.یەکسەر ڕاپۆرت بدە — هەتا خێراتر، زیان کەمتر. |
Exercisesڕاهێنانەکان
Name the type of social engineering in each case: (a) a USB stick labelled "Exam answers" is left in the library; (b) a caller says he is from your bank's fraud team and asks you to read out a code; (c) a stranger follows you through the badge door of the lab; (d) a text says your parcel is held and links to a payment page; (e) a supplier's "new bank details" arrive by e-mail from an address one letter different from the real one; (f) your phone keeps asking you to approve a login you did not start.
لە هەر ڕووداوێکدا جۆری ناو ببە: (أ) کە لەسەری نووسراوە «وەڵامەکانی تاقیکردنەوە» لە کتێبخانەدا بەجێ هێڵراوە؛ (ب) کەسێک تەلەفۆن دەکات و دەڵێت لە تیمی فێڵی بانکەکەتەوەیە و داوات لێ دەکات کۆدێک بخوێنیتەوە؛ (ج) کەسێکی نەناسراو بە دوای تۆدا لە دەرگای کارتیی تاقیگەکە دێتە ژوورەوە؛ (د) دەڵێت پاکەتەکەت ڕاگیراوە و بۆ لاپەڕەیەکی پارەدان تێدایە؛ (هـ) «زانیاریی بانکیی نوێ»ی دابینکەرێک بە لە ناونیشانێکەوە دێت کە یەک پیتی لەگەڵ ناونیشانە ڕاستەقینەکەدا جیاوازە؛ (و) مۆبایلەکەت بەردەوام داوات لێ دەکات ڕەزامەندی بە چوونە ژوورەوەیەک بدەیت کە خۆت دەستت پێ نەکردووە.
Show answerوەڵامەکە پیشان بدە
- (a) Baiting.
- (b) Vishing (with pretexting).
- (c) Tailgating.
- (d) Smishing — phishing by text message.
- (e) Business e-mail compromise using a look-alike address (spoofing).
- (f) MFA fatigue: someone has your password. Deny, change the password, report.
- (أ) ئەمە .
- (ب) (لەگەڵ ).
- (ج) ئەمە .
- (د) بە .
- (هـ) بە ناونیشانێکی هاوشێوە ().
- (و) : کەسێک هەیە. ڕەتی بکەرەوە، بگۆڕە، ڕاپۆرت بدە.
You receive: "Aram Mobile: your SIM will be blocked TODAY. Confirm your details at http://aram-mobile-verify.example within 1 hour." (Aram Mobile is a made-up company.) List the warning signs and say what you should do.
ئەمەت بۆ دێت: «Aram Mobile: سیمکارتەکەت ئەمڕۆ دادەخرێت. لە ماوەی 1 کاتژمێردا زانیارییەکانت لە http://aram-mobile-verify.example پشتڕاست بکەرەوە.» (Aram Mobile کۆمپانیایەکی خەیاڵییە.) نیشانەکانی ئاگادارکردنەوە ڕیز بکە و بڵێ دەبێت چی بکەیت.
Show answerوەڵامەکە پیشان بدە
- Fear and urgency: "blocked TODAY", "within 1 hour".
- A link in an unexpected text, on a look-alike address with an extra word ("-verify"), not the company's own domain, and without https.
- It asks you to "confirm your details" — a request for personal data.
- ترس و پەلە: «ئەمڕۆ دادەخرێت»، «لە ماوەی 1 کاتژمێردا».
- لە نامەیەکی چاوەڕواننەکراودا، لەسەر ناونیشانێکی هاوشێوە بە وشەیەکی زیادەوە («-verify»)، نەک خودی کۆمپانیاکە و بەبێ https.
- داوات لێ دەکات «زانیارییەکانت پشتڕاست بکەیتەوە» — داواکردنی .
What to do: do not open the link. Check your account in the operator's official app or call its official number. Report the message (many phones have "Report junk"), then delete it.
چی بکەیت: مەکەرەوە. هەژمارەکەت لە فەرمیی کۆمپانیاکەدا بپشکنە یان پەیوەندی بە ژمارە فەرمییەکەیەوە بکە. ڕاپۆرتی نامەکە بدە (زۆر مۆبایل «Report junk»یان هەیە)، پاشان بیسڕەوە.
Karwan's electronics shop pays its suppliers by bank transfer. Write a short rule (three or four points) that would stop both a BEC e-mail and a deepfake phone call from stealing a payment.
دوکانی ئەلیکترۆنیاتی کاروان بە گواستنەوەی بانکی پارە دەدات بە دابینکەرەکانی. ڕێسایەکی کورت بنووسە (سێ یان چوار خاڵ) کە ڕێگە لە BEC و پەیوەندییەکی تەلەفۆنیی بگرێت بۆ دزینی پارەدانێک.
Show answerوەڵامەکە پیشان بدە
- No change of bank details is accepted by e-mail, chat or phone call alone.
- Every change is confirmed by calling the supplier on the number already in the shop's records.
- Payments above an agreed amount need a second person's approval.
- "Urgent" and "secret" requests get more checking, not less.
- هیچ گۆڕانکارییەک لە زانیاریی بانکیدا تەنها بە ، چات یان پەیوەندیی تەلەفۆنی قبووڵ ناکرێت.
- هەر گۆڕانکارییەک بە پەیوەندیکردن بە دابینکەرەکەوە پشتڕاست دەکرێتەوە، بەو ژمارەیەی پێشتر لە تۆمارەکانی دوکانەکەدایە.
- پارەدانی سەرووی بڕێکی ڕێککەوتوو پێویستی بە ڕەزامەندیی کەسێکی دووەم هەیە.
- داواکارییە «بەپەلە» و «نهێنی»ـیەکان پشکنینی زیاتریان دەوێت، نەک کەمتر.
For each case, name the kind of theft and say what the victim should do first: (a) Hana's banking app shows three online purchases with her card that she never made; (b) a man gave Aram's name and ID number when the traffic police stopped him; (c) a clinic sends Shilan a bill for a treatment she never had; (d) someone makes a social-media account with Rezan's photo and name and asks his friends for money. Which laws can victims use at home?
بۆ هەر ڕووداوێک جۆری دزییەکە ناو ببە و بڵێ قوربانییەکە یەکەم جار دەبێت چی بکات: (أ) ئەپی بانکی هانا سێ کڕینی ئۆنلاین بە کارتەکەی پیشان دەدات کە هەرگیز نەیکردوون؛ (ب) پیاوێک کاتێک پۆلیسی هاتووچۆ ڕایگرت ناو و ژمارەی ناسنامەی ئارامی دا؛ (ج) نۆرینگەیەک پسوولەیەک بۆ شیلان دەنێرێت بۆ چارەسەرێک کە هەرگیز وەری نەگرتووە؛ (د) کەسێک بە وێنە و ناوی ڕێزان هەژمارێک لە دروست دەکات و داوای پارە لە هاوڕێکانی دەکات. قوربانییەکان لە وڵاتی خۆماندا دەتوانن پشت بە کام یاسا ببەستن؟
Show answerوەڵامەکە پیشان بدە
- (a) Card-account theft, a kind of financial identity theft. Call the bank at once on the number printed on the card, block the card and dispute the payments.
- (b) Criminal identity theft. Go to the police with your own ID so the record is corrected.
- (c) Medical identity theft. Tell the clinic and the insurer, and ask for the medical file to be corrected.
- (d) Impersonation used for fraud. Report the fake account in the app, warn friends through a channel you trust, and report it to the police.
- (أ) دزینی هەژماری کارت، کە جۆرێکە لە دارایی. یەکسەر بەو ژمارەیەی لەسەر کارتەکە نووسراوە پەیوەندی بە بانکەکەوە بکە، کارتەکە ڕابگرە و ناڕەزایی لەسەر پارەدانەکان دەرببڕە.
- (ب) تاوانکاری. لەگەڵ ناسنامەی خۆت بڕۆ بۆ پۆلیس بۆ ئەوەی تۆمارەکە ڕاست بکرێتەوە.
- (ج) پزیشکی. نۆرینگەکە و کۆمپانیای بیمە ئاگادار بکەرەوە و داوا بکە دۆسیە پزیشکییەکە ڕاست بکرێتەوە.
- (د) بۆ فێڵکردن. هەژمارە ساختەکە لە ئەپەکەدا ڕاپۆرت بکە، لە ڕێگەی کەناڵێکی متمانەپێکراوەوە هاوڕێکان ئاگادار بکەرەوە و ڕاپۆرت بدە بە پۆلیس.
In every case, keep the evidence (screenshots with date and time). Fraud done with computers is punished under Iraq's general criminal law, and in the Kurdistan Region Law No. 6 of 2008 also punishes misusing phones and the Internet to harm people. Where to complain is in Where to report a cybercrime. This is general information, not legal advice.
لە هەموو ڕووداوەکاندا بەڵگەکان هەڵبگرە ( بە ڕێکەوت و کاتەوە). فێڵکردن بە کۆمپیوتەر بەپێی یاسا گشتییە تاوانکارییەکانی عێراق سزا دەدرێت و لە هەرێمی کوردستان یاسای ژمارە 6ی ساڵی 2008یش سزای بەکارهێنانی خراپی مۆبایل و دەدات بۆ زیانگەیاندن بە خەڵک. شوێنی سکاڵاکردن لە تاوانی سایبەری لە کوێ ڕاپۆرت بکەیتـدایە. ئەمە زانیاریی گشتییە، نەک ئامۆژگاریی یاسایی.
Summary and reviewپوختە و پێداچوونەوە
- Social engineering manipulates people, not machines, into revealing secrets or doing harmful things. It pulls on trust, fear, urgency and curiosity.
- Eight classic types: baiting, dumpster diving, pretexting, phishing, quid pro quo, spear phishing, tailgating, vishing (B-D-P-P-Q-S-T-V).
- Modern channels: smishing, QR-code phishing, business e-mail compromise, MFA fatigue and deepfake voices and videos.
- Real cases: Twilio (August 2022, smishing) and Uber (September 2022, bought password + MFA fatigue).
- Defences: regular awareness training, phishing-resistant MFA, verification through a second channel, and fast, blame-free reporting.
- کاریگەری لەسەر خەڵک دادەنێت، نەک ئامێر، بۆ ئەوەی نهێنی ئاشکرا بکەن یان کاری زیانبەخش بکەن. متمانە، ترس، پەلە و کونجکۆڵی دەجووڵێنێت.
- هەشت جۆری کلاسیکی: ، ، ، ، ، ، و (B-D-P-P-Q-S-T-V).
- کەناڵە نوێیەکان: بە ، ، ، و دەنگ و ڤیدیۆی .
- ڕووداوە ڕاستەقینەکان: Twilio (ئابی 2022، بە ) و Uber (ئەیلوولی 2022، کڕدراو + ).
- بەرگرییەکان: ڕاهێنانی بەردەوامی ، MFAـی بەرگەگر لە بەرامبەر ، پشتڕاستکردنەوە لە ڕێگەی کەناڵێکی دووەمەوە و ڕاپۆرتکردنی خێرا و بێلۆمە.
What is the difference between phishing and spear phishing?جیاوازیی نێوان فیشینگ و فیشینگی ئامانجدار چییە؟
Phishing sends the same message to many people; spear phishing is written for one person or team using details about them.
هەمان نامە بۆ خەڵکێکی زۆر دەنێرێت؛ بۆ یەک کەس یان تیم دەنووسرێت بە بەکارهێنانی وردەکاریی دەربارەیان.
Why is a sign-in prompt you did not start a warning?بۆچی داواکارییەکی چوونە ژوورەوە کە خۆت دەستت پێ نەکردووە ئاگادارکردنەوەیە؟
It appears only after the correct password was typed, so someone else has your password.
تەنها دوای نووسینی دروست دەردەکەوێت، بۆیە کەسێکی تر هەیە.
What single habit defeats BEC and deepfake calls?کام تاکە خوو BEC و پەیوەندیی دیپفەیک دەبەزێنێت؟
Verifying through a second channel you choose, such as calling a number you already have.
پشتڕاستکردنەوە لە ڕێگەی کەناڵێکی دووەمەوە کە خۆت هەڵیدەبژێریت، وەک پەیوەندیکردن بە ژمارەیەک کە پێشتر هەتە.
Why are spelling mistakes no longer a reliable sign of phishing?بۆچی هەڵەی ڕێنووس ئیتر نیشانەیەکی متمانەپێکراوی فیشینگ نییە؟
AI tools can write flawless messages, so judge a message by what it asks you to do.
ئامرازەکانی دەتوانن نامەی بێهەڵە بنووسن، بۆیە نامەیەک بەپێی ئەوە هەڵبسەنگێنە کە داوات لێ دەکات چی بکەیت.
Videoڤیدیۆ
Watch a videoسەیری ڤیدیۆیەک بکە
A video that viewers liked a lot and praised in their comments, chosen for this lesson.ڤیدیۆیەک کە بینەران زۆریان پێ خۆش بووە و لە کۆمێنتەکانیاندا ستایشیان کردووە، بۆ ئەم وانەیە هەڵبژێردراوە.
A calm talk on "hacking the human": the phases of an attack, an impersonation case, the emotional triggers attackers use, and a QR-code fraud case.
وتارێکی هێمن دەربارەی «هاککردنی مرۆڤ»: قۆناغەکانی ، ڕووداوێکی ، ئەو هەستانەی دەیانجووڵێنن و ڕووداوێکی فێڵکردن بە .
Whole talk (10:44): what social engineering is, emotional levers, real cases.
هەموو وتارەکە (10:44): چییە، ئەو هەستانەی دەیانجووڵێنێت و ڕووداوی ڕاستەقینە.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Injection Attacks: SQL Injection and Cross-Site Scriptingهێرشەکانی تێخزاندن: تێخزاندنی SQL و XSS
Related lecturesوانە پەیوەندیدارەکان
- Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
- Passwords, MFA and Access Controlتێپەڕەوشەکان، MFA و کۆنترۆڵی دەستڕاگەیشتن
- Security and Online Safetyئاسایش و سەلامەتی لە ئینتەرنێتدا
- Malware Today: Infostealers, Banking Trojans, RATs, Cryptojacking and Moreنەرمەواڵەی زیانبەخشی ئەمڕۆ: نەرمەواڵە زانیاریدزەکان، ئەسپەکانی ترۆیای بانکی، RAT، کریپتۆجاکینگ و زیاتر
- How E-mail Worksئیمەیڵ چۆن کار دەکات
- Digital Citizenship: Footprints, Netiquette and Cyberbullyingهاووڵاتیبوونی دیجیتاڵی: شوێنپێ دیجیتاڵییەکان، ئادابی ئینتەرنێت و ئازاردانی سایبەری
- Building a Security Cultureبونیادنانی کولتووری ئاسایش
- Computer-Crime Laws: Budapest, the CFAA, the UK and the Law at Homeیاساکانی تاوانی سایبەری: بوداپێست، CFAA، بەریتانیا و یاسا لە وڵاتی خۆمان
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- CISA Secure Our World: Recognize and report phishing
- CISA fact sheet: Implementing Number Matching in MFA Applications (October 2022)
- CISA fact sheet: Implementing Phishing-Resistant MFA (October 2022)
- Twilio: Incident report — August 2022 social engineering attack
- BleepingComputer: Twilio hackers hit over 130 orgs in massive Okta phishing attacks (0ktapus, August 2022)
- Help Net Security: Uber data breach — Lapsus$, MFA fatigue (20 September 2022)
- CNN: Arup revealed as victim of $25 million deepfake scam (16 May 2024)
- CNBC: QR codes may be a gateway to identity theft, FTC warns (December 2023)
- FBI Internet Crime Complaint Center: 2025 IC3 Annual Report (business e-mail compromise and identity-theft figures)
- US Federal Trade Commission: How to spot, avoid, and report tech support scams (fake virus pop-ups)
- UT Southwestern Information Security: Scareware (close the browser, not just the pop-up)
- US Federal Trade Commission: What to know about identity theft
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.