Chapterبەش 3 · Lectureوانە 3.6
Health Data and National Rules: HIPAA and China's Cybersecurity Lawدراوەی تەندروستی و یاسا نیشتیمانییەکان: HIPAA و یاسای ئاسایشی سایبەری چین
Two more legal frameworks. HIPAA: protected health information, covered entities and business associates, the Privacy, Security and Breach Notification Rules, today's inflation-adjusted penalties and the Anthem case. China: the Cybersecurity Law (amended from 1 January 2026) with the Data Security Law and the PIPL, critical infrastructure, data localisation, consent, cross-border transfers, penalties and the Didi fine. Ends with the lecture's comparison table, rebuilt and corrected.
دوو چوارچێوەی یاسایی تر. : ، دامەزراوە گیراوەکان و هاوبەشە بازرگانییەکان، ڕێساکانی ، و ، سزاکانی ئەمڕۆ کە بەپێی هەڵاوسان ڕێکخراون و نموونەی Anthem. چین: یاسای (هەموارکراو لە ١ی کانوونی دووەمی ٢٠٢٦ەوە) لەگەڵ یاسای و PIPL، ، ، ، گواستنەوەی دەرەوەی سنوور، سزاکان و سزای دیدی. بە خشتەی بەراوردکاریی وانەکە کۆتایی دێت، دووبارە دروستکراو و چاککراو.
What you will learnچی فێر دەبیت
- Explain what PHI is and who must follow HIPAA.
- Describe HIPAA's three rules and apply the breach-notification deadlines.
- Read today's HIPAA penalty tiers and explain why the old amounts changed.
- Summarise China's Cybersecurity Law, Data Security Law and PIPL: CII, localisation, consent, transfers and penalties.
- Compare the GDPR, HIPAA and China's laws in one table.
- ڕوونی بکەیتەوە PHI چییە و کێ دەبێت پەیڕەوی بکات.
- سێ ڕێساکەی وەسف بکەیت و ماوەکانی جێبەجێ بکەیت.
- ئاستەکانی ئەمڕۆی سزای بخوێنیتەوە و ڕوونی بکەیتەوە بۆچی بڕە کۆنەکان گۆڕاون.
- یاسای ، یاسای و PIPLـی چین کورت بکەیتەوە: CII، ، ، گواستنەوە و سزاکان.
- ، و یاساکانی چین لە یەک خشتەدا بەراورد بکەیت.
HIPAA: health data in the United StatesHIPAA: دراوەی تەندروستی لە ئەمریکا
Europe's GDPR protects all personal data. Many countries also have laws for one especially sensitive kind of data. The best-known is the United States' Health Insurance Portability and Accountability Act (HIPAA) of 1996. Its purpose, as the notes say, is to protect the privacy and security of healthcare data in the US.
GDPRـی ئەوروپا هەموو دەپارێزێت. زۆر وڵاتیش یاسایان هەیە بۆ جۆرێکی زۆر هەستیاری . ناسراوترینیان یاسای ئەمریکیی گواستنەوە و لێپرسینەوەی بیمەی تەندروستی ()، کە لە ١٩٩٦دا دەرچووە. مەبەستی، وەک تێبینییەکان دەڵێن، پاراستنی و تەندروستییە لە ئەمریکا.
Under , any health information that can identify a person, such as medical records, test results, bills, names, addresses or phone numbers linked to care. In electronic form it is called ePHI.
بەپێی ، هەر زانیارییەکی تەندروستییە کە بتوانێت کەسێک بناسێنێت، وەک تۆماری پزیشکی، ئەنجامی پشکنین، پسوولە، ناو، ناونیشان یان ژمارەی تەلەفۆن کە بە چارەسەرەوە پەیوەستن. بە شێوەی ئەلیکترۆنی پێی دەڵێن ePHI.
The data it protects is Protected Health Information (PHI): medical records, billing information, and any data that can identify a person in connection with their health or care, such as the patient's name, address, place of birth and mobile number. When PHI is stored or sent electronically it is called ePHI.
ئەو دەیپارێزێت (PHI)ـە: تۆماری پزیشکی، زانیاریی پسوولە و هەر کە بتوانێت کەسێک بناسێنێتەوە لە پەیوەندی لەگەڵ تەندروستی یان چارەسەرییەوە، وەک ناو، ناونیشان، شوێنی لەدایکبوون و ژمارەی مۆبایلی نەخۆش. کاتێک PHI بە شێوەی ئەلیکترۆنی هەڵدەگیرێت یان دەنێردرێت، پێی دەوترێت ePHI.
Who must obey it? HIPAA applies to covered entities and their business associates that handle PHI. Covered entities are health plans (insurers), health care clearinghouses (companies that process health bills) and health care providers (doctors, clinics, hospitals) that send health information electronically. A business associate works for a covered entity and handles PHI for it, for example a billing company or a cloud provider that stores a hospital's records.
کێ دەبێت پابەندی بێت؟ دامەزراوە گیراوەکان (covered entities) و هاوبەشە بازرگانییەکانیان (business associates) دەگرێتەوە کە مامەڵە لەگەڵ PHI دەکەن. دامەزراوە گیراوەکان بریتین لە پلانەکانی تەندروستی (کۆمپانیاکانی بیمە)، ناوەندەکانی ڕێکخستنی پسوولەی تەندروستی و دابینکەرانی چاودێریی تەندروستی (پزیشک، کلینیک، نەخۆشخانە) کە زانیاریی تەندروستی بە شێوەی ئەلیکترۆنی دەنێرن. هاوبەشی بازرگانی بۆ دامەزراوەیەکی گیراو کار دەکات و مامەڵە لەگەڵ PHIـەکەی دەکات، بۆ نموونە کۆمپانیایەکی پسوولە یان دابینکەرێکی هەوری کە تۆماری نەخۆشخانەیەک هەڵدەگرێت.
The three HIPAA rulesسێ ڕێساکەی HIPAA
The notes list HIPAA's main provisions as three rules. Each answers a different question:
تێبینییەکان خاڵە سەرەکییەکانی وەک سێ ڕێسا دەژمێرن. هەریەکەیان وەڵامی پرسیارێکی جیاواز دەداتەوە:
| Ruleڕێسا | Question it answersوەڵامی چ پرسیارێک دەداتەوە | Examplesنموونە |
|---|---|---|
| Privacy Ruleڕێسای | Who may use or disclose PHI, and for what?کێ دەتوانێت PHI بەکار بهێنێت یان ئاشکرای بکات و بۆ چی؟ | A doctor may share records with another doctor treating you, but not sell them to an advertiser; patients can see their own records.پزیشکێک دەتوانێت تۆمارەکان لەگەڵ پزیشکێکی تر کە چارەسەرت دەکات بەش بکات، بەڵام نایفرۆشێت بە ڕیکلامکەرێک؛ نەخۆشەکان دەتوانن تۆماری خۆیان ببینن. |
| Security Ruleڕێسای | How is electronic PHI (ePHI) protected?PHIـی ئەلیکترۆنی (ePHI) چۆن دەپارێزرێت؟ | Administrative safeguards: risk analysis, staff training. Physical: locked server rooms, controlled workstations. Technical: access control, audit logs, encryption in transit.پاراستنی کارگێڕی: ، ڕاهێنانی کارمەندان. فیزیکی: ژووری داخراو، ئامێری کاری کۆنترۆڵکراو. تەکنیکی: ، پشکنین، لە کاتی ناردندا. |
| Breach Notification Ruleڕێسای | Who must be told after a breach, and when?دوای کێ دەبێت ئاگادار بکرێتەوە و کەی؟ | The affected individuals, the Department of Health and Human Services (HHS), and sometimes the media: next screen.ئەو کەسانەی زیانیان پێ گەیشتووە، وەزارەتی تەندروستی و خزمەتگوزارییە مرۆییەکان (HHS) و هەندێک جار میدیا: پەردەی داهاتوو. |
The Security Rule's goal is written in a familiar way: covered entities must ensure the confidentiality, integrity and availability of all ePHI, the CIA triad.
ئامانجی ڕێسای بە شێوەیەکی ناسراو نووسراوە: دامەزراوە گیراوەکان دەبێت ، و هەموو ePHI دابین بکەن، واتە سێگۆشەی CIA.
The three HIPAA rulesسێ ڕێساکەی HIPAA
The Breach Notification Rule step by stepڕێسای ئاگادارکردنەوەی دزەکردنی دراوە هەنگاو بە هەنگاو
The notes: after a data breach, entities must notify the affected individuals, the Department of Health and Human Services (HHS), and sometimes the media. The regulations give the details:
تێبینییەکان: دوای ، دامەزراوەکان دەبێت ئەو کەسانەی زیانیان پێ گەیشتووە، وەزارەتی تەندروستی و خزمەتگوزارییە مرۆییەکان (HHS) و هەندێک جار میدیا ئاگادار بکەنەوە. ڕێساکان وردەکارییەکان دەدەن:
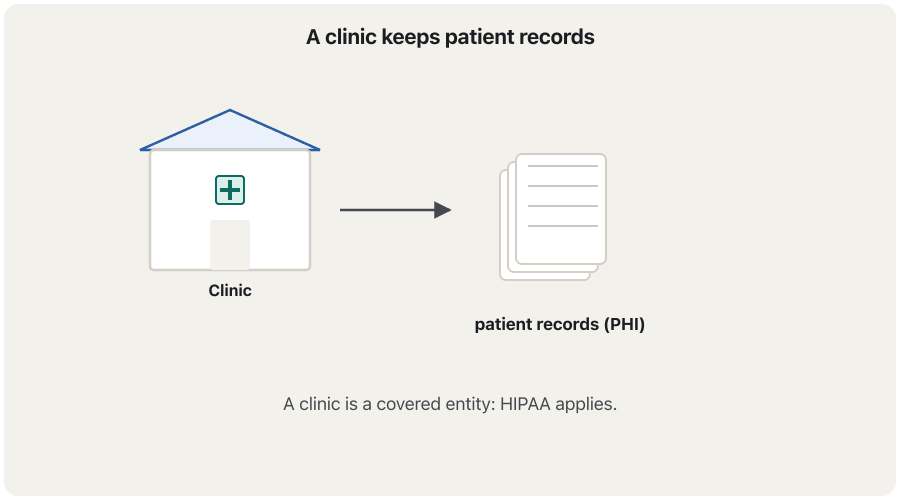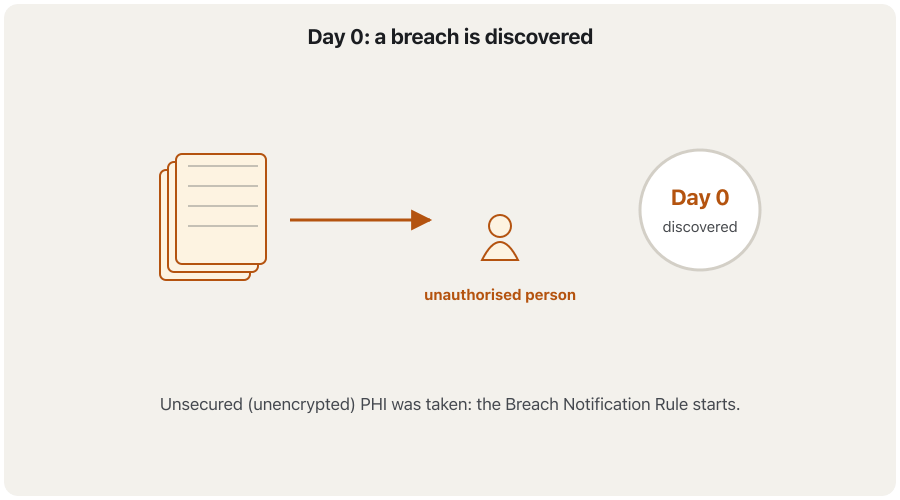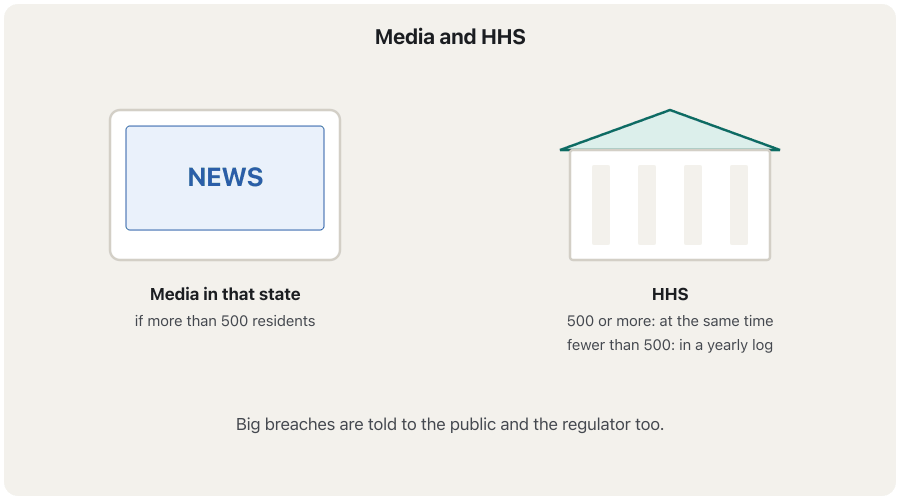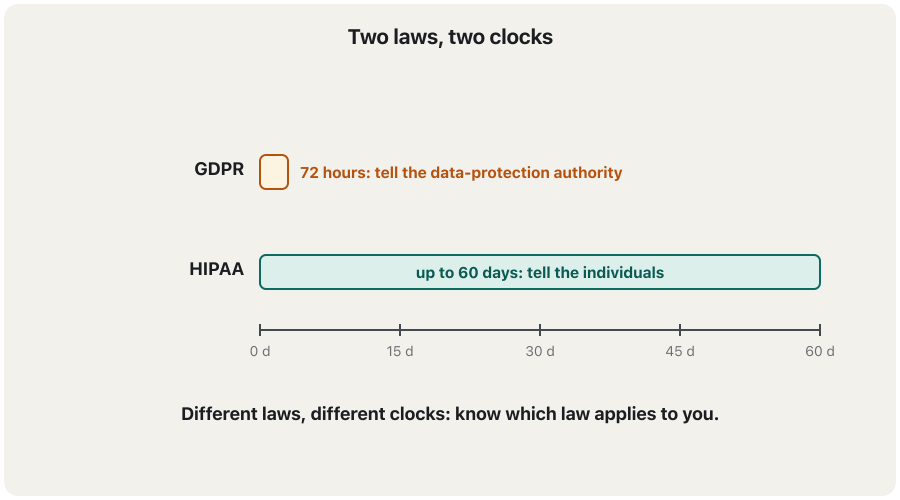
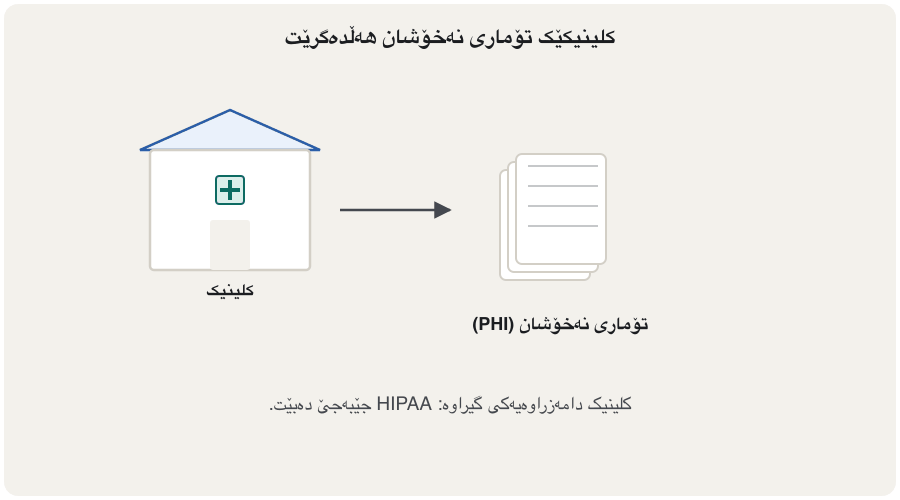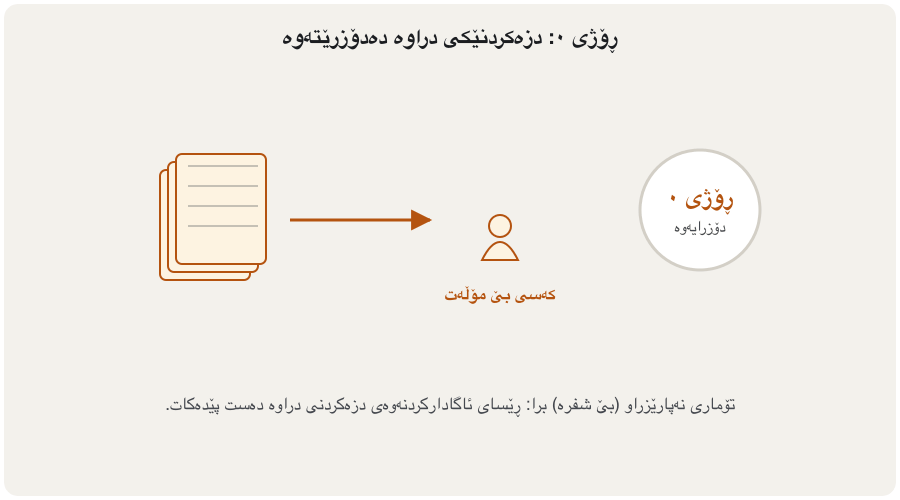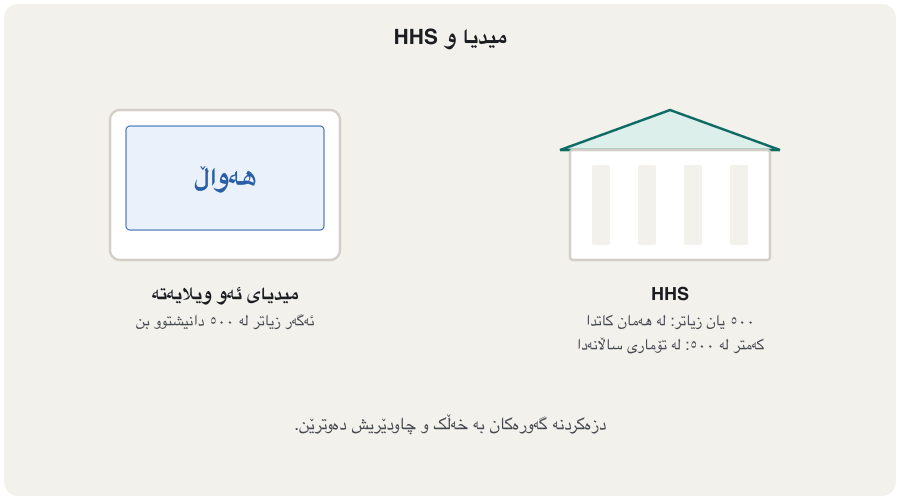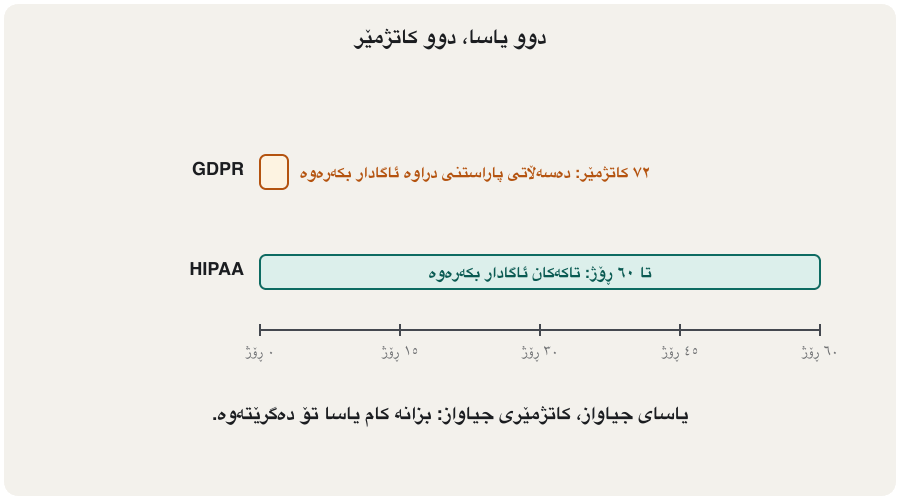
- Individuals: without unreasonable delay and no later than 60 calendar days after the breach is discovered.
- Media: if more than 500 residents of one state are affected, prominent media outlets in that state are told too, within the same 60 days.
- HHS: for 500 or more people, at the same time as the individuals; for fewer than 500, in a yearly log sent within 60 days after the end of the year.
- Only unsecured PHI: the rule covers PHI that was not made unusable, unreadable or indecipherable to outsiders. Strong encryption done the way HHS describes can mean no notification is needed.
- تاکەکان: بەبێ دواکەوتنی ناماقووڵ و لە ٦٠ ڕۆژی ڕۆژژمێری زیاتر نا دوای دۆزینەوەی .
- میدیا: ئەگەر زیاتر لە ٥٠٠ دانیشتووی یەک ویلایەت زیانیان پێ گەیشتبێت، میدیا دیارەکانی ئەو ویلایەتەش ئاگادار دەکرێنەوە، لە هەمان ٦٠ ڕۆژدا.
- HHS: بۆ ٥٠٠ کەس یان زیاتر، لە هەمان کاتی ئاگادارکردنەوەی تاکەکاندا؛ بۆ کەمتر لە ٥٠٠، لە تۆمارێکی ساڵانەدا کە لە ماوەی ٦٠ ڕۆژ دوای کۆتایی ساڵ دەنێردرێت.
- تەنها PHIـی نەپارێزراو: ڕێساکە ئەو PHI دەگرێتەوە کە نەکراوە بە شتێکی بەکارنەهاتوو، نەخوێندراو یان تێنەگەیشتوو بۆ کەسانی دەرەکی. بەهێز بەو شێوەیەی HHS وەسفی دەکات دەتوانێت واتای ئەوە بێت کە ئاگادارکردنەوە پێویست نییە.
HIPAA penalties: four tiers, adjusted for inflationسزاکانی HIPAA: چوار ئاست، ڕێکخراو بەپێی هەڵاوسان
The notes give HIPAA penalties as $100 to $50,000 per violation, capped at $1.5 million per year for repeated violations. Those were the amounts set by the HITECH Act in 2009. Today the civil penalties depend on how much the organisation was at fault, and US law requires them to be adjusted for inflation, normally every year.
تێبینییەکان سزاکانی وەک ١٠٠ تا ٥٠،٠٠٠ دۆلار بۆ هەر سەرپێچییەک، بە سنووری ١.٥ ملیۆن دۆلار لە ساڵێکدا بۆ سەرپێچیی دووبارە دەدەن. ئەمانە ئەو بڕانە بوون کە یاسای HITECH لە ٢٠٠٩دا دایناون. ئەمڕۆ سزا مەدەنییەکان بەندن بە ئەوەی ڕێکخراوەکە چەند هەڵەی کردووە و یاسای ئەمریکا داوا دەکات بەپێی هەڵاوسان ڕێک بخرێن، زۆرجار هەموو ساڵێک.
| Tier: how much at fault?ئاست: چەند هەڵەی کردووە؟ | Per violation (min – max)بۆ هەر سەرپێچییەک (کەمترین – زۆرترین) | Calendar-year cap in the ruleسنووری ساڵانە لە ڕێساکەدا |
|---|---|---|
| 1. Did not know, and could not reasonably have known١. نەیدەزانی و بە شێوەیەکی ماقووڵ نەیدەتوانی بزانێت | $145 – $73,011 | $2,190,294 |
| 2. Reasonable cause, not wilful neglect٢. هۆی ماقووڵ، نەک کەمتەرخەمیی بە ئەنقەست | $1,461 – $73,011 | $2,190,294 |
| 3. Wilful neglect, corrected within 30 days٣. کەمتەرخەمیی بە ئەنقەست، لە ماوەی ٣٠ ڕۆژدا چاک کرا | $14,602 – $73,011 | $2,190,294 |
| 4. Wilful neglect, not corrected in time٤. کەمتەرخەمیی بە ئەنقەست، لە کاتی خۆیدا چاک نەکرا | $73,011 – $2,190,294 | $2,190,294 |
Lower yearly caps in practiceسنووری ساڵانەی نزمتر لە ڕاستیدا
A HIPAA case: Anthem, $16 millionنموونەیەکی HIPAA: Anthem، ١٦ ملیۆن دۆلار
The notes' example: Anthem Inc. paid $16 million in 2018 for a breach affecting 79 million people, then the largest HIPAA settlement. Anthem is a large US health insurer. Attackers got in through spear-phishing e-mails (targeted fake e-mails) and stayed inside for weeks, taking the records of almost 79 million people. In October 2018 the HHS Office for Civil Rights announced the settlement. Besides the money, Anthem had to follow a corrective plan under government supervision, starting with a thorough risk analysis; regulators stressed that large health organisations are expected to monitor their systems and react to incidents quickly.
نموونەی تێبینییەکان: کۆمپانیای Anthem لە ٢٠١٨دا ١٦ ملیۆن دۆلاری دا بەهۆی کە ٧٩ ملیۆن کەسی گرتەوە، کە ئەو کات گەورەترین ڕێککەوتنی بوو. Anthem کۆمپانیایەکی گەورەی بیمەی تەندروستیی ئەمریکییە. لە ڕێگەی (ئیمەیڵی ساختەی ئامانجدار) چوونە ژوورەوە و چەند هەفتەیەک لە ناوەوە مانەوە و تۆماری نزیکەی ٧٩ ملیۆن کەسیان برد. لە تشرینی یەکەمی ٢٠١٨دا نووسینگەی مافە مەدەنییەکانی HHS ڕێککەوتنەکەی ڕاگەیاند. جگە لە پارەکە، Anthem دەبوو پلانێکی چاککردن لەژێر چاودێریی حکوومەتدا پەیڕەو بکات، کە بە وردەوە دەست پێدەکات؛ چاودێران جەختیان کردەوە کە چاوەڕێ دەکرێت ڕێکخراوە گەورەکانی تەندروستی چاودێریی سیستەمەکانیان بکەن و بە خێرایی وەڵامی ڕووداوەکان بدەنەوە.
China's Cybersecurity Lawیاسای ئاسایشی سایبەری چین
The third framework is China's Cybersecurity Law (adopted in November 2016, in force since 1 June 2017). The notes give its purpose: to strengthen network security, protect critical information infrastructure and safeguard personal information. It applies to all businesses operating in China, including foreign companies.
سێیەم چوارچێوە یاسای چینە (لە تشرینی دووەمی ٢٠١٦دا پەسەند کرا، لە ١ی حوزەیرانی ٢٠١٧ەوە جێبەجێ دەکرێت). تێبینییەکان مەبەستەکەی دەدەن: بەهێزکردنی ، پاراستنی زانیاری و پاراستنی زانیاریی کەسی. هەموو ئەو کار و کۆمپانیایانە دەگرێتەوە کە لە چین کار دەکەن، لەوانە کۆمپانیا بیانییەکان.
- Critical information infrastructure (CII): organisations in key sectors must follow stricter security standards, because an attack on them could seriously harm national security, people's lives or the public interest. The notes' examples are finance, transport and healthcare; the law's own list (Article 31) names public communications, energy, transport, water, finance, public services and e-government, plus any other system whose loss would cause such serious harm.
- Data localisation: personal information and important data collected in China must be stored inside China.
- User consent: companies must get users' consent before collecting personal data, say why and how it is used, and collect only what their service needs.
- Data transfers: sending personal data across the border needs a security assessment first.
- (CII): ڕێکخراوەکانی کەرتە سەرەکییەکان دەبێت پەیڕەوی ستانداردی توندتر بکەن، چونکە بۆ سەریان دەتوانێت زیانی گەورە بە ، ژیانی خەڵک یان بەرژەوەندیی گشتی بگەیەنێت. نموونەکانی تێبینییەکان دارایی، گواستنەوە و تەندروستین؛ لیستی خودی یاساکە (ماددەی ٣١) پەیوەندییە گشتییەکان، وزە، گواستنەوە، ئاو، دارایی، خزمەتگوزارییە گشتییەکان و حکوومەتی ئەلیکترۆنی ناو دەهێنێت، لەگەڵ هەر سیستەمێکی تر کە لەدەستدانی زیانێکی ئاوها گەورە دروست بکات.
- : زانیاریی کەسی و گرنگ کە لە چین کۆکراونەتەوە دەبێت لە ناو چیندا هەڵبگیرێن.
- : کۆمپانیاکان دەبێت پێش کۆکردنەوەی وەربگرن، بڵێن بۆچی و چۆن بەکار دێت و تەنها ئەوەندە کۆ بکەنەوە کە خزمەتگوزارییەکەیان پێویستی پێیەتی.
- گواستنەوەی : ناردنی بۆ دەرەوەی سنوور سەرەتا پێویستی بە هەڵسەنگاندنی هەیە.
A legal rule that some , especially citizens' , must be stored on servers inside the country. China's Cybersecurity Law is a well-known example.
ڕێسایەکی یاساییە کە هەندێک ، بەتایبەتی ، دەبێت لەسەر ناو وڵات خەزن بکرێن. یاسای چین نموونەیەکی ناسراوە.
Localisation and transfers todayهێشتنەوەی دراوە لە ناو وڵات و ناردنی دراوە بۆ دەرەوە، ئەمڕۆ
Three laws that work togetherسێ یاسا کە پێکەوە کار دەکەن
The notes name one Chinese law, but today three laws are read together. The Cybersecurity Law (2017) covers network security and CII. The Data Security Law (DSL, in force 1 September 2021) covers all handling of data, sorts data by importance ('important data', 'core data') and controls handing data to foreign courts or police. The Personal Information Protection Law (PIPL, in force 1 November 2021) is China's main personal-data law, close in many ways to the GDPR: it has several lawful bases besides consent, rules for cross-border transfers, and it also reaches companies abroad that offer products or services to people in China or analyse their behaviour.
تێبینییەکان ناوی یەک یاسای چین دەهێنن، بەڵام ئەمڕۆ سێ یاسا پێکەوە دەخوێنرێنەوە. یاسای (٢٠١٧) و CII دەگرێتەوە. یاسای (DSL، لە ١ی ئەیلوولی ٢٠٢١ەوە) هەموو مامەڵەکردنێک لەگەڵ دەگرێتەوە، بەپێی گرنگی پۆلێن دەکات (« گرنگ»، « بنەڕەتی») و کۆنترۆڵی دانی بە دادگا یان پۆلیسی بیانی دەکات. یاسای پاراستنی زانیاریی کەسی (PIPL، لە ١ی تشرینی دووەمی ٢٠٢١ەوە) یاسا سەرەکییەکەی چینە بۆ و لە زۆر ڕووەوە لە نزیکە: جگە لە چەند تری هەیە، ڕێسای گواستنەوەی دەرەوەی سنووری هەیە و ئەو کۆمپانیا بیانییانەش دەگرێتەوە کە بەرهەم یان خزمەتگوزاری پێشکەش بە خەڵکی ناو چین دەکەن یان ڕەفتاریان شی دەکەنەوە.
Penalties under the Cybersecurity Lawسزاکان بەپێی یاسای ئاسایشی سایبەری چین
The notes list the penalties for breaking the Cybersecurity Law as severe fines, revocation (cancelling) of business licences, and criminal charges. Under the original law, regulators could order corrections, give warnings, confiscate illegal income and fine up to about RMB 1 million in many cases; responsible managers could be fined too; serious cases could lead to suspended business, closed websites or cancelled licences.
تێبینییەکان سزاکانی شکاندنی یاسای بەم شێوەیە دەژمێرن: سزای دارایی قورس، هەڵوەشاندنەوەی (پووچەڵکردنەوەی) مۆڵەتی بازرگانی و تۆمەتی تاوانکاری. بەپێی یاسا ڕەسەنەکە، چاودێران دەیانتوانی فەرمانی چاککردن بدەن، ئاگادار بکەنەوە، داهاتی نایاسایی دەستبەسەر بگرن و لە زۆر حاڵەتدا تا نزیکەی ١ ملیۆن یوان سزای دارایی بدەن؛ بەڕێوەبەرە بەرپرسەکانیش دەکرا سزای دارایی بدرێن؛ حاڵەتە قورسەکان دەیانتوانی ببنە هۆی ڕاگرتنی کار، داخستنی یان هەڵوەشاندنەوەی مۆڵەتەکان.
The 2026 amendment and the PIPL's finesهەموارکردنەوەی ٢٠٢٦ و سزاکانی PIPL
The 2026 amendment. On 28 October 2025 China amended the Cybersecurity Law for the first time; the new version has been in force since 1 January 2026. Fines are now higher: where the consequences are 'particularly serious', a company can be fined RMB 2 to 10 million, and the responsible persons RMB 200,000 to 1 million. CII operators can be fined for a first violation, the law reaches foreign organisations whose activities endanger China's cybersecurity more widely, and a new article supports the development and safe use of artificial intelligence.
هەموارکردنەوەی ٢٠٢٦. لە ٢٨ی تشرینی یەکەمی ٢٠٢٥دا چین بۆ یەکەمجار یاسای هەموار کرد؛ وەشانە نوێیەکە لە ١ی کانوونی دووەمی ٢٠٢٦ەوە جێبەجێ دەکرێت. سزا داراییەکان ئێستا بەرزترن: کاتێک ئەنجامەکان «زۆر قورس» بن، کۆمپانیایەک دەتوانرێت ٢ تا ١٠ ملیۆن یوان سزا بدرێت و کەسە بەرپرسەکان ٢٠٠،٠٠٠ تا ١ ملیۆن یوان. بەڕێوەبەرانی CII دەکرێت بۆ یەکەم سەرپێچی سزای دارایی بدرێن، یاساکە بە شێوەیەکی فراوانتر ئەو ڕێکخراوە بیانییانە دەگرێتەوە کە چالاکییەکانیان چین دەخەنە مەترسییەوە و ماددەیەکی نوێ پاڵپشتیی پەرەپێدان و بەکارهێنانی سەلامەتی دەکات.
Under the PIPL, the most serious personal-information violations can bring fines of up to RMB 50 million or 5% of the previous year's turnover, suspension of business or cancelled licences, and fines of RMB 100,000 to 1 million for the responsible persons, who can also be banned from senior posts for a time.
بەپێی PIPL، قورسترین سەرپێچییەکانی زانیاریی کەسی دەتوانن ببنە هۆی سزای دارایی تا ٥٠ ملیۆن یوان یان ٥٪ی داهاتی ساڵی پێشوو، ڕاگرتنی کار یان هەڵوەشاندنەوەی مۆڵەت و سزای دارایی ١٠٠،٠٠٠ تا ١ ملیۆن یوان بۆ کەسە بەرپرسەکان، کە دەکرێت بۆ ماوەیەکیش لە پۆستە باڵاکان قەدەغە بکرێن.
A Chinese case: Didi, 2021–2022نموونەیەکی چینی: دیدی، ٢٠٢١–٢٠٢٢
The notes' example: in 2021 the ride-hailing giant Didi was investigated for alleged data-handling violations, which led to a ban on downloading its app. Didi had listed its shares on the New York Stock Exchange in June 2021. Days later, in July 2021, China's Cyberspace Administration (CAC) opened a review, ordered app stores to remove Didi's apps and stopped it from signing up new users.
نموونەی تێبینییەکان: لە ٢٠٢١دا لە کۆمپانیای گەورەی گواستنەوەی دیدی لێکۆڵینەوە کرا بەهۆی سەرپێچیی گومانلێکراو لە مامەڵەکردن لەگەڵ ، کە بووە هۆی قەدەغەکردنی دابەزاندنی . دیدی لە حوزەیرانی ٢٠٢١دا پشکەکانی لە بازاڕی پشکی نیویۆرک خستبووە ڕوو. چەند ڕۆژێک دواتر، لە تەممووزی ٢٠٢١دا، دەزگای سایبەریی چین (CAC) پێداچوونەوەیەکی دەست پێکرد، فەرمانی دا دیدی لە لابدرێن و ڕێی لە تۆمارکردنی بەکارهێنەری نوێ گرت.
The three laws side by sideسێ یاساکە لە تەنیشت یەک
The lecture ends this part with a comparison table. Here it is rebuilt, with the old numbers corrected and China's three laws together.
وانەکە ئەم بەشە بە خشتەیەکی بەراوردکاری کۆتایی پێدەهێنێت. ئەمە دووبارە دروستکراوەکەیەتی، لەگەڵ چاککردنی ژمارە کۆنەکان و سێ یاساکەی چین پێکەوە.
| Aspectلایەن | GDPR (Europe) (ئەوروپا) | HIPAA (USA) (ئەمریکا) | Cybersecurity Law + DSL + PIPL (China)یاسای + DSL + PIPL (چین) |
|---|---|---|---|
| Focusناوەڕۆک | Personal data protection and privacy کەسی و | Health-care data privacy and security و تەندروستی | Network security, critical infrastructure, data security, personal information, data localisation ، ، ، زانیاریی کەسی، |
| Scopeبواری جێبەجێکردن | Any organisation handling data of people in the EU/EEA, wherever it isهەر ڕێکخراوێک کە مامەڵە لەگەڵ خەڵکی ناو یەکێتیی ئەوروپا دەکات، لە هەر شوێنێک بێت | Health plans, clearinghouses, providers and their business associatesپلانەکانی تەندروستی، ناوەندەکانی پسوولە، دابینکەران و هاوبەشە بازرگانییەکانیان | Businesses operating in China, including foreign ones; PIPL also reaches some activities abroadکار و کۆمپانیاکانی ناو چین، لەوانە بیانییەکان؛ PIPL هەندێک چالاکیی دەرەوەش دەگرێتەوە |
| Key provisionsخاڵە سەرەکییەکان | Lawful basis and consent, eight rights, 72-hour breach notice, accountability, fines و ، هەشت ماف، ئاگادارکردنەوەی ٧٢ کاتژمێر، ، سزای دارایی | Privacy, Security and Breach Notification Rules (60 days)ڕێساکانی ، و (٦٠ ڕۆژ) | CII rules, localisation, consent, cross-border assessments or contractsڕێساکانی CII، ، ، هەڵسەنگاندن یان گرێبەستی دەرەوەی سنوور |
| Penaltiesسزاکان | Up to €20 M or 4% of worldwide turnover (lower tier €10 M or 2%)تا ٢٠ ملیۆن یۆرۆ یان ٤٪ی داهاتی جیهانی (ئاستی نزم ١٠ ملیۆن یان ٢٪) | $145 to $73,011 per violation; up to $2,190,294 a year (2026 levels)١٤٥ تا ٧٣،٠١١ دۆلار بۆ هەر سەرپێچییەک؛ تا ٢،١٩٠،٢٩٤ دۆلار لە ساڵێکدا (ئاستەکانی ٢٠٢٦) | CSL up to RMB 10 M (2026); PIPL up to RMB 50 M or 5%; licence revocation; criminal law for crimesCSL تا ١٠ ملیۆن یوان (٢٠٢٦)؛ PIPL تا ٥٠ ملیۆن یوان یان ٥٪؛ هەڵوەشاندنەوەی مۆڵەت؛ یاسای سزادان بۆ تاوانەکان |
| Exampleنموونە | Amazon €746 M (2021, annulled on appeal 2026); Meta €1.2 bn (2023)ئەمازۆن ٧٤٦ ملیۆن یۆرۆ (٢٠٢١، لە ٢٠٢٦ هەڵوەشێنرایەوە)؛ مێتا ١.٢ ملیار یۆرۆ (٢٠٢٣) | Anthem $16 M settlement (2018)Anthem ١٦ ملیۆن دۆلار ڕێککەوتن (٢٠١٨) | Didi 8.026 bn yuan fine (2022)دیدی ٨.٠٢٦ ملیار یوان سزا (٢٠٢٢) |
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Correct ideaبیرۆکەی دروست |
|---|---|
| 'HIPAA fines are $100 to $50,000.'«سزاکانی ١٠٠ تا ٥٠،٠٠٠ دۆلارن.» | Those were 2009 amounts; today $145 to $73,011 per violation (up to $2,190,294 for the top tier), adjusted for inflation.ئەوانە بڕەکانی ٢٠٠٩ بوون؛ ئەمڕۆ ١٤٥ تا ٧٣،٠١١ دۆلار بۆ هەر سەرپێچییەک (تا ٢،١٩٠،٢٩٤ دۆلار بۆ ئاستی سەرەوە)، ڕێکخراو بەپێی هەڵاوسان. |
| 'HIPAA covers every company that has health data.'« هەموو کۆمپانیایەک دەگرێتەوە کە تەندروستیی هەیە.» | Only covered entities and their business associates; a fitness app selling straight to users may fall outside it (other laws can still apply).تەنها دامەزراوە گیراوەکان و هاوبەشە بازرگانییەکانیان؛ ئەپێکی وەرزش کە ڕاستەوخۆ بە دەفرۆشرێت لەوانەیە نەیگرێتەوە (یاسای تر دەکرێت جێبەجێ ببن). |
| 'All companies in China must keep all data in China.'«هەموو کۆمپانیایەک لە چین دەبێت هەموو لە چین بهێڵێتەوە.» | Strict localisation is for CII operators and very large processors; others can transfer after an assessment, certification or standard contract, or under an exemption. توند بۆ بەڕێوەبەرانی CII و کۆمپانیا زۆر گەورەکانە؛ ئەوانی تر دەتوانن دوای هەڵسەنگاندن، بڕوانامە یان گرێبەستی ستاندارد، یان بە بەدەرکردن، بیگوازنەوە. |
| 'China's Cybersecurity Law punishes with execution.'«یاسای چین بە لەسێدارەدان سزا دەدات.» | It sets fines, suspensions, licence revocation and short detention; crimes go to the Criminal Law.سزای دارایی، ڕاگرتن، هەڵوەشاندنەوەی مۆڵەت و دەستبەسەرکردنی کورت دادەنێت؛ تاوانەکان دەچنە ژێر یاسای سزادان. |
| 'Didi was only investigated.'«تەنها لە دیدی لێکۆڵینەوە کرا.» | It was fined 8.026 billion yuan in July 2022.لە تەممووزی ٢٠٢٢دا ٨.٠٢٦ ملیار یوان سزا درا. |
Exercisesڕاهێنانەکان
For each case, say whether the GDPR, HIPAA or China's laws apply (more than one may): (a) a hospital in Chicago stores patient files on a cloud server; (b) a Chinese bank sends its customers' records to a data centre in Singapore; (c) an Iraqi online course sells to students living in France; (d) a US cloud company stores a hospital's records for it.
بۆ هەر حاڵەتێک بڵێ ، یان یاساکانی چین جێبەجێ دەبن (دەکرێت زیاتر لە یەک بێت): (أ) نەخۆشخانەیەک لە شیکاگۆ فایلی نەخۆشان لەسەر هەوری هەڵدەگرێت؛ (ب) بانکێکی چینی تۆماری کڕیارەکانی دەنێرێت بۆ سەنتەرێکی لە سەنگاپوور؛ (ج) کۆرسێکی سەرهێڵی عێراقی بە خوێندکارانی نیشتەجێی فەرەنسا دەفرۆشرێت؛ (د) کۆمپانیایەکی هەوریی ئەمریکی تۆماری نەخۆشخانەیەک بۆی هەڵدەگرێت.
Show answerوەڵامەکە پیشان بدە
- (a) HIPAA: the hospital is a covered entity.
- (b) China's laws: a bank is likely CII, so the transfer needs a security assessment (PIPL and the Cybersecurity Law).
- (c) GDPR: it offers services to people in the EU (Article 3), although it is in Iraq.
- (d) HIPAA: the cloud company is a business associate of the hospital.
- (أ) : نەخۆشخانەکە دامەزراوەیەکی گیراوە.
- (ب) یاساکانی چین: بانک لەوانەیە CII بێت، بۆیە گواستنەوەکە پێویستی بە هەڵسەنگاندنی هەیە (PIPL و یاسای ).
- (ج) : خزمەتگوزاری پێشکەش بە خەڵکی ناو یەکێتیی ئەوروپا دەکات (ماددەی ٣)، هەرچەندە لە عێراقە.
- (د) : کۆمپانیا هەورییەکە هاوبەشێکی بازرگانیی نەخۆشخانەکەیە.
A clinic had 10 violations of the same rule because of reasonable cause (tier 2). Using the table in the rule, give the smallest and the largest total for the year, before any enforcement-discretion cap.
کلینیکێک ١٠ سەرپێچیی هەمان ڕێسای کردووە بە هۆیەکی ماقووڵ (ئاستی ٢). بە بەکارهێنانی خشتەکەی ناو ڕێساکە، کەمترین و زۆرترین کۆی ساڵانە بڵێ، پێش هەر سنوورێکی ئازادیی جێبەجێکردن.
Show answerوەڵامەکە پیشان بدە
is the smallest yearly total and the largest. With the 2019 enforcement-discretion cap for tier 2 ($100,000 before inflation adjustment), the real yearly total would be limited further.
کەمترین کۆی ساڵانەیە و زۆرترینیان. بە سنووری ئازادیی جێبەجێکردنی ٢٠١٩ بۆ ئاستی ٢ (١٠٠،٠٠٠ دۆلار پێش ڕێکخستنی هەڵاوسان)، کۆی ساڵانەی ڕاستەقینە زیاتر سنووردار دەبێت.
The lecture's table said: HIPAA penalties '$100 to $50,000 per violation' and Didi '(investigation for data mishandling)'. Rewrite both cells for today and give one source for each.
خشتەکەی وانەکە دەیگوت: سزاکانی «١٠٠ تا ٥٠،٠٠٠ دۆلار بۆ هەر سەرپێچییەک» و دیدی «(لێکۆڵینەوە بۆ خراپ مامەڵەکردن لەگەڵ )». هەردوو خانەکە بۆ ئەمڕۆ دووبارە بنووسەوە و بۆ هەریەکەیان سەرچاوەیەک بدە.
Show answerوەڵامەکە پیشان بدە
- HIPAA: '$145 to $73,011 per violation, up to $2,190,294 a year for the top tier (HHS, 2025 levels in force from 28 January 2026; no 2026 adjustment)'. Source: the Federal Register rule of 28 January 2026 and the HHS notice of 21 October 2026.
- Didi: '8.026 billion yuan fine by the CAC (July 2022)'. Source: Al Jazeera, 21 July 2022.
- : «١٤٥ تا ٧٣،٠١١ دۆلار بۆ هەر سەرپێچییەک، تا ٢،١٩٠،٢٩٤ دۆلار لە ساڵێکدا بۆ ئاستی سەرەوە (HHS، ئاستەکانی ٢٠٢٥ کە لە ٢٨ی کانوونی دووەمی ٢٠٢٦ەوە کاریان پێ دەکرێت؛ بۆ ٢٠٢٦ ڕێکخستن نییە)». سەرچاوە: ڕێساکەی تۆماری فیدراڵی لە ٢٨ی کانوونی دووەمی ٢٠٢٦ و ئاگادارییەکەی HHS لە ٢١ی تشرینی یەکەمی ٢٠٢٦.
- دیدی: «٨.٠٢٦ ملیار یوان سزای دارایی لەلایەن CAC (تەممووزی ٢٠٢٢)». سەرچاوە: ئەلجەزیرە، ٢١ی تەممووزی ٢٠٢٢.
Summary and reviewکورتە و پێداچوونەوە
- HIPAA (US, 1996) protects PHI held by covered entities and their business associates, through the Privacy, Security and Breach Notification Rules.
- HIPAA breach: tell individuals within 60 days; the media if more than 500 in a state; HHS at once for 500 or more, yearly for fewer.
- HIPAA penalties follow four tiers of fault and are adjusted for inflation: today $145 to $73,011 per violation, up to $2,190,294 a year; Anthem paid $16 million in 2018.
- China: the Cybersecurity Law (2017, amended from 1 January 2026), the Data Security Law and the PIPL (both 2021) cover CII, localisation, consent and cross-border transfers.
- China's penalties: fines (up to RMB 10 M under the amended CSL, RMB 50 M or 5% under the PIPL), suspension, licence revocation; no death penalty in these laws. Didi: 8.026 billion yuan (2022).
- (ئەمریکا، ١٩٩٦) ئەو دەپارێزێت کە لای دامەزراوە گیراوەکان و هاوبەشە بازرگانییەکانیانە، لە ڕێگەی ڕێساکانی ، و .
- : تاکەکان لە ماوەی ٦٠ ڕۆژدا ئاگادار بکەرەوە؛ میدیا ئەگەر زیاتر لە ٥٠٠ لە یەک ویلایەت بن؛ HHS یەکسەر بۆ ٥٠٠ یان زیاتر، ساڵانە بۆ کەمتر.
- سزاکانی چوار ئاستی هەڵە پەیڕەو دەکەن و بەپێی هەڵاوسان ڕێک دەخرێن: ئەمڕۆ ١٤٥ تا ٧٣،٠١١ دۆلار بۆ هەر سەرپێچییەک، تا ٢،١٩٠،٢٩٤ دۆلار لە ساڵێکدا؛ Anthem لە ٢٠١٨دا ١٦ ملیۆن دۆلاری دا.
- چین: یاسای (٢٠١٧، هەموارکراو لە ١ی کانوونی دووەمی ٢٠٢٦ەوە)، یاسای و PIPL (هەردووکیان ٢٠٢١) CII، ، و گواستنەوەی دەرەوەی سنوور دەگرنەوە.
- سزاکانی چین: سزای دارایی (تا ١٠ ملیۆن یوان بەپێی CSLـی هەموارکراو، ٥٠ ملیۆن یوان یان ٥٪ بەپێی PIPL)، ڕاگرتن، هەڵوەشاندنەوەی مۆڵەت؛ لەم یاسایانەدا لەسێدارەدان نییە. دیدی: ٨.٠٢٦ ملیار یوان (٢٠٢٢).
What are HIPAA's three rules?سێ ڕێساکەی HIPAA چین؟
Privacy Rule, Security Rule (administrative, physical, technical safeguards), Breach Notification Rule.
ڕێسای ، ڕێسای (پاراستنی کارگێڕی، فیزیکی، تەکنیکی)، ڕێسای .
Who is a business associate? Give an example.هاوبەشی بازرگانی کێیە؟ نموونەیەک بهێنەرەوە.
Someone who handles PHI for a covered entity, e.g. a billing company or a cloud provider.
کەسێک یان کۆمپانیایەک کە بۆ دامەزراوەیەکی گیراو مامەڵە لەگەڵ PHI دەکات، بۆ نموونە کۆمپانیایەکی پسوولە یان دابینکەرێکی هەوری.
Which Chinese law requires CII operators to store data in China?کام یاسای چین داوا لە بەڕێوەبەرانی CII دەکات دراوە لە چین هەڵبگرن؟
The Cybersecurity Law, Article 37 (the PIPL adds very large processors).
یاسای ، ماددەی ٣٧ (PIPL کۆمپانیا زۆر گەورەکانیش زیاد دەکات).
When did the amended Cybersecurity Law come into force?یاسای ئاسایشی سایبەری هەموارکراو کەی جێبەجێ بوو؟
On 1 January 2026 (adopted 28 October 2025).
لە ١ی کانوونی دووەمی ٢٠٢٦ (لە ٢٨ی تشرینی یەکەمی ٢٠٢٥ پەسەند کرا).
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Computer-Crime Laws: Budapest, the CFAA, the UK and the Law at Homeیاساکانی تاوانی سایبەری: بوداپێست، CFAA، بەریتانیا و یاسا لە وڵاتی خۆمان
Related lecturesوانە پەیوەندیدارەکان
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- eCFR 45 CFR 160.103: definitions (covered entity, business associate, protected health information)
- eCFR 45 CFR 164.306: Security standards, general rules (confidentiality, integrity, availability of ePHI)
- eCFR 45 CFR 164.402: definitions (unsecured protected health information)
- eCFR 45 CFR 164.404, 164.406, 164.408: notification to individuals, media and the Secretary
- Federal Register 91 FR 3665 (28 January 2026): HHS Annual Civil Monetary Penalties Inflation Adjustment
- Federal Register (21 October 2026): No Adjustment to HHS Civil Monetary Penalty Amounts for 2026
- Federal Register 84 FR 18151 (30 April 2019): Notification of Enforcement Discretion Regarding HIPAA Civil Money Penalties
- HIPAA Journal: HHS confirms HIPAA penalties will not be adjusted for inflation this year (22 October 2026)
- Cleary Gottlieb: HHS settles with Anthem for record $16 million (October 2018)
- Bitdefender Business Insights: Anthem agrees to $16 million settlement (spear phishing, corrective action plan)
- DigiChina (Stanford): Translation, Cybersecurity Law of the PRC (effective 1 June 2017)
- DigiChina (Stanford): Translation, Data Security Law of the PRC
- DigiChina (Stanford): Translation, Personal Information Protection Law of the PRC (effective 1 November 2021)
- China Briefing: China's Cybersecurity Law amendment (adopted 28 October 2025, effective 1 January 2026)
- Latham & Watkins: China finalises exemptions to cross-border data transfer rules (CAC Provisions of 22 March 2024)
- Al Jazeera: China fines Didi $1.2bn for violating data security laws (21 July 2022)
- Jiemian: Didi reopens new user registration after more than a year of rectification
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.