Chapterبەش 4 · Lectureوانە 4.2
Malware Today: Infostealers, Banking Trojans, RATs, Cryptojacking and Moreنەرمەواڵەی زیانبەخشی ئەمڕۆ: نەرمەواڵە زانیاریدزەکان، ئەسپەکانی ترۆیای بانکی، RAT، کریپتۆجاکینگ و زیاتر
The malware types that grew fastest by 2024 — infostealers, malvertising, mobile banking Trojans, RATs, cryptojacking, AI-assisted attacks, fleeceware and IoT botnets — plus fileless and supply-chain attacks, each with a verified example and the defences that break it.
ئەو جۆرانەی کە تا ٢٠٢٤ خێراترین گەشەیان کرد — ، ، بانکی لەسەر مۆبایل، RAT، ، هێرشی یارمەتیدراو بە ، و — لەگەڵ هێرشی بێفایل و ، هەریەکەیان بە نموونەیەکی پشتڕاستکراو و ئەو بەرگرییانەی دەیشکێنن.
What you will learnچی فێر دەبیت
- Explain how today's malware works as a criminal business.
- Describe infostealers, malvertising, mobile banking Trojans, RATs, cryptojacking, AI-assisted attacks, fleeceware and IoT attacks, with a verified example of each.
- Explain why stolen session cookies can bypass MFA and what to do after an infection.
- Explain fileless and supply-chain attacks and how defenders detect and limit them.
- Check malware 'facts' against reliable sources and correct outdated claims.
- ڕوونی بکەیتەوە ئەمڕۆ چۆن وەک بازرگانییەکی تاوانکاری کار دەکات.
- ، ، بانکی، RAT، ، هێرشی یارمەتیدراو بە ، و بۆ سەر وەسف بکەیت، بە نموونەیەکی پشتڕاستکراو بۆ هەریەکەیان.
- ڕوونی بکەیتەوە بۆچی دزراو دەتوانێت لە تێبپەڕێت و دوای تووشبوون چی بکرێت.
- هێرشی بێفایل و ڕوون بکەیتەوە و بەرگریکاران چۆن دەیاندۆزنەوە و سنووردارییان دەکەن.
- «ڕاستییەکانی» لەگەڵ سەرچاوە متمانەپێکراوەکان بەراورد بکەیت و بانگەشە کۆنەکان ڕاست بکەیتەوە.
Malware today is a businessنەرمەواڵەی زیانبەخشی ئەمڕۆ بازرگانییە
The classic types from Malware are still around, but how criminals use them has changed. Today malware is an industry: one group writes a stealer and rents it out, another buys the stolen passwords, a third uses them to break into companies and sells that access to a ransomware gang. Each step is a product with a price. The course notes describe eight types that grew strongly by late 2024; this lesson checks every example against reliable reports and adds two more ways attackers work today: fileless attacks and supply-chain attacks.
جۆرە کلاسیکەکانی نەرمەواڵەی زیانبەخش هێشتا هەن، بەڵام شێوازی بەکارهێنانیان لە لایەن تاوانبارانەوە گۆڕاوە. ئەمڕۆ پیشەسازییەکە: گرووپێک دزێک دەنووسێت و بە کرێی دەدات، گرووپێکی تر دزراوەکان دەکڕێت، سێیەمیان بەکاریان دەهێنێت بۆ دزەکردن بۆ ناو کۆمپانیاکان و ئەو دەستڕاگەیشتنە بە دەستەیەکی دەفرۆشێت. هەر هەنگاوێک بەرهەمێکە بە نرخێک. تێبینییەکانی کۆرسەکە هەشت جۆر وەسف دەکەن کە تا کۆتایی ٢٠٢٤ بە توندی گەشەیان کرد؛ ئەم وانەیە هەموو نموونەیەک لەگەڵ ڕاپۆرتە متمانەپێکراوەکان بەراورد دەکات و دوو ڕێگای تری کارکردنی ئەمڕۆ زیاد دەکات: هێرشی بێفایل و .
Infostealers: your saved passwords, packed and soldنەرمەواڵە زانیاریدزەکان: تێپەڕەوشە هەڵگیراوەکانت، پێچراو و فرۆشراو
An infostealer is malware made to copy sensitive information from an infected device: passwords saved in the browser, cookies that keep you logged in, card details, crypto wallets, files. It usually arrives through malicious ads, fake or 'cracked' software and infected websites. In seconds it packs everything into a file (criminals call it a log) and sends it away. Logs are sold in bulk on criminal forums or used directly for the next attack. A stolen session cookie is especially dangerous: it can let an attacker into an account without the password or the second factor, because the website thinks the session is still yours.
کە بۆ کۆپیکردنی زانیاریی هەستیار لە ئامێرێکی تووشبوو دروست کراوە: هەڵگیراوەکان لە ، ئەو لە ژوورەوە دەتهێڵنەوە، زانیاریی کارت، جزدانی ، . زۆرجار لە ڕێگەی ، ساختە یان «شکێنراو» و تووشبووەکانەوە دێت. لە چەند چرکەیەکدا هەموو شتێک لە دەپێچێت (تاوانباران پێی دەڵێن لۆگ) و دەینێرێت. ئەم لۆگانە بە کۆمەڵ لە مەکۆ تاوانکارییەکاندا دەفرۆشرێن یان ڕاستەوخۆ بۆ داهاتوو بەکار دەهێنرێن. دزراو بە تایبەتی مەترسیدارە: دەتوانێت بەبێ یان هۆکاری دووەم بخاتە ناو هەژمارێکەوە، چونکە وا دەزانێت هێشتا هی تۆیە.
made to copy saved , , card details and other personal data from an infected device and send them to criminals, who sell them or use them for further attacks.
جۆرێکە لە کە بۆ کۆپیکردنی تێپەڕەوشە هەڵگیراوەکان، ، زانیاریی کارتی بانکی و زانیاریی کەسیی تر لە ئامێرێکی تووشبوو دروست کراوە و دەیاننێرێت بۆ تاوانباران، کە دەیانفرۆشن یان بۆ هێرشی تر بەکاریان دەهێنن.
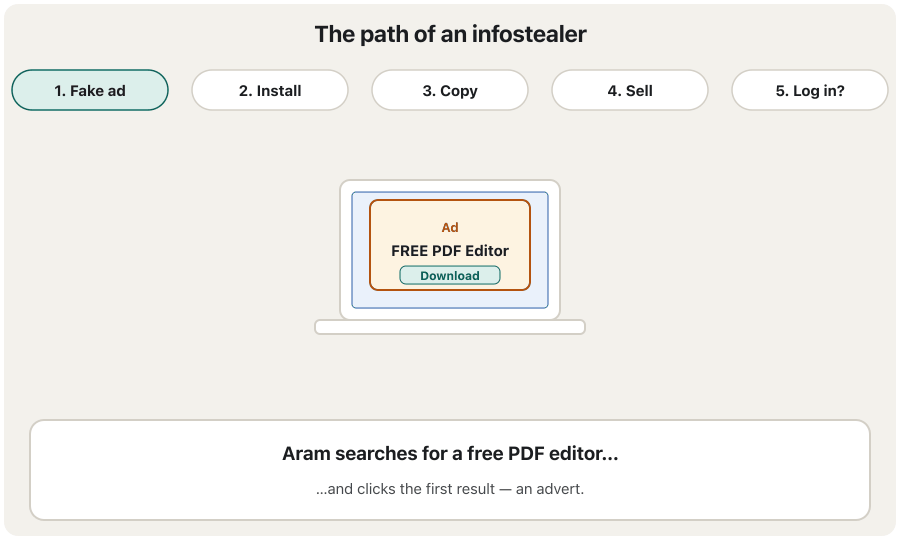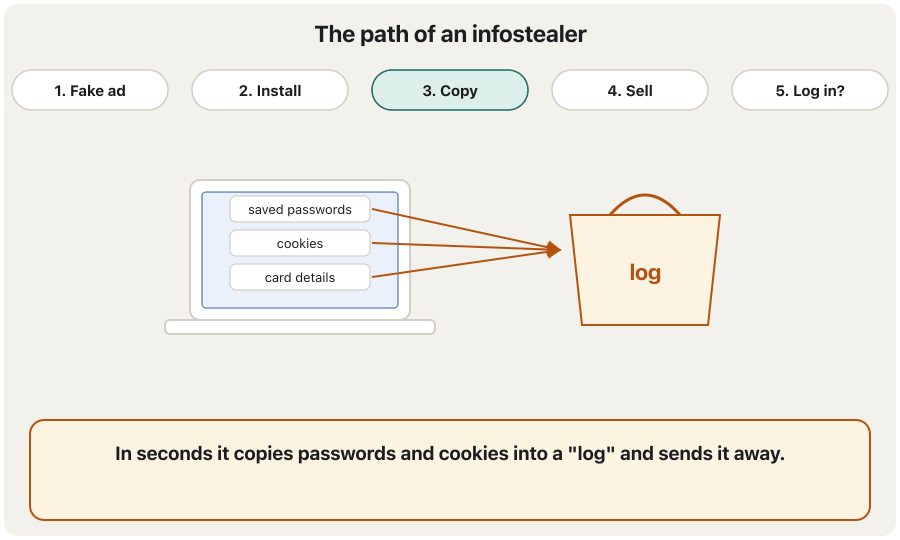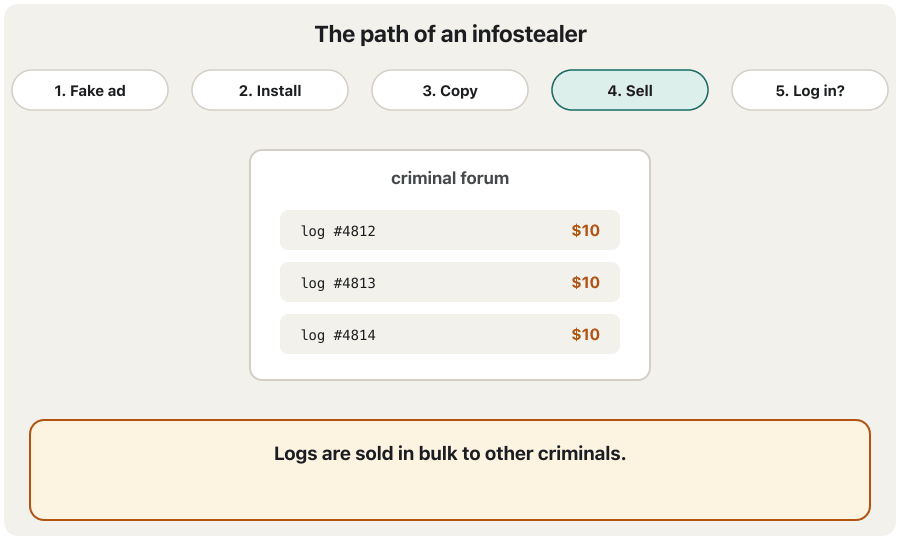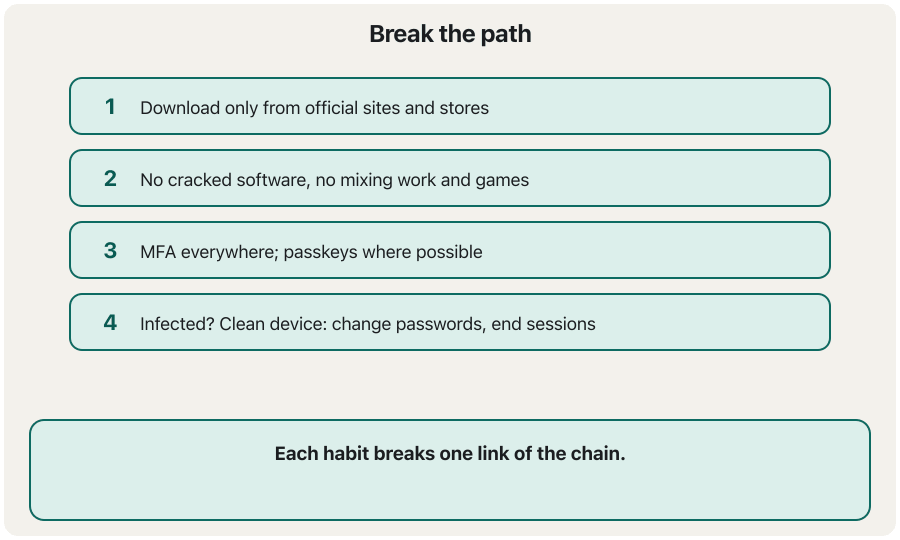
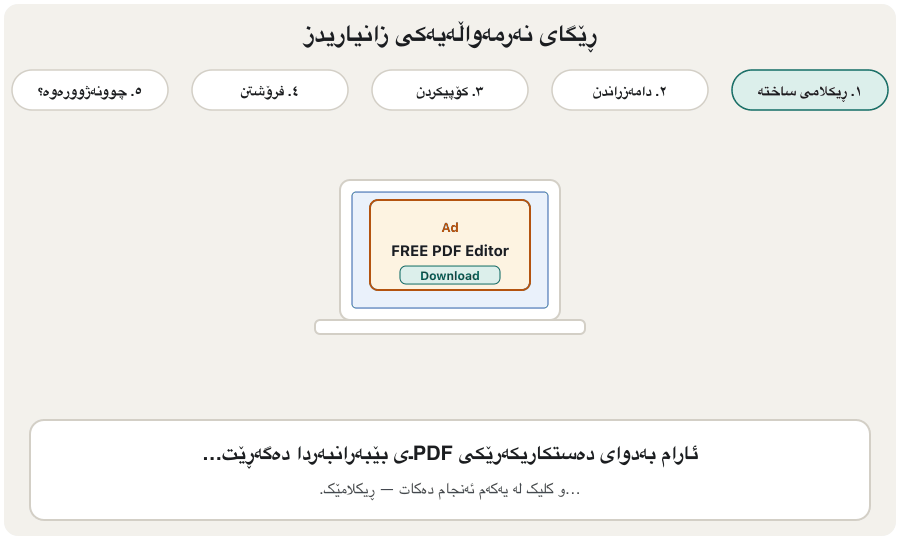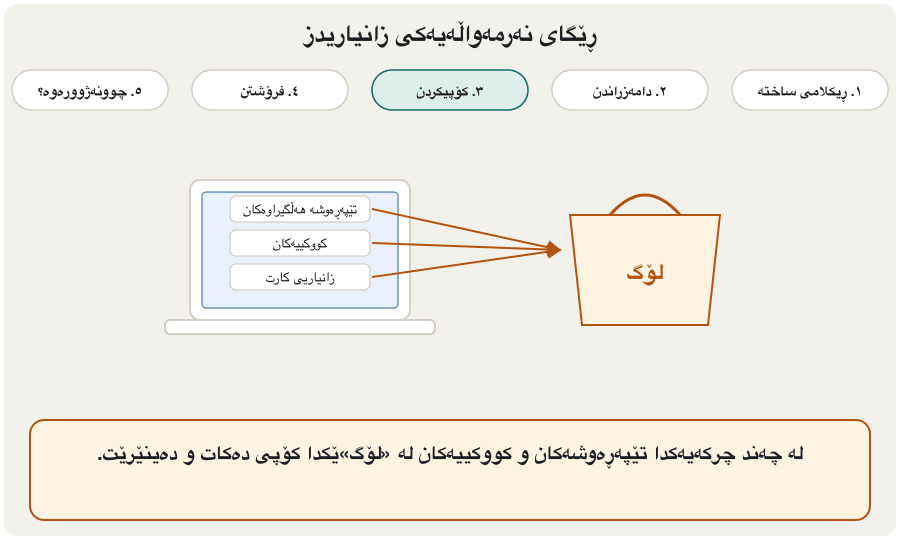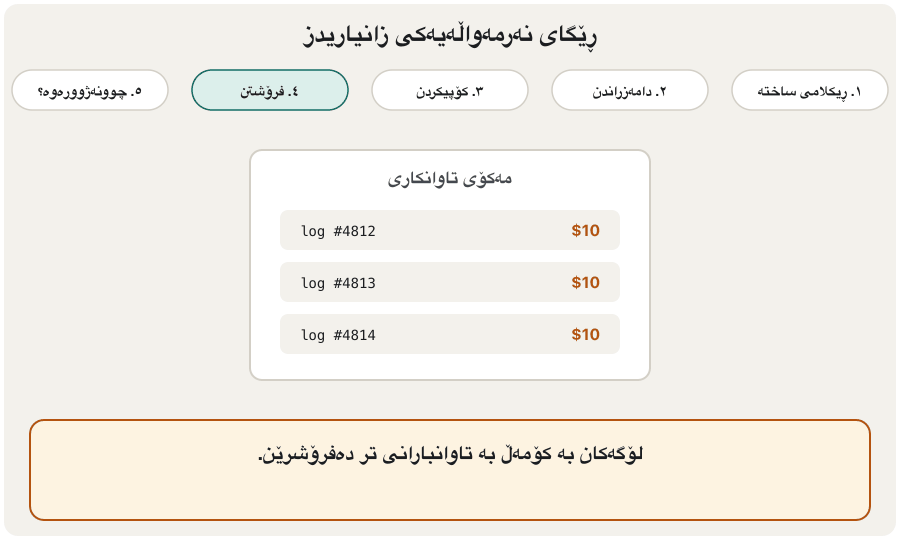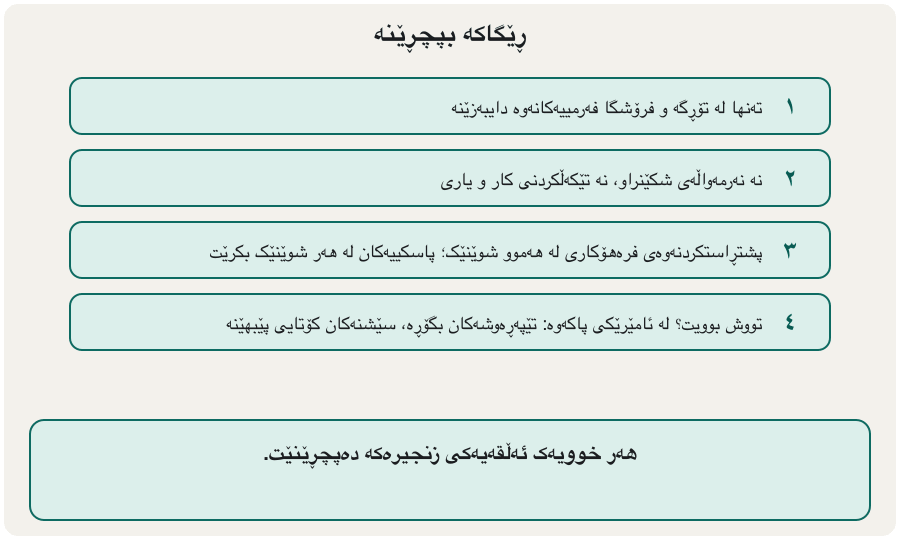
Infostealers: your saved passwords, packed and soldنەرمەواڵە زانیاریدزەکان: تێپەڕەوشە هەڵگیراوەکانت، پێچراو و فرۆشراو
A documented case: Snowflake customers (2024)دۆسیەیەکی بەڵگەدار: کڕیارانی Snowflake (٢٠٢٤)
A well-documented case: Snowflake customers (2024). In mid-2024 attackers logged in to the cloud data accounts of about 165 organisations that used the Snowflake platform and stole large amounts of data. Mandiant found that the platform itself had not been hacked: the attackers used usernames and passwords stolen by infostealers — some infections went back to 2020 — and the accounts had no multi-factor authentication, passwords that had never been changed, and no limits on where logins could come from.
دۆسیەیەکی بە باشی بەڵگەدار: کڕیارانی Snowflake (٢٠٢٤). لە ناوەڕاستی ٢٠٢٤دا چوونە ناو هەژمارەکانی هەوریی نزیکەی ١٦٥ ڕێکخراو کە پلاتفۆرمی Snowflakeـیان بەکار دەهێنا و بڕێکی زۆر دزی. Mandiant دۆزییەوە کە خودی پلاتفۆرمەکە هاک نەکرابوو: و بەکار هێنا کە دزیبوویانن — هەندێک تووشبوون دەگەڕانەوە بۆ ٢٠٢٠ — و هەژمارەکان نەبوو، هەرگیز نەگۆڕدرابوون و هیچ سنوورێک نەبوو بۆ ئەوەی لە کوێوە دەتوانرێت بچیتە ژوورەوە.
Infostealers: your saved passwords, packed and soldنەرمەواڵە زانیاریدزەکان: تێپەڕەوشە هەڵگیراوەکانت، پێچراو و فرۆشراو
Defending against infostealersبەرگری دژی نەرمەواڵە زانیاریدزەکان
- Never install cracked software or 'free' tools from ads. Type the official website yourself or use an official store.
- Use MFA everywhere, and passkeys where possible, so a stolen password alone does not open the account.
- Use a password manager rather than saving passwords in a browser on shared or old computers.
- Do not mix work and personal use on the same laptop — in the Snowflake case, contractors' laptops used for games and pirated software were infected.
- After an infection, change all saved passwords from a clean device and sign out of all sessions, because stolen cookies stay valid until the session ends.
- هەرگیز شکێنراو یان ئامرازی «بێبەرانبەر» لە ڕیکلامەکانەوە دامەمەزرێنە. خۆت فەرمی بنووسە یان فرۆشگایەکی فەرمی بەکار بهێنە.
- پشتڕاستکردنەوەی فرەهۆکاری لە هەموو شوێنێک بەکار بهێنە و پاسکییەکان لە هەر شوێنێک بکرێت، بۆ ئەوەی دزراو بە تەنها هەژمارەکە نەکاتەوە.
- بەڕێوەبەرێکی تێپەڕەوشە بەکار بهێنە لە جیاتی هەڵگرتنی لە لەسەر هاوبەش یان کۆن.
- کار و بەکارهێنانی کەسی تێکەڵ مەکە لەسەر هەمان — لە دۆسیەی Snowflakeـدا گرێبەستکاران کە بۆ یاری و دزراو بەکار دەهێنران تووش بوون.
- دوای تووشبوون، هەموو هەڵگیراوەکان لە ئامێرێکی پاکەوە بگۆڕە و لە هەموو بچۆ دەرەوە، چونکە دزراوەکان تا کۆتایی کار دەکەن.
After an infostealer: stay calm, list key accounts, replace cards, sign out of every session from a clean device, change passwords, wipe the PC.
دوای : ئارام بە، لیستی بنووسە، کارتە بانکییەکانت بگۆڕە، لە ئامێرێکی پاکەوە لە هەموو بچۆ دەرەوە، بگۆڕە و بسڕەوە.
Plays 0:00-6:42; stops before the dark-web search tool (the sponsor).
لە 0:00 تا 6:42 پەخش دەبێت؛ پێش ئامرازی گەڕان لە وێبی تاریک (ڕیکلامی سپۆنسەرەکە) ڕادەوەستێت.
Malvertising: malware in the advertsڕیکلامی زیانبەخش: نەرمەواڵەی زیانبەخش لەناو ڕیکلامەکاندا
Malvertising (malicious advertising) hides harmful code or links inside online adverts, often bought on real advertising networks. A typical trick: you search for a free program, and the first result is an advert that looks exactly like the official website but leads to a fake copy with malware — very often an infostealer. Some malicious ads try to redirect you to phishing pages. Because the ads appear on trusted search engines and news sites, careful people are fooled too.
کۆدی زیانبەخش یان لەناو ڕیکلامە ئۆنلاینەکاندا دەشارێتەوە، کە زۆرجار لە تۆڕە ڕاستەقینەکانی ڕیکلامدا کڕدراون. فێڵێکی باو: بەدوای بەرنامەیەکی بێبەرانبەردا دەگەڕێیت و یەکەم ئەنجام ڕیکلامێکە کە ڕێک وەک فەرمی دەردەکەوێت بەڵام بەرەو کۆپییەکی ساختە بە دەتبات — زۆرجار . هەندێک هەوڵ دەدەن بەرەو پەڕەکانی بتگوازنەوە. لەبەر ئەوەی ڕیکلامەکان لەسەر بزوێنەرە گەڕانە متمانەپێکراوەکان و هەواڵ دەردەکەون، خەڵکی وریاش فریو دەخۆن.
Hiding or links to fake websites inside online adverts, sometimes on trusted websites or in search results, so that people who click on the advert, or even just see it, are attacked.
شاردنەوەی یان بەستەری تۆڕگەی ساختەیە لە ناو ڕیکلامە ئۆنلاینەکاندا، هەندێک جار لەسەر تۆڕگەی متمانەپێکراو یان لە ئەنجامی گەڕاندا، بۆ ئەوەی هێرش بکرێتە سەر ئەو کەسانەی کلیک لە ڕیکلامەکە دەکەن یان تەنانەت تەنیا دەیبینن.
Malwarebytes reported that malvertising 'made a comeback' in 2023. The brands most often copied in fake download ads included Amazon, Notepad++ and TradingView, and the commonest malware it found that year were stealers such as Vidar and RedLine.
Malwarebytes ڕاپۆرتی دا کە لە ٢٠٢٣دا «گەڕایەوە». ئەو براندانەی زۆرتر لە ڕیکلامی ساختەی کۆپی کران Amazon، Notepad++ و TradingView بوون و باوترین کە ئەو ساڵە دۆزییەوە دزەکانی وەک Vidar و RedLine بوون.
Mobile banking Trojansئەسپەکانی ترۆیای بانکی لەسەر مۆبایل
A mobile banking Trojan pretends to be a normal app — a browser update, a video player, a 'security' tool — and, once installed, steals banking logins or takes over the phone to move money. Most of them do not come from the official store: a message or a website persuades the victim to download an installation file and side-load it. Then the app asks for Accessibility permission. This Android feature exists to help people with disabilities, but it lets an app read the screen and tap buttons — in practice, full control of the phone.
بانکی لەسەر مۆبایل خۆی وەک ئاسایی پیشان دەدات — ، لێدەری ڤیدیۆ، ئامرازێکی «» — و کاتێک دامەزرا، بانکی دەدزێت یان مۆبایلەکە دەگرێتە دەست بۆ گواستنەوەی پارە. زۆربەیان لە فرۆشگا فەرمییەکەوە نایەن: نامەیەک یان قوربانییەکە قایل دەکات دامەزراندن دابەزێنێت و لە دەرەوەی فرۆشگا دایبمەزرێنێت. پاشان داوای مۆڵەتی Accessibility دەکات. ئەم تایبەتمەندییەی Android بۆ یارمەتیدانی کەسانی خاوەن پێداویستیی تایبەت هەیە، بەڵام ڕێگە بە دەدات شاشەکە بخوێنێتەوە و دوگمەکان دابگرێت — لە ڕاستیدا کۆنترۆڵی تەواوی مۆبایلەکە.
Mobile banking Trojansئەسپەکانی ترۆیای بانکی لەسەر مۆبایل
Example: ToxicPanda (2024)نموونە: ToxicPanda (٢٠٢٤)
Example: ToxicPanda (identified in late October 2024). Researchers at the Italian company Cleafy found this Android banking Trojan on more than 1,500 devices — over half in Italy, the rest mainly in Portugal, Spain and parts of Latin America. Victims were tricked into side-loading it. It abused Accessibility services, read the one-time codes banks send by SMS so it could get around two-factor authentication, and let criminals control the phone remotely to make transfers from the victim's own device, which makes the fraud harder for banks to notice.
نموونە: ToxicPanda (لە کۆتایی تشرینی یەکەمی ٢٠٢٤دا ناسرایەوە). توێژەرانی کۆمپانیای ئیتاڵیی Cleafy ئەم بانکیی Androidـەیان لەسەر زیاتر لە ١٬٥٠٠ ئامێر دۆزییەوە — زیاتر لە نیوەیان لە ئیتاڵیا، ئەوانی تر بە شێوەیەکی سەرەکی لە پورتوگال، ئیسپانیا و بەشێک لە ئەمریکای لاتین. قوربانییەکان فریو دران بۆ ئەوەی لە دەرەوەی فرۆشگا دایبمەزرێنن. خزمەتگوزارییەکانی Accessibilityـی خراپ بەکار هێنا، ناو بانکەکانی دەخوێندەوە بۆ ئەوەی لە تێبپەڕێت و ڕێگەی بە تاوانباران دەدا لە دوورەوە مۆبایلەکە کۆنترۆڵ بکەن بۆ گواستنەوەی پارە لە ئامێری خودی قوربانییەکەوە، کە دۆزینەوەی فێڵەکە بۆ بانکەکان قورستر دەکات.
Remote access Trojans (RATs)ئەسپەکانی ترۆیای دەستڕاگەیشتن لە دوورەوە (RAT)
A remote access Trojan (RAT) gives an attacker control of an infected computer from far away, as if they were sitting at it: they can browse files, run programs, record the screen and switch on the camera. RATs are a favourite tool of cyber-espionage — secretly stealing valuable information such as research, plans or private communication over computer networks.
(RAT) کۆنترۆڵی تووشبوو لە دوورەوە دەداتە ، وەک ئەوەی لە پێشیەوە دانیشتبێت: دەتوانێت بەناو بگەڕێت، بەرنامە کار پێبکات، شاشەکە تۆمار بکات و کامێراکە هەڵبکات. RATـەکان ئامرازی دڵخوازی — دزینی زانیاریی بەنرخ بە نهێنی، وەک توێژینەوە، پلان یان پەیوەندیی تایبەتی لە ڕێگەی .
A that secretly gives an attacker full to an infected computer or phone, so they can see the screen, copy files, record with the camera or install more malware.
کە بە نهێنی بە دەدات بۆ کۆمپیوتەر یان مۆبایلێکی تووشبوو، بە شێوەیەکی تەواو، بۆ ئەوەی شاشەکە ببینێت، فایلەکان کۆپی بکات، بە کامێراکە تۆمار بکات یان زیاتر دابمەزرێنێت.
Remote access Trojans (RATs)ئەسپەکانی ترۆیای دەستڕاگەیشتن لە دوورەوە (RAT)
Example: SugarGh0st (2023–2024)نموونە: SugarGh0st (٢٠٢٣–٢٠٢٤)
Example: SugarGh0st. SugarGh0st is a customised version of an older RAT called Gh0st RAT. Cisco Talos first described it in November 2023, when it was used against targets in Central and East Asia. In May 2024 Proofpoint reported a small campaign that sent it, inside a zip file attached to an AI-themed e-mail, to fewer than 10 people linked to one leading US artificial-intelligence organisation. Proofpoint judged that the goal was probably non-public information about generative AI, and it could not say with high confidence who was behind it.
نموونە: SugarGh0st. SugarGh0st وەشانێکی گۆڕدراوی RATێکی کۆنترە بە ناوی Gh0st RAT. Cisco Talos یەکەم جار لە تشرینی دووەمی ٢٠٢٣دا وەسفی کرد، کاتێک دژی ئامانجەکان لە ئاسیای ناوەڕاست و ڕۆژهەڵات بەکار دەهات. لە ئایاری ٢٠٢٤دا Proofpoint ڕاپۆرتی هەڵمەتێکی بچووکی دا کە ئەوی، لەناو zip کە بە دەربارەی هاوپێچ کرابوو، بۆ کەمتر لە ١٠ کەس نارد کە پەیوەندییان بە ڕێکخراوێکی پێشەنگی ئەمریکاوە هەبوو. Proofpoint بڕیاری دا کە ئامانجەکە ڕەنگە زانیاریی بڵاونەکراوە بووبێت دەربارەی و نەیتوانی بە دڵنیاییەکی بەرز بڵێت کێ لە پشتیەوە بوو.
Cryptojacking: your electricity, their moneyکریپتۆجاکینگ: کارەبای تۆ، پارەی ئەوان
Cryptojacking malware secretly uses someone else's computer, phone or cloud server to mine cryptocurrency — to do the heavy calculations that are rewarded with new coins. The attacker keeps the coins; the victim pays with slow devices, hot processors, high electricity or cloud bills and worn-out hardware. It can hide in a program, in a hacked server, or as a script on a website that mines while the page is open.
بە نهێنی ، مۆبایل یان هەوریی کەسێکی تر بەکار دەهێنێت بۆ دەرهێنانی — بۆ ئەنجامدانی ئەو هەژمارە قورسانەی کە بە پارەی نوێ پاداشت دەدرێنەوە. پارەکان بۆ خۆی دەبات؛ قوربانییەکە بە ئامێری خاو، پرۆسێسەری گەرم، پسوولەی کارەبا یان هەوری بەرز و فەرسوود باجەکەی دەدات. دەتوانێت لە بەرنامەیەکدا، لە هاککراودا یان وەک لەسەر خۆی بشارێتەوە کە تا پەڕەکە کراوە بێت دەردەهێنێت.
Secretly using someone else's computer, phone or cloud server to mine for the attacker. The victim pays with slow devices, high electricity bills and worn-out hardware.
بەکارهێنانی نهێنیی کۆمپیوتەر، مۆبایل یان هەوریی کەسێکی ترە بۆ دەرهێنانی بۆ . قوربانییەکە بە ئامێری خاو، پسوولەی کارەبای زۆر و فەرسوودە باجەکەی دەدات.
The security company SonicWall counted 1.1 billion cryptojacking attempts in 2023 — a record, up 659% on the year before. So the notes' 'over 1 billion by the end of 2023' is right. But the trend is not simply 'rising with Bitcoin': in the first half of 2024 SonicWall saw cryptojacking fall by 60%, as criminals moved to other ways of making money.
کۆمپانیای SonicWall لە ٢٠٢٣دا ١٫١ ملیار هەوڵی ژمارد — ڕیکۆردێک، ٦٥٩٪ زیاتر لە ساڵی پێشوو. کەواتە «زیاتر لە ١ ملیار تا کۆتایی ٢٠٢٣»ی تێبینییەکان ڕاستە. بەڵام ڕەوتەکە تەنها «بەرزبوونەوە لەگەڵ Bitcoin» نییە: لە نیوەی یەکەمی ٢٠٢٤دا SonicWall بینی ٦٠٪ کەم بووەوە، چونکە تاوانباران ڕوویان کردە ڕێگای تری پارە پەیداکردن.
- Signs: fans running loudly, a hot device, CPU near 100% when nothing is open, a sudden jump in the cloud bill.
- Defences: patch servers (attackers often enter through old holes), watch CPU use and set cloud billing alerts, use EDR, and block mining scripts in the browser.
- نیشانەکان: پانکەکان بە دەنگی بەرز کار دەکەن، ئامێرێکی گەرم، نزیکەی ١٠٠٪ کاتێک هیچ شتێک کراوە نییە، بەرزبوونەوەی لەناکاوی پسوولەی هەوری.
- بەرگرییەکان: بکە ( زۆرجار لە ڕێگەی کونە کۆنەکانەوە دێنە ژوورەوە)، چاودێریی بەکارهێنانی بکە و ئاگادارکەرەوەی پسوولەی هەوری دابنێ، بەکار بهێنە و دەرهێنان لە ڕابگرە.
AI-powered malware and AI-written phishingنەرمەواڵەی زیانبەخشی بە هێزی ژیریی دەستکرد و فیشینگی نووسراو بە ژیریی دەستکرد
Attackers use AI just as defenders do. The course describes AI-powered malware that can change its behaviour to avoid detection, and AI-generated content that makes phishing and social engineering more convincing. Today the clearest effect is on phishing: AI writes fluent, personal messages in any language with no spelling mistakes, so the old advice 'look for bad grammar' no longer works. Deepfake voices and videos are the same idea applied to calls (see AI ethics).
وەک بەرگریکاران بەکار دەهێنن. کۆرسەکە بە هێزی وەسف دەکات کە دەتوانێت ڕەفتاری بگۆڕێت بۆ ئەوەی نەدۆزرێتەوە، هەروەها ناوەڕۆکی دروستکراو بە کە و باوەڕپێکراوتر دەکات. ئەمڕۆ ڕوونترین کاریگەری لەسەر فیشینگ دەبینرێت: نامەی ڕەوان و کەسی بە هەر زمانێک بێ هەڵەی ڕێنووس دەنووسێت، بۆیە ئامۆژگاریی کۆن «بەدوای ڕێزمانی خراپدا بگەڕێ» ئیتر کار ناکات. دەنگ و ڤیدیۆی هەمان بیرۆکەیە کە بۆ پەیوەندییەکان بەکار دێت (بڕوانە ئەخلاقی ژیریی دەستکرد).
AI-powered malware and AI-written phishingنەرمەواڵەی زیانبەخشی بە هێزی ژیریی دەستکرد و فیشینگی نووسراو بە ژیریی دەستکرد
Malware that asks an AI for helpنەرمەواڵەی زیانبەخش کە داوای یارمەتی لە ژیریی دەستکرد دەکات
Evidence for malware that uses AI while running is newer. In November 2025 Google's threat-intelligence team reported the first malware families it had seen asking an AI model, during an attack, to write new commands or to rewrite their own code to avoid detection. Most were still experimental. ENISA's Threat Landscape 2026 expects AI models to be used more and more to support attacks. The defences have not changed: patching, EDR that watches behaviour, MFA, and people who verify unusual requests.
بەڵگە بۆ کە لە کاتی کارکردندا بەکار دەهێنێت نوێترە. لە تشرینی دووەمی ٢٠٢٥دا تیمی زانیاریی Google ڕاپۆرتی یەکەم خێزانەکانی دا کە بینیبوونی لە کاتی داوا لە دەکەن فەرمانی نوێ بنووسێت یان کۆدەکەی خۆیان دووبارە بنووسێتەوە بۆ ئەوەی نەدۆزرێنەوە. زۆربەیان هێشتا لە قۆناغی تاقیکردنەوەدا بوون. ڕاپۆرتی دیمەنی هەڕەشەکانی ENISA ٢٠٢٦ چاوەڕێ دەکات زیاتر و زیاتر بۆ پشتگیریکردنی بەکار بهێنرێن. بەرگرییەکان نەگۆڕاون: ، کە چاودێریی ڕەفتار دەکات، و خەڵکێک کە داواکارییە نائاساییەکان پشتڕاست دەکەنەوە.
Fleeceware: legal-looking, expensive tricksfleeceware: فێڵی گران کە یاسایی دەردەکەون
Fleeceware is an app that charges far too much for very little — a QR-code reader, a calculator, a photo filter. It offers a short 'free trial' that quietly turns into an expensive weekly or yearly subscription. Many users delete the app and think the trial is over, but deleting an app does not cancel a subscription. The name comes from to fleece: to shear a sheep's wool, and in everyday English to take someone's money by overcharging them.
کە پارەیەکی زۆر لە بەرامبەر شتێکی زۆر کەمدا وەردەگرێت — خوێنەرەوەی ، ، فلتەری وێنە. «تاقیکردنەوەیەکی بێبەرانبەر»ـی کورت پێشکەش دەکات کە بە بێدەنگی دەبێتە بەشداربوونێکی گرانی هەفتانە یان ساڵانە. زۆر بەکارهێنەر دەسڕنەوە و وا دەزانن تاقیکردنەوەکە تەواو بووە، بەڵام سڕینەوەی بەشداربوون هەڵناوەشێنێتەوە. ناوەکە لە to fleeceـەوە هاتووە: بڕینی خوری مەڕ و لە ئینگلیزیی ڕۆژانەدا بردنی پارەی کەسێک بە نرخی زیادە.
An app that tricks users into an expensive subscription for something simple, for example a free trial that turns into a large weekly payment unless it is cancelled. It is often legal but deceptive.
ئەپێکە کە بەکارهێنەران فریو دەدات بۆ بەشداربوون بە پارەیەکی زۆر لە بەرامبەر شتێکی سادەدا، بۆ نموونە تاقیکردنەوەیەکی بێبەرانبەر کە ئەگەر هەڵنەوەشێنرێتەوە دەبێتە پارەدانێکی گەورەی هەفتانە. زۆرجار یاساییە بەڵام فریودەرە.
Attacks on Internet of Things devicesهێرشەکان بۆ سەر ئامێرەکانی ئینتەرنێتی شتەکان
Internet of Things (IoT) devices — cameras, routers, smart TVs, video recorders, even door bells — are small computers that are often forgotten. Many ship with a default password that the owner never changes, and many never get updates. Attackers scan the Internet for them, log in with lists of factory passwords, and take them over to spy, to reach the rest of the home or office network, or to build a botnet.
ئامێرەکانی — کامێرا، ، ، تۆمارکەری ڤیدیۆ، تەنانەت زەنگی دەرگا — بچووکن کە زۆرجار لەبیر دەکرێن. زۆریان لەگەڵ دێن کە خاوەنەکەی هەرگیز نایگۆڕێت و زۆریان هەرگیز وەرناگرن. بەدوایاندا لە دەگەڕێن، بە لیستی کارگە دەچنە ژوورەوە و دەیانگرنە دەست بۆ سیخوڕی، بۆ گەیشتن بە بەشەکانی تری ماڵ یان نووسینگە، یان بۆ دروستکردنی .
The factory that a device or program comes with, such as admin. It is often published in manuals and online, so it must be changed before the device is used.
کارگەیە کە ئامێرێک یان بەرنامەیەک لەگەڵیدا دێت، وەک admin. زۆرجار لە ڕێنماییەکان و ئینتەرنێتدا بڵاو کراوەتەوە، بۆیە دەبێت پێش بەکارهێنانی ئامێرەکە بگۆڕدرێت.
Where these devices are used — in homes, schools and whole smart cities — and how to set them up safely is taught in The risks of a smart city and IoT security basics.
ئەم ئامێرانە لە کوێ بەکار دێن — لە ماڵ، قوتابخانە و تەنانەت لە — و چۆن بە سەلامەتی ڕێک دەخرێن لە مەترسییەکانی شارێکی هۆشمەند و بنەماکانی ئاسایشی ئینتەرنێتی شتەکاندا فێر دەکرێت.
Attacks on Internet of Things devicesهێرشەکان بۆ سەر ئامێرەکانی ئینتەرنێتی شتەکان
Mirai: a botnet built from cameras and routersMirai: بۆتنێتێک کە لە کامێرا و ڕێدۆزەکان دروست کرا
Example: Mirai and its variants. Mirai appeared in 2016. It searched the Internet for cameras, routers and video recorders and tried a short list of 62 default username-and-password pairs. With these devices it ran some of the largest DDoS attacks seen at that time: more than 620 Gbit/s against a security journalist's website and at least 1.1 Tbit/s against the French hosting company OVH. Its source code was published at the end of September 2016, so criminals have built many variants since — which is why 'Mirai' still appears in reports years later. Mirai lived only in memory: restarting a device removed it, but the device was infected again within minutes unless its password was changed.
نموونە: Mirai و جۆرە گۆڕدراوەکانی. Mirai لە ٢٠١٦دا دەرکەوت. لە بەدوای کامێرا، و تۆمارکەری ڤیدیۆدا دەگەڕا و لیستێکی کورتی ٦٢ جووت و بنەڕەتی تاقی دەکردەوە. بەم ئامێرانە هەندێک لە گەورەترین ئەو کاتەی ئەنجام دا: زیاتر لە ٦٢٠ گیگابیت لە چرکەیەکدا دژی ڕۆژنامەنووسێکی و بەلایەنی کەمەوە ١٫١ تێرابیت لە چرکەیەکدا دژی کۆمپانیای میوانداریی فەرەنسیی OVH. لە کۆتایی ئەیلوولی ٢٠١٦دا بڵاو کرایەوە، بۆیە تاوانباران لەو کاتەوە زۆر جۆری گۆڕدراویان دروست کردووە — بۆیە «Mirai» ساڵانێک دواتریش لە ڕاپۆرتەکاندا دەردەکەوێت. Mirai تەنها لە دەژیا: دووبارە هەڵکردنەوەی ئامێرەکە لای دەبرد، بەڵام ئامێرەکە لە ماوەی چەند خولەکێکدا دووبارە تووش دەبووەوە مەگەر بگۆڕدرابا.
How Mirai was built: weak default passwords on cameras, routers and baby monitors turned them into zombies for record DDoS attacks.
Mirai چۆن دروست کرا: کامێرا، و ئامێری چاودێریی منداڵ کە نەگۆڕابوو، بوونە زۆمبی بۆ DDoSـی بێوێنە.
Plays 2:26-3:38: Mirai used IoT devices with unchanged default passwords and hit a journalist's website with 620 Gbit/s.
لە 2:26 تا 3:38 پەخش دەبێت: Mirai ئەو ئامێرانەی بەکارهێنا کە نەگۆڕابوو، پاشان بە 620 Gbit/s لە ڕۆژنامەنووسێکی دا.
Fileless malware: living off the landنەرمەواڵەی زیانبەخشی بێفایل: ژیان بە ئامرازی ناوخۆ
Most antivirus looks for bad files. Fileless malware avoids leaving a normal program file on the disk. It runs in memory, or it uses tools that are already part of the operating system — on Windows, for example PowerShell and WMI. Security people call this living off the land: the attacker 'lives' on what the land already offers, so the activity looks like normal administration. Microsoft describes three levels: some threats write no file at all (code sent over the network straight into memory, as with the exploit used by WannaCry); some hide commands in places such as the Windows WMI store; some use a file only as a trigger for scripts.
زۆربەی بەدوای خراپدا دەگەڕێت. خۆی لە بەجێهێشتنی ئاسایی بەرنامە لەسەر دیسک دەپارێزێت. لە کار دەکات، یان ئەو ئامرازانە بەکار دەهێنێت کە پێشتر بەشێکن لە — لەسەر Windows، بۆ نموونە PowerShell و WMI. کەسانی بواری پێی دەڵێن ژیان بە ئامرازی ناوخۆ: بەو شتانە «دەژی» کە سیستەمەکە خۆی پێشکەشی دەکات، بۆیە چالاکییەکە وەک بەڕێوەبردنی ئاسایی دەردەکەوێت. Microsoft سێ ئاست وەسف دەکات: هەندێک هیچ نانووسن (کۆد کە بە ڕاستەوخۆ بۆ ناو دەنێردرێت، وەک ئەو WannaCry بەکاری هێنا)؛ هەندێکیان فەرمانەکان لە شوێنی وەک کۆگای WMIـی Windowsـدا دەشارنەوە؛ هەندێکیان تەنها وەک دەستپێکەری بەکار دەهێنن.
that runs only in memory or through tools already built into the , without saving a normal program file, so that scans files finds it hard to notice.
جۆرێکە لە کە تەنیا لە بیرگەدا یان لە ڕێگەی ئامرازە ئامادەکانی ناو کار دەکات، بێ ئەوەی فایلێکی ئاسایی بەرنامە خەزن بکات، بۆیە کە فایلەکان دەپشکنێت بە قورسی هەستی پێ دەکات.
- Behaviour monitoring and EDR — judge what a process does, not only what file it came from.
- Restrict scripting — allow PowerShell only for administrators, log its use, and block Office macros.
- Application allow-listing — only approved programs and scripts may run.
- Patching — many fileless attacks start with an exploit of an old hole.
- چاودێریی ڕەفتار و — هەڵسەنگاندنی ئەوەی پرۆسەیەک دەیکات، نەک تەنها لە کام هاتووە.
- سنووردارکردنی — PowerShell تەنها بۆ بەڕێوەبەران ڕێگەپێبدە، بەکارهێنانی تۆمار بکە و Office ڕابگرە.
- بۆ بەرنامەکان — تەنها بەرنامە و پەسەندکراوەکان دەتوانن کار بکەن.
- — زۆر هێرشی بێفایل بە کونێکی کۆن دەست پێدەکات.
Supply-chain attacks: poisoning what you trustهێرشەکانی زنجیرەی دابینکردن: ژەهراویکردنی ئەو شتەی متمانەت پێیەتی
In a supply-chain attack the attacker does not attack you directly. They compromise something you already trust — a software company, an update server, an open-source library, a service provider — so that the malware arrives through a normal, signed update. One break-in reaches thousands of customers at once.
لە ڕاستەوخۆ هێرش ناکاتە سەر تۆ. شتێک تێک دەدات کە پێشتر متمانەت پێی هەیە — کۆمپانیایەکی ، ، کتێبخانەیەکی ، دابینکەرێکی خزمەتگوزاری — بۆ ئەوەی لە ڕێگەی ئاسایی و واژووکراوەوە بگات. یەک دزەکردن لە یەک کاتدا دەگاتە هەزاران کڕیار.
An attack on a trusted supplier, such as a software company or a service provider, so that the harm reaches all of its customers, for example through a poisoned .
هێرشێکە بۆ سەر دابینکەرێکی متمانەپێکراو، وەک کۆمپانیایەکی یان دابینکەرێکی خزمەتگوزاری، بۆ ئەوەی زیانەکە بگاتە هەموو کڕیارەکانی، بۆ نموونە لە ڕێگەی ژەهراوییەوە.
- NotPetya (27 June 2017): spread first through an update of a tax-accounting program widely used by businesses in Ukraine, then moved through company networks using the same Windows hole as WannaCry. It looked like ransomware but was really a wiper: the files could not be recovered. Large international companies were hit and estimated global losses were over US$10 billion. The ransomware lesson tells the full story: Ransomware.
- SolarWinds (2020), the best-known supply-chain attack on governments, is taught in SolarWinds (2020): a poisoned update.
- NotPetya (٢٧ی حوزەیرانی ٢٠١٧): سەرەتا لە ڕێگەی بەرنامەیەکی ژمێریاریی باجەوە بڵاو بووەوە کە لە ئۆکرانیا بە فراوانی لە لایەن کۆمپانیاکانەوە بەکار دەهات، پاشان بە بەکارهێنانی هەمان کونی Windows وەک WannaCry بەناو کۆمپانیاکاندا جووڵا. وەک دەردەکەوت بەڵام لە ڕاستیدا بوو: نەدەگەڕێندرانەوە. کۆمپانیای گەورەی نێودەوڵەتی پێکران و زیانی جیهانیی خەمڵێنراو لە ١٠ ملیار دۆلار زیاتر بوو. وانەی هەموو چیرۆکەکە دەگێڕێتەوە: نەرمەواڵەی بارمتەگر.
- SolarWinds (٢٠٢٠)، ناسراوترین بۆ سەر حکوومەتەکان، لە SolarWinds (٢٠٢٠): نوێکردنەوەیەکی ژەهراویدا دەخوێندرێت.
Supply-chain attacks: poisoning what you trustهێرشەکانی زنجیرەی دابینکردن: ژەهراویکردنی ئەو شتەی متمانەت پێیەتی
XZ Utils (2024): a backdoor caught in timeXZ Utils (٢٠٢٤): پشتەدەرگایەک کە بە کات گیرا
XZ Utils (March 2024): someone spent more than two years becoming a trusted helper of a small open-source compression tool used in Linux, then hid a backdoor in versions 5.6.0 and 5.6.1 (rated 10 out of 10 for severity). A developer noticed that remote logins had become slightly slower and used more processor time, investigated, and raised the alarm — mostly before the poisoned versions reached normal, stable systems. US agency CISA told users to go back to a clean version.
XZ Utils (ئاداری ٢٠٢٤): کەسێک زیاتر لە دوو ساڵی تەرخان کرد بۆ ئەوەی ببێتە یارمەتیدەرێکی متمانەپێکراوی ئامرازێکی بچووکی پەستاوتن کە لە Linuxـدا بەکار دێت، پاشان لە وەشانەکانی 5.6.0 و 5.6.1دا شاردەوە (لە ڕووی مەترسییەوە ١٠ لە ١٠ هەڵسەنگێنرا). پەرەپێدەرێک تێبینی کرد کە چوونەژوورەوەی دوور کەمێک خاوتر بووە و کاتی پرۆسێسەری زیاتر بەکار دەهێنێت، لێکۆڵینەوەی کرد و ئاگادارکردنەوەی دا — زۆربەی جار پێش ئەوەی وەشانە ژەهراوییەکان بگەنە سیستەمە ئاسایی و جێگیرەکان. دەزگای ئەمریکیی CISA بە بەکارهێنەرانی گوت بگەڕێنەوە بۆ وەشانێکی پاک.
How an attacker spent years gaining trust in an open-source project, hid a backdoor in XZ Utils, and was caught because SSH logins became slower.
چۆن چەند ساڵێک متمانەی پڕۆژەیەکی بەدەست هێنا، لە XZ Utilsـدا شاردەوە و بەهۆی خاوبوونەوەی SSH گیرا.
Plays 0:00-3:20: the XZ Utils backdoor, how it worked, how a developer noticed slower logins, and the years-long trust campaign.
لە 0:00 تا 3:20 پەخش دەبێت: XZ Utils، چۆن کاری دەکرد، چۆن هەستی کرد خاوتر بووە، هەروەها هەڵمەتی چەند ساڵەی بەدەستهێنانی متمانە.
Summary of the attacks, with corrected factsپوختەی هێرشەکان، بە ڕاستییە ڕاستکراوەکانەوە
The course ends this part with a summary table. Here it is rebuilt with the corrected facts from this lesson, on two screens.
کۆرسەکە ئەم بەشە بە خشتەیەکی پوختە کۆتایی پێدەهێنێت. لێرەدا بە ڕاستییە ڕاستکراوەکانی ئەم وانەیە دووبارە دروست کراوەتەوە، لە دوو پەڕەدا.
| Typeجۆر | Exampleنموونە | Whenکەی | Victimsقوربانییەکان | Impactکاریگەری |
|---|---|---|---|---|
| Infostealers | Snowflake customer accounts; Hot Topic (cause suggested, not confirmed)هەژمارەکانی کڕیارانی Snowflake؛ Hot Topic (هۆکار پێشنیار کراوە، پشتڕاست نەکراوەتەوە) | 2024 (Hot Topic: Oct 2024)٢٠٢٤ (Hot Topic: تشرینی یەکەمی ٢٠٢٤) | About 165 organisations; Hot Topic customersنزیکەی ١٦٥ ڕێکخراو؛ کڕیارانی Hot Topic | Large data theft; about 57 million Hot Topic accounts confirmed (350 million claimed)دزینی گەورەی ؛ نزیکەی ٥٧ ملیۆن هەژماری Hot Topic پشتڕاست کرایەوە (٣٥٠ ملیۆن بانگەشە کرا) |
| Malvertising | Fake download ads copying popular softwareڕیکلامی ساختەی کە بەناوبانگ کۆپی دەکەن | Comeback in 2023گەڕانەوە لە ٢٠٢٣دا | People searching for softwareئەو کەسانەی بەدوای دەگەڕێن | Malware downloads, often stealersدابەزاندنی ، زۆرجار دزەکان |
| Mobile banking Trojans بانکی لەسەر مۆبایل | ToxicPanda | Identified late Oct 2024لە کۆتایی تشرینی یەکەمی ٢٠٢٤ ناسرایەوە | >1,500 Android devices, mostly Italyزیاتر لە ١٬٥٠٠ ئامێری Android، زۆربەیان ئیتاڵیا | Bank accounts taken over from the victim's own phoneهەژماری بانکی لە مۆبایلی خودی قوربانییەوە گیرا |
| Remote access Trojans | SugarGh0st | Documented Nov 2023; US campaign May 2024تشرینی دووەمی ٢٠٢٣ تۆمار کرا؛ هەڵمەتی ئەمریکا ئایاری ٢٠٢٤ | Fewer than 10 people at one US AI organisationکەمتر لە ١٠ کەس لە یەک ڕێکخراوی ئەمریکی | Aimed at non-public information on generative AIئامانجی زانیاریی بڵاونەکراوە بوو دەربارەی |
| Cryptojacking | Record yearساڵی ڕیکۆرد | 2023 (then down 60% in the first half of 2024)٢٠٢٣ (پاشان ٦٠٪ کەمبوونەوە لە نیوەی یەکەمی ٢٠٢٤) | Businesses and individualsکۆمپانیاکان و تاکەکان | 1.1 billion attempts; energy and computing costs١٫١ ملیار هەوڵ؛ تێچووی وزە و هەژمارکردن |
Summary of the attacks, with corrected factsپوختەی هێرشەکان، بە ڕاستییە ڕاستکراوەکانەوە
Summary of the attacks (2), and what was correctedپوختەی هێرشەکان (٢) و ئەوەی ڕاست کرایەوە
| Typeجۆر | Exampleنموونە | Whenکەی | Victimsقوربانییەکان | Impactکاریگەری |
|---|---|---|---|---|
| AI-powered malware بە هێزی | AI-written phishing; first malware that calls AI models (reported Nov 2025) نووسراو بە ؛ یەکەم کە داوا لە دەکات (تشرینی دووەمی ٢٠٢٥ ڕاپۆرت کرا) | 2024–2025٢٠٢٤–٢٠٢٥ | Everyoneهەمووان | More convincing phishing; AI-using malware still mostly experimental باوەڕپێکراوتر؛ کە بەکار دەهێنێت هێشتا زیاتر تاقیکارییە |
| Fleeceware | 20+ subscription apps on Google Playزیاتر لە ٢٠ بەشداربوون لەسەر Google Play | Reported Jan 2020کانوونی دووەمی ٢٠٢٠ ڕاپۆرت کرا | Android usersبەکارهێنەرانی Android | Nearly 600 million installs (Google's count)نزیکەی ٦٠٠ ملیۆن دامەزراندن (ژماردنی Google) |
| IoT device attacks بۆ سەر ئامێرەکانی | Mirai and its variantsMirai و جۆرە گۆڕدراوەکانی | Since 2016لە ٢٠١٦ـەوە | Owners of cameras and routers; websites hit by DDoSخاوەنی کامێرا و ؛ پێکراوەکان بە | DDoS attacks of over 1 Tbit/s; spying risk زیاتر لە ١ تێرابیت لە چرکەیەکدا؛ سیخوڕی |
| Fileless (added)بێفایل (زیادکراو) | Living off the land with PowerShell and WMIژیان بە ئامرازی ناوخۆ بە PowerShell و WMI | Ongoingبەردەوام | Organisationsڕێکخراوەکان | Hard for file-scanning antivirus to see پشکنەری بە قورسی دەیبینێت |
| Supply chain (added)زنجیرەی دابینکردن (زیادکراو) | NotPetya; XZ UtilsNotPetya؛ XZ Utils | 2017; 2024٢٠١٧؛ ٢٠٢٤ | Customers of the poisoned softwareکڕیارانی ژەهراویکراو | NotPetya: over US$10 billion; XZ: caught earlyNotPetya: زیاتر لە ١٠ ملیار دۆلار؛ XZ: زوو گیرا |
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Correct ideaبیرۆکەی ڕاست |
|---|---|---|
| 'MFA makes stolen cookies harmless.'« دزراوەکان بێزیان دەکات.» | A stolen session cookie can skip the login, MFA included دزراو دەتوانێت تێبپەڕێنێت، لەوانە | After an infection, end all sessions as well as changing passwordsدوای تووشبوون، کۆتایی بە هەموو بهێنە و بگۆڕە |
| 'The first search result is the official site.'«یەکەم ئەنجامی گەڕان فەرمییە.» | Malvertising buys the top spot شوێنی سەرەوە دەکڕێت | Go to the official site directlyڕاستەوخۆ بڕۆ بۆ فەرمی |
| 'An app that asks for Accessibility must need it.'« کە داوای Accessibility دەکات حەتمەن پێویستی پێیەتی.» | Banking Trojans ask for it to control the phone بانکی داوای دەکەن بۆ کۆنترۆڵکردنی مۆبایلەکە | Deny it to any app that is not a real accessibility toolبۆ هەر کە ئامرازێکی ڕاستەقینەی Accessibility نییە ڕەتی بکەرەوە |
| 'Deleting the app cancels the subscription.'«سڕینەوەی بەشداربوون هەڵدەوەشێنێتەوە.» | Subscriptions live in the store accountبەشداربوونەکان لە هەژماری فرۆشگادا دەمێننەوە | Cancel in the store's subscription settingsلە ڕێکخستنەکانی بەشداربوونی فرۆشگاکەدا هەڵیبوەشێنەوە |
| 'My camera is too small to matter.'«کامێراکەم ئەوەندە بچووکە کە گرنگ نییە.» | Botnets are built from millions of small devices لە ملیۆنان ئامێری بچووک دروست دەکرێن | Change the default password and update the firmware بگۆڕە و نوێ بکەرەوە |
| 'If I trust the supplier, its updates are safe.'«ئەگەر متمانەم بە دابینکەرەکە هەبێت، سەلامەتن.» | Supply-chain attacks poison trusted updates متمانەپێکراو ژەهراوی دەکەن | Limit what update tools can reach; segment; keep offline backupsسنوور بۆ ئەوە دابنێ کە ئامرازەکانی دەگەنە کوێ؛ بەشبەش بکە؛ دەرهێڵ بهێڵەوە |
Exercisesڕاهێنانەکان
Which type from this lesson fits each clue? (a) A shop's cloud bill triples and its servers run at full CPU. (b) A login to your e-mail succeeds from another country although you use MFA, two days after you installed a 'free' game. (c) A text message says 'Your bank app needs an update' and links to a file to install. (d) A weekly $7 charge appears after you tried a QR-code app for three days. (e) Your router's admin page still has the password 'admin'.
کام جۆری ئەم وانەیە لەگەڵ هەر نیشانەیەکدا دەگونجێت؟ (أ) پسوولەی هەوریی دوکانێک سێ هێندە دەبێت و بە تەواو کار دەکەن. (ب) بۆ لە وڵاتێکی ترەوە سەرکەوتوو دەبێت هەرچەندە بەکار دەهێنیت، دوو ڕۆژ دوای ئەوەی یارییەکی «بێبەرانبەر»ـت دامەزراند. (ج) دەڵێت « بانکەکەت پێویستی بە هەیە» و بۆ دەدات بۆ دامەزراندن. (د) دوای ئەوەی سێ ڕۆژ تاقی کردەوە، بڕینی هەفتانەی ٧ دۆلار دەردەکەوێت. (هـ) پەڕەی بەڕێوەبردنی هێشتا «admin»ـی هەیە.
Show answerوەڵامەکە پیشان بدە
- (a) Cryptojacking — hidden mining uses the CPU and raises the bill.
- (b) Infostealer — the 'free' game stole a session cookie, which skipped MFA. End all sessions and change passwords from a clean device.
- (c) Mobile banking Trojan (smishing + side-loading) — update apps only from the official store.
- (d) Fleeceware — cancel the subscription in the app store.
- (e) An IoT risk — a Mirai-style botnet could take the router over; change the password and update the firmware.
- (أ) — دەرهێنانی شاراوە بەکار دەهێنێت و پسوولەکە بەرز دەکاتەوە.
- (ب) — یارییە «بێبەرانبەر»ـەکە دزی، کە تێپەڕاند. کۆتایی بە هەموو بهێنە و لە ئامێرێکی پاکەوە بگۆڕە.
- (ج) بانکی لەسەر مۆبایل ( بە + دامەزراندن لە دەرەوەی فرۆشگا) — تەنها لە فرۆشگا فەرمییەکەوە نوێ بکەرەوە.
- (د) — بەشداربوونەکە لە هەڵبوەشێنەوە.
- (هـ) — وەک Mirai دەتوانێت بگرێتە دەست؛ بگۆڕە و نوێ بکەرەوە.
The original table said: 'Infostealers | Dark X on Hot Topic | Mid-2023 | Retailer Hot Topic | Data of 350M customers stolen'. Rewrite the row so that every cell is accurate, and say which source you would cite for each fact.
خشتە ئەسڵییەکە دەیگوت: «Infostealers | Dark X on Hot Topic | Mid-2023 | Retailer Hot Topic | Data of 350M customers stolen». ڕیزەکە دووبارە بنووسەرەوە بۆ ئەوەی هەموو خانەیەک ورد بێت و بڵێ بۆ هەر ڕاستییەک کام سەرچاوە دەهێنیتەوە.
Show answerوەڵامەکە پیشان بدە
| Cellخانە | Accurate versionوەشانی ورد | Sourceسەرچاوە |
|---|---|---|
| Exampleنموونە | Hot Topic breach, claimed by an actor calling itself 'Satanic'دزەکردن بۆ Hot Topic، کە کەسێک بە ناوی «Satanic» بانگەشەی بۆ کرد | TechCrunch, 13 Nov 2024 |
| Whenکەی | October 2024تشرینی یەکەمی ٢٠٢٤ | Have I Been Pwned (via TechCrunch) |
| Impactکاریگەری | About 57 million accounts confirmed; 350 million was the attacker's claimنزیکەی ٥٧ ملیۆن هەژمار پشتڕاست کرایەوە؛ ٣٥٠ ملیۆن بانگەشەی بوو | TechCrunch; HIBP |
| Causeهۆکار | Infostealer-stolen credentials suggested by researchers; not confirmed by the company دزراو بە لە لایەن توێژەرانەوە پێشنیار کرا؛ کۆمپانیاکە پشتڕاستی نەکردەوە | Hudson Rock (via TechCrunch) |
Summaryپوختە
- Malware is now an industry: stealers, stolen-data markets, access brokers and ransomware gangs work as a chain.
- Infostealers copy saved passwords and cookies; stolen logins without MFA caused the 2024 Snowflake customer breaches.
- Malvertising buys real ads; mobile banking Trojans such as ToxicPanda abuse Accessibility and read one-time codes; RATs such as SugarGh0st serve espionage.
- Cryptojacking hit a record 1.1 billion attempts in 2023, then fell; fleeceware overcharges through subscriptions; IoT attacks (Mirai) use default passwords to build botnets.
- AI makes phishing more convincing; malware that calls AI models appeared in 2025, mostly experimental. Fileless attacks use the system's own tools; supply-chain attacks poison trusted updates (NotPetya, XZ Utils).
- Defence first: official sources only, MFA and passkeys, end sessions after an infection, deny Accessibility to unknown apps, change default passwords, patch, EDR and offline backups.
- ئێستا پیشەسازییە: دزەکان، بازاڕی دزراو، دەڵاڵانی دەستڕاگەیشتن و دەستەکانی وەک زنجیرەیەک کار دەکەن.
- و هەڵگیراوەکان کۆپی دەکەن؛ دزراو بەبێ بوونە هۆی دزەکردنەکانی کڕیارانی Snowflake لە ٢٠٢٤دا.
- ڕیکلامی ڕاستەقینە دەکڕێت؛ بانکی لەسەر مۆبایل وەک ToxicPanda Accessibility خراپ بەکار دەهێنن و دەخوێننەوە؛ RATـەکان وەک SugarGh0st خزمەتی دەکەن.
- لە ٢٠٢٣دا گەیشتە ڕیکۆردی ١٫١ ملیار هەوڵ، پاشان کەم بووەوە؛ لە ڕێگەی بەشداربوونەوە پارەی زیادە وەردەگرێت؛ بۆ سەر (Mirai) بەکار دەهێنن بۆ دروستکردنی .
- باوەڕپێکراوتر دەکات؛ کە داوا لە دەکات لە ٢٠٢٥دا دەرکەوت، زیاتر تاقیکاری. هێرشە بێفایلەکان ئامرازەکانی خودی سیستەم بەکار دەهێنن؛ متمانەپێکراو ژەهراوی دەکەن (NotPetya، XZ Utils).
- سەرەتا بەرگری: تەنها سەرچاوە فەرمییەکان، و ، دوای تووشبوون کۆتایی بە بهێنە، Accessibility بە نەناسراو مەدە، بگۆڕە، ، و دەرهێڵ.
How can an infostealer get past MFA?نەرمەواڵەیەکی زانیاریدز چۆن دەتوانێت لە پشتڕاستکردنەوەی فرەهۆکاری تێبپەڕێت؟
By stealing a session cookie from a logged-in browser: the website treats the attacker as the user who already passed MFA.
بە دزینی لە کە لە ژوورەوەیە: وەک ئەو بەکارهێنەرە مامەڵە دەکات کە پێشتر لە تێپەڕیوە.
What made Mirai able to build such a large botnet?چی وای لە Mirai کرد بتوانێت بۆتنێتێکی ئەوەندە گەورە دروست بکات؟
Millions of IoT devices still used factory default passwords, and Mirai tried a short list of them across the Internet.
ملیۆنان ئامێری هێشتا کارگەیان بەکار دەهێنا و Mirai لیستێکی کورتی ئەوانی لە سەرانسەری تاقی کردەوە.
Why is fileless malware hard to find, and what helps?بۆچی دۆزینەوەی نەرمەواڵەی زیانبەخشی بێفایل قورسە و چی یارمەتی دەدات؟
It leaves no normal malicious file and uses trusted tools such as PowerShell; behaviour monitoring (EDR), script restrictions and allow-listing help.
هیچ زیانبەخشی ئاسایی بەجێناهێڵێت و ئامرازی متمانەپێکراوی وەک PowerShell بەکار دەهێنێت؛ چاودێریی ڕەفتار ()، سنووردارکردنی و یارمەتی دەدەن.
Why was the 600 million fleeceware figure corrected?بۆچی ژمارەی ٦٠٠ ملیۆنی fleeceware ڕاست کرایەوە؟
It comes from a January 2020 Sophos report and counts installs reported by Google, not users in 2024.
لە ڕاپۆرتێکی Sophos لە کانوونی دووەمی ٢٠٢٠ـەوە دێت و ئەو دامەزراندنانە دەژمێرێت کە Google ڕاپۆرتی کردوون، نەک بەکارهێنەران لە ٢٠٢٤دا.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
Related lecturesوانە پەیوەندیدارەکان
- Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
- Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
- AI in Cybersecurity: Bias, Privacy, Surveillance and Deepfakesژیریی دەستکرد لە ئاسایشی سایبەردا: لاسەنگی، تایبەتێتی، چاودێری و دیپفەیکەکان
- Passwords, MFA and Access Controlتێپەڕەوشەکان، MFA و کۆنترۆڵی دەستڕاگەیشتن
- Real Incidents: From MoneyGram to GPS Spoofingڕووداوە ڕاستەقینەکان: لە MoneyGramـەوە تا هەڵخەڵەتاندنی GPS
- Emerging Technologies: IoT, VR/AR, Robots and Blockchainتەکنەلۆجیا نوێیەکان: ئینتەرنێتی شتەکان، ڕاستیی گریمانەیی/ڕاستیی زیادکراو، ڕۆبۆتەکان و بلۆکچەین
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- TechCrunch: Hot Topic data breach exposed personal data of 57 million customers (13 Nov 2024)
- Google Cloud / Mandiant: UNC5537 targets Snowflake customer instances for data theft and extortion (June 2024)
- Malwarebytes: 2024 ThreatDown State of Malware (press release, 6 Feb 2024)
- Infosecurity Magazine: ToxicPanda malware targets Android banking (5 Nov 2024)
- Proofpoint: Security Brief — Artificial Sweetener: SugarGh0st RAT used to target American AI experts (May 2024)
- SonicWall: Latest threat intelligence — cryptojacking 1.1 billion hits in 2023
- SonicWall: 2024 mid-year report (cryptojacking down 60%)
- Google Threat Intelligence Group: Advances in threat actor usage of AI tools (6 Nov 2025)
- ENISA Threat Landscape (2026 edition)
- Sophos: Intercept X for Mobile press release (Jan 2020; fleeceware apps with nearly 600 million installs)
- CISA Alert TA16-288A: Heightened DDoS threat posed by Mirai and other botnets
- Microsoft Learn: Fileless threats
- CCDCOE International Cyber Law: NotPetya (2017)
- CISA: Reported supply chain compromise affecting XZ Utils (CVE-2024-3094), 29 Mar 2024
- Wikipedia: XZ Utils backdoor
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.