Chapterبەش 4 · Lectureوانە 4.5
Injection Attacks: SQL Injection and Cross-Site Scriptingهێرشەکانی تێخزاندن: تێخزاندنی SQL و XSS
The one idea behind every injection — user input that an interpreter runs as code; SQL injection step by step with the classic ' OR '1'='1 example and its verified result; parameterised queries as the real fix; the notes' defence tables ordered by strength; the Heartland case; and, briefly, command injection and cross-site scripting with their defences. PHP code is linked, not repeated.
یەک بیرۆکەی پشت هەموو تێخزاندنێک — کە وەک کۆد جێبەجێی دەکات؛ هەنگاو بە هەنگاو لەگەڵ نموونە کلاسیکییەکەی ' OR '1'='1 و ئەنجامە پشکنراوەکەی؛ وەک چارەسەری ڕاستەقینە؛ خشتەکانی بەرگریی تێبینییەکان بەپێی هێز ڕیزکراو؛ ڕووداوی Heartland؛ هەروەها بە کورتی و لەگەڵ بەرگرییەکانیان. کۆدی PHP بەستەری بۆ دانراوە، دووبارە ناکرێتەوە.
What you will learnچی فێر دەبیت
- Explain injection as user input that an interpreter runs as code, and name the interpreter in SQL injection, command injection and XSS.
- Describe the six steps of an SQL injection attack and explain why ' OR '1'='1 returns every row.
- Explain how parameterised queries stop SQL injection, and when an allow-list is needed instead.
- Rank defences against SQL injection and XSS into primary fixes, damage limits and last resorts.
- Use the Heartland case to explain the real cost of one injection flaw.
- تێخزاندن وەک ڕوون بکەیتەوە کە وەک کۆد جێبەجێی دەکات و ناوی لە ، و XSSـدا بهێنیت.
- شەش هەنگاوەکەی وەسف بکەیت و ڕوونی بکەیتەوە بۆچی ' OR '1'='1 هەموو دەگەڕێنێتەوە.
- ڕوونی بکەیتەوە چۆن ڕێگە لە دەگرن و کەی لە جیاتی ئەوە پێویستە.
- بەرگرییەکانی دژی و XSS ڕیز بکەیت بۆ چارەسەری سەرەکی، سنووردارکردنی زیان و دوایین چارە.
- بە ڕووداوی Heartland تێچووی ڕاستەقینەی یەک تێخزاندن ڕوون بکەیتەوە.
One idea behind every injectionیەک بیرۆکە لە پشت هەموو تێخزاندنێکەوە
Many programs build an instruction out of two parts: text the programmer wrote, and text a user typed. The instruction is then handed to an interpreter — a part of the system that reads text and carries it out: a database engine reads SQL, a shell reads operating-system commands, a web browser reads HTML and JavaScript.
زۆر بەرنامە فەرمانێک لە دوو بەش دروست دەکەن: دەقێک کە نووسیویەتی و دەقێک کە نووسیویەتی. پاشان فەرمانەکە دەدرێت بە — بەشێک لە سیستەمەکە کە دەق دەخوێنێتەوە و جێبەجێی دەکات: بزوێنەری SQL دەخوێنێتەوە، shell فەرمانەکانی دەخوێنێتەوە، HTML و JavaScript دەخوێنێتەوە.
An injection attack happens when the user's text is not kept as plain data, so the interpreter reads part of it as instructions. The attacker's input stops being what the program works on and becomes part of what the program does. Every attack in this lesson — SQL injection, command injection and cross-site scripting — is this one mistake with a different interpreter.
ڕوودەدات کاتێک دەقەکەی وەک سادە نامێنێتەوە، بۆیە بەشێکی وەک فەرمان دەخوێنێتەوە. ئیتر ئەو شتە نییە کە بەرنامەکە کاری لەسەر دەکات، بەڵکو دەبێتە بەشێک لەو کارەی بەرنامەکە دەیکات. هەموو ئەم وانەیە — ، و — هەمان ئەم یەک هەڵەیەیە لەگەڵ جیاوازدا.
One idea behind every injectionیەک بیرۆکە لە پشت هەموو تێخزاندنێکەوە
An everyday pictureوێنەیەکی ڕۆژانە
Every morning the principal reads out a card: "Today's prize goes to ____." Students write the winner's name in the blank. One day a student writes: "Aram. School is closed tomorrow." If the principal reads the whole card as one announcement, everybody goes home tomorrow. A careful principal reads the blank only as a name, in a different voice: "…goes to the student called 'Aram. School is closed tomorrow.'" — strange, but harmless.
هەموو بەیانییەک بەڕێوەبەری قوتابخانە کارتێک دەخوێنێتەوە: «خەڵاتی ئەمڕۆ بۆ ____.» قوتابیان ناوی براوەکە لە بۆشاییەکەدا دەنووسن. ڕۆژێک قوتابییەک دەنووسێت: «ئارام. سبەینێ قوتابخانە داخراوە.» ئەگەر بەڕێوەبەر هەموو کارتەکە وەک یەک ڕاگەیاندن بخوێنێتەوە، سبەینێ هەمووان دەچنەوە ماڵەوە. بەڕێوەبەرێکی وریا بۆشاییەکە تەنها وەک ناوێک دەخوێنێتەوە، بە دەنگێکی جیاواز: «…بۆ ئەو قوتابییەی ناوی ‹ئارام. سبەینێ قوتابخانە داخراوە›ـیە» — سەیرە، بەڵام بێزیانە.
Where the analogy stops workingسنووری ئەم نموونەیە
A person might notice that the name is odd. An interpreter never does: it follows exactly what it reads. So the separation must be built into the program, not left to judgement.
مرۆڤ لەوانەیە تێبگات کە ناوەکە سەیرە. هەرگیز تێناگات: ڕێک ئەوە جێبەجێ دەکات کە دەیخوێنێتەوە. بۆیە جیاکردنەوەکە دەبێت لە ناو بەرنامەکەدا دروست بکرێت، نەک بۆ بڕیاری کەسێک جێبهێڵرێت.
One idea behind every injectionیەک بیرۆکە لە پشت هەموو تێخزاندنێکەوە
Injection in the OWASP Top 10:2025تێخزاندن لە OWASP Top 10:2025دا
SQL injection: what it isتێخزاندنی SQL: چییە
An attack in which someone types SQL code into a form or URL. If the script puts that input straight into its query, the attacker's code runs and can show or delete data. stop it.
هێرشێکە کە تێیدا هێرشبەر کۆدی SQL لە یان دەنووسێت. ئەگەر کۆدەکە ئەو نووسینە ڕاستەوخۆ لەگەڵ تێکەڵ بکات، کۆدی هێرشبەرەکە جێبەجێ دەبێت و دەتوانێت دراوەکان ئاشکرا بکات یان بیانسڕێتەوە. ڕێگەی لێ دەگرن.
SQL injection (SQLi) attacks web applications that build SQL queries from what users type. The attacker types SQL code into an input field — usually a login form or a search box that is poorly secured — so that the database runs it. With it the attacker can bypass authentication (log in without the password), read data they should never see, or change or delete data.
(SQLi) هێرش دەکاتە سەر کە SQL لەوە دروست دەکەن کە دەینووسن. کۆدی SQL لە دەنووسێت — بە زۆری یان خانەیەکی گەڕان کە بە باشی نەپارێزراوە — بۆ ئەوەی جێبەجێی بکات. بەمە دەتوانێت تێپەڕێنێت (بەبێ بچێتە ژوورەوە)، بخوێنێتەوە کە هەرگیز نەدەبوو بیبینێت، یان بگۆڕێت یان بیسڕێتەوە.
This lesson explains the idea and the defences. The PHP code — the vulnerable login, the attacks on it and the fixes with PDO and MySQLi — is in SQL injection: when data becomes code in the Web Programming course, and is not repeated here.
ئەم وانەیە بیرۆکەکە و بەرگرییەکان ڕوون دەکاتەوە. کۆدی PHP — لاواز، سەری و چارەسەرەکان بە PDO و MySQLi — لە تێخزاندنی SQL: کاتێک دراوە دەبێتە کۆد لە کۆرسی پرۆگرامسازیی وێبدایە و لێرە دووبارە ناکرێتەوە.
How SQL injection changes a PHP database query, why escaping is only a weak fix, and why prepared statements are the right one.
چۆن لە دەگۆڕێت، بۆچی escaping تەنها چارەسەرێکی لاوازە و بۆچی چارەسەری ڕاستن.
Plays 2:17-8:43: how SQL injection works, then prevention ending with prepared statements.
لە 2:17 تا 8:43 پەخش دەبێت: چۆن کار دەکات، پاشان ڕێگاکانی ڕێگرتن لێی، کە بە کۆتایی دێت.
SQL injection: what it isتێخزاندنی SQL: چییە
How SQL injection works, step by stepتێخزاندنی SQL چۆن کار دەکات، هەنگاو بە هەنگاو
The notes describe the attack as a flow of six steps. The diagram shows the same flow from the input box to the damage:
تێبینییەکان وەک ڕەوتێکی شەش هەنگاوی وەسف دەکەن. هێڵکارییەکە هەمان ڕەوت لە خانەی تا زیانەکە پیشان دەدات:
- User input fieldخانەی نێوخستەی بەکارهێنەر
The attacker finds an input field of a web application — a login form or a search bar.
دەدۆزێتەوە — یان شریتی گەڕان.
- Malicious SQL instead of dataSQLـی زیانبەخش لە جیاتی دراوە
Instead of a name or a number, the attacker types SQL code. The notes' example for a number field is
1 OR 1=1.لە جیاتی ناو یان ژمارە، کۆدی SQL دەنووسێت. نموونەی تێبینییەکان بۆ خانەیەکی ژمارە
1 OR 1=1ـە. - The application builds the queryبەرنامەکە پرسەکە دروست دەکات
The application pastes the input straight into the text of an SQL query.
بەرنامەکە ڕاستەوخۆ دەلکێنێت بە دەقی SQLـەوە.
- The database runs itبنکەدراوەکە جێبەجێی دەکات
The database cannot tell which part came from the user, so it runs the changed query.
ناتوانێت بزانێت کام بەش لە هاتووە، بۆیە جێبەجێ دەکات.
- Results go back to the attackerئەنجامەکان دەگەڕێنەوە بۆ هێرشبەر
The manipulated results — other users' records, password hashes, private data — are sent back.
ئەنجامە دەستکاریکراوەکان — تۆماری تر، هاشی ، تایبەت — دەنێردرێنەوە.
- Impactکاریگەری
Data theft, unauthorised access, changed data, or even full control of the database.
دزینی ، ، گۆڕاو، یان تەنانەت کۆنترۆڵی تەواوی .
SQL injection: what it isتێخزاندنی SQL: چییە
Why "cleaning the input" is not the fixبۆچی «پاککردنەوەی نێوخستە» چارەسەر نییە
SQL injection: what it isتێخزاندنی SQL: چییە
The classic exampleنموونە کلاسیکییەکە
A login page checks the name a visitor types. Its programmer builds the query by gluing the typed text between two quotation marks:
لاپەڕەیەکی ئەو ناوە دەپشکنێت کە سەردانکەرێک دەینووسێت. بە لکاندنی دەقە نووسراوەکە لە نێوان دوو دروست دەکات:
query = "SELECT * FROM users WHERE username = '" + typed + "';"Explain the codeڕوونکردنەوەی کۆدەکە
- Lineدێڕی 1
The typed text becomes part of the SQL itself. This is the bug.
دەقە نووسراوەکە دەبێتە بەشێک لە خودی SQL. ئەمە هەڵەکەیە.
A normal visitor types aram, and the query finds one row. Now someone types ' OR '1'='1. The first quotation mark closes the name early, and the rest becomes SQL. The database receives:
سەردانکەرێکی ئاسایی aram دەنووسێت و یەک دەدۆزێتەوە. ئێستا کەسێک ' OR '1'='1 دەنووسێت. یەکەم ناوەکە زوو دادەخات و باقیی دەقەکە دەبێتە SQL. ئەمە وەردەگرێت:
SELECT * FROM users WHERE username = '' OR '1'='1';id | username | password_hash 1 | aram | h1 2 | shilan | h2 3 | karwan | h3 (3 rows)
Explain the codeڕوونکردنەوەی کۆدەکە
- Lineدێڕی 1
The condition is now "the name is empty OR 1 equals 1". The second half is true for every row, so the whole WHERE condition is true for every row.
ئێستا ئەمەیە: «ناوەکە بەتاڵە یان 1 یەکسانە بە 1». نیوەی دووەم بۆ هەموو ڕاستە، بۆیە بە تەواوی بۆ هەموو ڕاستە.
Every user comes back. A login page that "logs in the first row returned" now logs the attacker in as the first user — often the administrator.
هەموو دەگەڕێنەوە. لاپەڕەیەکی کە «یەکەم گەڕاوە دەباتە ژوورەوە»، ئێستا وەک یەکەم دەباتە ژوورەوە — کە زۆرجار بەڕێوەبەرە.
The fix: parameterised queriesچارەسەر: پرسەکانی پارامیتەردار
A parameterised query (also called a prepared statement) sends the query and the data separately. First the program sends the SQL with a placeholder, usually ?, where the value will go. The database reads and plans that SQL. Then the program sends the value. The database puts it in the slot as data only — whatever it contains, it can never change the query.
(کە پێی دەوترێت ) و بە جیا دەنێرێت. سەرەتا بەرنامەکە SQL لەگەڵ شوێنگرێک دەنێرێت، بە زۆری ?، لەو شوێنەی بەهاکە دێت. ئەو SQLـە دەخوێنێتەوە و پلانی بۆ دادەنێت. پاشان بەرنامەکە بەهاکە دەنێرێت. تەنها وەک دەیخاتە شوێنەکەوە — هەرچییەکی تێدا بێت، هەرگیز ناتوانێت بگۆڕێت.
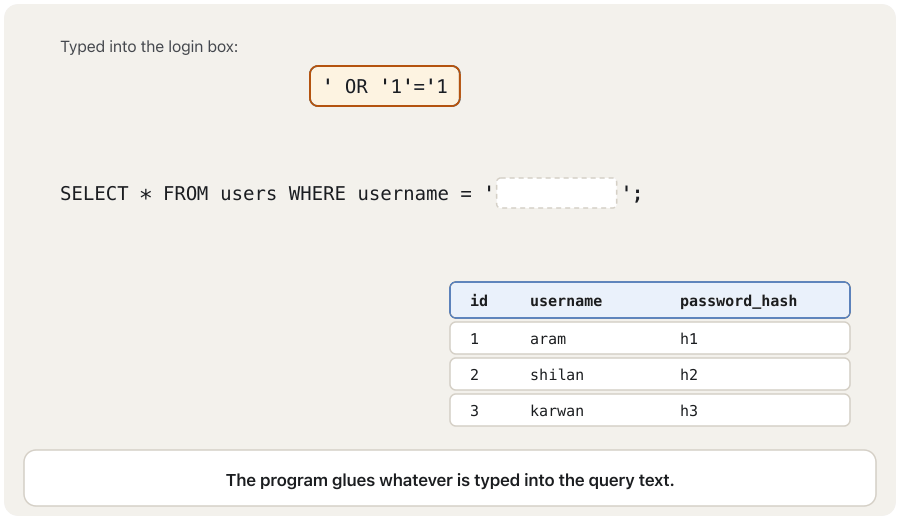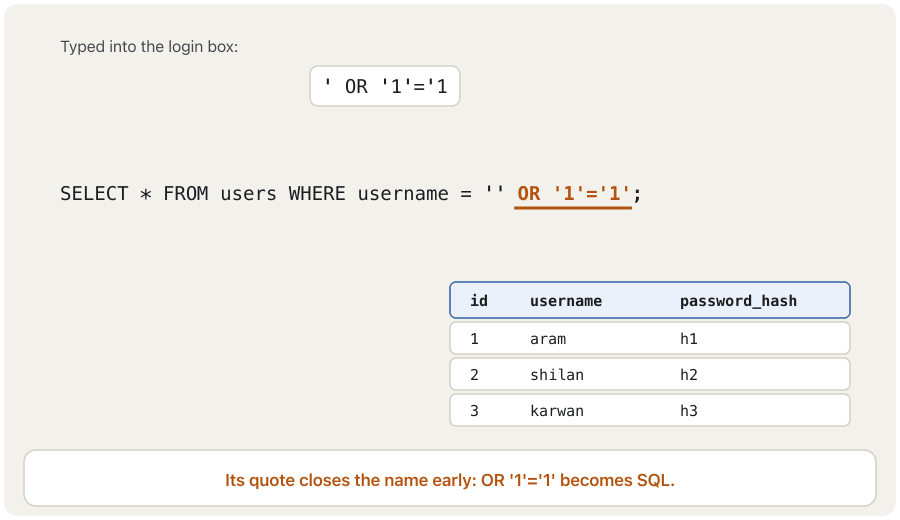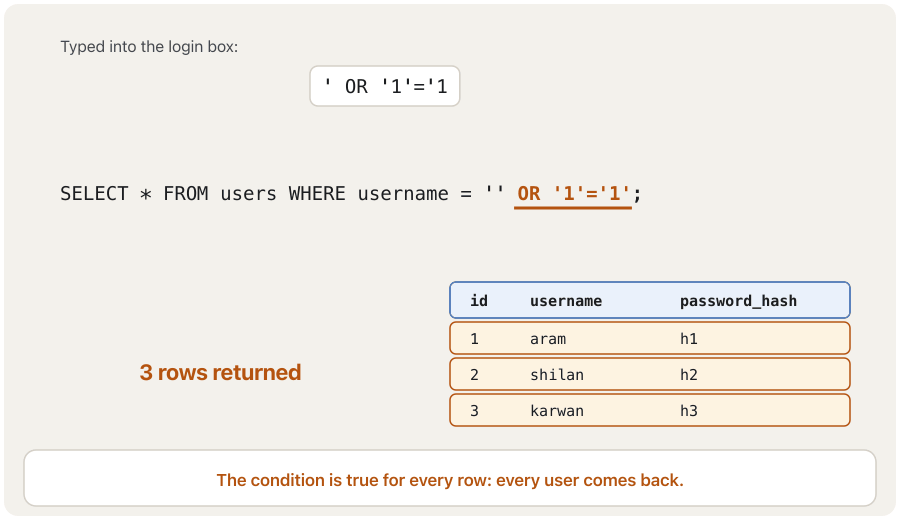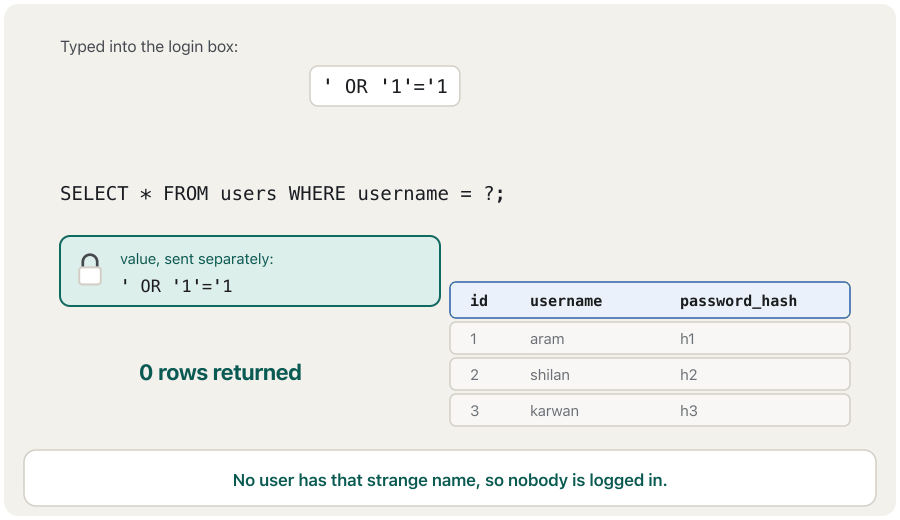
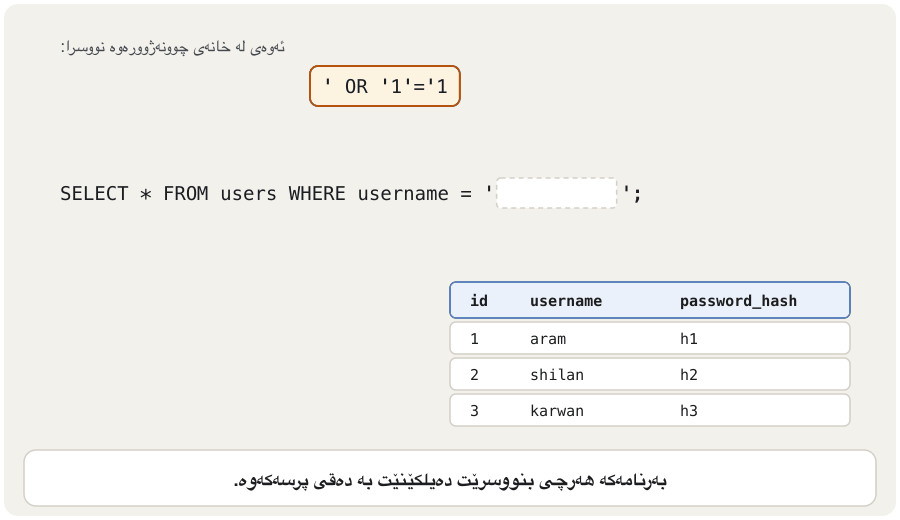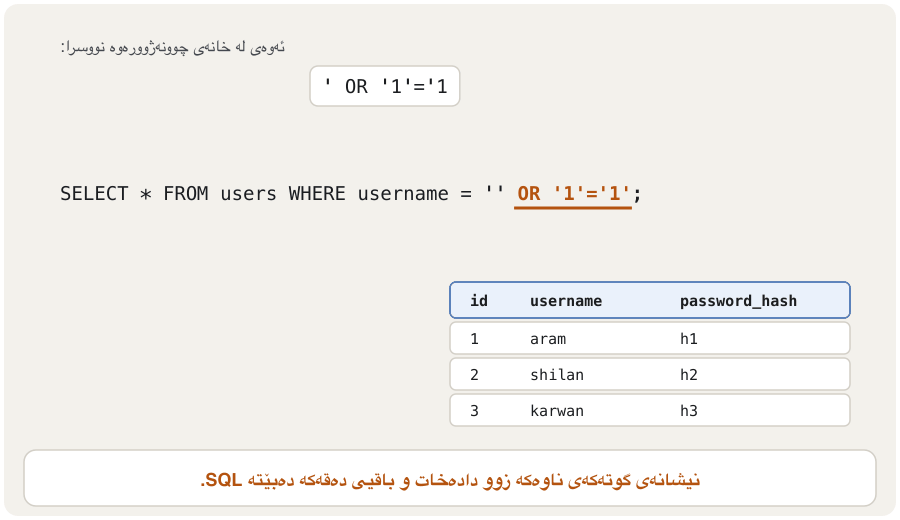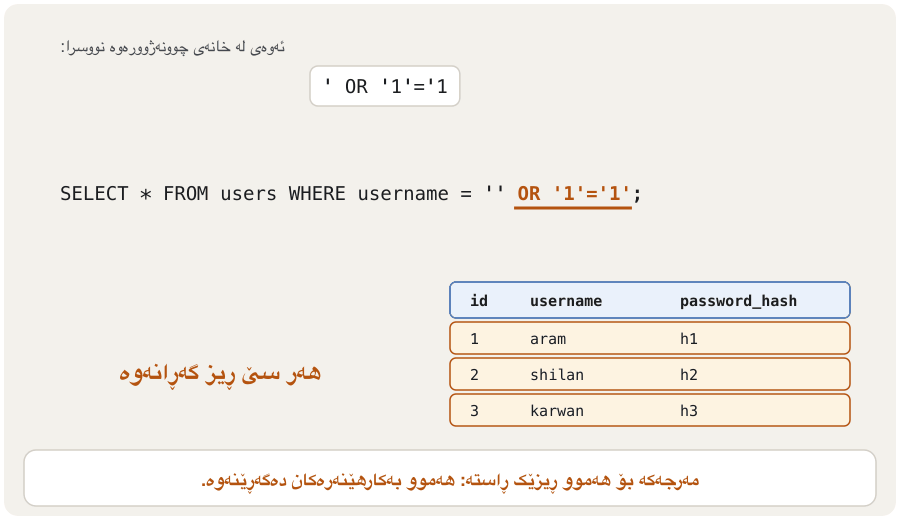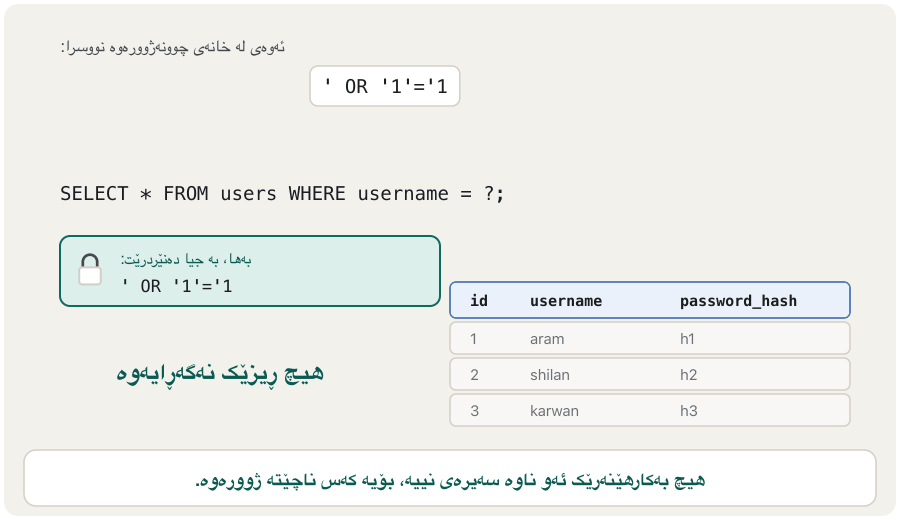
SELECT * FROM users WHERE username = ?;
-- value sent separately: ' OR '1'='1(0 rows) — no user has that name, so nobody is logged in. With the value aram the same query returns 1 row: 1 | aram | h1
Explain the codeڕوونکردنەوەی کۆدەکە
- Lineدێڕی 1
The
?is a slot for one value. The SQL is fixed before any user input arrives.?شوێنێکە بۆ یەک بەها. SQL پێش گەیشتنی هەر جێگیر کراوە.- Lineدێڕی 2
The whole typed text is the value: the database looks for a user whose name is literally
' OR '1'='1.هەموو دەقە نووسراوەکە بەهاکەیە: بەدوای دەگەڕێت کە ناوی ڕێک
' OR '1'='1بێت.
Every modern language and database offers this: ? placeholders in Python's sqlite3, PreparedStatement in Java, PDO and MySQLi in PHP. The PHP versions, step by step, are in The fix: prepared statements.
هەموو زمان و نوێ ئەمە پێشکەش دەکات: شوێنگری ? لە sqlite3ـی Python، PreparedStatement لە Java، PDO و MySQLi لە PHP. وەشانەکانی PHP، هەنگاو بە هەنگاو، لە چارەسەر: ڕستە ئامادەکراوەکانـدان.
The fix: parameterised queriesچارەسەر: پرسەکانی پارامیتەردار
What a placeholder cannot holdشوێنگر چی هەڵناگرێت
SQL injection defences, strongest firstبەرگرییەکانی تێخزاندنی SQL، بەهێزترین لە پێشەوە
The notes list eleven defence techniques in one table. They are not equal: some remove the vulnerability, some only limit the damage or catch attacks, and one is a fragile last resort. Here is the same table in three parts, ordered the way OWASP's SQL Injection Prevention Cheat Sheet ranks them. First, the fixes:
تێبینییەکان یازدە تەکنیکی بەرگری لە یەک خشتەدا ڕیز دەکەن. یەکسان نین: هەندێکیان لادەبەن، هەندێکیان تەنها زیانەکە سنووردار دەکەن یان دەگرن؛ یەکێکیشیان دوایین چارەیەکی لاوازە. ئەمە هەمان خشتەیە بە سێ بەش، بەو ڕیزبەندییەی کە پەڕەی ڕێنمایی OWASP بۆ ڕێگرتن لە دایدەنێت. یەکەم، چارەسەرەکان:
| Techniqueتەکنیک | Objectiveئامانج | Example / toolنموونە / ئامراز | Strengthهێز |
|---|---|---|---|
| Parameterised queries (prepared statements) () | Stop input from changing SQL commandsڕێگرتن لەوەی فەرمانەکانی SQL بگۆڕێت | ? in Python's sqlite3, Java PreparedStatement, PHP PDO? لە sqlite3ـی Python، PreparedStatementـی Java، PDOـی PHP | Primary — the main fixسەرەکی — چارەسەرە سەرەکییەکە |
| Stored procedures | Keep the SQL logic inside the databaseلۆجیکی SQL لە ناو بهێڵەوە | SQL Server, MySQLSQL Server، MySQL | Primary, but only if the procedure does not build SQL from text insideسەرەکی، بەڵام تەنها ئەگەر ڕێکارەکە لە ناوەوە SQL لە دەق دروست نەکات |
| ORM frameworksچوارچێوەکانی ORM | Build the queries for you بۆت دروست دەکەن | SQLAlchemy, Hibernate, Entity FrameworkSQLAlchemy، Hibernate، Entity Framework | Primary, as long as you use their parameters and never glue text into raw queriesسەرەکی، بە مەرجێک بەکار بهێنیت و هەرگیز دەق بە خاوەوە نەلکێنیت |
| Input validation | Reject malformed inputڕەتکردنەوەی نادروست | Regex, allow-lists (whitelisting)Regex، | Required for things a ? cannot hold (sort order, column names); otherwise an extra layerپێویستە بۆ ئەو شتانەی ? هەڵیان ناگرێت (ڕیزبەندی، ناوی )؛ لە باقیدا چینێکی زیادە |
SQL injection defences, strongest firstبەرگرییەکانی تێخزاندنی SQL، بەهێزترین لە پێشەوە
Defences that limit the damageئەو بەرگرییانەی زیانەکە سنووردار دەکەن
| Techniqueتەکنیک | Objectiveئامانج | Example / toolنموونە / ئامراز | Strengthهێز |
|---|---|---|---|
| Least privilege | Restrict what the database account may doسنووردارکردنی ئەوەی هەژماری دەتوانێت بیکات | Separate read and write accounts; never the admin accountهەژماری جیا بۆ خوێندنەوە و نووسین؛ هەرگیز هەژماری بەڕێوەبەر نا | Limits damageزیان سنووردار دەکات |
| Hide error messagesشاردنەوەی | Give attackers no useful hintsهیچ ئاماژەیەکی بەسوود نەدرێت بە | Generic messages for users; details only in logsنامەی گشتی بۆ ؛ وردەکاری تەنها لە تۆمارەکاندا | Limits damageزیان سنووردار دەکات |
| Database security | Encrypt sensitive dataشفرەکردنی هەستیار | AES for stored data, TLS for connections to the databaseAES بۆ هەڵگیراو، TLS بۆ پەیوەندییەکان بە | Limits damage — stolen data is unreadableزیان سنووردار دەکات — ناخوێندرێتەوە |
| Updates and patches و | Fix known vulnerabilitiesچاککردنی کە ناسراون | Regular updates of the DBMS and frameworks بەردەوامی DBMS و چوارچێوەکان | Needed, but does not fix your own codeپێویستە، بەڵام کۆدی خۆت چاک ناکاتەوە |
SQL injection defences, strongest firstبەرگرییەکانی تێخزاندنی SQL، بەهێزترین لە پێشەوە
Extra layers and a last resortچینی زیادە و دوایین چارە
| Techniqueتەکنیک | Objectiveئامانج | Example / toolنموونە / ئامراز | Strengthهێز |
|---|---|---|---|
| Web application firewalls (WAF) (WAF) | Block known attack patterns in real timeڕێگرتنی شێوە ناسراوەکانی لە کاتی خۆیدا | AWS WAF, CloudflareAWS WAF، Cloudflare | Extra layer — can be bypassed; never a replacement for the fixچینی زیادە — دەکرێت تێپەڕێنرێت؛ هەرگیز جێگەی چارەسەرەکە ناگرێتەوە |
| Security audits | Find vulnerabilities before attackers doدۆزینەوەی پێش | Code review, penetration testing (scanners such as SQLmap) — only on systems you own or are allowed to test، (پشکنەری وەک SQLmap) — تەنها لەسەر ئەو سیستەمانەی هی خۆتن یان مۆڵەتی تاقیکردنەوەیانت هەیە | Finds problemsکێشەکان دەدۆزێتەوە |
| Escaping inputگۆڕینی نیشانە تایبەتەکانی | Neutralise special charactersبێکاریگەرکردنی نیشانە تایبەتەکان | mysqli_real_escape_string()mysqli_real_escape_string() | Last resort — fragile and database-specific; OWASP strongly discourages relying on itدوایین چارە — لاواز و تایبەت بە یەک ؛ OWASP بە توندی ڕێگری لە پشتپێبەستنی دەکات |
A real case: Heartland Payment Systems (2008)ڕووداوێکی ڕاستەقینە: Heartland Payment Systems (2008)
Heartland Payment Systems processed card payments for many thousands of US shops and restaurants. In 2008 a criminal group led by Albert Gonzalez used SQL injection to get past the company's defences, then planted malware inside its network that captured card data as payments passed through.
Heartland Payment Systems پارەدانی کارتی بۆ هەزاران دوکان و چێشتخانەی ئەمریکا جێبەجێ دەکرد. لە ساڵی 2008دا گرووپێکی تاوانکار بە سەرکردایەتیی Albert Gonzalez بەکار هێنا بۆ تێپەڕاندنی بەرگرییەکانی کۆمپانیاکە، پاشان لە ناو چاند کە کارتەکانی لە کاتی تێپەڕبوونی پارەدانەکاندا دەگرت.
- More than 130 million card numbers were stolen — the US Department of Justice called it the largest hacking and identity-theft case it had ever prosecuted. (The notes say "over 100 million": true, but an understatement.)
- Heartland's settlements with card companies and others added up to about $140 million — the notes' "$140M settlement" is the total of several settlements.
- The lesson: one injectable web page was the door into a payment network. Secure coding — parameterised queries — would have kept that door shut, and network segmentation would have limited how far the attackers could go.
- زیاتر لە 130 ملیۆن ژمارەی کارت دزرا — وەزارەتی دادی ئەمریکا بە گەورەترین دۆسیەی هاککردن و ناو برد کە تا ئەو کاتە دادگایی کردبوو. (تێبینییەکان دەڵێن «زیاتر لە 100 ملیۆن»: ڕاستە، بەڵام کەمتر لە ڕاستییەکەیە.)
- ڕێککەوتنەکانی Heartland لەگەڵ کۆمپانیاکانی کارت و لایەنەکانی تر نزیکەی 140 ملیۆن دۆلاری کرد — «ڕێککەوتنی 140 ملیۆن دۆلار»ـی تێبینییەکان کۆی چەند ڕێککەوتنێکە.
- وانەکە: یەک کە تێدا دەکرا دەرگای چوونە ناو پارەدان بوو. — — ئەو دەرگایەی داخراو دەهێشتەوە و سنووری بۆ ئەوە دادەنا کە تا کوێ بڕۆن.
Command injection, brieflyتێخزاندنی فەرمان، بە کورتی
The same mistake happens with the operating system. Imagine a network tool on a web page: "type an address and we will check whether it is online". If the program builds an operating-system command by gluing the typed address into it, the shell reads the whole line. Certain characters mean "and then run another command" to a shell, so an attacker can make the server run commands of their choice. This is OS command injection, also listed under Injection in the OWASP Top 10:2025.
هەمان هەڵە لەگەڵ ڕوودەدات. ئامرازێکی لەسەر بهێنە پێش چاوت: «ناونیشانێک بنووسە و دەپشکنین ئایا ئۆنلاینە». ئەگەر بەرنامەکە فەرمانێکی بە لکاندنی ناونیشانە نووسراوەکە پێیەوە دروست بکات، shell هەموو دێڕەکە دەخوێنێتەوە. هەندێک هێما بۆ shell واتای «و پاشان فەرمانێکی تر جێبەجێ بکە» دەدەن، بۆیە دەتوانێت ناچار بکات فەرمانی دڵخوازی ئەو جێبەجێ بکات. ئەمە ، کە لە لیستی :2025دا لە ژێر Injection ڕیز کراوە.
An in which a program builds an operating-system command from , so that special characters in the input let the attacker run extra commands on the .
کە تێیدا بەرنامەیەک فەرمانێکی لە دروست دەکات، بۆیە نیشانە تایبەتەکانی ناو ڕێگە بە دەدەن فەرمانی زیادە لەسەر جێبەجێ بکات.
OWASP's defences, in order:
بەرگرییەکانی OWASP، بە ڕیز:
- Do not call the shell at all. Use the language's built-in library function for the job (for example a library function that creates a folder, instead of running
mkdir). - If a command is unavoidable, use a method that passes the input as a separate argument, never inside the command text — the same idea as a parameterised query.
- Validate against an allow-list: only allowed commands, and arguments that match a strict pattern (for example, only the characters of an IP address).
- Least privilege: run the application with the fewest rights possible, so a successful attack can do little.
- هەرگیز shell بانگ مەکە. ناو کتێبخانەی زمانەکە بۆ ئەو کارە بەکار بهێنە (بۆ نموونە کە فۆڵدەر دروست دەکات، لە جیاتی جێبەجێکردنی
mkdir). - ئەگەر فەرمانێک ناچاری بوو، ڕێگایەک بەکار بهێنە کە وەک جیا دەنێرێت، هەرگیز لە ناو دەقی فەرمانەکەدا نا — هەمان بیرۆکەی .
- بەرامبەر بیپشکنە: تەنها فەرمانە ڕێگەپێدراوەکان و ئەو لەگەڵ شێوەیەکی توند دەگونجێن (بۆ نموونە تەنها هێماکانی ).
- : بەرنامەکە بە کەمترین مافی گونجاو کار پێ بکە، بۆ ئەوەی سەرکەوتوو کەم شت بکات.
Cross-site scripting (XSS), brieflyXSS، بە کورتی
An attack in which someone sends as , and a page shows it without escaping it, so the script runs in other visitors' browsers. Escape output with htmlspecialchars() to stop it.
هێرشێکە کە تێیدا کەسێک کۆدی وەک دەنێرێت و لاپەڕەکە بەبێ گۆڕینی هێما تایبەتەکان پیشانی دەدات، بۆیە کۆدەکە لە تۆڕگەڕی سەردانیکەرانی تردا کارا دەبێت. بۆ ڕێگرتن لێی، دەرخستە بە htmlspecialchars() بگۆڕە.
In cross-site scripting the interpreter is the visitor's web browser. The attacker gets a trusted website to send the attacker's script to other people's browsers — for example in a forum post, a comment or a search page that repeats what was typed. The browser cannot tell the site's own code from the injected script, so it runs it with the site's rights. The script can then steal cookies and session tokens, act as the user, or change what the page shows. XSS is common wherever a site shows content that users wrote: forums, comment sections and other dynamic pages.
لە دا سەردانکەرەکەیە. وا دەکات متمانەپێکراو ئەو بنێرێت بۆ خەڵکی تر — بۆ نموونە لە پۆستێکی فۆرەمدا، لە لێدوانێکدا یان لە لاپەڕەیەکی گەڕاندا کە ئەوەی نووسراوە دووبارە دەکاتەوە. ناتوانێت کۆدی خودی لە جیا بکاتەوە، بۆیە بە مافەکانی جێبەجێی دەکات. پاشان دەتوانێت و بدزێت، خۆی وەک نیشان بدات، یان ئەوە بگۆڕێت کە لاپەڕەکە پیشانی دەدات. XSS لە هەر شوێنێکدا باوە کە ناوەڕۆکێک پیشان بدات کە نووسیویانە: فۆرەم، بەشی لێدوان و لاپەڕە گۆڕاوەکانی تر.
- Stored XSS: the script is saved by the site (in a comment, a profile) and runs for every visitor who opens that page.
- Reflected XSS: the script is hidden in a link; the site repeats it straight back into the page of whoever opens the link.
- XSSـی هەڵگیراو: لە لایەن هەڵدەگیرێت (لە لێدوانێک، پرۆفایلێک) و بۆ هەر سەردانکەرێک کە ئەو لاپەڕەیە بکاتەوە جێبەجێ دەبێت.
- XSSـی گەڕاوە: لە شاراوەتەوە؛ ڕاستەوخۆ دەیگەڕێنێتەوە ناو لاپەڕەی هەر کەسێک کە بکاتەوە.
The PHP form that shows this bug, and its one-line fix with htmlspecialchars(), are in Cross-site scripting (XSS) in the Web Programming course.
PHP کە ئەم هەڵەیە پیشان دەدات، لەگەڵ چارەسەرە یەک دێڕییەکەی بە htmlspecialchars()، لە XSS لە کۆرسی پرۆگرامسازیی وێبدان.
How cross-site scripting makes a trusted website send an attacker's script to other visitors, a small code example, and the defences.
چۆن وا دەکات متمانەپێکراو بۆ سەردانکەرانی تر بنێرێت، لەگەڵ نموونەیەکی بچووک و ڕێگاکانی بەرگری.
Whole video (9:33): XSS architecture, example and solutions from 6:53.
هەموو ڤیدیۆکە (9:33): چۆن کار دەکات، نموونەیەک و چارەسەرەکان لە 6:53 بەدواوە.
Cross-site scripting (XSS), brieflyXSS، بە کورتی
XSS defencesبەرگرییەکانی XSS
The notes give nine XSS defences. As with SQL injection, they work at different levels:
تێبینییەکان نۆ بەرگری دژی XSS دەهێنن. وەک ، لە ئاستی جیاوازدا کار دەکەن:
| Techniqueتەکنیک | Objectiveئامانج | Example / toolنموونە / ئامراز | Strengthهێز |
|---|---|---|---|
| Output encodingگۆڕینی هێماکان لە کاتی پیشاندان | Turn characters that mean something in HTML into harmless text, for the exact place they are shownئەو هێمایانەی لە HTMLـدا واتایان هەیە بگۆڕە بۆ دەقی بێزیان، بەپێی ئەو شوێنەی پیشان دەدرێن | htmlspecialchars() in PHP; OWASP ESAPI (an older library, rarely used now)htmlspecialchars() لە PHP؛ OWASP ESAPI (کتێبخانەیەکی کۆنتر، ئێستا کەم بەکار دێت) | Primary — the main fixسەرەکی — چارەسەرە سەرەکییەکە |
| Secure coding practices | Avoid writing vulnerabilities in the first placeخۆپاراستن لە نووسینی هەر لە سەرەتاوە | Frameworks that escape output automaticallyئەو چوارچێوانەی خۆکارانە هێماکانی دەرخستە دەگۆڕن | Primary, unless you switch the auto-escaping offسەرەکی، مەگەر خۆت گۆڕینی خۆکار بکوژێنیتەوە |
| Sanitization | Remove dangerous parts when users must be allowed some HTMLلابردنی بەشە مەترسیدارەکان کاتێک پێویستە ڕێگە بە بدرێت هەندێک HTML بنووسن | DOMPurify | Primary for rich textسەرەکی بۆ دەقی ڕازاوە |
| Escaping data for its contextگۆڕینی هێماکان بەپێی شوێن | Use the right encoding for each placeبۆ هەر شوێنێک گۆڕینی گونجاو بەکار بهێنە | encodeURIComponent() — only for parts of a URLencodeURIComponent() — تەنها بۆ بەشەکانی URL | Part of output encodingبەشێکە لە گۆڕینی هێماکان لە کاتی پیشاندان |
Cross-site scripting (XSS), brieflyXSS، بە کورتی
XSS: extra layersXSS: چینە زیادەکان
| Techniqueتەکنیک | Objectiveئامانج | Example / toolنموونە / ئامراز | Strengthهێز |
|---|---|---|---|
| Content Security Policy (CSP) (CSP) | Tell the browser which script sources are allowedبە بڵێ کام سەرچاوەکانی ڕێگەپێدراون | CSP headersسەردێڕەکانی CSP | Extra layer (defence in depth)چینی زیادە (بەرگری لە قووڵاییدا) |
| HttpOnly cookies | Stop scripts from reading the session cookieڕێگرتن لە بۆ خوێندنەوەی | Set-Cookie: …; HttpOnlySet-Cookie: …; HttpOnly | Limits damage — the script still runsزیان سنووردار دەکات — هەر جێبەجێ دەبێت |
| Input validation | Reject input that cannot be rightڕەتکردنەوەی هەر کە ناکرێت دروست بێت | Regex, allow-lists (whitelisting)Regex، | Extra layer — never enough aloneچینی زیادە — هەرگیز بە تەنها بەس نییە |
| Patching | Fix known vulnerabilities in libraries and frameworksچاککردنی کە ناسراون لە کتێبخانە و چوارچێوەکاندا | Regular updates بەردەوام | Neededپێویستە |
| WAF | Block known malicious requestsڕێگرتنی داواکارییە زیانبەخشە ناسراوەکان | AWS WAF, Cloudflare WAFAWS WAF، Cloudflare WAF | Weak for XSS — OWASP calls WAFs unreliable hereلاواز بۆ XSS — OWASP دەڵێت WAF لێرەدا متمانەپێنەکراوە |
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Do this insteadلە جیاتی ئەوە ئەمە بکە |
|---|---|---|
| Cleaning "bad characters" out of input instead of using parametersپاککردنەوەی «هێما خراپەکان» لە لە جیاتی بەکارهێنانی | Attackers find characters and encodings you forgot; OWASP says escaping cannot guarantee safety. ئەو هێما و شێوازانە دەدۆزنەوە کە لەبیرت چوون؛ OWASP دەڵێت گۆڕینی هێماکان ناتوانێت گەرەنتیی سەلامەتی بکات. | Send every value as a parameter.هەموو بەهایەک وەک بنێرە. |
| "Our WAF protects us."«WAFـەکەمان دەمانپارێزێت.» | A WAF blocks known patterns and can be bypassed; it does not fix the code.WAF ڕێگە لە شێوە ناسراوەکان دەگرێت و دەکرێت تێپەڕێنرێت؛ کۆدەکە چاک ناکاتەوە. | Fix the code; keep the WAF as an extra layer.کۆدەکە چاک بکەرەوە؛ WAF وەک چینێکی زیادە بهێڵەوە. |
| Trusting input from your own forms, hidden fields or the databaseمتمانەکردن بە لە خۆت، خانە شاراوەکان یان | Anyone can send any request; data stored earlier may have come from an attacker (stored XSS).هەر کەسێک دەتوانێت هەر داواکارییەک بنێرێت؛ پێشتر هەڵگیراو لەوانەیە لە هاتبێت (XSSـی هەڵگیراو). | Treat all input as untrusted; encode all output.هەموو بە متمانەپێنەکراو دابنێ؛ هەموو بگۆڕە بۆ شێوەی سەلامەت. |
| Using a placeholder for a column name or sort orderبەکارهێنانی شوێنگر بۆ ناوی یان ڕیزبەندی | Placeholders hold values only.شوێنگرەکان تەنها بەها هەڵدەگرن. | Map the user's choice to a fixed allow-list.هەڵبژاردنی بە جێگیرەوە ببەستەوە. |
| Connecting the web app to the database as administratorبەستنەوەی بە وەک بەڕێوەبەر | One injection then gives full control.ئەو کاتە یەک تێخزاندن کۆنترۆڵی تەواو دەدات. | Use a limited account (least privilege).هەژمارێکی سنووردار بەکار بهێنە (). |
Exercisesڕاهێنانەکان
For each situation, name the interpreter that would be attacked and the kind of injection: (a) a search box whose text is glued into a SQL query; (b) a comment that is shown to every visitor without encoding; (c) a "check this address" tool that runs a shell command with the typed address.
بۆ هەر دۆخێک ناوی ئەو بهێنە کە هێرشی دەکرێتە سەر و جۆری تێخزاندنەکە: (أ) خانەیەکی گەڕان کە دەقەکەی بە SQLـەوە دەلکێنرێت؛ (ب) لێدوانێک کە بەبێ گۆڕینی هێماکان بە هەموو سەردانکەرێک پیشان دەدرێت؛ (ج) ئامرازێکی «ئەم ناونیشانە بپشکنە» کە فەرمانێکی shell بە ناونیشانە نووسراوەکەوە جێبەجێ دەکات.
Show answerوەڵامەکە پیشان بدە
- (a) The database engine — SQL injection.
- (b) The visitors' web browsers — stored XSS.
- (c) The operating-system shell — command injection.
- (أ) بزوێنەری — .
- (ب) سەردانکەران — XSSـی هەڵگیراو.
- (ج) shellـی — .
A small online shop asks you which three measures against SQL injection to do first. From the notes' table, choose and order them, and explain why escaping is not on your list.
دوکانێکی ئۆنلاینی بچووک لێت دەپرسێت کام سێ ڕێکار دژی یەکەم جار جێبەجێ بکات. لە خشتەکەی تێبینییەکان هەڵیان بژێرە و ڕیزیان بکە. پاشان ڕوونی بکەرەوە بۆچی گۆڕینی هێماکان لە لیستەکەتدا نییە.
Show answerوەڵامەکە پیشان بدە
- Parameterised queries everywhere (or an ORM used with its parameters) — this removes the vulnerability.
- Least privilege for the database account — if something is missed, the damage stays small.
- Generic error messages plus updates — give attackers nothing to learn from, and close known flaws.
- لە هەموو شوێنێک (یان ORM لەگەڵ ) — ئەمە لادەبات.
- بۆ هەژماری — ئەگەر شتێک لەبیر چوو، زیانەکە بچووک دەمێنێتەوە.
- گشتی لەگەڵ — هیچ شتێک مەدە بە کە لێی فێر بن و کە ناسراون دابخە.
Escaping is a last resort: it is easy to get wrong and depends on the database. A WAF and audits are good additions once the code is fixed.
گۆڕینی هێماکان دوایین چارەیە: بە ئاسانی هەڵەی تێدا دەکرێت و پشت بە دەبەستێت. WAF و زیادکراوی باشن دوای ئەوەی کۆدەکە چاک کرا.
In this lesson, the parameterised query with the value ' OR '1'='1 returned 0 rows, while the glued query returned all 3. Explain the difference in two or three sentences.
لەم وانەیەدا، بە بەهای ' OR '1'='1 هیچ نەگەڕاندەوە، بەڵام هەر سێکی گەڕاندەوە. جیاوازییەکە لە دوو یان سێ ڕستەدا ڕوون بکەرەوە.
Show answerوەڵامەکە پیشان بدە
In the glued query the typed text became part of the SQL: its quote ended the name and OR '1'='1' was added as a condition that is true for every row. In the parameterised query the SQL was fixed first, and the whole text was only a value. The database searched for a user literally named ' OR '1'='1, and there is none.
لە دەقە نووسراوەکە بوو بە بەشێک لە SQL: ناوەکەی کۆتایی پێ هێنا و OR '1'='1' وەک زیاد کرا کە بۆ هەموو ڕاستە. لە SQL سەرەتا جێگیر کرا و هەموو دەقەکە تەنها بەهایەک بوو. بەدوای گەڕا کە ڕێک ناوی ' OR '1'='1 بێت و هیچ نییە.
A product page lets users sort by price, "low to high" or "high to low". The developer wants to put the choice into the query with a ?. Why will that not work, and what should he do?
لاپەڕەیەکی کاڵا ڕێگە بە دەدات بەپێی نرخ ڕیز بکەن، «کەم بۆ زۆر» یان «زۆر بۆ کەم». دەیەوێت هەڵبژاردنەکە بە ? بخاتە ناو . بۆچی ئەمە کار ناکات و دەبێت چی بکات؟
Show answerوەڵامەکە پیشان بدە
A ? can only hold a value, not an SQL keyword such as ASC or DESC. He should map the choice to a fixed allow-list in the program: "low to high" → ASC, "high to low" → DESC, anything else → refuse or use a default. The keyword then comes from his code, never from the user's text.
? تەنها دەتوانێت بەهایەک هەڵبگرێت، نەک وشەیەکی SQLـی وەک ASC یان DESC. دەبێت هەڵبژاردنەکە لە بەرنامەکەدا بە جێگیرەوە ببەستێتەوە: «کەم بۆ زۆر» ← ASC، «زۆر بۆ کەم» ← DESC، هەر شتێکی تر ← ڕەتکردنەوە یان . ئەو کاتە وشەکە لە کۆدی ئەوەوە دێت، هەرگیز لە دەقی نا.
Summary and reviewپوختە و پێداچوونەوە
- Injection happens when user input is mixed into an instruction, so an interpreter (database, shell, browser) runs part of it as code. OWASP Top 10:2025 ranks Injection number 5.
- SQL injection follows six steps from an input field to data theft. The classic
' OR '1'='1makes the WHERE condition true for every row, so every row comes back. - Parameterised queries are the main fix: the SQL is fixed first and the input is sent as a value. Least privilege, error hiding, encryption, patches, WAFs and audits are extra layers; escaping is a last resort.
- Heartland (2008): SQL injection opened the way to more than 130 million stolen card numbers and about $140 million in settlements.
- Command injection: avoid the shell; pass arguments separately; allow-list; least privilege.
- XSS runs the attacker's script in visitors' browsers. Encode output for its context; sanitize allowed HTML; add CSP and HttpOnly cookies as extra layers.
- تێخزاندن ڕوودەدات کاتێک تێکەڵی فەرمانێک دەکرێت، بۆیە (، shell، ) بەشێکی وەک کۆد جێبەجێ دەکات. :2025 تێخزاندن دەخاتە پلەی 5.
- شەش هەنگاو لە خانەی تا دزینی دەبڕێت. نموونە کلاسیکییەکەی
' OR '1'='1بۆ هەموو ڕاست دەکات، بۆیە هەموو دەگەڕێنەوە. - چارەسەرە سەرەکییەکەن: SQL سەرەتا جێگیر دەکرێت و وەک بەها دەنێردرێت. ، شاردنەوەی هەڵە، ، ، WAF و چینی زیادەن؛ گۆڕینی هێماکان دوایین چارەیە.
- Heartland (2008): ڕێگای بۆ دزینی زیاتر لە 130 ملیۆن ژمارەی کارت و نزیکەی 140 ملیۆن دۆلار ڕێککەوتن کردەوە.
- : خۆت لە shell بەدوور بگرە؛ بە جیا بنێرە؛ ؛ .
- XSS لە سەردانکەراندا جێبەجێ دەکات. دەرخستە بەپێی شوێنەکەی بگۆڕە؛ HTMLـی ڕێگەپێدراو پاک بکەرەوە؛ CSP و HttpOnly وەک چینی زیادە زیاد بکە.
What makes a parameterised query safe?چی پرسێکی پارامیتەردار سەلامەت دەکات؟
The SQL is sent and fixed before the data; the data fills a slot as a value and can never change the command.
SQL پێش دەنێردرێت و جێگیر دەکرێت؛ وەک بەها شوێنێک پڕ دەکاتەوە و هەرگیز ناتوانێت فەرمانەکە بگۆڕێت.
Why is a WAF not enough against injection?بۆچی WAF دژی تێخزاندن بەس نییە؟
It only recognises known patterns and can be bypassed; the vulnerability stays in the code.
تەنها شێوە ناسراوەکان دەناسێتەوە و دەکرێت تێپەڕێنرێت؛ لە کۆدەکەدا دەمێنێتەوە.
What is the main defence against XSS?بەرگریی سەرەکی دژی XSS چییە؟
Context-aware output encoding (for example htmlspecialchars() in PHP, or a framework's automatic escaping).
گۆڕینی هێماکانی دەرخستە بەپێی شوێن (بۆ نموونە htmlspecialchars() لە PHP، یان گۆڕینی خۆکاری چوارچێوەیەک).
What can a ? placeholder not hold?شوێنگری ? چی هەڵناگرێت؟
Table or column names and SQL keywords such as ASC/DESC — use an allow-list for those.
ناوی یان و وشەکانی SQLـی وەک ASC/DESC — بۆ ئەوانە بەکار بهێنە.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Passwords, MFA and Access Controlتێپەڕەوشەکان، MFA و کۆنترۆڵی دەستڕاگەیشتن
Related lecturesوانە پەیوەندیدارەکان
- Securing Data in PHP and MySQLپاراستنی دراوە لە PHP و MySQL
- Form Security and Sticky Formsئاسایشی فۆرم و فۆرمە لکاوەکان
- Finding and Rating Vulnerabilities: Scanning, OWASP and CVSSدۆزینەوە و هەڵسەنگاندنی خاڵە لاوازەکان: پشکنین، OWASP و CVSS
- Database Security: Threats and Countermeasuresئاسایشی بنکەدراوە: هەڕەشەکان و ڕێوشوێنەکانی بەرگری
- Better SELECT Queries: Conditions, Ranges, Lists, Patterns and NULLباشترکردنی فەرمانی SELECT: مەرجەکان، ماوەکان، لیست، شێوازی دەق و NULL
- Where Vulnerabilities Come Fromخاڵە لاوازەکان لە کوێوە دێن
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- OWASP Top 10:2025 — A05 Injection
- OWASP Cheat Sheet Series: SQL Injection Prevention Cheat Sheet
- OWASP Cheat Sheet Series: OS Command Injection Defense Cheat Sheet
- OWASP Cheat Sheet Series: Cross Site Scripting Prevention Cheat Sheet
- US Department of Justice: Alleged international hacker indicted for massive attack on U.S. retail and banking networks (17 August 2009)
- IEEE Spectrum: Heartland slowly but steadily settles IT breach lawsuits
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.