Chapterبەش 8 · Lectureوانە 8.3
Real Incidents: From MoneyGram to GPS Spoofingڕووداوە ڕاستەقینەکان: لە MoneyGramـەوە تا هەڵخەڵەتاندنی GPS
Real incidents told with checked facts: MoneyGram (September 2024, help-desk social engineering) and why local companies stay quiet, the SolarWinds supply-chain attack and its attribution, supply-chain tampering, the UK Ministry of Defence payroll breach, ransomware at Indonesia's national data centre, the CrowdStrike outage that was not an attack, how to treat unconfirmed leak claims, and GPS jamming and spoofing — with Baghdad among EASA's affected regions. The last lesson of the course ends with a summary of the whole course and what to learn next.
ڕووداوە ڕاستەقینەکان بە زانیاریی پشکنراو: MoneyGram (ئەیلوولی 2024، ) و بۆچی کۆمپانیا ناوخۆییەکان بێدەنگ دەبن، SolarWinds و ، دەستکاریکردنی زنجیرەی دابینکردن، دزەکردنی سیستەمی مووچەی وەزارەتی بەرگریی بەریتانیا، لە ناوەندی نیشتیمانیی ئیندۆنیزیا، وەستانەکەی CrowdStrike کە نەبوو، چۆن مامەڵە لەگەڵ بانگەشەی دزەکردنی پشتڕاستنەکراوە بکەیت و و — بەغدا لە نێو ناوچە کاریگەرەکانی EASAـدایە. دوا وانەی کۆرسەکە بە پوختەی هەموو کۆرسەکە و ئەوەی دواتر فێری ببیت کۆتایی دێت.
What you will learnچی فێر دەبیت
- Read an incident story critically: date, victim, entry point, impact, attribution and confidence.
- Describe the MoneyGram, SolarWinds, UK MoD payroll and Indonesian data-centre incidents with correct facts and the lesson of each.
- Explain why the CrowdStrike outage was not an attack, and why it still matters for availability and resilience.
- Distinguish GPS jamming from spoofing, and name defences including cross-checking and signed signals.
- Summarise the whole course and choose what to learn next.
- چیرۆکی ڕووداوێک بە ڕەخنەگرانە بخوێنیتەوە: بەروار، قوربانی، خاڵی چوونە ژوورەوە، کاریگەری، و ئاستی دڵنیایی.
- ڕووداوەکانی MoneyGram، SolarWinds، مووچەی وەزارەتی بەرگریی بەریتانیا و ناوەندی ئیندۆنیزیا بە زانیاریی دروست و وانەی هەریەکەیان وەسف بکەیت.
- ڕوونی بکەیتەوە بۆچی وەستانەکەی CrowdStrike نەبوو و بۆچی هێشتا بۆ و خۆڕاگری گرنگە.
- لە جیا بکەیتەوە و بەرگرییەکان ناو بهێنیت، بە بەراوردکردن و واژووکراویشەوە.
- هەموو کۆرسەکە کورت بکەیتەوە و هەڵبژێریت دواتر چی فێر ببیت.
How to read an incident storyچۆن چیرۆکی ڕووداوێک بخوێنیتەوە
The report ends with real stories, from Kurdistan and from abroad, of cyber incidents that touched national security. This lesson tells them with checked facts. Incident stories spread fast and change as they spread, so before you repeat one, ask five questions:
ڕاپۆرتەکە بە چیرۆکی ڕاستەقینە کۆتایی دێت، لە کوردستان و لە دەرەوە، دەربارەی ڕووداوە سایبەرییەکان کە کاریگەرییان لەسەر هەبوو. ئەم وانەیە بە زانیاریی پشکنراو دەیانگێڕێتەوە. چیرۆکی ڕووداوەکان خێرا بڵاو دەبنەوە و لە کاتی بڵاوبوونەوەدا دەگۆڕێن، بۆیە پێش ئەوەی یەکێکیان دووبارە بکەیتەوە، پێنج پرسیار بکە:
- When?کەی؟
The exact month and year, from a dated report. Many mistakes start with a wrong date.
مانگ و ساڵی ورد، لە ڕاپۆرتێکی بەرواردار. زۆر هەڵە بە بەروارێکی هەڵە دەست پێ دەکەن.
- Who was hit?کێ زیانی پێ گەیشت؟
The organisation, and who depended on it.
ڕێکخراوەکە و ئەوانەی پشتیان پێی دەبەست.
- How did the attackers get in?هێرشبەرەکان چۆن چوونە ژوورەوە؟
The entry point: a password, a help desk, an update, an unpatched hole — or was it no attack at all?
خاڵی چوونە ژوورەوە: ، ، ، کونێکی پینەنەکراو — یان هەر نەبوو؟
- What was the impact?کاریگەرییەکەی چی بوو؟
Which corner of the CIA triad was hurt: confidentiality (data stolen), integrity (data changed) or availability (service stopped)?
کام گۆشەی زیانی پێ گەیشت: ( دزرا)، ( گۆڕدرا) یان (خزمەتگوزاری وەستا)؟
- Who did it — and how sure are we?کێ کردی — و چەند دڵنیاین؟
Attribution takes time and is rarely certain. Many attacks are never officially attributed.
کاتی دەوێت و کەم جار دڵنیایە. زۆر هەرگیز بە فەرمی بکەرەکەیان دیاری ناکرێت.
Deciding, from technical evidence and intelligence, who is behind a . It is slow and rarely certain, so governments say how confident they are, and many attacks are never officially attributed.
بڕیاردانە، لەسەر بنەمای بەڵگەی تەکنیکی و هەواڵگری، کە کێ لە پشت بووە. کارێکی هێواشە و کەم جار دڵنیایە، بۆیە حکومەتەکان دەڵێن چەند دڵنیان، هەروەها زۆر هێرش هەرگیز بە فەرمی بکەرەکەیان دیاری ناکرێت.
How to read an incident storyچۆن چیرۆکی ڕووداوێک بخوێنیتەوە
The incidents in this lessonڕووداوەکانی ئەم وانەیە
| Incidentڕووداو | Whenکەی | What kindچ جۆرێک | Main harmزیانی سەرەکی |
|---|---|---|---|
| MoneyGram | September 2024ئەیلوولی 2024 | Social engineering of a help desk | Availability (5-day outage) and confidentiality (customer data stolen) (5 ڕۆژ وەستان) و ( کڕیاران دزرا) |
| SolarWinds | 2020 | Software supply-chain attack | Confidentiality (espionage) (سیخوڕی) |
| UK Ministry of Defence payrollسیستەمی مووچەی وەزارەتی بەرگریی بەریتانیا | May 2024ئایاری 2024 | Breach at a contractorدزەکردن لە لای بەڵێندەرێک | Confidentiality (personal data) ( کەسی) |
| Indonesia's national data centreناوەندی نیشتیمانیی ئیندۆنیزیا | June 2024حوزەیرانی 2024 | Ransomware | Availability (210 institutions) (210 دامەزراوە) |
| CrowdStrike | July 2024تەممووزی 2024 | Faulty update — not an attack هەڵە — نەبوو | Availability (8.5 million PCs) (8.5 ملیۆن ) |
| GPS interferenceتێکدانی | Since 2022لە 2022ـەوە | Jamming and spoofing و | Integrity of position data شوێن |
MoneyGram (September 2024): five days without transfersMoneyGram (ئەیلوولی 2024): پێنج ڕۆژ بێ ناردنی پارە
People in Kurdistan send and receive money from abroad through several services, including mobile wallets. Some of these services work with MoneyGram, an American company that moves money between countries; it is available in about 200 countries and has offered transfers in Iraq through local partners since 2015.
خەڵکی کوردستان لە ڕێگەی چەند خزمەتگوزارییەکەوە پارە بۆ دەرەوە دەنێرن و لە دەرەوە وەردەگرن، لەوانە جزدانی مۆبایل. هەندێک لەم خزمەتگوزارییانە لەگەڵ MoneyGram کار دەکەن، کۆمپانیایەکی ئەمریکی کە پارە لە نێوان وڵاتاندا دەگوازێتەوە؛ لە نزیکەی 200 وڵاتدا بەردەستە و لە 2015ـەوە لە ڕێگەی هاوبەشە ناوخۆییەکانەوە ناردنی پارەی لە عێراقدا پێشکەش کردووە.
On 20 September 2024 customers began reporting that transfers failed and the website was down. MoneyGram took its systems offline to contain an attack and on 23 September confirmed a 'cybersecurity issue'. Transfers worked again from about 25 September — roughly five days of outage, worldwide. According to a source quoted by BleepingComputer, the attackers got in through social engineering against the company's IT help desk: they tricked staff into giving them an employee's sign-in details, then went after the company's internal user directory (Windows Active Directory). MoneyGram said it had no evidence of ransomware, but in October it confirmed that the attackers, inside its systems from 20 to 22 September, had stolen customers' personal data such as names, contact details, ID documents and bank account numbers.
لە 20ـی ئەیلوولی 2024 کڕیاران دەستیان کرد بە ڕاپۆرتکردنی ئەوەی کە ناردنی پارە سەرناکەوێت و کار ناکات. MoneyGram سیستەمەکانی کوژاندەوە بۆ ئەوەی سنووردار بکات و لە 23ـی ئەیلوول پشتڕاستی کردەوە کە «کێشەیەکی » هەیە. ناردنی پارە لە نزیکەی 25ـی ئەیلوولـەوە دووبارە کاری کردەوە — نزیکەی پێنج ڕۆژ وەستان، لە هەموو جیهاندا. بەپێی سەرچاوەیەک کە BleepingComputer گوتەی هێناوەتەوە، دژی ITـی کۆمپانیاکە بەکار هێنا: کارمەندانیان هەڵخەڵەتاند بۆ ئەوەی کارمەندێکیان بدەنێ، پاشان بەدوای لیستی ناوخۆیی کۆمپانیاکەدا چوون (Windows Active Directory). MoneyGram گوتی هیچ بەڵگەیەکی نییە، بەڵام لە تشرینی یەکەمدا پشتڕاستی کردەوە کە ، کە لە 20 تا 22ـی ئەیلوول لە ناو سیستەمەکانیدا بوون، کڕیارانیان دزیوە، وەک ناو، زانیاریی پەیوەندی، بەڵگەنامەی ناسنامە و ژمارەی حسابی بانکی.
MoneyGram (September 2024): five days without transfersMoneyGram (ئەیلوولی 2024): پێنج ڕۆژ بێ ناردنی پارە
What the MoneyGram attack teachesئەوەی هێرشی MoneyGram فێرمان دەکات
Because MoneyGram's whole network was down, every service that sends money through it stopped too — including transfers to and from Iraq. The report's authors noticed the outage through a local mobile wallet.
لەبەر ئەوەی هەموو MoneyGram وەستابوو، هەموو ئەو خزمەتگوزارییانەی لە ڕێگەیەوە پارە دەنێرن وەستان — ناردنی پارە بۆ عێراق و لە عێراقیشەوە. نووسەرانی ڕاپۆرتەکە وەستانەکەیان لە ڕێگەی جزدانێکی مۆبایلی ناوخۆییەوە بینی.
MoneyGram (September 2024): five days without transfersMoneyGram (ئەیلوولی 2024): پێنج ڕۆژ بێ ناردنی پارە
Why we hear so little about local incidentsبۆچی کەم دەربارەی ڕووداوە ناوخۆییەکان دەبیستین
The report's authors wanted to show real incidents from Kurdistan but found almost none to cite. Two reasons: there are fewer local technology companies, and even when companies are attacked they usually do not announce it, mainly to protect their reputation and not to lose customers and subscribers.
نووسەرانی ڕاپۆرتەکە ویستیان ڕووداوی ڕاستەقینە لە کوردستانەوە پیشان بدەن، بەڵام نزیکەی هیچیان نەدۆزییەوە کە ئاماژەی پێ بدەن. دوو هۆکار: کۆمپانیای تەکنەلۆجیای ناوخۆیی کەمترن، هەروەها تەنانەت کاتێک دەکرێتە سەر کۆمپانیاکان، زۆرجار ڕایناگەیەنن، بەپلەی یەکەم بۆ پاراستنی ناوبانگ و بۆ ئەوەی کڕیار و بەشداربوو لەدەست نەدەن.
Silence feels safe for the company but costs everyone else: customers do not know to change their passwords, other companies cannot learn from the case, and the same attackers try again elsewhere. That is why many countries now have breach-notification rules — in the EU's GDPR, for example, a serious personal-data breach must be reported to the authority within 72 hours (Breach notification). Iraq has no personal-data protection law yet (see Iraq and the Kurdistan Region today).
بێدەنگی بۆ کۆمپانیاکە سەلامەت دەردەکەوێت، بەڵام تێچووی بۆ هەموو کەسێکی تر هەیە: کڕیاران نازانن بگۆڕن، کۆمپانیاکانی تر ناتوانن لە ڕووداوەکە فێر ببن، هەروەها هەمان لە شوێنێکی تر هەوڵ دەدەنەوە. هەر بۆیە ئێستا زۆر وڵات یاسای هەیە — بۆ نموونە لە GDPRـی یەکێتیی ئەوروپادا، جددیی کەسی دەبێت لە 72 کاتژمێردا بە دەسەڵاتی پەیوەندیدار ڕابگەیەنرێت (ئاگادارکردنەوەی دزەکردنی دراوە). عێراق هێشتا یاسای پاراستنی کەسیی نییە (سەیری عێراق و هەرێمی کوردستان ئەمڕۆ بکە).
SolarWinds (2020): a poisoned updateSolarWinds (2020): نوێکردنەوەیەکی ژەهراوی
SolarWinds is an American company that makes software to help organisations manage their computer networks. One of its products, Orion, was used by about 33,000 public and private organisations — including many US government institutions, which made it a valuable target.
SolarWinds کۆمپانیایەکی ئەمریکییە کە دروست دەکات بۆ یارمەتیدانی ڕێکخراوەکان لە بەڕێوەبردنی . یەکێک لە بەرهەمەکانی، Orion، لەلایەن نزیکەی 33,000 ڕێکخراوی گشتی و تایبەتەوە بەکار دەهات — لەوانە زۆرێک لە دامەزراوە حکومییەکانی ئەمریکا، ئەمەش کردییە ئامانجێکی بەنرخ.
In 2020 attackers broke into SolarWinds and hid malicious code inside Orion's software updates (the company was first compromised around March 2020). Customers downloaded the new version as usual — it came from the real company — and the hidden code opened a back door into their networks. SolarWinds told the US Securities and Exchange Commission in December 2020 that fewer than 18,000 customers may have installed an infected version. The attackers then chose a much smaller number of victims to go deeper, and stole sensitive information.
لە 2020دا دزەیان کردە ناو SolarWinds و کۆدی زیانبەخشیان لە ناو Orionـدا شاردەوە (کۆمپانیاکە یەکەم جار نزیکەی ئاداری 2020 دزەی پێ کرا). کڕیاران وەشانە نوێیەکەیان وەک هەمیشە دابەزاند — لە کۆمپانیا ڕاستەقینەکەوە هاتبوو — و کۆدە شاراوەکە بۆ ناو کردەوە. SolarWinds لە کانوونی یەکەمی 2020دا بە دەستەی ئاسایشی بازاڕی پشکی ئەمریکای ڕاگەیاند کە کەمتر لە 18,000 کڕیار لەوانەیە وەشانێکی تووشبوویان دامەزراندبێت. پاشان ژمارەیەکی زۆر کەمتر لە قوربانییەکانیان هەڵبژارد بۆ ئەوەی قووڵتر بچنە ناوەوە و هەستیاریان دزی.
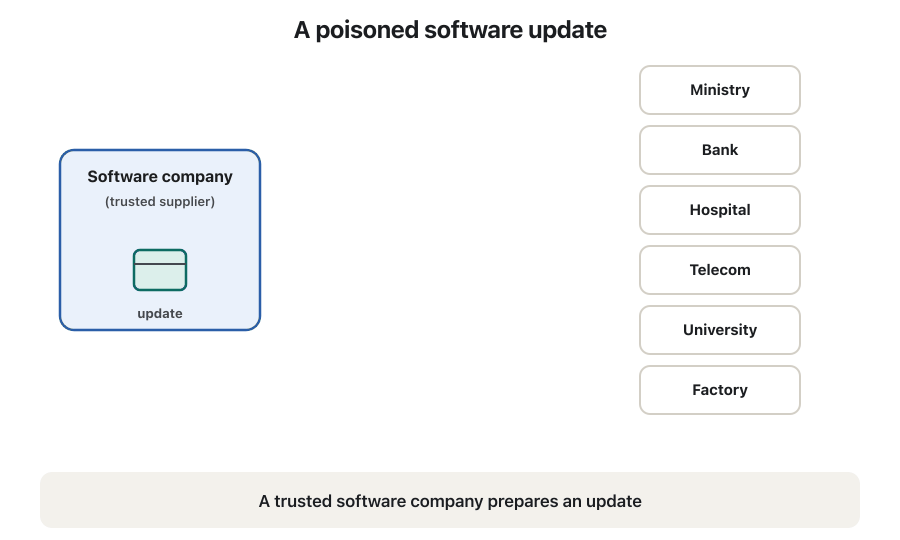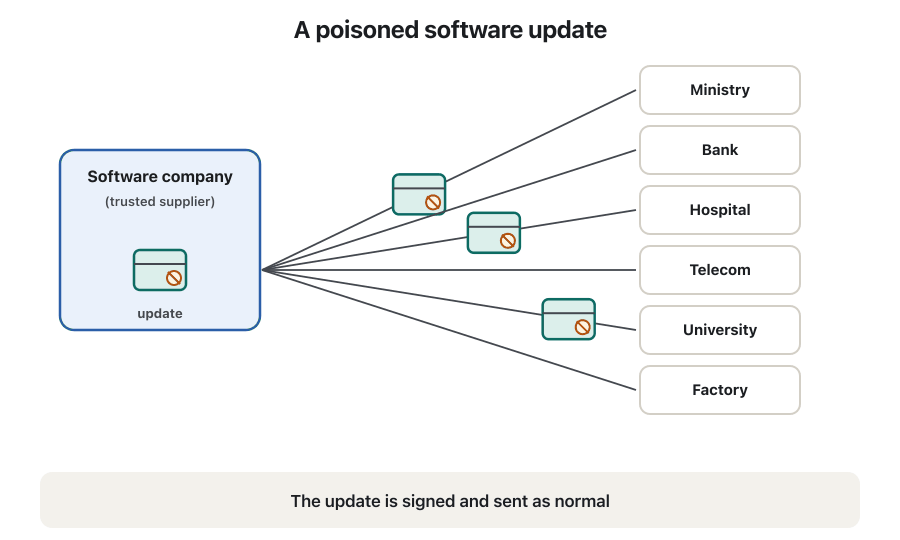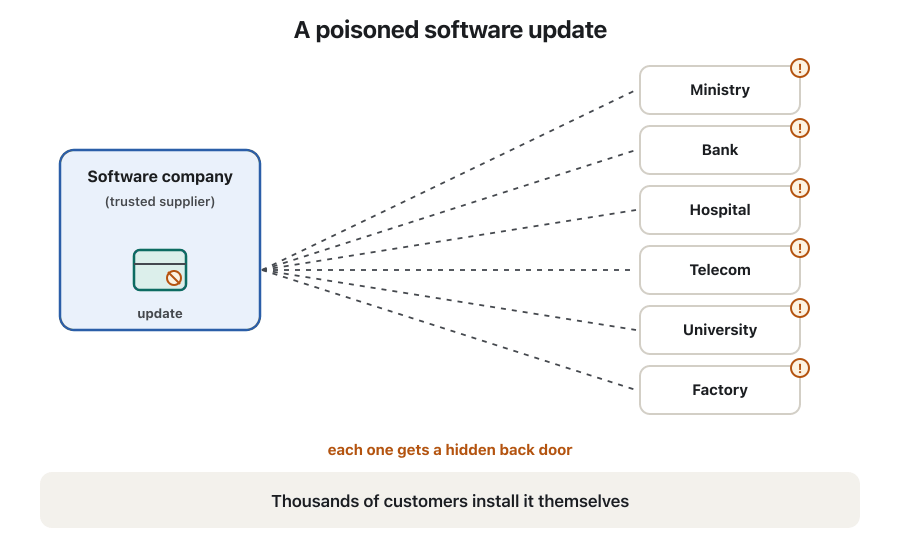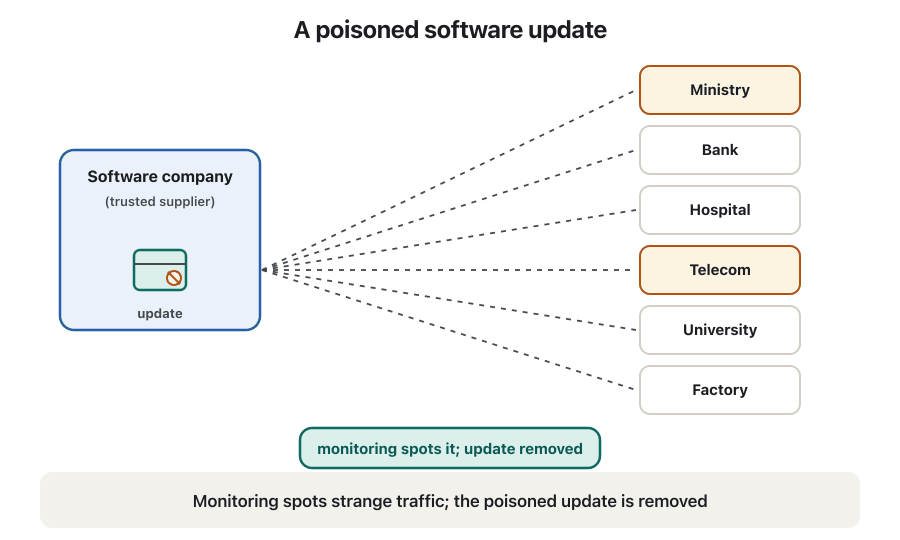
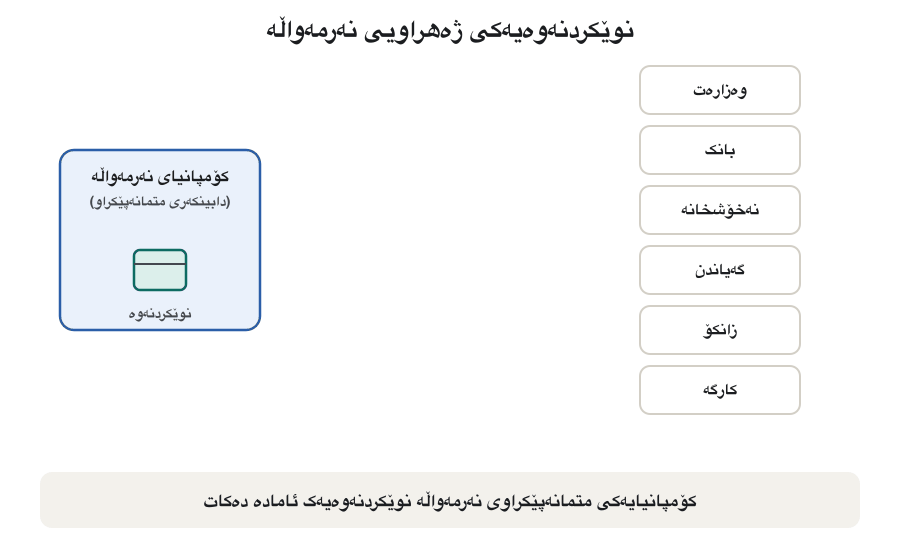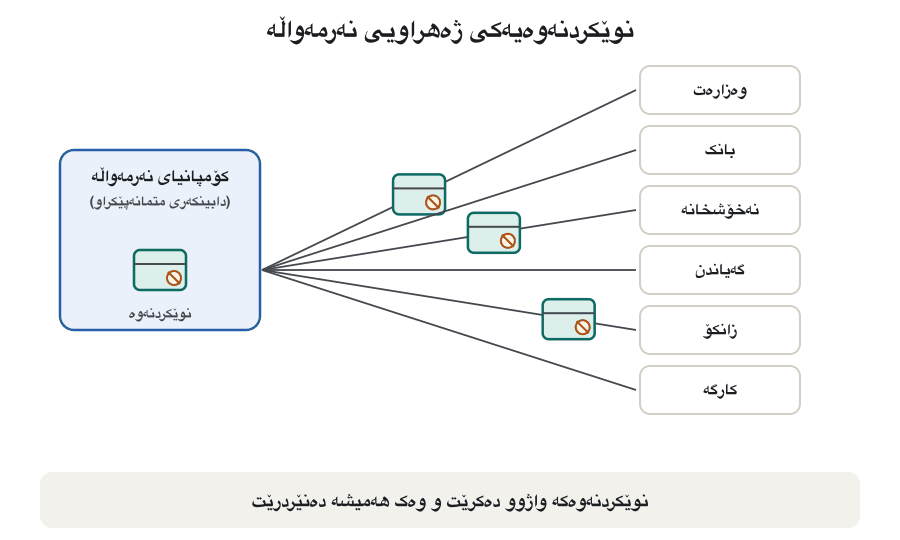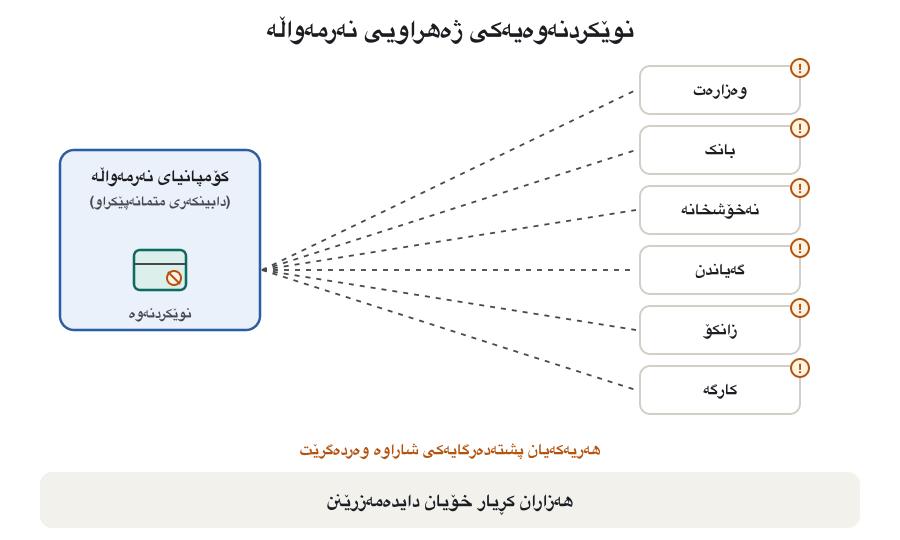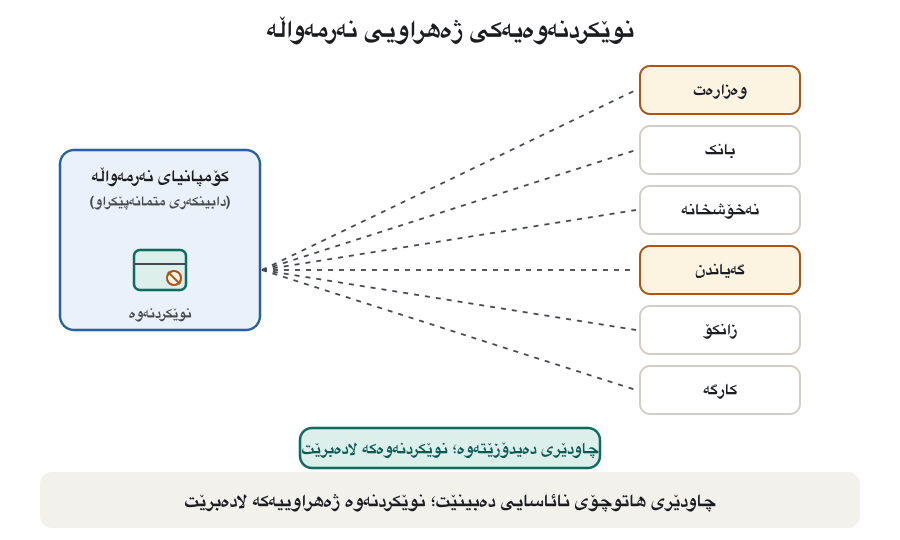
How attackers hid malicious code inside SolarWinds Orion updates so thousands of customers installed a back door: a supply-chain attack explained simply.
چۆن کۆدی زیانبەخشیان لە ناو SolarWinds Orion شاردەوە تا هەزاران کڕیار دابمەزرێنن: بە سادەیی.
Orion and the infected update (0:26), supply-chain details (1:55), advanced persistent threats (3:12).
Orion و (0:26)، وردەکارییەکانی (1:55)، پێشکەوتووی بەردەوام (APT، 3:12).
SolarWinds (2020): a poisoned updateSolarWinds (2020): نوێکردنەوەیەکی ژەهراوی
Found in December 2020, attributed in April 2021لە کانوونی یەکەمی 2020 دۆزرایەوە، لە نیسانی 2021 بکەرەکەی دیاری کرا
The campaign was found in December 2020 by the security company FireEye, which had itself been hacked. On 15 April 2021 the US government formally attributed it, with 'high confidence', to Russia's foreign intelligence service (SVR), also known as APT29; the UK's NCSC agreed it was 'highly likely'. By then it was known to have reached nine US federal agencies and about 100 private companies.
هەڵمەتەکە لە کانوونی یەکەمی 2020دا لەلایەن کۆمپانیای FireEyeـەوە دۆزرایەوە، کە خۆی دزەی پێ کرابوو. لە 15ـی نیسانی 2021 حکومەتی ئەمریکا بە فەرمی، بە «دڵنیاییەکی بەرز»، دایە پاڵ دەزگای هەواڵگریی دەرەوەی ڕووسیا (SVR)، کە بە APT29یش ناسراوە؛ NCSCـی بەریتانیا هاوڕا بوو کە «بە ئەگەری زۆر» وایە. تا ئەو کاتە زانرا کە گەیشتبووە نۆ دەزگای فیدراڵیی ئەمریکا و نزیکەی 100 کۆمپانیای تایبەت.
SolarWinds (2020): a poisoned updateSolarWinds (2020): نوێکردنەوەیەکی ژەهراوی
Supply chains: software and hardwareزنجیرەی دابینکردن: نەرمەواڵە و ڕەقەواڵە
A supply-chain attack strikes a trusted supplier so that the harm reaches all of its customers. Software is not the only chain that can be poisoned: devices can be tampered with on their way to the buyer, too.
لە دابینکەرێکی متمانەپێکراو دەدات بۆ ئەوەی زیانەکە بگاتە هەموو کڕیارەکانی. تاکە زنجیرە نییە کە ژەهراوی بکرێت: ئامێرەکانیش دەکرێت لە ڕێگای گەیشتنیان بە کڕیار دەستکارییان بکرێت.
- Know your suppliers: buy software and devices from vendors who take security seriously, through official channels.
- Keep a list of the software, libraries and devices you use, so you can react quickly to a warning.
- Least privilege for tools: a monitoring tool such as Orion should not be able to reach everything.
- Watch for unusual behaviour even from trusted software: unexpected outgoing traffic was one of the SolarWinds signs.
- دابینکەرەکانت بناسە: و ئامێر لە دابینکەرانێک بکڕە کە بە جددی وەردەگرن، لە ڕێگەی کەناڵە فەرمییەکانەوە.
- لیستێک هەڵبگرە لەو ، کتێبخانە و ئامێرانەی بەکاریان دەهێنیت، بۆ ئەوەی بە خێرایی وەڵامی ئاگادارییەک بدەیتەوە.
- بۆ ئامرازەکان: ئامرازێکی چاودێریی وەک Orion نابێت بتوانێت بگاتە هەموو شتێک.
- چاودێریی ڕەفتاری نائاسایی بکە تەنانەت لە متمانەپێکراویشەوە: هاتوچۆی چاوەڕواننەکراوی دەرەوە یەکێک بوو لە نیشانەکانی SolarWinds.
UK Ministry of Defence payroll (May 2024)سیستەمی مووچەی وەزارەتی بەرگریی بەریتانیا (ئایاری 2024)
On 7 May 2024 the UK Defence Secretary told Parliament that attackers had broken into a payroll system run by an outside contractor for the armed forces — a system separate from the ministry's own network. It held mainly names and bank details, and in a few cases addresses, of serving regular and reserve personnel and some veterans: an estimated 270,000 records. The ministry took the system offline; salaries were still paid.
لە 7ـی ئایاری 2024 وەزیری بەرگریی بەریتانیا بە پەرلەمانی ڕاگەیاند کە دزەیان کردووەتە ناو سیستەمێکی مووچە کە بەڵێندەرێکی دەرەکی بۆ هێزە چەکدارەکان بەڕێوەی دەبرد — سیستەمێک کە لە خودی وەزارەتەکە جیا بوو. بە زۆری ناو و زانیاریی بانکی و لە چەند حاڵەتێکدا ناونیشانی سەربازانی ئێستا، یەدەگ و هەندێک سەربازی خانەنشینی تێدا بوو: نزیکەی 270,000 تۆمار. وەزارەتەکە سیستەمەکەی کوژاندەوە؛ مووچەکان هەر دران.
The lesson: third-party risk. An organisation can protect its own network well and still lose data through a supplier who handles that data. Contracts should require security, suppliers' access should be limited, and their systems should be checked.
وانەکە: لایەنی سێیەم. ڕێکخراوێک دەتوانێت خۆی بە باشی بپارێزێت و هێشتا لە ڕێگەی دابینکەرێکەوە کە ئەو بەڕێوە دەبات لەدەست بدات. گرێبەستەکان دەبێت داوای بکەن، دەستڕاگەیشتنی دابینکەران دەبێت سنووردار بێت و سیستەمەکانیان بپشکنرێن.
Indonesia's national data centre (June 2024)ناوەندی نیشتیمانیی دراوەی ئیندۆنیزیا (حوزەیرانی 2024)
Around 20 June 2024, ransomware called Brain Cipher — built from leaked LockBit code — hit Indonesia's Temporary National Data Centre, which hosted services for about 210 national and local institutions. Immigration systems went down, and long queues formed at the immigration gates of Jakarta's main airport. The attackers demanded US$8 million.
نزیکەی 20ـی حوزەیرانی 2024، بە ناوی Brain Cipher — کە لە کۆدی دزەکردووی LockBit دروست کرابوو — لە ناوەندی کاتیی نیشتیمانیی ئیندۆنیزیای دا، کە خزمەتگوزاریی بۆ نزیکەی 210 دامەزراوەی نیشتیمانی و ناوخۆیی هەڵدەگرت. سیستەمەکانی کۆچ و پاسەپۆرت وەستان و ڕیزی درێژ لە بەردەم دەروازەکانی پاسەپۆرتی فڕۆکەخانە سەرەکییەکەی جاکارتا دروست بوو. داوای 8 ملیۆن دۆلاریان کرد.
On 3 July the group published the decryption key for free. Afterwards the minister said that backups were now mandatory for every ministry using the centre — 'not optional anymore' — the government blamed careless password sharing by a user, and a senior official resigned.
لە 3ـی تەممووز گرووپەکە کردنەوەکەی بە خۆڕایی بڵاو کردەوە. دواتر وەزیرەکە گوتی ئێستا بۆ هەموو وەزارەتێک کە ناوەندەکە بەکار دەهێنێت ناچارین — «ئیتر ئارەزوومەندانە نین» — حکومەت هاوبەشکردنی بێئاگایانەی لەلایەن تاوانبار کرد، هەروەها بەرپرسێکی باڵا دەستی لەکار کێشایەوە.
CrowdStrike (July 2024): a global outage that was not an attackCrowdStrike (تەممووزی 2024): وەستانێکی جیهانی کە هێرش نەبوو
On 19 July 2024 at 04:09 UTC, the security company CrowdStrike sent a small configuration update ('Channel File 291') to its Falcon protection software on Windows computers. A logic error in it made those computers crash with a blue screen and restart again and again. The faulty file was replaced 78 minutes later, at 05:27 UTC, but machines that had already crashed often had to be fixed by hand, one by one. Microsoft estimated that 8.5 million Windows devices were affected — less than 1% of all Windows machines — yet airlines, hospitals, banks and broadcasters around the world stopped work. Mac and Linux computers were not affected.
لە 19ـی تەممووزی 2024 کاتژمێر 04:09ـی UTC، کۆمپانیای CrowdStrike بچووکی ڕێکخستنی («Channel File 291») بۆ پاراستنی Falcon لەسەر Windows نارد. تێیدا وای لەو کرد بە شاشەی شین بوەستن و جار لە دوای جار دەست پێ بکەنەوە. فایلە هەڵەکە 78 خولەک دواتر، لە 05:27ـی UTC، گۆڕدرا، بەڵام ئەو ئامێرانەی پێشتر وەستابوون زۆرجار دەبوو یەک بە یەک بە دەست چاک بکرێنەوە. Microsoft خەمڵاندی کە 8.5 ملیۆن ئامێری Windows کاریگەرییان لەسەر بوو — کەمتر لە 1%ـی هەموو ئامێرەکانی Windows — کەچی کۆمپانیاکانی فڕۆکەوانی، نەخۆشخانە، بانک و کەناڵەکانی پەخش لە هەموو جیهاندا لە کار وەستان. Mac و Linux کاریگەرییان لەسەر نەبوو.
How one faulty CrowdStrike update crashed Windows computers worldwide in July 2024, and why each machine had to be fixed by hand.
چۆن هەڵەی CrowdStrike لە تەممووزی 2024 Windows لە هەموو جیهاندا لە کار خست و بۆچی دەبوو هەر ئامێرێک بە دەست چاک بکرێتەوە.
A BBC explainer from the day: the outage, the manual fix (1:08), root cause and testing (2:33), why only Windows was hit (3:04).
ڕوونکردنەوەیەکی BBC لە هەمان ڕۆژدا: وەستانەکە، چاککردنەوەی دەستی (1:08)، هۆکاری بنەڕەتی و (2:33)، بۆچی تەنها Windows تووش بوو (3:04).
CrowdStrike (July 2024): a global outage that was not an attackCrowdStrike (تەممووزی 2024): وەستانێکی جیهانی کە هێرش نەبوو
Lessons from the outageوانەکانی وەستانەکە
What organisations learned from 19 July 2024:
ئەوەی ڕێکخراوەکان لە 19ـی تەممووزی 2024 فێر بوون:
- Test updates and roll them out in stages — a few computers first, then more — so a bad update stops early.
- Plan for working without computers — paper check-in at airports, paper records in hospitals (Business continuity).
- Do not depend on a single product everywhere for critical work, where it can be avoided.
- Beware of scams after a big outage — criminals send fake 'fix' messages while everyone is confused.
- تاقی بکەرەوە و بە قۆناغ بڵاویان بکەرەوە — سەرەتا چەند ، پاشان زیاتر — بۆ ئەوەی خراپ زوو ڕابگیرێت.
- پلان دابنێ بۆ کارکردن بەبێ — پشکنینی کاغەزی لە فڕۆکەخانەکان، تۆماری کاغەزی لە نەخۆشخانەکان (بەردەوامیی کار).
- پشت بە یەک بەرهەم لە هەموو شوێنێک مەبەستە بۆ کاری گرنگ، ئەگەر بکرێت.
- دوای وەستانێکی گەورە ئاگاداری فێڵ بە — تاوانباران لە کاتی شڵەژانی هەمووان نامەی ساختەی «چارەسەر» دەنێرن.
Claims are not confirmed incidentsبانگەشە ڕووداوی پشتڕاستکراوە نییە
Criminals often post on 'leak forums' that they have stolen a database — of a company, a bank or a ministry — and show a few sample lines to prove it. Some claims are true. Others are old data from an earlier leak, data from a different organisation, or plain lies told to gain fame or to scare the victim into paying.
تاوانباران زۆرجار لە «مەکۆکانی دزەپێکردن»دا بڵاو دەکەنەوە کە — هی کۆمپانیایەک، بانکێک یان وەزارەتێک — یان دزیوە و چەند دێڕێکی نموونە پیشان دەدەن بۆ سەلماندنی. هەندێک بانگەشە ڕاستن. هەندێکی تر کۆنی دزەکردنێکی پێشووترن، ڕێکخراوێکی ترن، یان تەنها درۆن بۆ بەدەستهێنانی ناوبانگ یان ترساندنی قوربانی بۆ ئەوەی پارە بدات.
- Wait for confirmationچاوەڕێی پشتڕاستکردنەوە بکە
From the organisation itself, a national CERT or a reliable news outlet that checked the data.
لە خودی ڕێکخراوەکە، نیشتیمانی یان دەزگایەکی هەواڵی باوەڕپێکراو کە پشکنیوە.
- Say 'claimed', not 'happened'بڵێ «بانگەشەی کراوە»، نەک «ڕوویدا»
Until it is confirmed, a claim is only a claim.
تا پشتڕاست نەکرێتەوە، بانگەشە تەنها بانگەشەیە.
- Never download or share leaked dataهەرگیز دراوەی دزەکردوو دامەبەزێنە یان هاوبەشی مەکە
It harms the people in it, may be illegal, and leak files often carry malware.
زیان بەو کەسانە دەگەیەنێت کە تێیدان، لەوانەیە نایاسایی بێت، هەروەها فایلەکانی دزەکردن زۆرجار تێدایە.
- Protect yourself anywayبەهەرحاڵ خۆت بپارێزە
If you might be affected, change that password and turn on MFA — it costs nothing.
ئەگەر لەوانەیە کاریگەریت لەسەر بێت، ئەو بگۆڕە و MFA چالاک بکە — هیچی تێناچێت.
GPS under attack: jamming and spoofingGPS لە ژێر هێرشدا: شێواندن و هەڵخەڵەتاندن
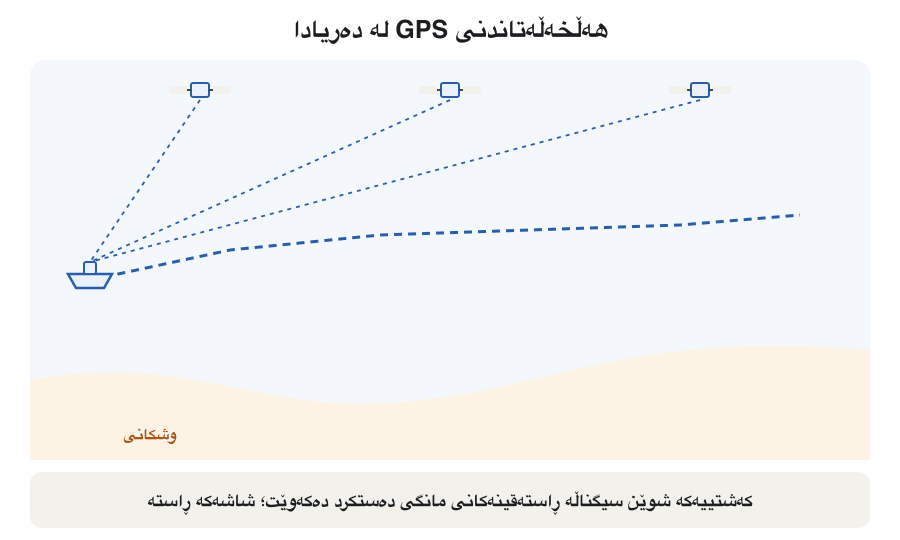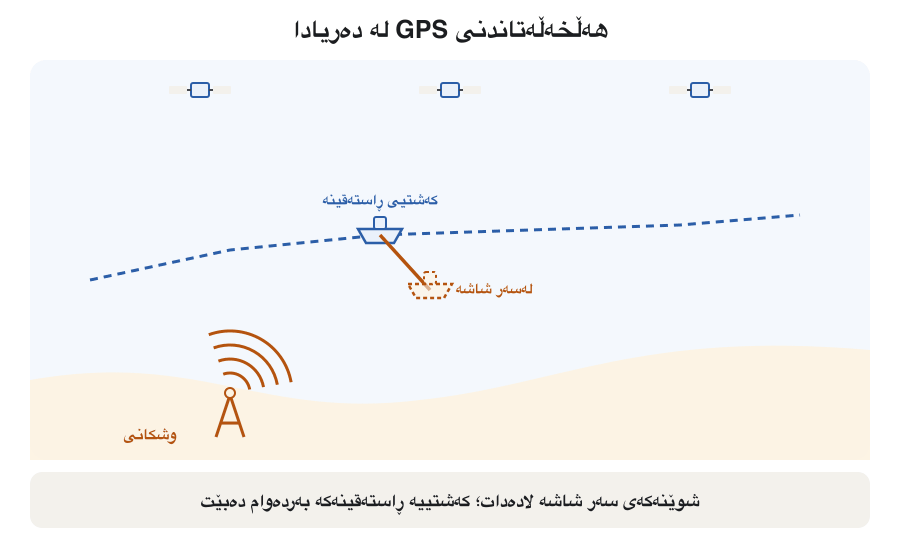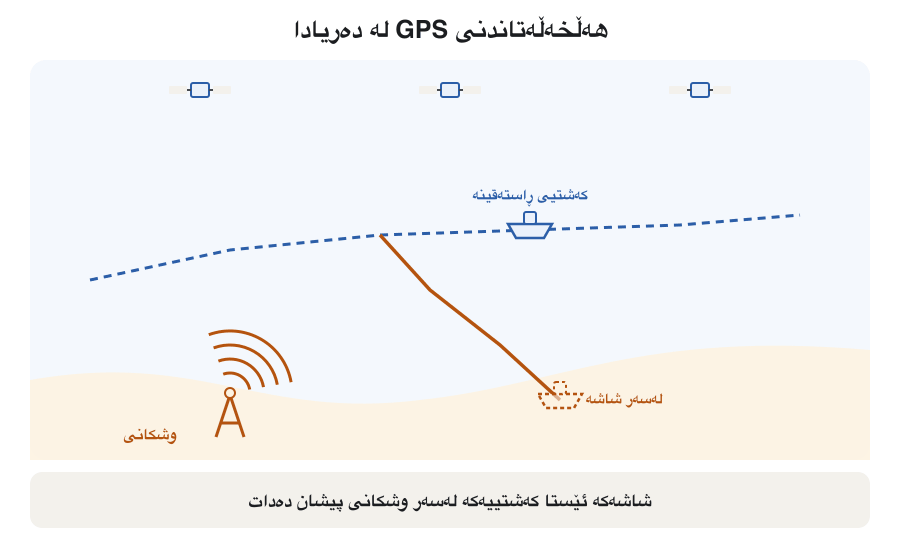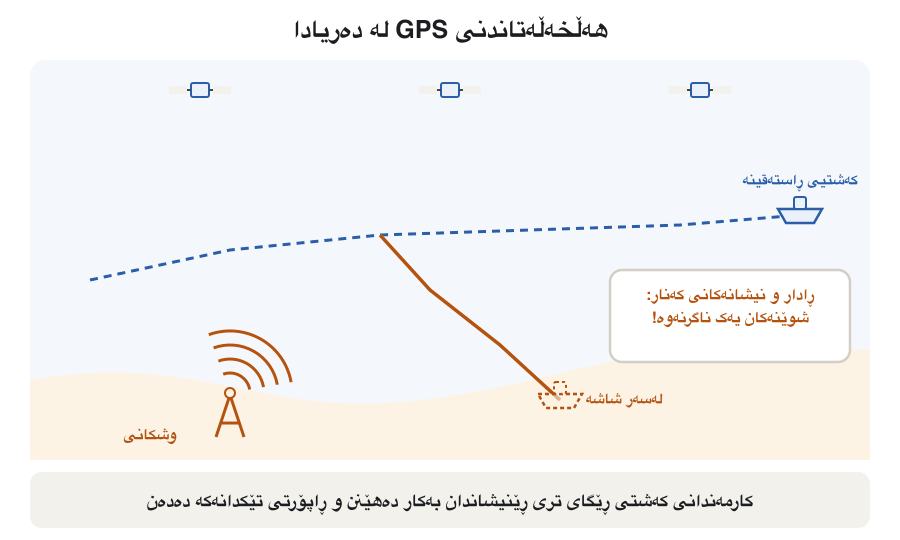
GPS (Global Positioning System) tells phones, cars, ships and planes where they are, from satellite signals; how it works is explained in How GPS finds you. Today receivers also use Europe's Galileo, Russia's GLONASS and China's BeiDou — together called GNSS. No system is 100% secure, and GPS can be attacked too. By the time they reach Earth from about 20,000 km away, satellite signals are very weak — and that is the weakness attackers use.
(Global Positioning System) لە ڕێگەی مانگە دەستکردەکانەوە بە مۆبایل، ئۆتۆمبێل، کەشتی و فڕۆکە دەڵێت لە کوێن؛ چۆنیەتیی کارکردنی لە GPS چۆن شوێنەکەت دەدۆزێتەوەدا ڕوون کراوەتەوە. ئەمڕۆ وەرگرەکان Galileoـی ئەوروپا، GLONASSـی ڕووسیا و BeiDouـی چینیش بەکار دەهێنن — پێکەوە پێیان دەگوترێت GNSS. هیچ سیستەمێک سەدا سەد پارێزراو نییە و GPSیش دەکرێت بکرێتە سەر. کاتێک مانگە دەستکردەکان لە دووریی نزیکەی 20,000 کیلۆمەترەوە دەگەنە زەوی، زۆر لاوازن — ئەمەش ئەو کە بەکاری دەهێنن.
| Questionپرسیار | Jamming | Spoofing |
|---|---|---|
| What the attacker sends چی دەنێرێت | Strong radio noiseژاوەژاوی ڕادیۆیی بەهێز | Fake satellite-like signals, stronger than the real ones ساختە وەک هی مانگی دەستکرد، بەهێزتر لە ڕاستەقینەکان |
| What the receiver doesوەرگرەکە چی دەکات | Loses the signal and its position و شوێنەکەی لەدەست دەدات | Accepts the fake signal as real and calculates a wrong position or time ساختەکە وەک ڕاستەقینە وەردەگرێت و شوێن یان کاتێکی هەڵە دەژمێرێت |
| Does the user notice? هەست پێ دەکات؟ | Usually yes: 'no signal'زۆرجار بەڵێ: « نییە» | Often not: the map looks normalزۆرجار نا: نەخشەکە ئاسایی دەردەکەوێت |
The difference between GPS jamming and spoofing, where interference happens today, and how airline pilots notice it and keep flying safely.
جیاوازیی و ، ئەمڕۆ لە کوێ تێکدانی ڕوودەدات و فڕۆکەوانەکان چۆن هەستی پێ دەکەن و بە سەلامەتی بەردەوام دەبن.
Jamming vs spoofing (0:32), a real spoofing event on a flight (0:52), how pilots respond (1:45).
بەرامبەر (0:32)، ڕووداوێکی ڕاستەقینەی لە گەشتێکی ئاسمانیدا (0:52)، فڕۆکەوانەکان چۆن وەڵام دەدەنەوە (1:45).
GPS under attack: jamming and spoofingGPS لە ژێر هێرشدا: شێواندن و هەڵخەڵەتاندن
How the report explains spoofingڕاپۆرتەکە چۆن هەڵخەڵەتاندنی GPS ڕوون دەکاتەوە
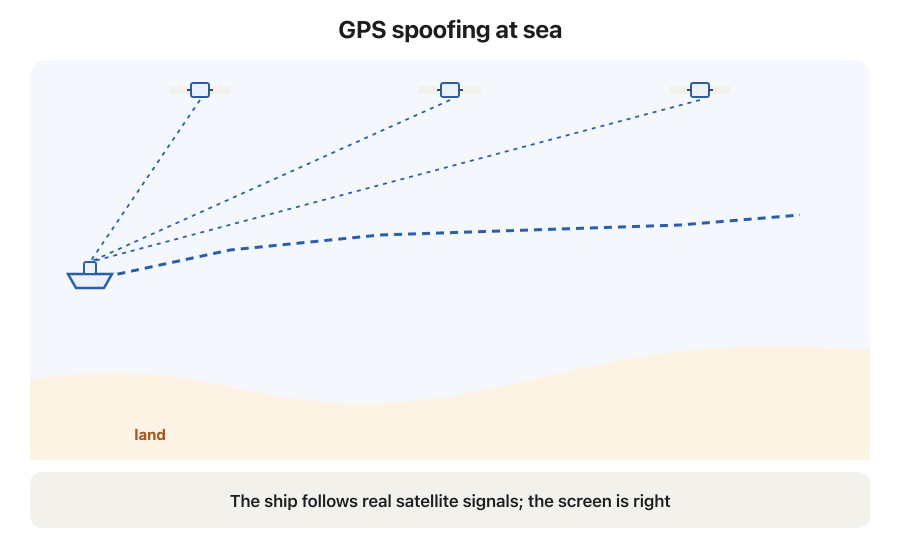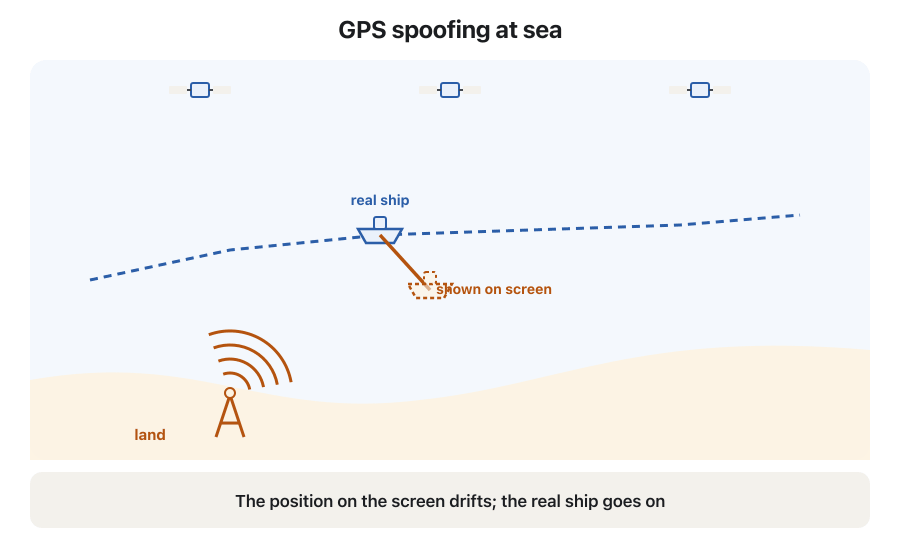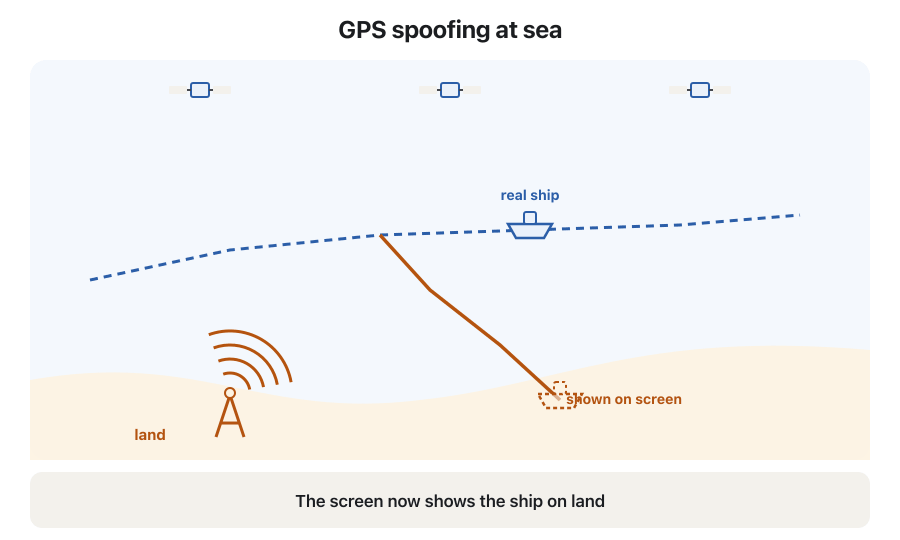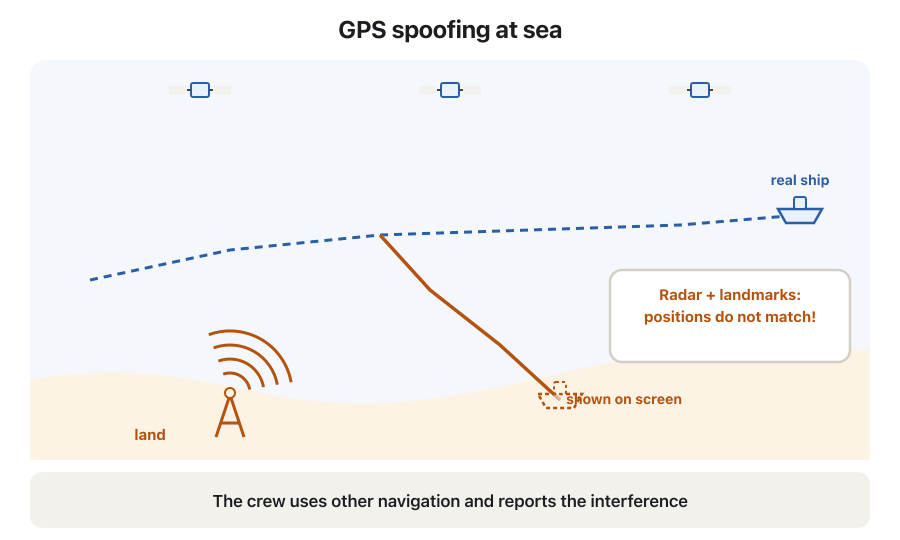
The report explains spoofing this way: the attacker creates a fake GPS signal that is stronger than the original, so the receiver mistakenly accepts it as the real one. Spoofing is a subtle threat («هەڕەشەی سایبەری», as the Kurdish report explains the English word cyberthreat): it does not stop the device, it makes the device believe a lie.
ڕاپۆرتەکە بەم شێوەیە ڕوون دەکاتەوە: ساختەی GPS دروست دەکات کە لە ڕەسەنەکە بەهێزترە، بۆیە وەرگرەکە بە هەڵە وەک ڕاستەقینە وەری دەگرێت. وردە (وەک ڕاپۆرتە کوردییەکە وشەی ئینگلیزیی cyberthreat ڕوون دەکاتەوە): ئامێرەکە ناوەستێنێت، وای لێ دەکات باوەڕ بە درۆیەک بکات.
GPS under attack: jamming and spoofingGPS لە ژێر هێرشدا: شێواندن و هەڵخەڵەتاندن
GPS interference in our regionتێکدانی GPS لە ناوچەکەماندا
This is not only theory. The EU Aviation Safety Agency (EASA) reports a notable increase in GNSS jamming and spoofing since February 2022, especially near conflict zones — in the Black Sea, the Baltic, the eastern Mediterranean and the Middle East. EASA publishes tables of the flight-information regions with the most reported interference; its tables of 14 October 2026 include Baghdad.
ئەمە تەنها تیۆری نییە. دەزگای سەلامەتیی فڕۆکەوانیی یەکێتیی ئەوروپا (EASA) ڕایدەگەیەنێت کە لە شوباتی 2022ـەوە شێواندن و GNSS بە شێوەیەکی بەرچاو زیادی کردووە، بەتایبەتی نزیک ناوچەکانی ململانێ — لە دەریای ڕەش، باڵتیک، ڕۆژهەڵاتی دەریای ناوەڕاست و ڕۆژهەڵاتی ناوەڕاست. EASA خشتەی ئەو ناوچانەی زانیاریی فڕین بڵاو دەکاتەوە کە زۆرترین شێواندنیان تێدا ڕاپۆرت کراوە؛ خشتەکانی 14ـی تشرینی یەکەمی 2026 بەغدایان تێدایە.
What crews notice, according to EASA: positions that disagree, a strange difference between ground speed and air speed, clocks that jump, and false terrain warnings. On the ground, people near affected areas sometimes see their phone's map put them somewhere they are not, and ships' tracking systems have shown vessels in impossible places.
ئەوەی کارمەندانی فڕۆکە هەستی پێ دەکەن، بەپێی EASA: شوێنەکان یەک ناگرنەوە، جیاوازییەکی سەیر لە نێوان خێرایی سەر زەوی و خێرایی ئاسماندا، کاتژمێرەکان باز دەدەن، هەروەها ئاگادارکردنەوەی ساختەی نزیکبوونەوە لە زەوی. لەسەر زەوی، خەڵکی نزیک ناوچە کاریگەرەکان هەندێک جار دەبینن نەخشەی مۆبایلەکەیان لە شوێنێکدا دایاندەنێت کە لێی نین، هەروەها سیستەمەکانی بەدواداچوونی کەشتی، کەشتییەکانیان لە شوێنی مەحاڵدا پیشان داوە.
GPS under attack: jamming and spoofingGPS لە ژێر هێرشدا: شێواندن و هەڵخەڵەتاندن
Defending against GPS attacksبەرگری دژی هێرشەکانی GPS
The report recommends that military agencies use anti-spoofing GPS systems to be ready for such threats; the presentation adds that anti-spoofing technology protects critical infrastructure — power grids, telecom networks and banks also use GPS time. Practical defences today:
ڕاپۆرتەکە پێشنیار دەکات دەزگا سەربازییەکان سیستەمی GPSـی دژە- بەکار بهێنن بۆ ئەوەی ئامادە بن بۆ لەم جۆرە؛ پێشکەشکردنەکە زیاد دەکات کە تەکنەلۆجیای دژە- دەپارێزێت — تۆڕەکانی کارەبا، گەیاندن و بانکەکانیش کاتی GPS بەکار دەهێنن. بەرگرییە پراکتیکییەکانی ئەمڕۆ:
- Cross-check with other sources: radar, radio navigation aids, inertial systems, landmarks. EASA's advice to crews: verify the position by non-GNSS means and report.
- Smarter receivers: use several satellite systems at once, and flag sudden jumps or signals that are suspiciously strong.
- Signed signals: since 24 July 2025 Europe's Galileo offers a free service called OSNMA that adds a cryptographic signature to its navigation data, so a receiver can check that the data really comes from Galileo. It helps detect spoofing; it cannot stop jamming.
- Report it: reports from pilots and ships are how EASA builds its interference tables.
- بەراوردکردن لەگەڵ سەرچاوەی تر: ڕادار، ئامرازە ڕادیۆییەکانی ڕێنیشاندان، سیستەمی ناوەکی (inertial)، نیشانەکانی سەر زەوی. ئامۆژگاریی EASA بۆ کارمەندانی فڕۆکە: شوێنەکە بە ڕێگای جگە لە GNSS پشتڕاست بکەنەوە و ڕاپۆرت بدەن.
- وەرگری زیرەکتر: لە یەک کاتدا چەند سیستەمێکی مانگی دەستکرد بەکار بهێنن و بازی لەناکاو یان بە شێوەیەکی گوماناوی بەهێز دیاری بکەن.
- واژووکراو: لە 24ـی تەممووزی 2025ـەوە Galileoـی ئەوروپا خزمەتگوزارییەکی بێبەرانبەر بە ناوی OSNMA پێشکەش دەکات کە واژوویەکی بۆ ڕێنیشاندانەکەی زیاد دەکات، بۆیە وەرگر دەتوانێت بپشکنێت کە بە ڕاستی لە Galileoـەوە هاتووە. یارمەتی دۆزینەوەی دەدات؛ ناتوانێت ڕابگرێت.
- ڕاپۆرتی بکە: ڕاپۆرتی فڕۆکەوان و کەشتییەکان ئەوەیە کە EASA خشتەکانی شێواندنی پێ دروست دەکات.
The whole course on one pageهەموو کۆرسەکە لە یەک پەڕەدا
This is the last lesson of the Cybersecurity course. Here is the path you have walked, chapter by chapter. Each chapter title links to its first lesson.
ئەمە دوا وانەی کۆرسی . ئەمە ئەو ڕێگایەیە کە بڕیوتە، بەش بە بەش. ناونیشانی هەر بەشێک بەستراوە بە یەکەم وانەکەیەوە.
| Chapterبەش | The big ideaبیرۆکە سەرەکییەکە |
|---|---|
| Foundations of Cybersecurityبنەماکانی ئاسایشی سایبەر | What we protect (CIA), threats, vulnerabilities and attacks, who attacks and why, and the principles of good defence.ئەوەی دەیپارێزین (CIA)، ، و ، کێ دەکات و بۆچی و بنەماکانی بەرگریی باش. |
| Risk and the Cost of Attacksمەترسی و تێچووی هێرشەکان | Risk as likelihood times impact, risk responses, and the hidden costs of an attack. وەک لێکدانی ئەگەر و کاریگەری، وەڵامدانەوەی و تێچووە شاراوەکانی . |
| Ethics and Lawئەخلاق و یاسا | Permission is everything: ethical hacking, disclosure, GDPR, HIPAA, crime laws and AI ethics.مۆڵەت هەموو شتێکە: ، ئاشکراکردن، GDPR، HIPAA، یاساکانی تاوان و ئەخلاقی . |
| Malware and Attacksنەرمەواڵەی زیانبەخش و هێرشەکان | Viruses to ransomware, social engineering and injection attacks — and the defence beside each.لە ڤایرۆسەوە تا ، و — لەگەڵ بەرگریی هەریەکەیان. |
| Protecting Accounts and Dataپاراستنی هەژمار و دراوە | Passwords, MFA and passkeys; encryption, hashing and signatures.، MFA و ؛ ، هاش و واژوو. |
| Vulnerabilities and Their Managementخاڵە لاوازەکان و بەڕێوەبردنیان | Where weak points come from, real breaches, the vulnerability lifecycle, scanning and CVSS. لە کوێوە دێن، ڕووداوە ڕاستەقینەکان، ، پشکنین و CVSS. |
| Defending an Organisationبەرگریکردن لە ڕێکخراوێک | Firewalls and segmentation, incident response, security operations and a culture where people report. و ، ، کارەکانی و کولتوورێک کە خەڵک تێیدا ڕاپۆرت دەکەن. |
| Cybersecurity and the Nationئاسایشی سایبەر و ئاسایشی نیشتیمانی | Critical infrastructure, how countries protect themselves (Iraq included) and real incidents.، وڵاتان چۆن خۆیان دەپارێزن (عێراقیش) و ڕووداوە ڕاستەقینەکان. |
The whole course on one pageهەموو کۆرسەکە لە یەک پەڕەدا
Three ideas that run through the courseسێ بیرۆکە کە بە ناو هەموو کۆرسەکەدا تێدەپەڕن
Three ideas run through every chapter. Defence in depth: no single control is enough, so layers catch what one misses. People matter: most attacks involve tricking or tiring a person, and a culture of reporting turns people into defenders. Plan for failure: backups, incident response and resilience decide how badly an attack — or an outage like CrowdStrike — hurts.
سێ بیرۆکە بە ناو هەموو بەشەکاندا تێدەپەڕن. : هیچ کۆنترۆڵێک بە تەنها بەس نییە، بۆیە چینەکان ئەوە دەگرن کە یەکێکیان لەدەستی دەدات. خەڵک گرنگن: زۆربەی هەڵخەڵەتاندن یان ماندووکردنی کەسێکیان تێدایە و کولتووری ڕاپۆرتکردن خەڵک دەکاتە بەرگریکار. پلان بۆ تێکچوون دابنێ: ، و خۆڕاگری بڕیار دەدەن کە — یان وەستانێکی وەک CrowdStrike — چەند زیان دەگەیەنێت.
What to learn nextدواتر چی فێر ببیت
Security sits on top of everything else in IT, so next learn the systems you want to protect:
لەسەر هەموو شتەکانی تری IT بونیاد دەنرێت، بۆیە دواتر ئەو سیستەمانە فێر ببە کە دەتەوێت بیانپارێزیت:
- Information Technology — how computers, operating systems and networks work: What is IT?, Software and operating systems, Types of networks and Network hardware. You cannot secure a network you do not understand.
- Web Programming with PHP and MySQL — build websites and see security from the developer's side: The Internet and the Web, then Securing data in PHP and MySQL (SQL injection, prepared statements, password hashing) and Form security.
- Database Administration — protect the data itself: Database security and Backup and recovery.
- Technical English — the vocabulary of security reports and job adverts: Security and online safety and Jobs and careers in IT.
- Careers — the security jobs and certificates to aim for: IT jobs and the skills they need.
- — ، و چۆن کار دەکەن: IT چییە؟، نەرمەواڵە و سیستەمەکانی وەگەڕخەر، جۆرەکانی ڕایەڵە و ڕەقەواڵەی ڕایەڵە. ناتوانیت بپارێزیت کە تێی ناگەیت.
- وێب بە PHP و MySQL — دروست بکە و لە لای گەشەپێدەرەوە ببینە: ئینتەرنێت و وێب، پاشان پاراستنی دراوە لە PHP و MySQLـدا (، ، ) و ئاسایشی فۆرم.
- بەڕێوەبردنی — خودی بپارێزە: ئاسایشی بنکەدراوە و باکئەپ و گەڕاندنەوە.
- ئینگلیزیی تەکنیکی — وشەکانی ڕاپۆرتەکانی و : ئاسایش و سەلامەتیی ئۆنلاین و کار و پیشە لە ITـدا.
- پیشەکان — کارەکانی و ئەو بڕوانامانەی دەتوانیت ئامانجیان بێت: کارەکانی IT و ئەو لێهاتووییانەی پێویستیانە.
Common mistakesهەڵە باوەکان
- Wrong dates. — MoneyGram was September 2024, not November. Always check a dated source.
- Blaming 'a careless employee'. — Social engineering is designed to fool trained people; fix the process.
- Calling every outage an attack. — CrowdStrike 2024 was a faulty update.
- Treating suspicion as attribution. — Say who officially attributed an attack, when, and with what confidence.
- Repeating leak claims. — A forum post is not a confirmed breach; never download leaked data.
- Mixing up jamming and spoofing. — Jamming hides the position; spoofing fakes it — and the receiver, not the sender, is fooled.
- Thinking 'we would have heard about it'. — Many local incidents are never announced.
- بەرواری هەڵە. — MoneyGram ئەیلوولی 2024 بوو، نەک تشرینی دووەم. هەمیشە سەرچاوەیەکی بەرواردار بپشکنە.
- تاوانبارکردنی «کارمەندێکی بێئاگا». — بۆ هەڵخەڵەتاندنی خەڵکی ڕاهێنراو داڕێژراوە؛ ڕێکارەکە چاک بکە.
- ناونانی هەموو وەستانێک بە . — CrowdStrike 2024 هەڵە بوو.
- دانانی گومان وەک دیاریکردنی بکەر. — بڵێ کێ بە فەرمی دایە پاڵ کێ، کەی و بە چ ئاستێکی دڵنیایی.
- دووبارەکردنەوەی بانگەشەی دزەکردن. — پۆستێکی مەکۆ پشتڕاستکراوە نییە؛ هەرگیز دزەکردوو دامەبەزێنە.
- تێکەڵکردنی و . — شوێنەکە دەشارێتەوە؛ ساختەی دەکات — هەروەها وەرگر هەڵدەخەڵەتێنرێت، نەک نێرەر.
- بیرکردنەوە لەوەی «دەمانبیست ئەگەر ڕووی بدایە». — زۆر ڕووداوی ناوخۆیی هەرگیز ڕاناگەیەنرێن.
Exercisesڕاهێنانەکان
For the MoneyGram incident, answer the five questions from the start of this lesson: when, who was hit, how the attackers got in, what the impact was, and who did it.
بۆ ڕووداوی MoneyGram، وەڵامی پێنج پرسیارەکەی سەرەتای ئەم وانەیە بدەرەوە: کەی، کێ زیانی پێ گەیشت، چۆن چوونە ژوورەوە، کاریگەرییەکە چی بوو و کێ کردی.
Show answerوەڵامەکە پیشان بدە
| Questionپرسیار | Answerوەڵام |
|---|---|
| When?کەی؟ | Problems from 20 September 2024; MoneyGram confirmed a cybersecurity issue on 23 September; transfers back from about 25 September.کێشە لە 20ـی ئەیلوولی 2024ـەوە؛ MoneyGram لە 23ـی ئەیلوول کێشەیەکی پشتڕاست کردەوە؛ ناردنی پارە لە نزیکەی 25ـی ئەیلوولەوە گەڕایەوە. |
| Who was hit?کێ زیانی پێ گەیشت؟ | MoneyGram, and every customer and partner service in about 200 countries, including transfers to and from Iraq.MoneyGram و هەموو کڕیار و خزمەتگوزارییەکی هاوبەش لە نزیکەی 200 وڵاتدا، بە ناردنی پارە بۆ عێراق و لە عێراقیشەوە. |
| How did they get in?چۆن چوونە ژوورەوە؟ | Social engineering of the IT help desk, then an employee's credentials and Active Directory. IT، پاشان کارمەندێک و Active Directory. |
| Impact?کاریگەری؟ | Availability: about five days without transfers worldwide. Confidentiality: customers' personal data was stolen (confirmed in October 2024).: نزیکەی پێنج ڕۆژ بێ ناردنی پارە لە هەموو جیهاندا. : کڕیاران دزرا (لە تشرینی یەکەمی 2024دا پشتڕاست کرایەوە). |
| Who did it?کێ کردی؟ | Not attributed; MoneyGram found no evidence of ransomware.بکەرەکەی دیاری نەکراوە؛ MoneyGram هیچ بەڵگەیەکی نەدۆزییەوە. |
Decide for each event whether it was a cyberattack, and which CIA corner it hurt: (a) CrowdStrike, July 2024; (b) SolarWinds, 2020; (c) Indonesia's data centre, June 2024; (d) the UK payroll system, May 2024.
بۆ هەر ڕووداوێک بڕیار بدە ئایا بوو و زیانی بە کام گۆشەی CIA گەیاند: (أ) CrowdStrike، تەممووزی 2024؛ (ب) SolarWinds، 2020؛ (ج) ناوەندی ئیندۆنیزیا، حوزەیرانی 2024؛ (د) سیستەمی مووچەی بەریتانیا، ئایاری 2024.
Show answerوەڵامەکە پیشان بدە
- (a) Not an attack — a faulty update; availability.
- (b) Attack (supply chain, espionage); confidentiality.
- (c) Attack (ransomware); availability.
- (d) Attack (breach at a contractor); confidentiality.
- (أ) نەبوو — هەڵە؛ .
- (ب) (زنجیرەی دابینکردن، سیخوڕی)؛ .
- (ج) ()؛ .
- (د) (دزەکردن لە لای بەڵێندەرێک)؛ .
In three sentences, explain to a friend who drives a taxi what GPS spoofing is, how it differs from jamming, and what to do if the map suddenly shows a wrong place.
لە سێ ڕستەدا بۆ هاوڕێیەک کە شۆفێری تەکسییە ڕوون بکەرەوە چییە، چ جیاوازییەکی لەگەڵ هەیە و ئەگەر نەخشەکە لەناکاو شوێنێکی هەڵەی پیشان دا چی بکات.
Show answerوەڵامەکە پیشان بدە
A possible answer: 'Spoofing is when a strong fake signal fools your phone's GPS into showing a wrong place, while the map still looks normal. Jamming is different: it just blocks the signal, so the map says there is no GPS. If the map suddenly jumps somewhere impossible, trust the street signs and your own knowledge of the city, not the map, until it settles.'
وەڵامێکی گونجاو: « ئەوەیە کە ساختەی بەهێز GPSـی مۆبایلەکەت هەڵدەخەڵەتێنێت تا شوێنێکی هەڵە پیشان بدات، لە کاتێکدا نەخشەکە هێشتا ئاسایی دەردەکەوێت. جیاوازە: تەنها دەگرێت، بۆیە نەخشەکە دەڵێت GPS نییە. ئەگەر نەخشەکە لەناکاو بازی دا بۆ شوێنێکی مەحاڵ، تا ئاسایی دەبێتەوە متمانە بە تابلۆکانی شەقام و زانیاریی خۆت لەسەر شارەکە بکە، نەک نەخشەکە.»
Summaryپوختە
- Read incident stories with five questions: when, who, how, what impact, who did it — and how sure we are.
- MoneyGram (September 2024): help-desk social engineering, about five days without transfers worldwide, customers' personal data stolen.
- Companies often hide incidents to protect their reputation; breach-notification rules exist because silence harms victims.
- SolarWinds (2020): malicious code in Orion updates; fewer than 18,000 customers installed it; attributed to Russia's SVR in April 2021. Supply chains of software and hardware can be poisoned.
- UK payroll (May 2024): a contractor's system, about 270,000 records, not officially attributed. Indonesia (June 2024): ransomware, 210 institutions, backups now mandatory.
- CrowdStrike (July 2024) was a faulty update, not an attack: availability can be lost without an attacker.
- Unconfirmed leak claims are not incidents: wait for confirmation and never download leaked data.
- GPS jamming hides the position; spoofing fakes it. EASA lists Baghdad among affected regions; cross-checking, smarter receivers, signed signals (Galileo OSNMA) and reporting are the defences.
- چیرۆکی ڕووداوەکان بە پێنج پرسیار بخوێنەرەوە: کەی، کێ، چۆن، چ کاریگەرییەک، کێ کردی — و چەند دڵنیاین.
- MoneyGram (ئەیلوولی 2024): ، نزیکەی پێنج ڕۆژ بێ ناردنی پارە لە هەموو جیهاندا و دزینی کڕیاران.
- کۆمپانیاکان زۆرجار ڕووداوەکان دەشارنەوە بۆ پاراستنی ناوبانگیان؛ یاساکانی هەن چونکە بێدەنگی زیان بە قوربانییەکان دەگەیەنێت.
- SolarWinds (2020): کۆدی زیانبەخش لە Orionـدا؛ کەمتر لە 18,000 کڕیار دایانمەزراند؛ لە نیسانی 2021دا درایە پاڵ SVRـی ڕووسیا. زنجیرەکانی دابینکردنی و دەکرێت ژەهراوی بکرێن.
- مووچەی بەریتانیا (ئایاری 2024): سیستەمی بەڵێندەرێک، نزیکەی 270,000 تۆمار، بکەرەکەی بە فەرمی دیاری نەکراوە. ئیندۆنیزیا (حوزەیرانی 2024): ، 210 دامەزراوە، ئێستا ناچارین.
- CrowdStrike (تەممووزی 2024) هەڵە بوو، نەک : دەکرێت بەبێ لەدەست بچێت.
- بانگەشەی دزەکردنی پشتڕاستنەکراوە ڕووداو نییە: چاوەڕێی پشتڕاستکردنەوە بکە و هەرگیز دزەکردوو دامەبەزێنە.
- شوێنەکە دەشارێتەوە؛ ساختەی دەکات. EASA بەغدا لە نێو ناوچە کاریگەرەکاندا ڕیز دەکات؛ بەراوردکردن، وەرگری زیرەکتر، واژووکراو (OSNMAـی Galileo) و ڕاپۆرتکردن بەرگرییەکانن.
Why is CrowdStrike 2024 in a lesson about incidents if it was not an attack?بۆچی CrowdStrike 2024 لە وانەیەکی ڕووداوەکاندایە ئەگەر هێرش نەبوو؟
Because it shows how much a country depends on a few software products, and that availability can be lost without any attacker.
چونکە پیشان دەدات وڵاتێک چەند پشت بە چەند بەرهەمێکی دەبەستێت و دەکرێت بەبێ هیچ لەدەست بچێت.
What is a supply-chain attack? Give one example from this lesson.هێرشی زنجیرەی دابینکردن چییە؟ نموونەیەک لەم وانەیە بهێنەرەوە.
An attack on a trusted supplier so that the harm reaches its customers — SolarWinds' poisoned Orion updates.
بۆ سەر دابینکەرێکی متمانەپێکراو بۆ ئەوەی زیانەکە بگاتە کڕیارەکانی — Orionـی SolarWinds.
Who is deceived in GPS spoofing?لە هەڵخەڵەتاندنی GPSـدا کێ هەڵدەخەڵەتێنرێت؟
The receiver (the phone, ship or plane), which accepts the stronger fake signal and computes a wrong position.
وەرگرەکە (مۆبایل، کەشتی یان فڕۆکە)، کە ساختە بەهێزترەکە وەردەگرێت و شوێنێکی هەڵە دەژمێرێت.
What should you do with a claimed leak you see online?دەبێت چی بکەیت لەگەڵ بانگەشەیەکی دزەکردن کە لە ئۆنلایندا دەیبینیت؟
Treat it as unconfirmed, do not download or share it, wait for official confirmation and protect your own accounts.
وەک پشتڕاستنەکراوە مامەڵەی لەگەڵ بکە، دای مەبەزێنە و هاوبەشی مەکە، چاوەڕێی پشتڕاستکردنەوەی فەرمی بکە و هەژمارەکانی خۆت بپارێزە.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
Related lecturesوانە پەیوەندیدارەکان
- Social Engineering and Phishingئەندازیاریی کۆمەڵایەتی و فیشینگ
- Malware Today: Infostealers, Banking Trojans, RATs, Cryptojacking and Moreنەرمەواڵەی زیانبەخشی ئەمڕۆ: نەرمەواڵە زانیاریدزەکان، ئەسپەکانی ترۆیای بانکی، RAT، کریپتۆجاکینگ و زیاتر
- Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
- Case Studies: Equifax, Colonial Pipeline and Capital Oneلێکۆڵینەوەی ڕووداو: Equifax، Colonial Pipeline و Capital One
- Confidentiality, Integrity and Availabilityبەنهێنی مانەوە، دروستی و بەردەستبوون
- Europe's GDPR: Rights, Breach Notification and FinesGDPRـی ئەوروپا: ماف، ئاگادارکردنەوەی دزەکردنی دراوە و سزای دارایی
- Encryption, Hashing and Digital Signaturesشفرەکردن، هاشکردن و واژووە دیجیتاڵییەکان
- Computer Communicationsپەیوەندیی کۆمپیوتەر
- What Is Information Technology?تەکنەلۆژیای زانیاری چییە؟
- The Internet and the Webئینتەرنێت و وێب
- Securing Data in PHP and MySQLپاراستنی دراوە لە PHP و MySQL
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- BleepingComputer: MoneyGram — no evidence ransomware is behind recent cyberattack (October 2024)
- SecurityWeek: MoneyGram says personal information stolen in recent cyberattack (8 October 2024)
- PR Newswire: MoneyGram launches money transfer services in Iraq (13 August 2015)
- KrebsOnSecurity: SolarWinds hack could affect 18K customers (15 December 2020)
- CyberScoop: White House formally attributes SolarWinds campaign to Russia's SVR (15 April 2021)
- Al Jazeera: How did Hezbollah get the pagers that exploded in Lebanon? (18 September 2024)
- BleepingComputer: UK confirms Ministry of Defence payroll data exposed in data breach (May 2024)
- Daily Tribune: Cyberattacker hits Indonesia's data center, demands $8M ransom (24 June 2024)
- GovInsider: Hacker group gives decryption key to Indonesian government (July 2024)
- CrowdStrike: Falcon content update for Windows hosts — technical details (19 July 2024)
- Microsoft: Helping our customers through the CrowdStrike outage (20 July 2024)
- EASA: Global Navigation Satellite System outages and alterations (tables of 14 October 2026)
- RNTF: Europe renews its info about GNSS interference — EASA SIB 2022-02R3 (July 2024)
- EUSPA: Galileo Open Service Navigation Message Authentication (OSNMA) — free, helps detect spoofing
- EUSPA: From testing to operations — Galileo OSNMA service now available to users (24 July 2025)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.