Chapterبەش 6 · Lectureوانە 6.2
Case Studies: Equifax, Colonial Pipeline and Capital Oneلێکۆڵینەوەی ڕووداو: Equifax، Colonial Pipeline و Capital One
Three real attacks, told with verified facts: Equifax (2017, an unpatched Apache Struts flaw and 76 days of hidden data theft), Colonial Pipeline (2021, a forgotten VPN account with a stolen password and no MFA, and a ransomware attack that stopped fuel deliveries) and Capital One (2019, a misconfigured firewall in the cloud). For each: cause, impact, how it was found and the lesson — then the lecture's four key takeaways: monitoring, audits, training and network segmentation.
سێ ڕاستەقینە بە زانیاریی پشتڕاستکراوە: Equifax (2017، کێشەیەکی پینەنەکراوی Apache Struts و 76 ڕۆژ دزینی شاراوەی )، Colonial Pipeline (2021، هەژمارێکی لەبیرکراوی بە دزراو و بێ MFA و کە گەیاندنی سووتەمەنیی وەستاند) و Capital One (2019، کە لە هەوردا بە هەڵە ڕێکخرابوو). بۆ هەریەکەیان: هۆکار، کاریگەری، چۆنیەتیی دۆزینەوە و وانە — پاشان چوار وانە سەرەکییەکەی وانەکە: چاودێری، پشکنین، ڕاهێنان و .
What you will learnچی فێر دەبیت
- Describe the cause, impact and lesson of the Equifax, Colonial Pipeline and Capital One breaches with correct facts.
- Link each case to the door it used: outdated software, weak authentication or misconfiguration.
- Explain the four key takeaways — monitoring, audits, training, segmentation — and where each would have helped.
- Spot inaccurate claims about breaches and correct them from reliable reports.
- هۆکار، کاریگەری و وانەی Equifax، Colonial Pipeline و Capital One بە زانیاریی دروست وەسف بکەیت.
- هەر ڕووداوێک بەو دەرگایەوە ببەستیتەوە کە بەکاری هێنا: کۆن، لاواز یان .
- چوار وانە سەرەکییەکە ڕوون بکەیتەوە — چاودێری، پشکنین، ڕاهێنان، — و بڵێیت هەریەکەیان لە کوێ یارمەتیی دەدا.
- قسەی نادروست دەربارەی بناسیتەوە و لە ڕاپۆرتە باوەڕپێکراوەکانەوە ڕاستیان بکەیتەوە.
Three real breaches, one patternسێ دزەکردنی دراوەی ڕاستەقینە، یەک شێوە
In Where vulnerabilities come from you met three doors into a system: bad code, old software and wrong settings. Lecture 4 now shows what happens when real attackers walk through such doors. It names three famous cases:
لە خاڵە لاوازەکان لە کوێوە دێن سێ دەرگات ناسی بۆ ناو سیستەمێک: کۆدی خراپ، کۆن و . ئێستا وانەی چوارەم نیشان دەدات کاتێک بەو دەرگایانەدا دێنە ژوورەوە چی ڕوو دەدات. سێ ڕووداوی بەناوبانگ ناو دەبات:
| Caseڕووداو | Yearساڵ | What happenedچی ڕوویدا |
|---|---|---|
| Equifax | 2017 | A data breach that exposed the personal data of about 147 million people. کە نزیکەی 147 ملیۆن کەسی ئاشکرا کرد. |
| Colonial Pipeline | 2021 | A ransomware attack that disrupted the fuel supply of the US East Coast. کە دابینکردنی سووتەمەنیی کەناری ڕۆژهەڵاتی ئەمریکای تێک دا. |
| Capital One | 2019 | A data breach that exposed the personal data of about 100 million people in the US (and 6 million in Canada). کە نزیکەی 100 ملیۆن کەسی لە ئەمریکا (و 6 ملیۆن لە کەنەدا) ئاشکرا کرد. |
Three real breaches, one patternسێ دزەکردنی دراوەی ڕاستەقینە، یەک شێوە
Cause, impact, lessonهۆکار، کاریگەری، وانە
For each case we ask the same three questions: Cause — which door did the attacker use? Impact — what was lost, and who was hurt? Lesson — what would have stopped it? Investigators, courts and government reports have checked these cases closely, so we can use real, verified facts.
بۆ هەر ڕووداوێک هەمان سێ پرسیار دەکەین: هۆکار — بە کام دەرگادا هات؟ کاریگەری — چی لەدەست چوو و کێ زیانی پێگەیشت؟ وانە — چی دەیتوانی ڕێگەی لێ بگرێت؟ لێکۆڵەران، دادگاکان و ڕاپۆرتە حکومییەکان بە وردی ئەم ڕووداوانەیان پشکنیوە، بۆیە دەتوانین زانیاریی ڕاستەقینە و پشتڕاستکراوە بەکار بهێنین.
After a match, a good football coach replays every goal his team let in. He does not ask 'who is to blame?' but 'where was the gap, and how do we close it next time?'. A case study is that replay for security teams.
دوای یارییەک، ڕاهێنەرێکی باشی تۆپی پێ هەموو ئەو گۆڵانە دووبارە سەیر دەکاتەوە کە تیپەکەی لێی کراوە. ناپرسێت «تاوانی کێیە؟» بەڵکو دەپرسێت «بۆشاییەکە لە کوێ بوو و جاری داهاتوو چۆن دایدەخەین؟». لێکۆڵینەوەی ڕووداو هەمان دووبارە سەیرکردنە بۆ تیمەکانی .
Where the analogy stops workingسنووری ئەم نموونەیە
A football replay shows everything on camera. Real investigations often stay partly secret, and companies may dispute some details, so we use only facts that official reports confirm.
دووبارە سەیرکردنی یارییەک هەموو شتێک لەسەر کامێرا نیشان دەدات. لێکۆڵینەوە ڕاستەقینەکان زۆرجار بەشێکیان نهێنی دەمێننەوە و لەوانەیە کۆمپانیاکان ناکۆک بن لەسەر هەندێک وردەکاری، بۆیە تەنها ئەو زانیاریانە بەکار دەهێنین کە ڕاپۆرتە فەرمییەکان پشتڕاستیان دەکەنەوە.
Equifax (2017): the patch that was never installedEquifax (2017): پینەیەک کە هەرگیز دانەمەزرا
Equifax is one of the three big US credit-reporting companies: it collects data about how people borrow and pay, so that banks can decide whether to give them a loan. Its website had an online dispute portal, where people could upload documents to correct mistakes in their credit report.
Equifax یەکێکە لە سێ کۆمپانیا گەورەکەی ئەمریکا کە ڕاپۆرتی قەرز ئامادە دەکەن: کۆ دەکاتەوە دەربارەی ئەوەی خەڵک چۆن قەرز وەردەگرن و دەیدەنەوە، بۆ ئەوەی بانکەکان بڕیار بدەن قەرزیان بدەنێ یان نا. پۆرتاڵێکی سکاڵای ئۆنلاینی هەبوو کە خەڵک دەیانتوانی بەڵگەنامەی تێدا بار بکەن بۆ ڕاستکردنەوەی هەڵەکانی ڕاپۆرتی قەرزەکەیان.
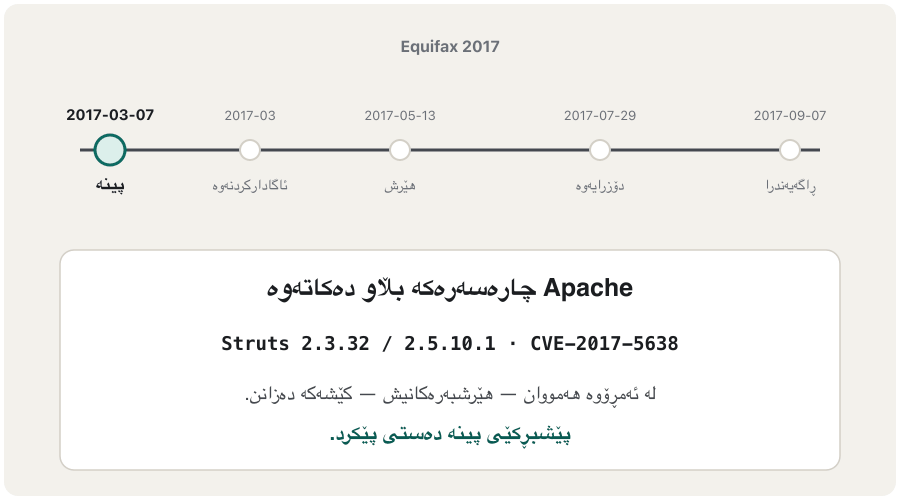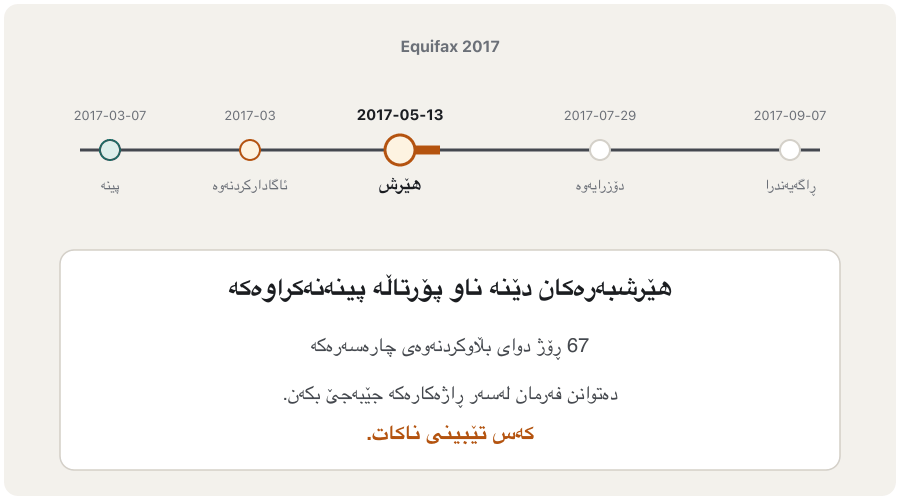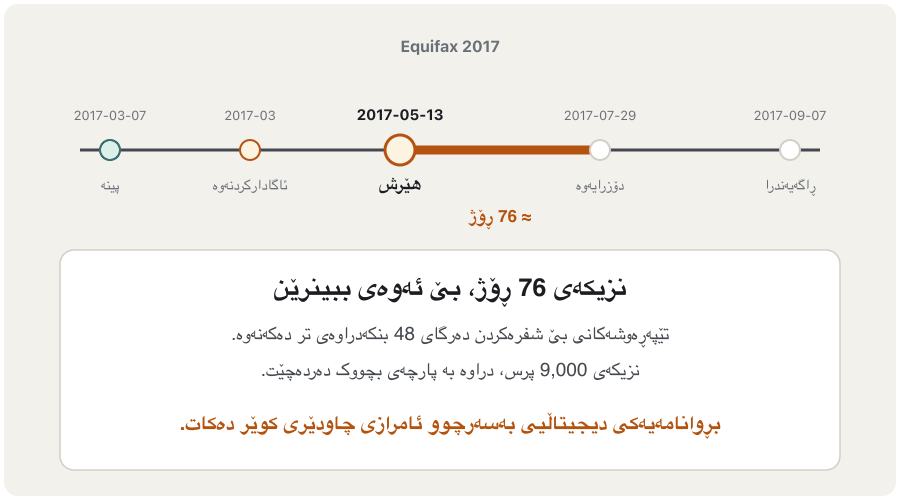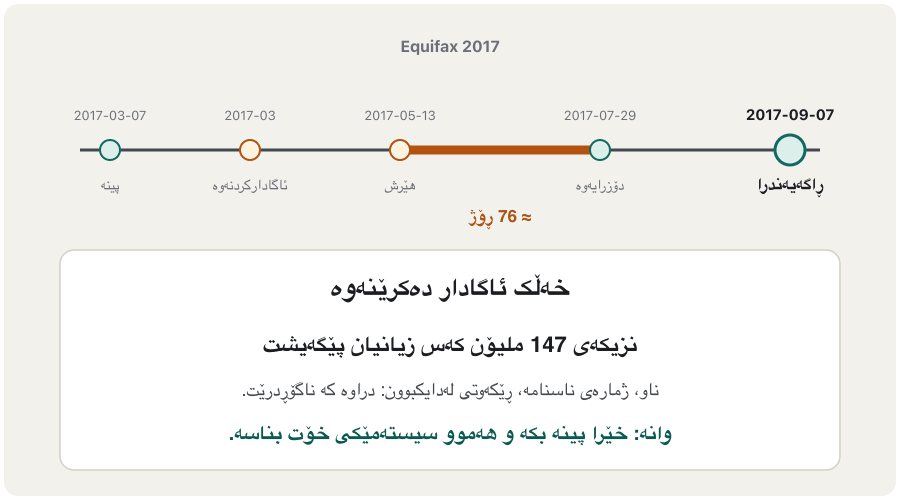
Cause. The lecture says the breach was caused by an unpatched Apache Struts vulnerability that let the attackers into the company's systems. Apache Struts is free software for building web applications, and the dispute portal was built with it. The flaw, CVE-2017-5638, let anyone on the internet run commands on the server by sending one specially shaped upload request. Apache published fixed versions on 7 March 2017. Equifax's portal was still not patched two months later.
هۆکار. وانەکە دەڵێت لە ئەنجامی پینەنەکراوی Apache Struts بوو کە ڕێگەی بە دا بچنە ناو سیستەمەکانی کۆمپانیاکە. Apache Struts بێبەرانبەرە بۆ دروستکردنی و پۆرتاڵی سکاڵاکە بەوە دروست کرابوو. کێشەکە، CVE-2017-5638، ڕێگەی دەدا بە هەر کەسێک لەسەر فەرمان لەسەر جێبەجێ بکات، تەنها بە ناردنی داواکارییەکی بارکردنی تایبەت. Apache لە 7ـی ئاداری 2017دا وەشانی چاککراوی بڵاو کردەوە. دوو مانگ دواتر هێشتا پۆرتاڵەکەی Equifax نەکرابوو.
Why was it missed? According to the US Government Accountability Office (GAO), Equifax did receive the US government's warning about the flaw in March 2017 and forwarded it to its system administrators — but the mailing list was out of date, so the people responsible for the portal never got it. A network scan a week later did not find the vulnerable portal either.
بۆچی لەبیر کرا؟ بەپێی نووسینگەی لێپرسینەوەی حکومەتی ئەمریکا (GAO)، Equifax لە ئاداری 2017دا ئاگادارکردنەوەی حکومەتی ئەمریکای دەربارەی کێشەکە وەرگرت و ناردی بۆ بەڕێوەبەرانی سیستەمەکانی — بەڵام لیستی ناردنەکە کۆن بوو، بۆیە ئەو کەسانەی بەرپرسی پۆرتاڵەکە بوون هەرگیز پێیان نەگەیشت. پشکنینێکی یەک هەفتە دواتریش پۆرتاڵە لاوازەکەی نەدۆزییەوە.
How the 2017 Equifax breach happened: an Apache Struts flaw announced in March was still unpatched when attackers got in from mid-May.
Equifax لە 2017 چۆن ڕوویدا: Apache Struts کە لە ئازاردا ڕاگەیەنرابوو، هێشتا نەکرابوو کاتێک لە ناوەڕاستی ئایارەوە چوونە ژوورەوە.
Plays 0:11-2:54: Equifax only; skips the sponsor and the fossil news. Made in September 2017, it gives the first count (143 million); the final count is about 147 million.
لە 0:11 تا 2:54 پەخش دەبێت: تەنها Equifax؛ ڕیکلامی سپۆنسەرەکە و هەواڵی بەردبووەکان تێدەپەڕێنێت. لە ئەیلوولی 2017 دروستکراوە، بۆیە یەکەم ژمارە دەڵێت (143 ملیۆن)؛ ژمارەی کۆتایی نزیکەی 147 ملیۆنە.
Equifax (2017): the patch that was never installedEquifax (2017): پینەیەک کە هەرگیز دانەمەزرا
The 76 days, step by step76 ڕۆژەکە، هەنگاو بە هەنگاو
The animation follows the GAO's account of what happened, from the day the patch appeared to the day the public was told.
ئەنیمەیشنەکە بەدوای گێڕانەوەی GAOـدا دەڕوات بۆ ئەوەی ڕوویدا، لەو ڕۆژەوەی دەرچوو تا ئەو ڕۆژەی خەڵک ئاگادار کرایەوە.
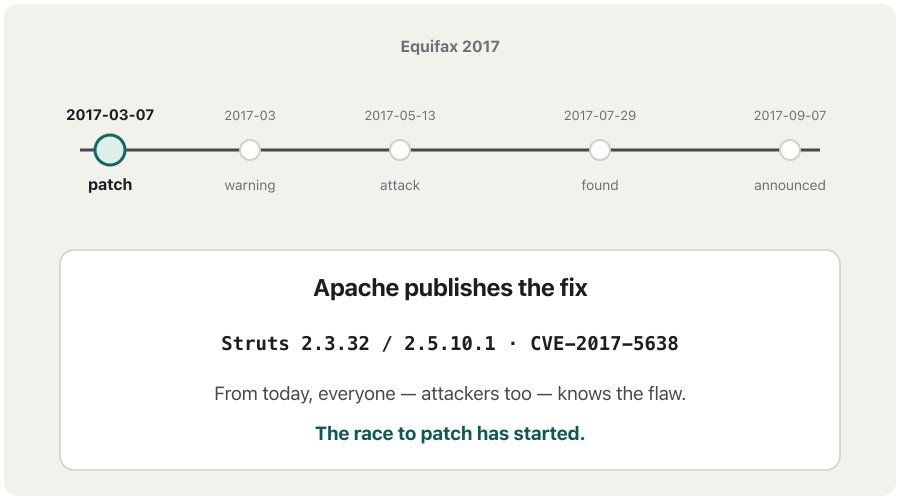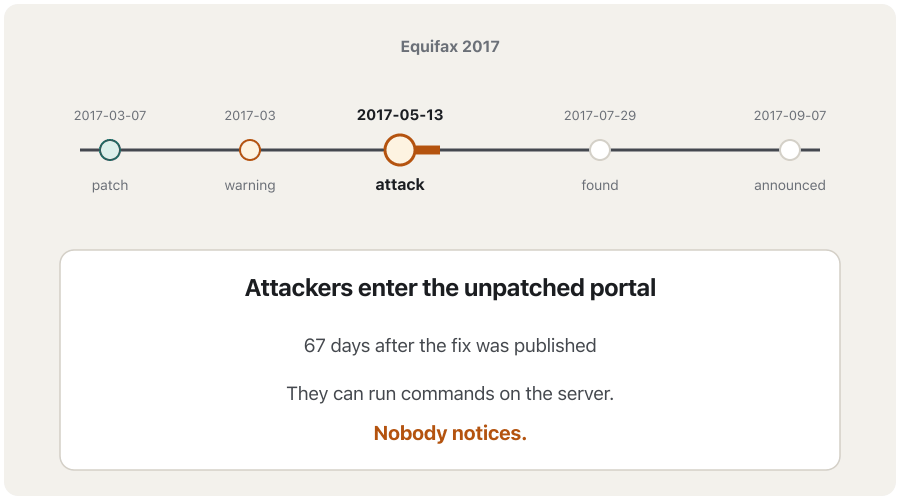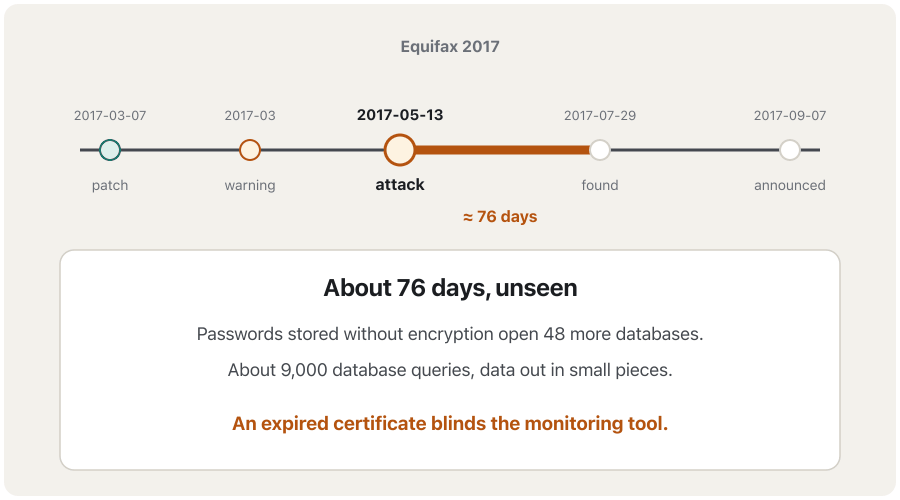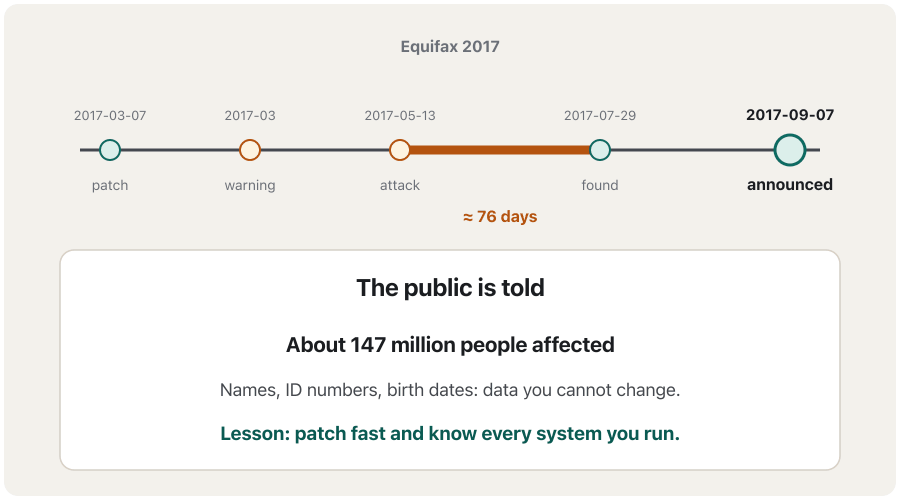
Two details show that one mistake is rarely enough on its own. First, the attackers found a store of usernames and passwords kept without encryption, which let them jump from the portal's 3 databases to 48 unrelated databases. Second, Equifax had a device that inspected network traffic for signs of attack, but its digital certificate had expired about 10 months earlier, so it could not look inside the encrypted traffic. The data left in small pieces over normal-looking encrypted connections.
دوو وردەکاری نیشان دەدەن کە یەک هەڵە بە تەنها بەس نییە. یەکەم، کۆگایەکی ناوی و بێ یان دۆزییەوە، کە ڕێگەی پێدان لە 3 پۆرتاڵەکەوە باز بدەن بۆ 48 تری پەیوەندینەدار. دووەم، Equifax ئامێرێکی هەبوو کە هاتوچۆی دەپشکنی بۆ نیشانەکانی ، بەڵام نزیکەی 10 مانگ پێشتر بەسەرچووبوو، بۆیە نەیدەتوانی ناو هاتوچۆ شفرەکراوەکە ببینێت. بە پارچەی بچووک دەرچوو، لە ڕێگەی پەیوەندیی شفرەکراوەوە کە ئاسایی دەردەکەوتن.
Equifax (2017): the patch that was never installedEquifax (2017): پینەیەک کە هەرگیز دانەمەزرا
Equifax: what was lostEquifax: چی لەدەست چوو
Impact. The lecture says the breach exposed the personal data of 147 million people, including Social Security numbers (the US national ID number), credit card information and other sensitive data. The official figures: the names, Social Security numbers and birth dates of about 147 million people, many addresses and some driver's licence numbers; card numbers of about 209,000 people; and dispute documents with personal data of about 182,000 people.
کاریگەری. وانەکە دەڵێت 147 ملیۆن کەسـی ئاشکرا کرد، لەوانە ژمارەی ئاسایشی کۆمەڵایەتی (ژمارەی ناسنامەی نیشتیمانیی ئەمریکا)، زانیاریی کارتی قەرز و هەستیاری تر. ژمارە فەرمییەکان: ناو، ژمارەی ئاسایشی کۆمەڵایەتی و ڕێکەوتی لەدایکبوونی نزیکەی 147 ملیۆن کەس، زۆر ناونیشان و هەندێک ژمارەی مۆڵەتی شۆفێری؛ ژمارەی کارتی نزیکەی 209,000 کەس؛ هەروەها بەڵگەنامەکانی سکاڵا کە نزیکەی 182,000 کەسیان تێدا بوو.
Equifax (2017): the patch that was never installedEquifax (2017): پینەیەک کە هەرگیز دانەمەزرا
Equifax: the bill and the root causesEquifax: تێچووەکە و هۆکارە بنەڕەتییەکان
The cost for Equifax was huge. In July 2019 it agreed a settlement with the US Federal Trade Commission (FTC) and other authorities that includes up to 425 million dollars to help the people affected, free identity-restoration help and extra free credit reports. Equifax's own investigation, quoted by the GAO, named four weaknesses: identification (the flaw was not found on the portal), detection (the expired certificate), segmentation (the databases were not separated from each other) and data governance (passwords kept unencrypted). It added a fifth: nothing limited how many database queries could be run.
تێچووی Equifax زۆر گەورە بوو. لە تەممووزی 2019دا لەگەڵ کۆمیسیۆنی بازرگانیی فیدراڵیی ئەمریکا (FTC) و دەسەڵاتەکانی تر ڕێککەوت کە تا 425 ملیۆن دۆلار بۆ یارمەتیی زیانلێکەوتووان، یارمەتیی بێبەرانبەری گەڕاندنەوەی ناسنامە و ڕاپۆرتی قەرزی بێبەرانبەری زیادە لەخۆ دەگرێت. لێکۆڵینەوەی خودی Equifax، کە GAO باسی دەکات، چوار لاوازی ناو برد: ناسینەوە (کێشەکە لەسەر پۆرتاڵەکە نەدۆزرایەوە)، دۆزینەوەی ( بەسەرچوو)، ( لە یەکتر جیا نەکرابوونەوە) و بەڕێوەبردنی ( بێ هەڵگیرابوون). پێنجەمیشی زیاد کرد: هیچ شتێک سنووری بۆ ژمارەی دانەنابوو.
Colonial Pipeline (2021): one password, no second factorColonial Pipeline (2021): یەک تێپەڕەوشە، بێ هۆکاری دووەم
Colonial Pipeline runs a very large fuel pipeline in the United States, from the Gulf Coast to the New York area. It carries petrol, diesel and jet fuel to the East Coast — about 45% of the petrol used there. A fuel pipeline is critical infrastructure: everyday life stops without it.
Colonial Pipeline هێڵێکی بۆریی زۆر گەورەی سووتەمەنی لە ئەمریکا بەڕێوە دەبات، لە کەناری کەنداوەوە تا ناوچەی نیویۆرک. بەنزین، دیزڵ و سووتەمەنیی فڕۆکە دەگەیەنێتە کەناری ڕۆژهەڵات — نزیکەی 45%ـی ئەو بەنزینەی لەوێ بەکار دێت. هێڵی بۆریی سووتەمەنی ـە: ژیانی ڕۆژانە بەبێ ئەو دەوەستێت.
Cause. The lecture says the attack used a compromised password and the lack of multi-factor authentication (MFA). Colonial's chief executive told the US Senate in June 2021 how it happened: the attackers logged in through an old ('legacy') VPN account that the IT team did not know was still active. The account was protected by a password only — a complicated one, but it had been stolen — and it did not ask for a second factor. Once inside, the criminal group DarkSide ran its ransomware on the company's business network on 7 May 2021.
هۆکار. وانەکە دەڵێت ئاشکرابوو و نەبوونی (MFA)ـی بەکار هێنا. بەڕێوەبەری باڵای Colonial لە حوزەیرانی 2021دا بە ئەنجومەنی پیرانی ئەمریکای گوت چۆن ڕوویدا: لە ڕێگەی هەژمارێکی کۆنی ـەوە چوونە ژوورەوە کە تیمی IT نەیدەزانی هێشتا کارایە. هەژمارەکە تەنها بە پارێزرابوو — ئاڵۆز، بەڵام دزرابوو — و داوای هۆکاری دووەمی نەدەکرد. کاتێک چوونە ناوەوە، گرووپە تاوانکارەکەی DarkSide لە 7ـی ئایاری 2021دا لەسەر بازرگانیی کۆمپانیاکە جێبەجێ کرد.
Colonial Pipeline (2021): one password, no second factorColonial Pipeline (2021): یەک تێپەڕەوشە، بێ هۆکاری دووەم
Colonial: when the fuel stoppedColonial: کاتێک سووتەمەنی وەستا
Impact. The lecture says the attack disrupted the fuel supply across the US East Coast and showed how vulnerable critical infrastructure is. The ransomware locked the company's business (IT) computers, not the pipeline's control system. To contain the attack, Colonial took its systems offline on 7 May, and that stopped the whole pipeline. It restarted on 12 May and announced normal operations on 15 May. In those days, long queues formed at petrol stations and some stations ran dry, partly because worried drivers bought extra fuel.
کاریگەری. وانەکە دەڵێت دابینکردنی سووتەمەنیی لە سەرانسەری کەناری ڕۆژهەڵاتی ئەمریکادا تێک دا و نیشانی دا چەند لاوازە. بازرگانی (IT)ـی کۆمپانیاکەی قفڵ کرد، نەک سیستەمی کۆنترۆڵی هێڵە بۆرییەکە. بۆ سنووردارکردنی ، Colonial لە 7ـی ئایاردا سیستەمەکانی کوژاندەوە و ئەمە هەموو هێڵە بۆرییەکەی وەستاند. لە 12ـی ئایاردا دەستی پێکردەوە و لە 15ـی ئایاردا ڕایگەیاند کارەکان گەڕاونەتەوە بۆ دۆخی ئاسایی. لەو ڕۆژانەدا ڕیزی درێژ لە بەردەم بەنزینخانەکان دروست بوو و هەندێک بەنزینخانە سووتەمەنییان نەما، بەشێکی لەبەر ئەوە بوو کە شۆفێرە نیگەرانەکان سووتەمەنیی زیادەیان دەکڕی.
Colonial paid the criminals a ransom of about 75 bitcoins, worth more than 4 million dollars at the time, the day after the attack. On 7 June 2021 the US Department of Justice announced that it had traced and seized 63.7 of those bitcoins (then about 2.3 million dollars). After the attack the US government created new rules and services: pipeline security directives from the Transportation Security Administration (TSA), the website StopRansomware.gov and closer cooperation between companies and CISA.
Colonial ڕۆژی دوای بارمتەیەکی نزیکەی 75 بیتکۆینـی دا بە تاوانکاران کە ئەو کاتە زیاتر لە 4 ملیۆن دۆلار بوو. لە 7ـی حوزەیرانی 2021دا وەزارەتی دادی ئەمریکا ڕایگەیاند کە 63.7 بیتکۆین لەو پارەیەی بەدواداچوون بۆ کردووە و دەستی بەسەردا گرتووە (ئەو کاتە نزیکەی 2.3 ملیۆن دۆلار). دوای حکومەتی ئەمریکا یاسا و خزمەتگوزاریی نوێی دروست کرد: ڕێنماییەکانی هێڵە بۆرییەکان لەلایەن دەزگای گواستنەوە (TSA)، StopRansomware.gov و هاوکاریی نزیکتری نێوان کۆمپانیاکان و CISA.
Capital One (2019): a wrong setting in the cloudCapital One (2019): ڕێکخستنێکی هەڵە لە هەوردا
Capital One is a large US bank, famous for credit cards. It was one of the first big banks to move much of its IT into the public cloud, renting servers and storage from a cloud provider instead of running its own data centres.
Capital One بانکێکی گەورەی ئەمریکایە و بە کارتی قەرز ناسراوە. یەکێک بوو لە یەکەم بانکە گەورەکان کە بەشێکی زۆری ITـەکەی گواستەوە بۆ : و شوێنی هەڵگرتنی لە بەکرێ دەگرت لە جیاتی ئەوەی سەنتەری خۆی بەڕێوە ببات.
Cause. The lecture says the breach was caused by a misconfigured web application firewall (WAF). The WAF stood in front of Capital One's web applications in the cloud. Because it was set up wrongly, an attacker could use it to obtain access to the bank's cloud storage and copy files on 22 and 23 March 2019. Capital One itself called it a 'configuration vulnerability'. The attacker was a former employee of the cloud provider; in June 2022 a US jury convicted her of wire fraud and of illegally accessing protected computers.
هۆکار. وانەکە دەڵێت لە ئەنجامی (WAF) بوو کە بە هەڵە ڕێکخرابوو. WAFـەکە لە بەردەم Capital One لە هەوردا بوو. لەبەر ئەوەی بە هەڵە ڕێکخرابوو، توانی لە ڕێگەیەوە دەستی بگات بە شوێنی هەڵگرتنی هەوریی بانکەکە و لە 22 و 23ـی ئاداری 2019دا فایلەکان کۆپی بکات. خودی Capital One ناوی نا « ڕێکخستن». کارمەندێکی پێشووی بوو؛ لە حوزەیرانی 2022دا دادگایەکی ئەمریکی بە تاوانی فێڵ و دەستڕاگەیشتنی نایاسایی بە پارێزراو تاوانباری کرد.
Who is responsible for such a setting? In the cloud, the provider protects the buildings, hardware and its own software, but the customer is responsible for how it configures its servers, firewalls and access rights. This split is the shared responsibility model. Capital One's mistake was on the customer's side.
کێ بەرپرسیارە لە ڕێکخستنێکی وا؟ لە هەوردا، دابینکەرەکە بیناکان، و خۆی دەپارێزێت، بەڵام کڕیار بەرپرسیارە لەوەی چۆن ، و مافەکانی دەستڕاگەیشتنی ڕێک دەخات. ئەم دابەشکردنە مۆدێلی بەرپرسیارێتیی هاوبەشـە. هەڵەکەی Capital One لە لای کڕیار بوو.
The 2019 Capital One breach: a misconfigured web application firewall in AWS let an outsider read cloud storage, who was at fault, and the lessons.
Capital One لە 2019: کە بە هەڵە ڕێکخرابوو لە AWSـدا ڕێگەی دا کەسێکی دەرەکی ناوەڕۆکی بخوێنێتەوە؛ هەروەها هەڵەی کێ بوو و .
Plays 0:00-11:07: how the leak was found, the SSRF request through the badly configured firewall, the over-permissive cloud role, who was at fault, and the lessons (IMDSv2, least privilege).
لە 0:00 تا 11:07 پەخش دەبێت: دزەکردنەکە چۆن دۆزرایەوە، SSRF بە ناو ، ڕۆڵی هەور بە زیاد لە پێویستەوە، هەڵەی کێ بوو و (IMDSv2 و ).
Capital One (2019): a wrong setting in the cloudCapital One (2019): ڕێکخستنێکی هەڵە لە هەوردا
Capital One: what was lost, and how it was foundCapital One: چی لەدەست چوو و چۆن دۆزرایەوە
Impact. The lecture says the breach exposed the data of 100 million customers, including names, addresses, Social Security numbers and credit card information. Capital One's own figures: about 100 million people in the US and 6 million in Canada — customers and also people who had only applied for a card. Most of the data came from credit-card applications from 2005 to early 2019: names, addresses, phone numbers, e-mail addresses, birth dates and incomes. Also taken: about 140,000 US Social Security numbers, about 80,000 linked bank account numbers and about 1 million Canadian Social Insurance Numbers.
کاریگەری. وانەکە دەڵێت 100 ملیۆن کڕیاری ئاشکرا کرد، لەوانە ناو، ناونیشان، ژمارەی ئاسایشی کۆمەڵایەتی و زانیاریی کارتی قەرز. ژمارەکانی خودی Capital One: نزیکەی 100 ملیۆن کەس لە ئەمریکا و 6 ملیۆن لە کەنەدا — کڕیاران و هەروەها ئەو کەسانەی تەنها داوای کارتیان کردبوو. زۆربەی لە فۆرمی داواکاریی کارتی قەرزەوە بوو لە 2005ـەوە تا سەرەتای 2019: ناو، ناونیشان، ژمارەی تەلەفۆن، ، ڕێکەوتی لەدایکبوون و داهات. هەروەها ئەمانەش بران: نزیکەی 140,000 ژمارەی ئاسایشی کۆمەڵایەتیی ئەمریکی، نزیکەی 80,000 ژمارەی هەژماری بانکیی پەیوەندیدار و نزیکەی 1 ملیۆن ژمارەی بیمەی کۆمەڵایەتیی کەنەدی.
Capital One (2019): a wrong setting in the cloudCapital One (2019): ڕێکخستنێکی هەڵە لە هەوردا
Capital One: how it was found, and the fineCapital One: چۆن دۆزرایەوە و سزاکە
How it was found. Not by Capital One's own monitoring. On 17 July 2019 an outside person sent a tip through the bank's Responsible Disclosure Program — the official channel for reporting security problems — saying that some of its data was visible online. The bank confirmed the breach two days later, almost four months after the data had been copied. In August 2020 the US banking regulator (the OCC) fined Capital One 80 million dollars, because it had moved important IT operations to the cloud without first setting up an effective way to assess the risks.
چۆن دۆزرایەوە. نەک بە چاودێریی خودی Capital One. لە 17ـی تەممووزی 2019دا کەسێکی دەرەکی لە ڕێگەی بەرنامەی ـی بانکەکەوە — کەناڵە فەرمییەکەی ڕاپۆرتکردنی کێشەکانی — ئاگاداری کردەوە کە هەندێک لە لەسەر دەبینرێت. بانکەکە دوو ڕۆژ دواتر پشتڕاست کردەوە، نزیکەی چوار مانگ دوای کۆپیکردنی . لە ئابی 2020دا دەزگای چاودێریی بانکەکانی ئەمریکا (OCC) Capital Oneـی 80 ملیۆن دۆلار سزا دا، چونکە پێش ئەوەی ڕێگەیەکی کاریگەری هەڵسەنگاندنی دابنێت، کارە گرنگەکانی ITـی گواستبووەوە بۆ هەور.
The three cases side by sideسێ ڕووداوەکە لە تەنیشت یەکتر
| Questionپرسیار | Equifax (2017) | Colonial Pipeline (2021) | Capital One (2019) |
|---|---|---|---|
| Doorدەرگا | Outdated software (unpatched Apache Struts) کۆن (Apache Strutsـی پینەنەکراو) | Weak login: stolen password, no MFA, forgotten VPN accountچوونەژوورەوەی لاواز: دزراو، بێ MFA، هەژمارێکی لەبیرکراوی | Misconfiguration (wrongly set firewall in the cloud) ( کە لە هەوردا بە هەڵە ڕێکخرابوو) |
| What made it worseچی خراپتری کرد | Unencrypted passwords, no segmentation, blind monitoring بێ ، بێ ، چاودێریی کوێر | Nobody knew the old account existed, so nobody watched itکەس نەیدەزانی هەژمارە کۆنەکە هەیە، بۆیە کەس چاودێریی نەدەکرد | Too much access to cloud storage; slow detectionدەستڕاگەیشتنی زۆر بە شوێنی هەڵگرتنی هەوری؛ دۆزینەوەی خاو |
| Found byدۆزرایەوە لەلایەن | Staff, during routine checks, after 76 daysکارمەندان، لە پشکنینی ئاسایی ڕۆژانەدا، دوای 76 ڕۆژ | The ransom note, the same dayنامەی بارمتەکە، هەمان ڕۆژ | An outside tip, almost 4 months laterئاگادارکردنەوەیەکی دەرەکی، نزیکەی 4 مانگ دواتر |
| Impactکاریگەری | ~147 million people; settlement up to $425 millionنزیکەی 147 ملیۆن کەس؛ ڕێککەوتن تا 425 ملیۆن دۆلار | Fuel stopped for 5 days; ransom paid; panic buyingسووتەمەنی 5 ڕۆژ وەستا؛ بارمتە درا؛ کڕینی بە پەشۆکاوی | ~106 million people; $80 million fineنزیکەی 106 ملیۆن کەس؛ 80 ملیۆن دۆلار سزا |
Look at the pattern. Each attack started at one door, but the damage grew because there was no second line of defence: nothing stopped the attackers from moving further, and nobody noticed them quickly. This is why security relies on defence in depth: many layers, so one mistake does not become a disaster.
سەیری ئەو شێوەیە بکە کە دووبارە دەبێتەوە. هەر لە یەک دەرگاوە دەستی پێکرد، بەڵام زیانەکە گەورە بوو چونکە هێڵی دووەمی بەرگری نەبوو: هیچ شتێک لە چوونە پێشەوە ڕانەگرت و کەس بە خێرایی تێبینیی نەکردن. هەر بۆیە پشت بە بەرگریی چەندچین دەبەستێت: چەندین چین، بۆ ئەوەی یەک هەڵە نەبێتە کارەسات.
Four key takeawaysچوار وانەی سەرەکی
The lecture ends the case studies with four key takeaways for reducing vulnerabilities. Each one would have helped in at least one of the three cases:
وانەکە لێکۆڵینەوەی ڕووداوەکان بە چوار وانەی سەرەکی بۆ کەمکردنەوەی کۆتایی پێ دەهێنێت. هەریەکەیان لانیکەم لە یەکێک لە سێ ڕووداوەکەدا یارمەتیی دەدا:
| Takeawayوانە | What it meansواتای چییە | Where it would have helpedلە کوێ یارمەتیی دەدا |
|---|---|---|
| 1. Proactive monitoring1. چاودێریی پێشوەختە | Use an intrusion detection system (IDS) and SIEM tools to spot suspicious activity in real time.سیستەمێکی دۆزینەوەی دزەکردن (IDS) و ئامرازەکانی SIEM بەکار بهێنە بۆ بینینی ڕاستەوخۆی چالاکیی گوماناوی. | Equifax (76 days unseen), Capital One (found by an outsider)Equifax (76 ڕۆژ نەبینرا)، Capital One (کەسێکی دەرەکی دۆزییەوە) |
| 2. Regular audits2. پشکنینی بەردەوام | Run periodic vulnerability assessments and penetration tests to find weak points before attackers do.بە شێوەی خولی هەڵسەنگاندنی و ئەنجام بدە بۆ دۆزینەوەی پێش . | Equifax (the unpatched portal), Capital One (the firewall setting), Colonial (the forgotten VPN account)Equifax (پۆرتاڵە پینەنەکراوەکە)، Capital One (ڕێکخستنی )، Colonial (هەژمارە لەبیرکراوەکەی ) |
| 3. Training and awareness3. ڕاهێنان و | Teach employees about phishing and social engineering, so attacks that rely on human error fail.کارمەندان فێری و بکە، بۆ ئەوەی ئەو پشت بە هەڵەی مرۆیی دەبەستن شکست بهێنن. | Colonial (a password leaked somehow); every companyColonial ( بە شێوەیەک دزەی کرد)؛ هەموو کۆمپانیایەک |
| 4. | Separate sensitive data and systems from less secure parts of the network, to limit the damage of a breach (how segmentation works). و سیستەمە هەستیارەکان لە بەشە کەمتر پارێزراوەکانی جیا بکەرەوە، بۆ سنووردارکردنی زیانی دزەکردن (بەشبەشکردنی ڕایەڵە چۆن کار دەکات). | Equifax (3 databases became 51); Colonial (keep business IT apart from pipeline control)Equifax (3 بوو بە 51)؛ Colonial (ITـی بازرگانی لە کۆنترۆڵی هێڵە بۆرییەکە جیا بکەرەوە) |
Four key takeawaysچوار وانەی سەرەکی
Two more lessons, and where to learn moreدوو وانەی تر و لە کوێ زیاتر فێر ببیت
Where to learn more: firewalls, IDS, SIEM and segmentation are taught in Network defences, in the chapter Defending an Organisation; penetration testing and its rules are in Ethics and ethical hacking; scanning is in Finding and rating vulnerabilities; phishing is in Social engineering and phishing.
بۆ فێربوونی زیاتر: ، IDS، و لە وانەی بەرگرییەکانی ڕایەڵە لە بەشی بەرگریکردن لە ڕێکخراوێکدا فێر دەکرێن؛ و یاساکانی لە ئەخلاق و هاککردنی ئەخلاقیدان؛ پشکنین لە دۆزینەوە و هەڵسەنگاندنی خاڵە لاوازەکاندایە؛ لە ئەندازیاریی کۆمەڵایەتی و فیشینگدایە.
Common mistakesهەڵە باوەکان
| Mistakeهەڵە | Why it is wrongبۆچی هەڵەیە | Betterباشتر |
|---|---|---|
| "Big companies get hacked by geniuses with secret tools."«کۆمپانیا گەورەکان لەلایەن بلیمەتانەوە بە ئامرازی نهێنی هاک دەکرێن.» | All three cases used known, avoidable weaknesses: a missed patch, a password without MFA, a wrong setting.هەر سێ ڕووداوەکە لاوازیی ناسراو و ڕێگەلێگیراویان بەکار هێنا: کە لەبیر کرا، بێ MFA، . | Do the basics well: patch, MFA, configuration reviews.بنەماکان باش جێبەجێ بکە: ، MFA، پێداچوونەوەی ڕێکخستنەکان. |
| "A complicated password is enough."« ئاڵۆز بەسە.» | Colonial's password was complicated, and it was stolen anyway. Colonial ئاڵۆز بوو، بەڵام هەر دزرا. | Add a second factor, and delete accounts nobody uses.هۆکاری دووەم زیاد بکە و ئەو هەژمارانە بسڕەوە کە کەس بەکاریان ناهێنێت. |
| "Our data is in the cloud, so the provider protects it."« لە هەوردایە، بۆیە دابینکەرەکە دەیپارێزێت.» | The customer configures its own firewalls and access rights (shared responsibility).کڕیار خۆی و مافەکانی دەستڕاگەیشتنی ڕێک دەخات (). | Review cloud settings regularly; give each system only the access it needs.بە بەردەوامی پێداچوونەوە بە ڕێکخستنەکانی هەوردا بکە؛ تەنها ئەو دەستڕاگەیشتنە بدە کە پێویستە. |
| "We patched almost everything."«نزیکەی هەموو شتێکمان کرد.» | Attackers need only the one system you missed, as at Equifax. تەنها پێویستیان بەو یەک سیستەمەیە کە لەبیرت کردووە، وەک لە Equifax. | Keep a complete inventory and check after patching that every system really changed.لیستێکی تەواوی سیستەمەکان ڕابگرە و دوای بپشکنە کە هەموو سیستەمێک بە ڕاستی گۆڕاوە. |
| "Paying the ransom ends the problem."«پارەدانی بارمتە کێشەکە کۆتایی پێ دەهێنێت.» | Colonial paid and still had to rebuild; paying funds the next attack.Colonial پارەی دا و هێشتا دەبوو دووبارە دروستی بکاتەوە؛ پارەدان داهاتوو دارایی دەکات. | Prepare backups and an incident plan so paying is never needed. و پلانی ڕووداو ئامادە بکە بۆ ئەوەی هەرگیز پێویست بە پارەدان نەبێت. |
Exercisesڕاهێنانەکان
Apache published the fixed Struts versions on 7 March 2017. The attackers began taking data from Equifax on 13 May 2017, and Equifax announced the breach on 7 September 2017. (a) How many days did Equifax have to install the patch before data theft began? (b) How many days passed from the start of the theft to the announcement?
Apache لە 7ـی ئاداری 2017دا وەشانە چاککراوەکانی Strutsـی بڵاو کردەوە. لە 13ـی ئایاری 2017دا دەستیان کرد بە بردنی لە Equifax و Equifax لە 7ـی ئەیلوولی 2017دا ڕاگەیاند. (أ) Equifax چەند ڕۆژی هەبوو بۆ دامەزراندنی پێش دەستپێکردنی دزینی ؟ (ب) لە دەستپێکردنی دزینەکەوە تا ڕاگەیاندنەکە چەند ڕۆژ تێپەڕی؟
Hintئاماژە
Count the days left in the first month, add the full months, then the days in the last month.
ئەو ڕۆژانەی مانگی یەکەم بژمێرە کە دوای بەروارەکە دێن، مانگە تەواوەکان زیاد بکە، پاشان ڕۆژەکانی مانگی کۆتایی.
Show answerوەڵامەکە پیشان بدە
(a) The rest of March after the 7th is 24 days, then all of April (30) and 13 days of May: 67 days — more than nine weeks with a public fix. (b) The rest of May after the 13th is 18 days, then June (30), July (31), August (31) and 7 days of September: 117 days. People could not protect themselves during that time because they did not know.
(أ) ڕۆژەکانی ئادار دوای ڕۆژی 7 دەکەنە 24 ڕۆژ، پاشان هەموو نیسان (30) و 13 ڕۆژی ئایار: 67 ڕۆژ — زیاتر لە نۆ هەفتە کە چارەسەرێکی ئاشکرا هەبوو. (ب) ڕۆژەکانی ئایار دوای ڕۆژی 13 دەکەنە 18 ڕۆژ، پاشان حوزەیران (30)، تەممووز (31)، ئاب (31) و 7 ڕۆژی ئەیلوول: 117 ڕۆژ. لەو کاتەدا خەڵک نەیاندەتوانی خۆیان بپارێزن چونکە نەیاندەزانی.
For each case, name the two takeaways (from the four in the lecture, or the two extra ones) that would have helped most, and say why in one sentence.
بۆ هەر ڕووداوێک، ئەو دوو وانەیە ناو ببە (لە چوار وانەکەی ناو وانەکە، یان دوو زیادەکە) کە زۆرترین یارمەتییان دەدا و بە یەک ڕستە بڵێ بۆچی.
Show answerوەڵامەکە پیشان بدە
- Equifax: know everything you run plus regular scanning (the portal's flaw would have been found and patched), and network segmentation (the attackers could not have reached 48 more databases). Monitoring with a valid certificate would have shortened the 76 days.
- Colonial Pipeline: regular audits (the forgotten VPN account would have been found and removed) and MFA as part of strong access control; segmentation between business IT and pipeline control makes it easier to keep critical operations running safely when the business network is hit.
- Capital One: regular audits of cloud configuration (the firewall setting) and proactive monitoring (unusual copying from cloud storage would have been seen in March, not reported by an outsider in July).
- Equifax: هەموو ئەو شتانە بناسە کە بەکاریان دەهێنیت لەگەڵ پشکنینی بەردەوام (کێشەی پۆرتاڵەکە دەدۆزرایەوە و دەکرا) و ( نەیاندەتوانی بگەنە 48 تر). چاودێری بە کارا 76 ڕۆژەکەی کورت دەکردەوە.
- Colonial Pipeline: پشکنینی بەردەوام (هەژمارە لەبیرکراوەکەی دەدۆزرایەوە و دەسڕایەوە) و MFA وەک بەشێک لە کۆنترۆڵی بەهێزی دەستڕاگەیشتن؛ لە نێوان ITـی بازرگانی و کۆنترۆڵی هێڵە بۆرییەکە ئاسانتری دەکات کارە گرنگەکان بە سەلامەتی بەردەوام بن کاتێک بازرگانی تووشی دەبێت.
- Capital One: پشکنینی بەردەوامی ڕێکخستنەکانی هەور (ڕێکخستنی ) و چاودێریی پێشوەختە (کۆپیکردنی نائاسایی لە شوێنی هەڵگرتنی هەوری لە ئاداردا دەبینرا، نەک لە تەممووزدا کەسێکی دەرەکی ڕاپۆرتی بکات).
The course notes say: 'The Capital One breach exposed the personal data of 100 million customers, including … credit card information.' Rewrite the sentence so that it is accurate.
تێبینییەکانی کۆرسەکە دەڵێن: « Capital One 100 ملیۆن کڕیاری ئاشکرا کرد، لەوانە … زانیاریی کارتی قەرز.» ڕستەکە بە شێوەیەکی دروست بنووسەرەوە.
Show answerوەڵامەکە پیشان بدە
For example: 'The Capital One breach exposed data of about 106 million people (about 100 million in the US and 6 million in Canada), customers and card applicants, mostly credit-card application data such as names, addresses, birth dates and incomes; about 140,000 Social Security numbers and 80,000 bank account numbers were also taken, but no card account numbers or log-in credentials.'
بۆ نموونە: « Capital One نزیکەی 106 ملیۆن کەسی ئاشکرا کرد (نزیکەی 100 ملیۆن لە ئەمریکا و 6 ملیۆن لە کەنەدا)، کڕیاران و داواکارانی کارت، زۆربەی داواکاریی کارتی قەرز وەک ناو، ناونیشان، ڕێکەوتی لەدایکبوون و داهات؛ هەروەها نزیکەی 140,000 ژمارەی ئاسایشی کۆمەڵایەتی و 80,000 ژمارەی هەژماری بانکی بران، بەڵام هیچ ژمارەی هەژماری کارت یان نەبران.»
Shilan Pay is a small, fictional payment company. A review finds: (a) the VPN account of an employee who left last year still works, with a password only; (b) the customer database is on the same network as the staff's PCs; (c) an update for the framework behind the website, released three weeks ago, is not installed; (d) nobody has reviewed the cloud storage settings since they were created. For each finding, name the case it resembles and the first thing to do.
Shilan Pay کۆمپانیایەکی بچووکی خەیاڵیی پارەدانە. پشکنینێک ئەمانە دەدۆزێتەوە: (أ) هەژماری کارمەندێک کە ساڵی پار ڕۆیشت هێشتا کار دەکات، تەنها بە ؛ (ب) کڕیاران لەسەر هەمان کارمەندانە؛ (ج) بۆ ئەو لەسەری دروست کراوە، کە سێ هەفتە پێش ئێستا دەرچووە، دانەمەزراوە؛ (د) کەس لە کاتی دروستکردنیانەوە پێداچوونەوەی بە ڕێکخستنەکانی نەکردووە. بۆ هەر دۆزراوەیەک، ئەو ڕووداوە ناو ببە کە لێی دەچێت و یەکەم کار کە دەبێت بکرێت.
Show answerوەڵامەکە پیشان بدە
| Findingدۆزراوە | Likeوەک | First stepهەنگاوی یەکەم |
|---|---|---|
| (a) | Colonial Pipeline | Disable the account today; require MFA on every remote login.ئەمڕۆ هەژمارەکە ناچالاک بکە؛ MFA بۆ هەموو چوونەژوورەوەیەک لە دوورەوە داوا بکە. |
| (b) | Equifax | Move the database into its own protected segment, reachable only from the servers that need it. بگوازەرەوە بۆ بەشێکی پارێزراوی جیای خۆی کە تەنها ئەو پێویستیانە پێی بگەن. |
| (c) | Equifax | Test the update and install it quickly; check afterwards that every server got it. تاقی بکەرەوە و بە خێرایی دایبمەزرێنە؛ دواتر بپشکنە کە هەموو وەریگرتووە. |
| (d) | Capital One | Review the settings against a checklist; allow only the access each system needs; turn on alerts for unusual downloads.ڕێکخستنەکان بە لیستێکی پشکنین بەراورد بکە؛ تەنها ئەو دەستڕاگەیشتنە ڕێگەپێدراو بکە کە هەر سیستەمێک پێویستیەتی؛ ئاگادارکەرەوە بۆ داگرتنی نائاسایی داگیرسێنە. |
Summary and reviewپوختە و پێداچوونەوە
- Equifax (2017): an Apache Struts flaw patched on 7 March was still open in May; attackers stole identity data of about 147 million people over 76 days. Lessons: patch fast, know every system, segment, keep monitoring working.
- Colonial Pipeline (2021): a forgotten VPN account with a stolen password and no MFA let DarkSide in; the company stopped the pipeline for days and paid a ransom. Lessons: MFA everywhere, remove unused accounts, separate business and control systems.
- Capital One (2019): a misconfigured cloud firewall exposed data of about 106 million people, found by an outside tip. Lessons: review cloud settings, least access, monitoring, a reporting channel.
- The four takeaways: proactive monitoring (IDS, SIEM), regular audits and penetration tests, training and awareness, network segmentation.
- Equifax (2017): کێشەیەکی Apache Struts کە لە 7ـی ئاداردا کرابوو، لە ئایاردا هێشتا کراوە بوو؛ لە ماوەی 76 ڕۆژدا ناسنامەی نزیکەی 147 ملیۆن کەسیان دزی. وانەکان: خێرا بکە، هەموو سیستەمێک بناسە، بەش بەش بکە، چاودێری بە کارایی بهێڵەرەوە.
- Colonial Pipeline (2021): هەژمارێکی لەبیرکراوی بە دزراو و بێ MFA ڕێگەی بە DarkSide دا بچێتە ژوورەوە؛ کۆمپانیاکە بۆ چەند ڕۆژێک هێڵە بۆرییەکەی وەستاند و بارمتەی دا. وانەکان: MFA لە هەموو شوێنێک، سڕینەوەی هەژمارە بەکارنەهاتووەکان، جیاکردنەوەی سیستەمی بازرگانی و کۆنترۆڵ.
- Capital One (2019): هەوری کە بە هەڵە ڕێکخرابوو نزیکەی 106 ملیۆن کەسی ئاشکرا کرد و بە ئاگادارکردنەوەیەکی دەرەکی دۆزرایەوە. وانەکان: پێداچوونەوە بە ڕێکخستنەکانی هەوردا، کەمترین دەستڕاگەیشتن، چاودێری، کەناڵی ڕاپۆرتکردن.
- چوار وانەکە: چاودێریی پێشوەختە (IDS، )، پشکنینی بەردەوام و ، ڕاهێنان و ، .
Why is identity data worse to lose than a card number?بۆچی لەدەستدانی دراوەی ناسنامە خراپترە لە ژمارەی کارت؟
A card can be cancelled and replaced; a name, birth date or national ID number cannot be changed, so it can be misused for years.
کارت دەکرێت هەڵبوەشێنرێتەوە و بگۆڕدرێت؛ ناو، ڕێکەوتی لەدایکبوون یان ژمارەی ناسنامەی نیشتیمانی ناگۆڕدرێن، بۆیە دەکرێت بۆ ساڵانێک خراپ بەکار بهێنرێن.
Was the Colonial attack a zero-day?ئایا هێرشی Colonial خاڵی لاوازی ڕۆژی سفر بوو؟
No. It used a stolen password on an account without MFA — a known, avoidable weakness.
نەخێر. دزراوی لەسەر هەژمارێکی بێ MFA بەکار هێنا — لاوازییەکی ناسراو و ڕێگەلێگیراو.
In the shared responsibility model, who had to set Capital One's firewall correctly?لە مۆدێلی بەرپرسیارێتیی هاوبەشدا، کێ دەبوو ئاگرەدیواری Capital One بە دروستی ڕێک بخات؟
Capital One, the customer. The cloud provider protects its own infrastructure; customers configure what they build on it.
Capital One، واتە کڕیارەکە. ژێرخانی خۆی دەپارێزێت؛ کڕیاران ئەوە ڕێک دەخەن کە لەسەری دروستی دەکەن.
Lesson complete!وانەکە تەواو بوو!
Well done. Review the key terms, then go on to the next lesson.دەستخۆش. سەیرێکی زاراوە سەرەکییەکان بکەرەوە، پاشان بڕۆ بۆ وانەی داهاتوو.
Key termsزاراوە سەرەکییەکان
The Vulnerability Lifecycle and Patchingسووڕی ژیانی خاڵی لاواز و پینەکردن
Related lecturesوانە پەیوەندیدارەکان
- The Vulnerability Lifecycle and Patchingسووڕی ژیانی خاڵی لاواز و پینەکردن
- Ransomware: WannaCry, NotPetya and Recent Attacksنەرمەواڵەی بارمتەگر: WannaCry، NotPetya و هێرشە نوێیەکان
- Passwords, MFA and Access Controlتێپەڕەوشەکان، MFA و کۆنترۆڵی دەستڕاگەیشتن
- The Real Cost of a Cyber Attackتێچووی ڕاستەقینەی هێرشێکی سایبەری
- Responsible Disclosure and Bug Bountiesئاشکراکردنی بەرپرسیارانە و خەڵاتی دۆزینەوەی باگ
- Encryption, Hashing and Digital Signaturesشفرەکردن، هاشکردن و واژووە دیجیتاڵییەکان
- Security by Obscurity, by Legislation, and the Trade-off Triangleئاسایش بە شاردنەوە، ئاسایش بە یاسا و سێگۆشەی هاوسەنگی
- Cloud Databasesبنکەدراوە هەورییەکان
References and further readingسەرچاوەکان و خوێندنەوەی زیاتر
- US GAO: Data Protection — Actions Taken by Equifax and Federal Agencies in Response to the 2017 Breach (GAO-18-559, August 2018)
- US Federal Trade Commission: Equifax Data Breach Settlement
- Apache Struts: 2017 announcements (Struts 2.3.32 and 2.5.10.1, 7 March 2017)
- NIST National Vulnerability Database: CVE-2017-5638
- GovInfoSecurity: Colonial CEO at Senate Hearing Details Ransomware Attack (8 June 2021)
- CISA: The Attack on Colonial Pipeline — What We've Learned and What We've Done Over the Past Two Years (May 2023)
- Associated Press (via KSAT): Pipeline operator says normal operations have resumed (15 May 2021)
- Reuters (via The Business Standard): US seizes $2.3 mln in bitcoin paid to Colonial Pipeline hackers (8 June 2021)
- Capital One: Information on the 2019 Capital One Cyber Incident
- CyberScoop: Capital One to pay $80 million penalty for 2019 breach (6 August 2020)
- Data Center Knowledge: Ex-Amazon cloud worker convicted of massive Capital One hack (June 2022)
- News4JAX (AP): Colonial Pipeline initiates restart (12 May 2021)
This lecture is a first edition. The Kurdish text and terminology are waiting for review by Kurdish IT teachers.ئەم وانەیە چاپی یەکەمە. دەقە کوردییەکە و زاراوەکانی چاوەڕێی پێداچوونەوەی مامۆستایانی کوردی بواری IT ن.